
How to prevent financial loss caused through Clipboard Hijacker
TrojanAlso Known As: Clipboard Hijacker virus

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What is Clipboard Hijacker?
Clipboard Hijacker is malicious software used by cyber criminals to make fraudulent cryptocurrency transactions. This can be achieved simply by changing cryptocurrency wallet addresses from those saved in users' clipboards to others owned by cyber criminals.
In this way, they use Clipboard Hijacker to steal cryptocurrency from other people who use cryptocurrencies and make associated transactions. This malware must be uninstalled immediately.
More about Clipboard Hijacker
The clipboard is a buffer in operating systems used to temporarily store data while it is moved (typically, copied) from one place to another. For example, data copied from a document is stored in the clipboard so that users can then paste it to another, perhaps different, document.
In this particular case, cyber criminals use Clipboard Hijacker to replace the cryptocurrency wallet addresses that are copied to the clipboard with addresses of other wallets. Many people make transactions by entering their wallet addresses manually and copy them to the clipboard.
Cyber criminals then use Clipboard Hijacker to replace it with another address so that unsuspecting victims transfer money to them and not the intended recipient.
People tend not to double-check wallet addresses entered, and cyber criminals then successfully trick them into making unintentional transactions. To prevent this, remove Clipboard Hijacker immediately and double-check all addresses before making cryptocurrency transactions.
| Name | Clipboard Hijacker virus |
| Threat Type | Clipboard hijacking malware. |
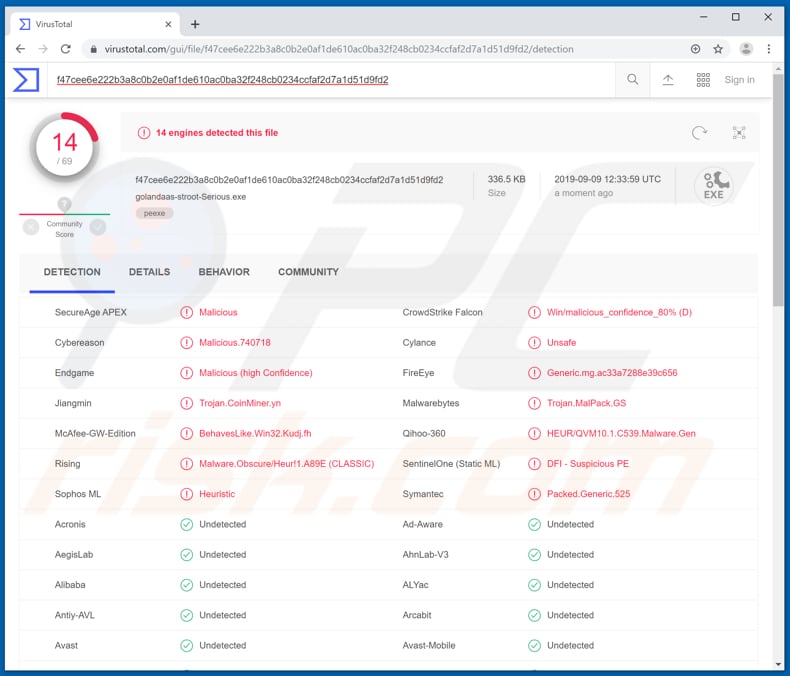
| Detection Names | AegisLab (Trojan.Win32.Generic.4!c), Endgame (Malicious (high Confidence)), ESET-NOD32 (PowerShell/Rozena.EA), Kaspersky (UDS:DangerousObject.Multi.Generic), Full List (VirusTotal) |
| Symptoms | Clipboard data stealers/hijackers are designed to stealthily infiltrate the victim's computer and remain silent, and thus no particular symptoms are clearly visible on an infected machine. |
| Distribution methods | Infected email attachments, malicious online advertisements, social engineering, software 'cracks'. |
| Damage | Stolen banking information, passwords, identity theft, victim's computer added to a botnet. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
Clipboard-hijacking malware in general
Many malicious programs are capable of replacing data saved to the clipboard. Other examples include Clipsa and Qulab.
Having malware such as Clipboard Hijacker installed on the system can lead to financial loss (loss of cryptocurrency). Cyber criminals might also use these programs to steal other personal information. In any case, all malware must be eliminated immediately.
How did Clipboard Hijacker infiltrate my computer?
Typically, malware such as Clipboard Hijacker is distributed using spam campaigns (emails), Trojans, untrustworthy software download sources/channels, unofficial tools that people use to activate software and fake software updaters. When cyber criminals use spam campaigns, they send emails that contain attachments.
Typically, they attach Microsoft Office documents, executable files such as .exe, archive files such as ZIP, RAR, PDF documents and JavaScript files. They disguise these attachments and/or emails as official and important and hope that recipients open the attached file.
It then installs malware. Malicious programs are also spread through Trojans, which, if installed, download and install other malicious programs. Examples of dubious download channels/tools are Peer-to-Peer networks (torrent clients, eMule and other tools), freeware download or file hosting websites, unofficial websites, third party downloaders, etc.
Cyber criminals use these to disguise infected files as harmless. When people download and open them, however, they install high-risk malware.
Software 'cracking' tools often download and install malicious programs rather than activating paid software or operating systems free of charge. Fake software update tools cause damage to systems by exploiting bugs/flaws of installed software that is out-of-date, or they install malicious software rather than updating legitimate programs already installed.
How to avoid installation of malware
If an email is received from an unknown, suspicious, or untrustworthy address and contains an attachment or web link, do not open it. All software should be downloaded from official websites and using direct download links. The aforementioned (and similar sources) should not be trusted.
Installed programs or operating systems must be updated through implemented functions or tools provided by official software developers. If installed software requires paid activation, it should not be performed using third party ('cracking') tools. These are illegal and often cause installation of malware.
Keep your computer safe by scanning it with reputable anti-virus or anti-spyware software regularly and keep it up-to-date. If you believe that your computer is already infected, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate infiltrated malware.
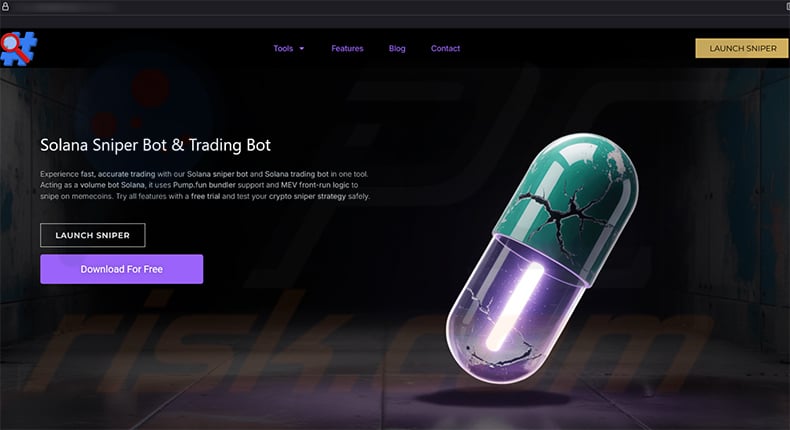
Update July 28, 2026 - According to research published by Check Point, a new clipboard hijacking campaign has been distributing Rust-based malware disguised as "edge" tools that promise unfair advantages in crypto trading and online gambling. Fake tools observed include automated cryptocurrency "sniper" bots for Solana and Pump.fun, an "Aviator Predictor" that claims to forecast the outcome of a popular multiplier game, and several crash-game "predictors." The malware has been confirmed to run on both Windows and macOS.
The campaign is built around an entire fake reputation ecosystem rather than a single download page. A dedicated phishing website, decryptor[.]net, acts as the central hub, offering the tools as a "free download" alongside a direct Telegram contact for "support." From there, the same operator promotes identical tools through GitHub and SourceForge project pages, a YouTube channel, paid press coverage, and posts on a popular Bitcoin discussion forum.
Fake website distributing the "Solana Sniper Bot" tool that installs the clipboard hijacker (source: research.checkpoint.com):
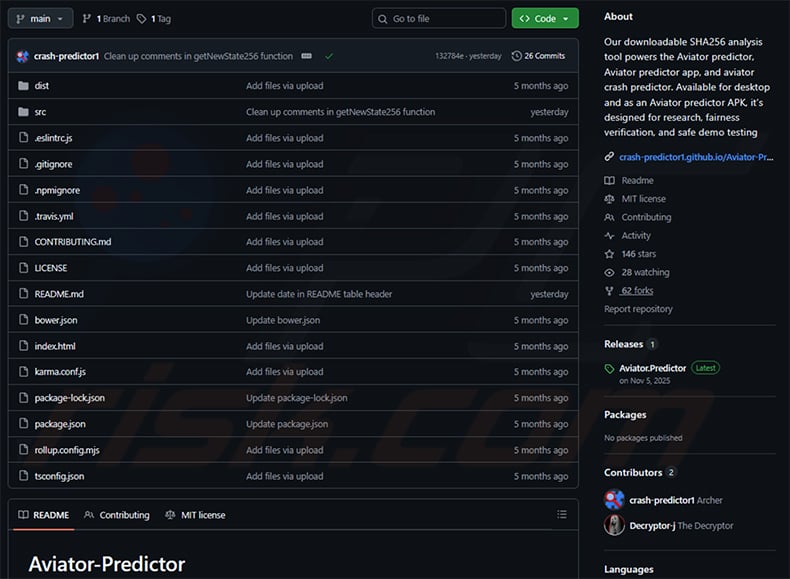
On GitHub and SourceForge, the tools carry inflated star counts, forks, and reviews that appear to come from a small ring of fake or repeat accounts rather than genuine users. One "Aviator Predictor" repository, uploaded under the account name "Decryptor-j," shows over 140 stars and 60 forks, while a SourceForge listing shows generic five-star reviews such as "everything is perfect" alongside claims of tens of thousands of downloads.
GitHub repository for the fake "Aviator Predictor" tool showing inflated stars and forks (source: research.checkpoint.com):
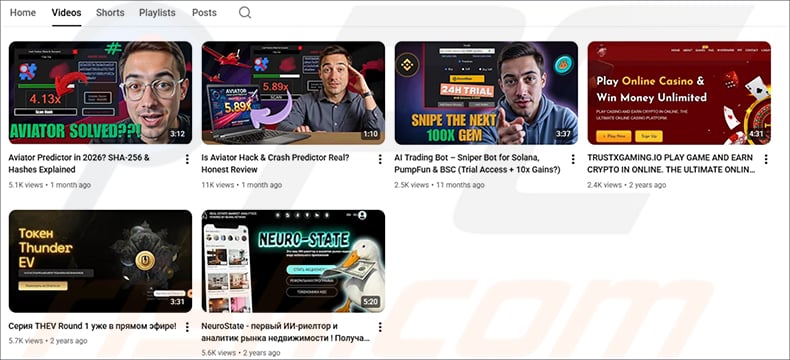
A dedicated YouTube channel promotes the same tools using an AI-generated presenter that appears identical across unrelated videos and topics. Despite claiming around 91,000 subscribers, the channel has accumulated fewer than 37,000 total views, a strong indicator the subscriber count was purchased rather than earned. A sudden, unexplained spike in view activity was also observed around the time the campaign intensified, and comments left on the videos are overwhelmingly positive and generic, following patterns typical of coordinated or fake engagement rather than organic feedback.
YouTube channel used to promote the fake crypto and gambling tools (source: research.checkpoint.com):
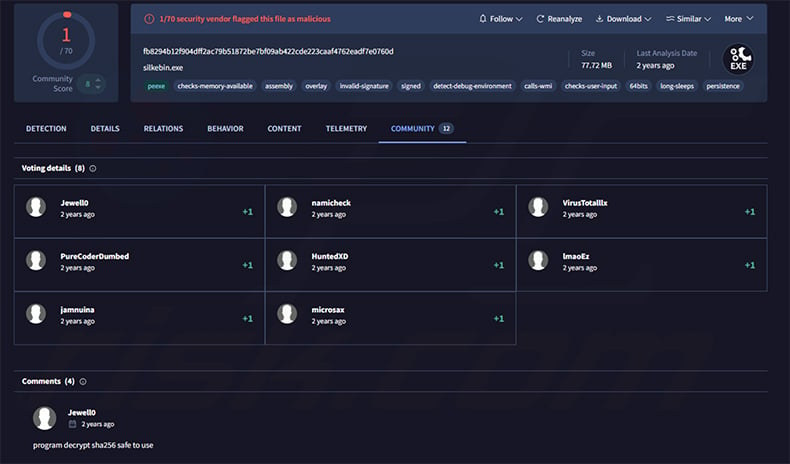
The same illusion of legitimacy extends to VirusTotal, the popular file-scanning service. Even though most security vendors do not flag the malware samples, a handful of the same accounts have been observed repeatedly leaving positive "safe" votes and comments such as "safe and clean" on multiple malicious files linked to this campaign, which can mislead both regular users and automated reputation-based detection systems that weigh community feedback.
VirusTotal community votes marking a malicious sample as "safe" (source: research.checkpoint.com):
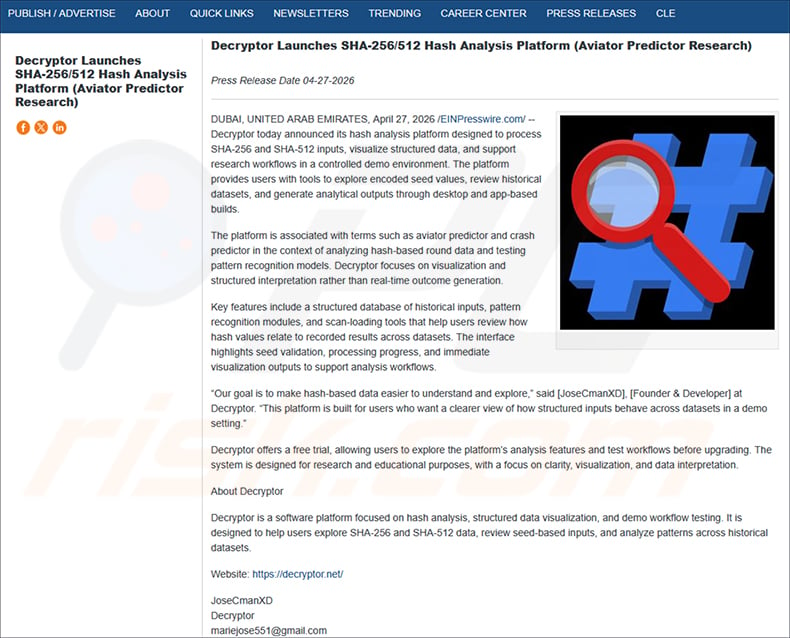
Perhaps most notably, the tools were also promoted through a fabricated corporate press release describing a fictitious "hash analysis platform," distributed through a legitimate press release wire service. As a side effect of that distribution method, the release was automatically republished by dozens of real, trusted local news websites across the United States, giving the malicious tools an appearance of mainstream media coverage they never earned.
The same fabricated press release republished across multiple legitimate United States news outlets (source: research.checkpoint.com):
Check Point also connected the operator behind this campaign to an online persona with a multi-year history of distributing clipboard hijacking tools. Records show the same individual was active on an underground "carding" forum as early as 2022, where they offered an earlier clipboard-hijacking builder tool to other cybercriminals, describing it as ready to spread and difficult to detect. This suggests the current campaign is a continuation of long-running activity rather than a first-time operation.
On the technical side, the installer includes a fake Windows security warning telling victims their download was "blocked by SmartScreen" and walks them through the exact steps needed to bypass this built-in Windows protection and run the file anyway. Once active, the malware continuously monitors the clipboard and swaps any copied cryptocurrency wallet address for one controlled by cybercriminals, with wallets linked to the campaign showing evidence of multiple successful transactions. (source: research.checkpoint.com).
How to remove malware manually?
Most trojan infections can be removed by running a full system scan with Combo Cleaner. The full manual procedure below is for cases where automatic removal failed, where you want to verify a scan caught everything, or where the threat has multiple persistence points.
Disconnect from the network
Unplug your Ethernet cable and turn off Wi-Fi. If you're on a laptop, the airplane-mode key works fastest.
Many trojans exfiltrate data - saved browser passwords, banking sessions, screenshots - and accept remote commands. Cutting the network stops both immediately. Keep it disconnected until Phase 4.
Boot into Safe Mode with Networking
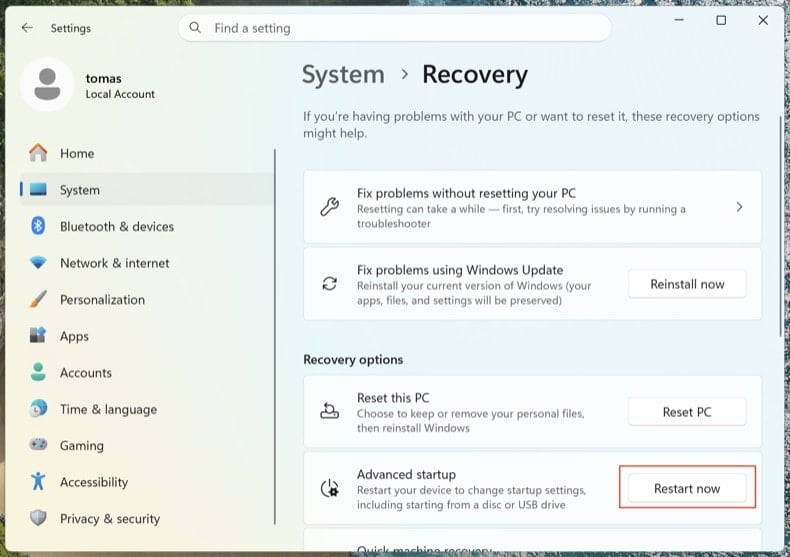
Safe Mode loads a minimal set of drivers and stops most malware from auto-running. "With Networking" lets you download tools - re-enable Wi-Fi only after you've booted in.
Open . Click Restart now next to Advanced startup.
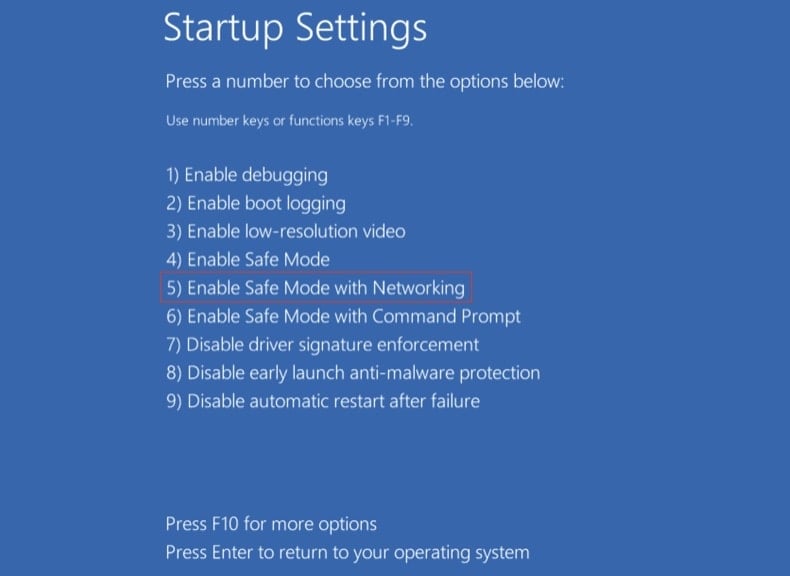
Your computer will restart into the "Choose an option" menu. Click . After the second reboot, press 5 or F5.
Click the Windows logo, hold Shift, click the Power icon and choose Restart. In the Choose an option screen, click . Press F5.
Windows 8
Go to the Start Screen, type Advanced, select Settings → Advanced startup options → Restart now → Troubleshoot → Advanced options → Startup settings → Restart → F5.
Note: Windows 8 reached end-of-life in January 2023 - running on it puts you at much higher risk of reinfection.
Windows 7
Click Start → Shut Down → Restart → OK. As the system boots, press F8 repeatedly until the Windows Advanced Options menu appears, then choose Safe Mode with Networking.
Note: Windows 7 reached end-of-life in January 2020 - running on it puts you at much higher risk of reinfection.
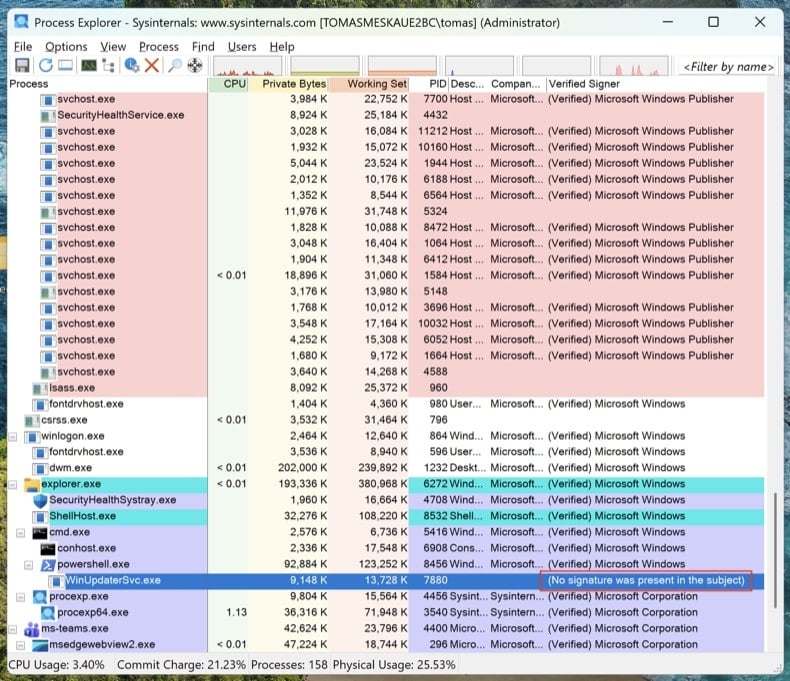
Inspect running processes with Process Explorer
Download Process Explorer from Microsoft Sysinternals. Run it as Administrator. Click and .
Sort by "Verified Signer." Anything unsigned running from %AppData%, %LocalAppData%, %Temp%, or %ProgramData% is suspicious. Right-click → Properties to see the full image path. Right-click → "Search Online" to look up unfamiliar process names.
Task Manager hides full file paths, doesn't show digital signatures, and groups processes in ways that make malware easy to miss. Process Explorer is the same tool Microsoft engineers use.
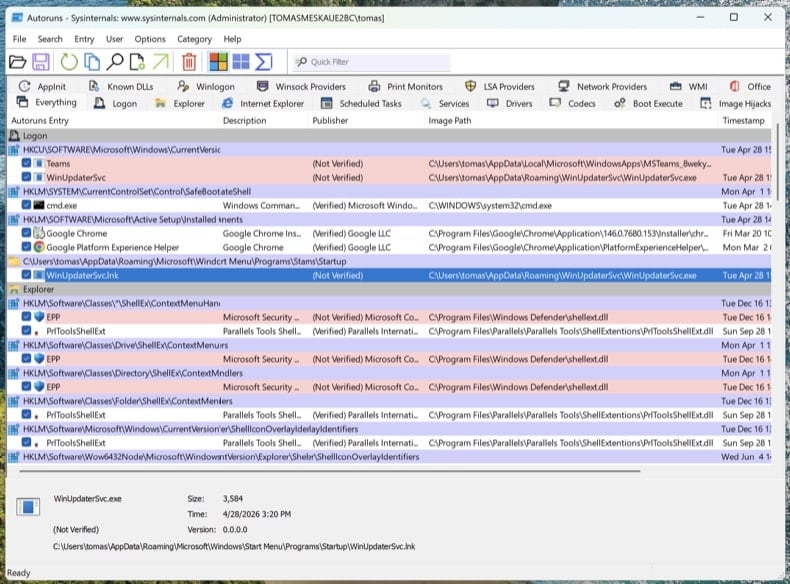
Map every persistence point with Autoruns
Download Autoruns. Right-click Autoruns.exe and choose Run as administrator - without elevation, Autoruns can't inspect protected registry hives.
In the menu, open and , then click Refresh.
Modern trojans don't just live in startup. Walk through these tabs and look for unsigned or unfamiliar entries:
- Logon - classic Run/RunOnce keys
- Scheduled Tasks - frequent hiding spot, especially tasks with PowerShell, MSHTA, or rundll32 actions
- Services - unsigned services in non-Microsoft folders
- WMI - Event Subscriptions are a stealthy persistence mechanism (MITRE T1546.003)
- Image Hijacks - Image File Execution Options "Debugger" abuse
- AppInit - DLLs loaded into every GUI process
- Browser plug-ins - unsigned add-ons across all installed browsers
Right-click any suspicious entry → "Jump to Image" to see the actual file. Right-click → "Search Online" opens VirusTotal for the file hash. Don't delete yet - just write down the file paths and entry names. We'll remove them after the scans.
Check the hosts file and DNS settings
Trojans often redirect bank, antivirus, and update domains to attacker-controlled servers by editing the hosts file or DNS settings.
Hosts file: Open Notepad as Administrator and open C:\Windows\System32\drivers\etc\hosts. Legitimate entries are commented with #. Any uncommented IP-to-domain mapping is suspicious - especially redirects for microsoft.com, windowsupdate, or your bank.
DNS settings: Open Command Prompt as Administrator and run ipconfig /all. Confirm your DNS servers point to your ISP, your router, or a known public resolver (Cloudflare 1.1.1.1, Google 8.8.8.8). Then open and verify both DNS and DNS over HTTPS (DoH) settings haven't been hijacked.
A clean PC with hijacked DNS is still a compromised PC. You'll think you're at chase.com and you'll be at the attacker's clone.
No single antivirus catches everything. The order below is intentional: offline scan first (catches rootkits before Windows fully loads), then on-demand scanners on the running system, then manual cleanup of anything they missed.
Run Microsoft Defender Offline
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. Your computer will restart into a stripped-down environment and scan before the full operating system loads.
Rootkits and bootkits hide from any scanner running on the same Windows session that's already infected. A pre-boot offline scan sees the disk before the malware can hide itself.
VB100 certified. Includes anti-trojan, registry/persistence scanning, anti-spyware in one pass. The 7-day free trial is available.
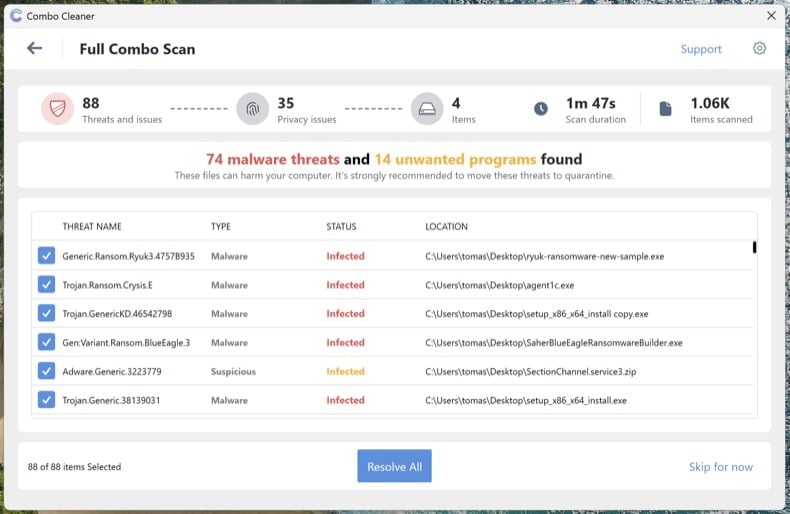
Download Combo CleanerRun Combo Cleaner full system scan
Install Combo Cleaner and run a full system scan (not the quick scan). Let it complete fully, review the detected threats, and apply the recommended actions. Combo Cleaner will quarantine known trojans and registry persistence.
Run Microsoft Safety Scanner as a second-opinion scan
Download Microsoft Safety Scanner (MSERT.exe), Microsoft's free on-demand tool. The binary expires every 10 days, which means every download has the latest signatures. Run a full scan after Combo Cleaner to catch anything one engine alone might miss.
Different scanning engines catch different threats. Running an additional Microsoft scan after Combo Cleaner is the single most underused verification step in malware removal.
Manually remove anything still listed in Autoruns
Reopen Autoruns. Anything you flagged in Step 4 that's still present hasn't been caught by the automated scans. For each remaining suspicious entry: right-click → Delete in Autoruns (this removes the persistence registration), then navigate to the file path and delete the actual file. Empty the Recycle Bin.
Some malware files reappear after deletion because something else on the system recreates them. If you delete a file and it returns within minutes, you have a remaining persistence point that Autoruns didn't show - usually a service or scheduled task running under SYSTEM. Re-run the scans from Steps 6-8 or proceed to a clean install (see end of guide).
Reset browsers and clear notification permissions
Trojans and adware frequently hijack browsers - change the default search engine, install rogue extensions, or grant themselves notification permissions to keep displaying scam pop-ups even after the malware is gone.
- Chrome: visit
chrome://settings/resetand click "Restore settings to their original defaults." Then visitchrome://settings/content/notificationsand remove any unfamiliar sites. - Edge: visit
edge://settings/reset. Then checkedge://settings/content/notifications. - Firefox: open
about:supportand click Refresh Firefox (Firefox uses "Refresh," not "Reset"). Then check Settings → Privacy & Security → Permissions → Notifications.
Review installed extensions in each browser and remove anything you don't recognize, especially extensions you didn't install yourself.
Re-enable Defender, Tamper Protection, and update everything
Many trojans disable security software. Open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all turned on. Tamper Protection prevents malware from disabling Defender silently.
Then run Windows Update () and update your browsers and applications. The infection vector that let the trojan in originally usually involves outdated software.
Change passwords from a clean device
If the trojan was an info-stealer (Lumma, RedLine, Vidar, and similar are extremely common), assume every password saved in your browser is compromised. Change them from a different, known-clean device - your phone is fine if it's not infected.
Recommended order:
- Primary email first - it's the recovery hub for everything else
- Banking and financial accounts
- Password manager master password (if you use one)
- Social media, shopping, and remaining accounts
Where available, enable phishing-resistant multi-factor authentication (passkeys / FIDO2 hardware keys / authenticator apps) - SMS-based MFA is bypassable by sophisticated attackers.
Verify the clean and monitor for 7 days
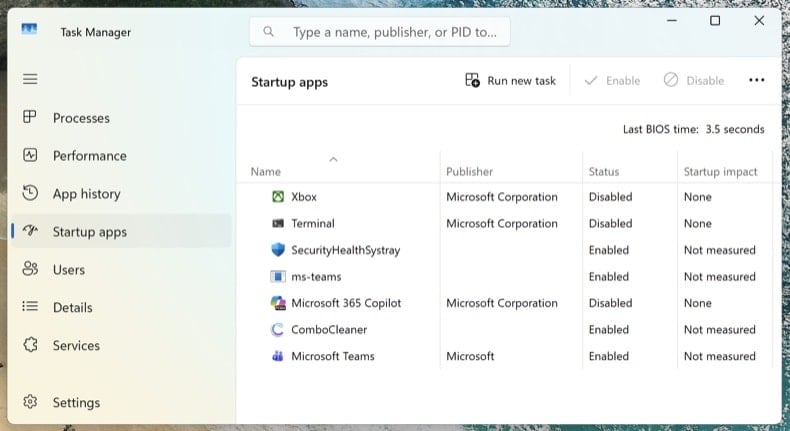
Reconnect to the network and run one final full scan with Combo Cleaner. Open Task Manager (Ctrl + Shift + Esc) and switch to the Startup apps tab - confirm nothing suspicious has reappeared.
Over the next 7 days, watch for symptom recurrence: unexpected high CPU usage, unknown processes returning, browser redirects, or pop-ups. If anything returns, you missed a persistence point and the procedure needs to be repeated - or you may have a deeper compromise that requires a clean install.
When to clean install Windows instead
Manual removal isn't always the right answer. Reinstalling Windows from scratch is the only way to be 100% certain when:
- The malware reappears after every removal attempt
- A bootkit or UEFI rootkit was detected (this class of threat sits below the operating system and survives a normal Windows reinstall)
- A confirmed credential-theft trojan ran with administrator privileges (Lumma, RedLine, Vidar) - the system likely has multiple unknown payloads
- The PC is used for online banking, business email, or anything where partial doubt isn't acceptable
A clean install is a 30-60 minute process: Windows 11 reinstall via . Back up documents to external storage first, scan the backup with Combo Cleaner before restoring it, and reinstall applications fresh - never restore them from a backup of the infected system.
Important: Manual removal requires advanced computer skills. If you're not confident identifying system files from malicious files, run an automated scan with Combo Cleaner and Windows Defender and stop there - that path catches the vast majority of consumer trojans without the risk of breaking Windows by deleting the wrong file.
Frequently Asked Questions (FAQ)
My computer is infected with a Clipboard Hijacker, should I format my storage device to get rid of it?
No, this malware can be removed without formatting the storage device. Our malware removal guide can be found above.
What are the biggest issues that malware can cause?
It depends on the type of malware. Typically, the biggest issues with having a computer infected with malware are data loss, monetary loss, hijacked personal accounts, identity theft, and (or) additional computer infections.
What is the purpose of a Clipboard Hijacker?
This malware replaces a cryptocurrency wallet address copied to the clipboard with an address owned by cybercriminals. It is used to steal cryptocurrency by tricking victims into making unintentional transactions.
How did a malware infiltrate my computer?
Most cybercriminals use phishing and other social engineering techniques (lime emails containing malicious links or attachments, fake system warning messages, etc.), drive-by downloads, P2P networks, unofficial software download websites, and cracked software distribution sites to distribute malware. In all cases, their goal is to trick users into executing malware by themselves.
Will Combo Cleaner protect me from malware?
Yes, Combo Cleaner can detect and eliminate almost all known malware. It is important to know that high-end malware usually hides deep in the operating system. In such cases, it is required to run a full system scan to eliminate malware from it.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion