
How to recognize scams like Start The Conversation With Bad News
Phishing/ScamAlso Known As: Start The Conversation With Bad News sextortion scam

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What is Start The Conversation With Bad News email scam?
The purpose of this email scam is to trick recipients into believing that their computers have been hacked and used to record an intimate video (a video of recipients visiting adult websites). Typically, scammers behind sextortion scams demand payment for not sharing the "recorded" video (or other intimate material).
Start The Conversation With Bad News sextortion scam in detail
Scammers claim that they have planted a Trojan virus on the recipients' computers. They also claim that they have hacked their email accounts. Their goal is to trick recipients into believing that they have recorded intimate videos and share them with all relatives, friends, and colleagues in contact lists of the recipients.
Scammers demand to be paid $1370 to the provided cryptocurrency wallet within 48 hours of receiving this email. They must not be paid: they do not have access to a computer, webcam, browsing history, or anything else they claim that they have access to.
| Name | Start The Conversation With Bad News Email Scam |
| Threat Type | Phishing, Scam, Social Engineering, Fraud |
| Fake Claim | A computer has been infected with a Trojan that allowed scammers to record an intimate video |
| Ransom Amount | $1370 in Bitcoins |
| Cyber Criminal Cryptowallet Address | 1NYCdN9eBXhT4tPSpu4EhpjC9gHXLzipLL, 17uRSEYKbco6kMrEc5aVCsCPAsFTVRPtsd, bc1qmqs2lavzy9k8ulcdgkrjj2njpcl62vksuhsytt, 1awD97gxBUEaiH432wJxknaLEAFdAEpso, 1N5J73F3gYPgZ8zkbnUhoryrYjQcqsA7St, 19yaJM8qhsyXnwoQP7zQbMkqJStoMYxPmE, 1J8MbLHX7qtshxEn5XJygGUgsAk89597WC, 1JfnsTBvRQYNvzxYFTQBtEUgojmPy2vd6F, 1Cc5SjkxeZSAqryhH2MiaRGQtCrTcmAAHj, 19Ya5oeV6zqsHa9TSyurpeF1LpYJqm84Yv, 17BSLhc597GybEuZ4DyFpdtceY3Moi3nWo, 1CDLcxiYqWBhDsxriEP92aFTLe9gyyRS4L, 12dYE7RcxkD5WhuSJEEvWcrMUPA8gcHwmX, 1KoJtFyg1dUuceaLekcf5MAKcDhj79eWvu, 123GtJkq3A7V2aBTB461pNaJWMbpdxY9cg, 1AJcoDsSGe9teEfzSMicXprJFae7729J5y, 3QyKsCx2qpwCfaqcAnJU8Rskkv5iKcdFNm, 0xb48570bcbad7a3d00598fd5d130e0c2a9f710d42, 1G8U8mNRBkBPmMrHZ3MMZnM1dH5bLKhLhp, 1GzNpKDWNuvQXuRWdK1RdDgX9YEizwynPQ, 1LzggssAAtthNh2bvUkbe6ADN5EJk8i1sd, 1qiua14J2UveEWHKSrytrnVC6QNAomv5Y, 1AABBXAzQw8wrayLbM9SeZy5PA6LWGC9Du, 1HbJxyHEKTKVzgp9rb7r7KVZLBoUp6qErH, 1PzZ3jX1zrGov2qyrMB8x3fKCrfxvTU2Tx |
| Distribution methods | |
| Damage | Monetary loss |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
More examples of similar email scams
"I Would Like To Avoid Any Accusations Against You Email Scam", "Im In Possession Of All Of Your Private Data Email Scam", "Unfortunately, There Are Some Bad News For You Email Scam". Sometimes, these emails contain old passwords that recipients have been used some time ago. Scammers obtain passwords from leaked databases.
How do spam campaigns infect computers?
Emails can be used to deliver malware by sending malicious attachments or website links. The purpose of such emails is to trick recipients into executing (opening) a malicious file. Most threat actors use malicious MS Office documents, JavaScript files, PDF documents, archive files, or executable files to deliver malware via emails.
How to avoid installation of malware?
Do not open links or attachments in emails sent from suspicious (or unknown) addresses. Especially when received emails are not relevant. Always use official websites and direct links as sources for downloading software (or files). Never use third-party tools to update or activate installed software. It should be achieved using tools provided by the official software developers.
If you've already opened malicious attachments, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate infiltrated malware.
Appearance of the Start The Conversation With Bad News sextortion email:
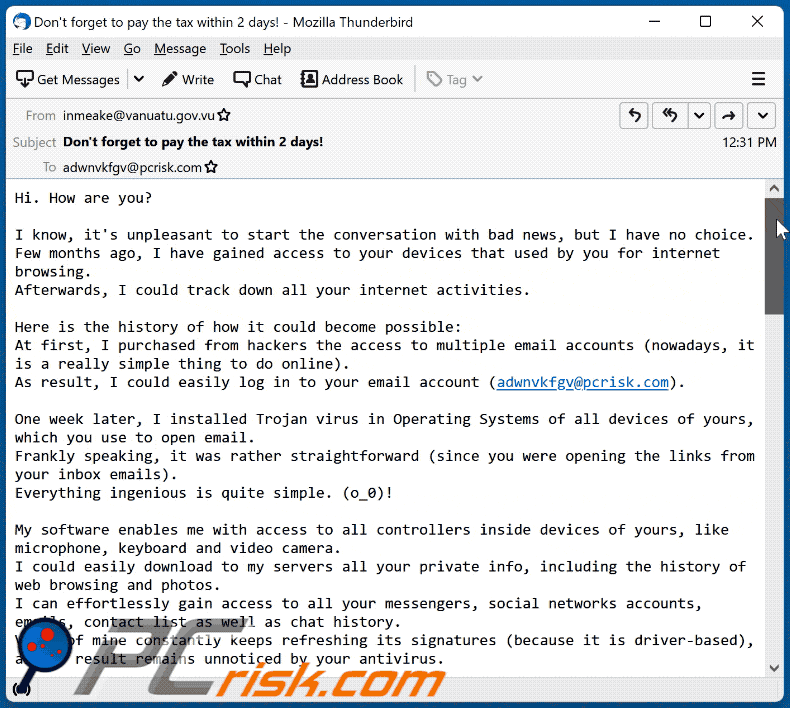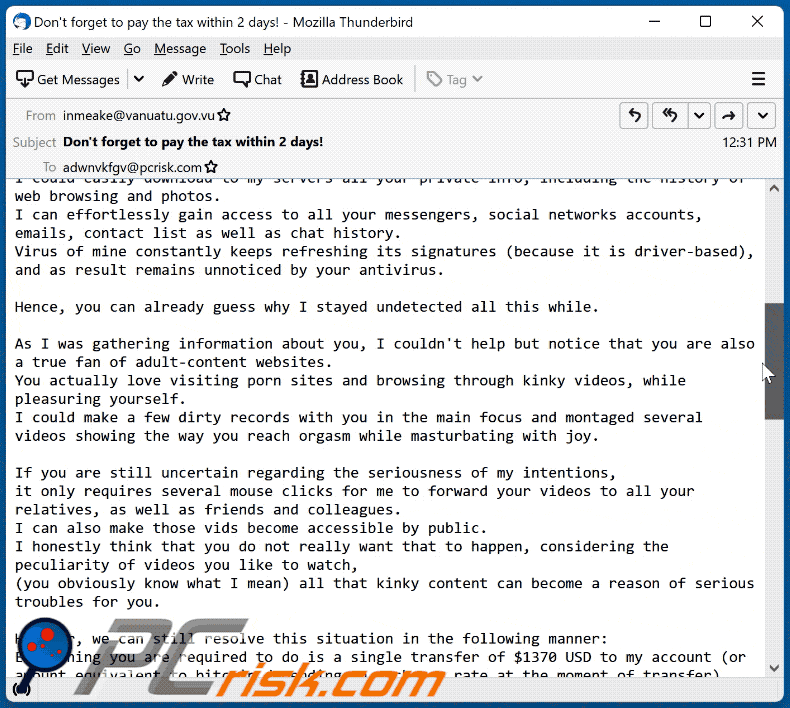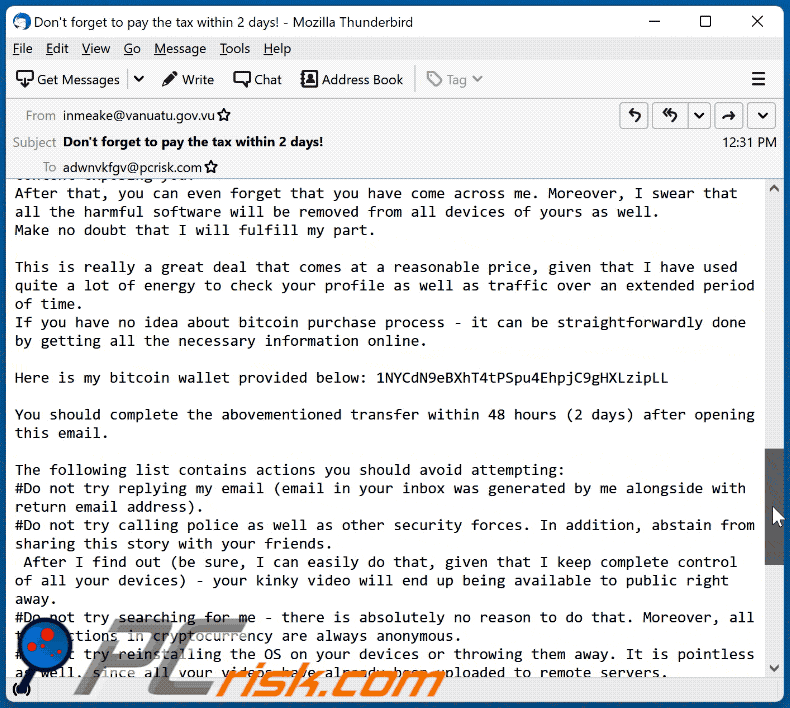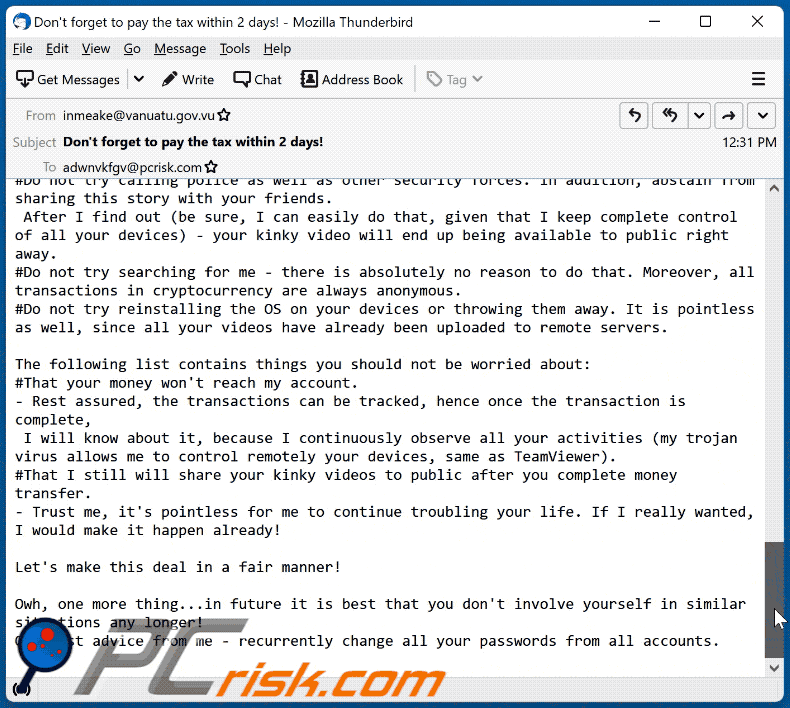
Text presented in the email letter:
Subject: Don't forget to pay the tax within 2 days!
Hi. How are you?
I know, it's unpleasant to start the conversation with bad news, but I have no choice.
Few months ago, I have gained access to your devices that used by you for internet browsing.
Afterwards, I could track down all your internet activities.Here is the history of how it could become possible:
At first, I purchased from hackers the access to multiple email accounts (nowadays, it is a really simple thing to do online).
As result, I could easily log in to your email account (-).One week later, I installed Trojan virus in Operating Systems of all devices of yours, which you use to open email.
Frankly speaking, it was rather straightforward (since you were opening the links from your inbox emails).
Everything ingenious is quite simple. (o_0)!My software enables me with access to all controllers inside devices of yours, like microphone, keyboard and video camera.
I could easily download to my servers all your private info, including the history of web browsing and photos.
I can effortlessly gain access to all your messengers, social networks accounts, emails, contact list as well as chat history.
Virus of mine constantly keeps refreshing its signatures (because it is driver-based), and as result remains unnoticed by your antivirus.Hence, you can already guess why I stayed undetected all this while.
As I was gathering information about you, I couldn't help but notice that you are also a true fan of adult-content websites.
You actually love visiting porn sites and browsing through kinky videos, while pleasuring yourself.
I could make a few dirty records with you in the main focus and montaged several videos showing the way you reach orgasm while masturbating with joy.If you are still uncertain regarding the seriousness of my intentions,
it only requires several mouse clicks for me to forward your videos to all your relatives, as well as friends and colleagues.
I can also make those vids become accessible by public.
I honestly think that you do not really want that to happen, considering the peculiarity of videos you like to watch,
(you obviously know what I mean) all that kinky content can become a reason of serious troubles for you.However, we can still resolve this situation in the following manner:
Everything you are required to do is a single transfer of $1370 USD to my account (or amount equivalent to bitcoin depending on exchange rate at the moment of transfer),
and once the transaction is complete, I will straight away remove all the dirty content exposing you.
After that, you can even forget that you have come across me. Moreover, I swear that all the harmful software will be removed from all devices of yours as well.
Make no doubt that I will fulfill my part.This is really a great deal that comes at a reasonable price, given that I have used quite a lot of energy to check your profile as well as traffic over an extended period of time.
If you have no idea about bitcoin purchase process - it can be straightforwardly done by getting all the necessary information online.Here is my bitcoin wallet provided below: 1NYCdN9eBXhT4tPSpu4EhpjC9gHXLzipLL, 1N5J73F3gYPgZ8zkbnUhoryrYjQcqsA7St, 1JfnsTBvRQYNvzxYFTQBtEUgojmPy2vd6F, 19Ya5oeV6zqsHa9TSyurpeF1LpYJqm84Yv, 17BSLhc597GybEuZ4DyFpdtceY3Moi3nWo, 1CDLcxiYqWBhDsxriEP92aFTLe9gyyRS4L
You should complete the abovementioned transfer within 48 hours (2 days) after opening this email.
The following list contains actions you should avoid attempting:
#Do not try replying my email (email in your inbox was generated by me alongside with return email address).
#Do not try calling police as well as other security forces. In addition, abstain from sharing this story with your friends.
After I find out (be sure, I can easily do that, given that I keep complete control of all your devices) - your kinky video will end up being available to public right away.
#Do not try searching for me - there is absolutely no reason to do that. Moreover, all transactions in cryptocurrency are always anonymous.
#Do not try reinstalling the OS on your devices or throwing them away. It is pointless as well, since all your videos have already been uploaded to remote servers.The following list contains things you should not be worried about:
#That your money won't reach my account.
- Rest assured, the transactions can be tracked, hence once the transaction is complete,
I will know about it, because I continuously observe all your activities (my trojan virus allows me to control remotely your devices, same as TeamViewer).
#That I still will share your kinky videos to public after you complete money transfer.
- Trust me, it's pointless for me to continue troubling your life. If I really wanted, I would make it happen already!Let's make this deal in a fair manner!
Owh, one more thing...in future it is best that you don't involve yourself in similar situations any longer!
One last advice from me - recurrently change all your passwords from all accounts.
A Polish variant of "Start The Conversation With Bad News" scam email:
Text presented within:
Subject: Nie zapomnij zapłacić podatku w ciągu 2 dni!
Cześć. Jak się masz?Wiem, że to nieprzyjemne zaczynać rozmowę od złych wieści, ale nie mam wyboru.
Kilka miesięcy temu, uzyskałem dostęp do twoich urządzeń, które używasz do przeglądania internetu.
Następnie mogłem prześledzić całą twoją aktywność w internecie.Oto historia tego, jak to było możliwe:
Na początku wykupiłem od hakerów dostęp do wielu kont pocztowych (w dzisiejszych czasach jest to naprawdę prosta rzecz do zrobienia w sieci).
W rezultacie mogłem łatwo zalogować się na Twoje konto pocztowe (********).Tydzień później zainstalowałem trojana w systemach operacyjnych wszystkich urządzeń, których używasz do otwierania poczty elektronicznej.
Szczerze mówiąc, było to dość proste (ponieważ otwierasz linki z wiadomości ze skrzynki mailowej).
Wszystko co genialne jest dość proste. 。゚・ (>﹏<) ・゚。
Moje oprogramowanie umożliwia mi dostęp do wszystkich kontrolerów twoich urządzeń, takich jak mikrofon, klawiatura i kamerka.
Mogę łatwo pobrać na moje serwery wszystkie twoje prywatne informacje, w tym historię przeglądania stron internetowych i zdjęcia.
Mogę bez trudu uzyskać dostęp do wszystkich twoich komunikatorów, kont na portalach społecznościowych, e-maili, listy kontaktów oraz historii czatów.
Mój wirus nieustannie odświeża swoje sygnatury (ponieważ jest oparty na sterownikach), w wyniku czego pozostaje niezauważony przez twój program antywirusowy.Dlatego już teraz możesz się domyślać, dlaczego przez cały ten czas pozostawałem niewykryty.
Zbierając informacje o tobie, nie mogłem nie zauważyć, że jesteś prawdziwym fanem stron z treściami dla dorosłych.
Uwielbiasz odwiedzać strony porno i przeglądać filmy erotyczne, jednocześnie sprawiając sobie przyjemność.
Mógłbym nagrać kilka sprośnych płyt z tobą w roli głównej i zmontować kilka filmów pokazujących, jak osiągasz orgazm podczas pełnej rozkoszy masturbacji.Jeśli nadal nie doceniasz powagi moich intencji, to wystarczy kilka kliknięć myszką, abym przekazał twoje filmy wszystkim krewnym, a także przyjaciołom i kolegom.
Mogę również sprawić, że te filmy staną się publicznie dostępne.
Szczerze myślę, że nie bardzo chcesz, aby tak się stało, biorąc pod uwagę specyfikę filmów, które lubisz oglądać (oczywiście wiesz, co mam na myśli),
wszystkie te zboczone treści mogą stać się dla ciebie źródłem poważnych kłopotów.Jednakże, nadal możemy rozwiązać tę sytuację w następujący sposób:
Wszystko, co jesteś zobowiązany zrobić, to jednorazowy przelew 5500zł na moje konto (lub kwota stanowiąca równowartość bitcoinów w zależności od kursu walut w momencie przelewu),
a po zakończeniu transakcji od razu usunę wszystkie zboczone treści, które cię demaskują.
Po tym możesz nawet zapomnieć, że trafiłeś na mnie. Co więcej, przysięgam, że wszystkie szkodliwe programy zostaną usunięte również z wszystkich twoich urządzeń.
Nie miej wątpliwości, że spełnię swoją obietnicę.Jest to naprawdę świetna oferta w rozsądnej cenie, biorąc pod uwagę, że zużyłem sporo energii, aby sprawdzić swój profil, a także ruch w sieci w dłuższym okresie czasu.
Jeśli nie masz pojęcia o procesie zakupu bitcoinów - można to zrobić prosto, uzyskując wszystkie niezbędne informacje online.Szczegóły mojego portfela Bitcoin poniżej: 12dYE7RcxkD5WhuSJEEvWcrMUPA8gcHwmX, 1KoJtFyg1dUuceaLekcf5MAKcDhj79eWvu
Musisz wykonać wyżej wymieniony przelew w ciągu 48 godzin (2 dni) od otwarcia tego e-maila.
Poniższa lista zawiera działania, których powinieneś unikać:
*Nie próbuj odpowiadać na mój email (email w twojej skrzynce został wygenerowany przeze mnie wraz ze zwrotnym adresem email).
*Nie próbuj dzwonić na policję, jak również do innych służb bezpieczeństwa. Ponadto, powstrzymaj się od dzielenia się tą historią z przyjaciółmi.
Po tym jak się o tym dowiem (bądź pewien, że mogę to łatwo zrobić,
biorąc pod uwagę, że mam całkowitą kontrolę nad wszystkimi twoimi urządzeniami) - twoje zboczone filmy będą od razu publicznie dostępne.
*Nie próbuj mnie szukać - nie ma absolutnie żadnego powodu, aby to robić. Co więcej, wszystkie transakcje w kryptowalucie są zawsze anonimowe.
*Nie próbuj reinstalować systemu operacyjnego na swoich urządzeniach ani ich wyrzucać. Jest to również bezcelowe, ponieważ wszystkie twoje filmy zostały już przesłane na zdalne serwery.Poniższa lista zawiera rzeczy, o które nie musisz się martwić:
*Że twoje pieniądze nie dotrą na moje konto.
- Spokojnie, transakcje można śledzić, a więc po zakończeniu transakcji będę o tym wiedział,
ponieważ stale obserwuję wszystkie twoje poczynania (mój trojan pozwala mi zdalnie kontrolować twoje urządzenia, tak jak TeamViewer).
*Że po zakończeniu transferu pieniędzy nadal będę publicznie udostępniał twoje zboczone filmy.
- Zaufaj mi, to nie ma sensu, abym dalej niepokoił twoje życie. Gdybym naprawdę chciał, już bym to zrobił!Zawrzyjmy ten układ w uczciwy sposób!
Aha, jeszcze jedno... na przyszłość lepiej nie angażuj się więcej w podobne sytuacje!
Ostatnia rada ode mnie - regularnie zmieniaj wszystkie swoje hasła do wszystkich kont.
A German variant of "Start The Conversation With Bad News" scam email:
Text presented within:
Subject: Vergessen Sie nicht, innerhalb von 2 Tagen die Steuer zu zahlen!
Hallo, wie geht es Ihnen?Ich weiß, es ist unangenehm, das Gespräch mit schlechten Nachrichten zu beginnen, aber ich habe keine andere Wahl.
Vor ein paar Monaten habe ich mir Zugang zu Ihren Geräten verschafft, die Sie zum Surfen im Internet benutzen.
Danach konnte ich alle Ihre Internetaktivitäten aufspüren.Hier ist die Vorgeschichte, wie es dazu kommen konnte:
Zunächst habe ich mir von Hackern den Zugang zu mehreren E-Mail-Konten erkauft (heutzutage ist das online sehr einfach zu bewerkstelligen).
So konnte ich mich problemlos in Ihr E-Mail-Konto einloggen (********).Eine Woche später habe ich in den Betriebssystemen aller Ihrer Geräte, die Sie zum Öffnen von E-Mails verwenden, einen Trojaner installiert.
Ehrlich gesagt, war das ziemlich einfach (da Sie die Links aus Ihren E-Mails im Posteingang geöffnet haben).
Das Geniale ist ganz einfach. 。゚・ (>﹏<) ・゚。Meine Software ermöglicht mir den Zugriff auf alle Steuerungen in Ihren Geräten, wie Mikrofon, Tastatur und Videokamera.
Ich kann ganz einfach alle Ihre privaten Daten auf meine Server herunterladen, einschließlich des Verlaufs Ihres Internet-Browsings und Ihrer Fotos.
Ich kann mühelos auf alle Ihre Messenger, Konten bei sozialen Netzwerken, E-Mails, Kontaktlisten und Chatverläufe zugreifen.
Mein Virus aktualisiert ständig seine Signaturen (weil er treiberbasiert ist) und bleibt daher von Ihrem Antivirusprogramm unbemerkt.Sie können sich also schon denken, warum ich die ganze Zeit unentdeckt geblieben bin.
Als ich Informationen über Sie sammelte, konnte ich nicht umhin festzustellen, dass Sie auch ein echter Fan von Webseiten mit Inhalten für Erwachsene sind.
Sie lieben es Pornoseiten zu besuchen und perverse Videos anzuschauen, während Sie sich selbst befriedigen.
Ich konnte ein paar schmutzige Aufnahmen mit Ihnen als Hauptdarsteller machen und mehrere Videos montieren, die zeigen, wie Sie beim lustvollen Masturbieren zum Orgasmus kommen.Wenn Sie immer noch unsicher sind, ob meine Absichten ernst gemeint sind, kann ich Ihre Videos mit wenigen Mausklicks an alle Ihre Verwandten, Freunde und Kollegen weiterleiten.
Ich kann diese Videos auch für die Öffentlichkeit zugänglich machen.
Ich glaube ehrlich gesagt nicht, dass Sie das wirklich wollen, denn in Anbetracht der Besonderheit der Videos,
die Sie sich gerne ansehen (Sie wissen natürlich, was ich meine), können all diese perversen Inhalte zu einem Grund für ernsthafte Probleme für Sie werden.Wir können diese Situation jedoch auf die folgende Weise lösen:
Alles, was Sie tun müssen, ist eine einmalige Überweisung von 1850€ auf mein Konto (oder den entsprechenden Betrag in Bitcoin,
je nach Wechselkurs zum Zeitpunkt der Überweisung) und sobald die Transaktion abgeschlossen ist, werde ich alle schmutzigen Inhalte, die Sie entblößen, sofort entfernen.
Danach können Sie sogar vergessen, dass Sie mir begegnet sind. Außerdem schwöre ich Ihnen, dass alle schädlichen Programme auch von allen Ihren Geräten entfernt werden.
Zweifeln Sie nicht daran, dass ich meinen Teil erfüllen werde.Das ist wirklich ein großartiges Angebot zu einem vernünftigen Preis, bedenkt man, dass ich ziemlich viel Energie darauf verwendet habe,
Ihr Profil und Ihren Datenverkehr über einen längeren Zeitraum zu überprüfen.
Wenn Sie keine Ahnung vom Bitcoin-Kaufprozess haben, können Sie ihn ganz einfach online durchführen, indem Sie sich alle notwendigen Informationen beschaffen.Hier finden Sie meine Bitcoin-Wallet: 123GtJkq3A7V2aBTB461pNaJWMbpdxY9cg
Sie sollten die oben genannte Überweisung innerhalb von 48 Stunden (2 Tagen) nach dem Öffnen dieser E-Mail abschließen.
Die folgende Liste enthält Aktionen, die Sie vermeiden sollten:
*Versuchen Sie nicht, auf meine E-Mail zu antworten (die E-Mail in Ihrem Posteingang wurde von mir zusammen mit der Absender-E-Mail-Adresse generiert).
*Versuchen Sie nicht, die Polizei oder andere Sicherheitskräfte anzurufen. Verzichten Sie außerdem darauf, diese Geschichte mit Ihren Freunden zu teilen.
Wenn ich das herausfinde (seien Sie sicher, dass ich das leicht tun kann, da ich die vollständige Kontrolle über alle Ihre Geräte habe),
wird Ihr perverses Video sofort öffentlich zugänglich sein.
*Versuchen Sie nicht, nach mir zu suchen - es gibt absolut keinen Grund, das zu tun. Außerdem sind alle Transaktionen in Kryptowährung immer anonym.
*Versuchen Sie nicht, das Betriebssystem auf Ihren Geräten neu zu installieren oder sie wegzuwerfen.
Das ist auch sinnlos, da alle Ihre Videos bereits auf entfernte Server hochgeladen wurden.Die folgende Liste enthält Dinge, über die Sie sich keine Sorgen machen sollten:
*Dass Ihr Geld nicht auf meinem Konto ankommt.
- Seien Sie versichert, dass die Transaktionen nachverfolgt werden können,
d.h. sobald die Transaktion abgeschlossen ist, werde ich davon wissen, denn ich beobachte ständig alle Ihre Aktivitäten
(mein Trojaner-Virus ermöglicht es mir, Ihre Geräte aus der Ferne zu kontrollieren, genau wie bei TeamViewer).
*Dass ich Ihre perversen Videos auch noch öffentlich machen werde, nachdem Sie den Geldtransfer abgeschlossen haben.
- Glauben Sie mir, es ist zwecklos, dass ich Ihr Leben weiter störe. Wenn ich es wirklich wollte, würde ich es schon längst tun!Lassen Sie uns dieses Geschäft auf faire Weise abschließen!
Ach ja, noch etwas... in Zukunft sollten Sie sich besser nicht mehr in ähnliche Situationen verwickeln lassen!
Ein letzter Rat von mir: Ändern Sie regelmäßig alle Ihre Passwörter für alle Konten.
A Dutch variant of "Start The Conversation With Bad News" spam email:
Text presented within:
Subject: Vergeet niet binnen 2 dagen je belasting te betalen!
Hallo, hoe gaat het met jou?Ik weet het, het is vervelend om een gesprek te beginnen met slecht nieuws, maar ik kan niet anders.
Enkele maanden geleden heb ik toegang gekregen tot je apparaten die je gebruikt om op het internet te browsen.
Vervolgens heb ik al je internet activiteiten kunnen traceren.Hieronder kun je lezen hoe ik dit voor elkaar heb gekregen:
Allereerst heb ik van hackers de toegang tot meerdere e-mail accounts gekocht (tegenwoordig is dat een fluitje van een cent om dat online te doen).
Daarna kon ik heel makkelijk op je e-mail account (-) inloggen.Een week later heb ik een Trojan virus geïnstalleerd in de besturingssystemen van al de apparaten die je gebruikt om je mails te openen en te lezen.
Om eerlijk te zijn ging dat vrij simpel (want je opent de links uit je inbox mails).
Geniale dingen kunnen vaak zo eenvoudig zijn.Mijn software geeft me toegang tot alle besturingssystemen binnenin je apparaten, zoals microfoon, toetsenbord en videocamera.
Ik kan gemakkelijk al je privé info naar mijn servers downloaden, ook de geschiedenis van je surfgedrag en je foto's.
Ik krijg moeiteloos toegang tot al je messengers, sociale netwerk accounts, emails, contactenlijst en chatgeschiedenis.
Mijn virus blijft zijn signatures steeds vernieuwen (omdat het een driver based virus is), en blijft daardoor onopgemerkt door je antivirus software.Je snapt inmiddels denk ik wel waarom ik al die tijd onopgemerkt ben gebleven.
Terwijl ik gegevens over je aan het verzamelen was, viel me ook op dat je een nogal grote liefhebber bent van pornosites.
Je houdt er echt veel van om pornosites te bezoeken en door bedenkelijke video's te bladeren, terwijl je de hand aan jezelf slaat, om het zo maar eens te zeggen.
Het is me gelukt een paar compromitterende foto's van je te maken via je webcam en verschillende video's te monteren waarop te zien is hoe je een orgasme bereikt terwijl je er een slinger aan geeft.Mocht je nog twijfelen aan de ernst van dit alles, er zijn maar een paar muisklikken voor nodig om je video's door te sturen naar al je familieleden, en ook naar vrienden en collega's.
Ik kan die video's bovendien ook openbaar toegankelijk maken. Ik vermoed eerlijk gezegd dat je daar niet echt op zit te wachten, gezien de bijzondere aard van de video's die je graag bekijkt,
je weet zelf wel wat ik bedoel, en je weet ook dat dat je in de problemen kan brengen.We kunnen deze hele toestand voorkomen en het als volgt oplossen:
Alles wat jij hoeft te doen is een eenmalige overmaking van 1790€ naar mijn rekening (of een gelijkwaardig bedrag in bitcoin, afhankelijk van de wisselkoers op het moment van de overmaking),
en als de transactie voltooid is, verwijder ik meteen al het vunzige materiaal van jou.
Daarna mag je mij weer helemaal vergeten. Ik zweer bovendien dat alle schadelijke software ook van al je apparaten verwijderd zal worden. Maak je geen zorgen, zal mijn belofte nakomen.Dit is echt een goede deal voor een redelijke prijs, gezien het feit dat ik heel wat tijd en moeite heb gestoken in het natrekken van jou en al je dataverkeer over een langere periode.
Als je geen idee hebt hoe het kopen van bitcoin in zijn werk gaat - het is simpel en alle benodigde informatie is online te verkrijgen.Hieronder vind je mijn bitcoin wallet: 1AJcoDsSGe9teEfzSMicXprJFae7729J5y
Je moet de bovenstaande overschrijving binnen 48 uur (2 dagen) na het openen van deze e-mail uitvoeren.
De onderstaande lijst bevat dingen die je maar beter uit je hoofd kunt laten:
*Probeer niet mijn e-mail te beantwoorden (e-mail in je inbox werd door mij gegenereerd, samen met een retour mailadres).
*Probeer niet de politie in te schakelen. Deel dit verhaal ook niet met je vrienden. Nadat ik erachter kom (en dat is niet zo moeilijk,
gezien het feit dat ik de volledige controle over al je apparaten heb) - zal je pikante video meteen voor het publiek toegankelijk zijn.
*Probeer me niet te zoeken - dat heeft ook absoluut geen zin. Bovendien zijn alle transacties in cryptocurrency altijd anoniem.
*Probeer niet het OS op je apparaten opnieuw te installeren of ze weg te gooien. Dat heeft ook geen zin, want al je video's zijn al geüpload naar externe servers.De onderstaande lijst bevat dingen waar je je verder geen zorgen over moet maken:
*Dat je geld mijn rekening niet zal bereiken.
- Wees gerust, de transacties kunnen gevolgd worden, dus als de transactie voltooid is, weet ik er gelijk van,
want ik houd al je activiteiten voortdurend in de gaten (mijn trojan virus stelt me in staat je apparaten op afstand te bedienen, net als TeamViewer).
*Dat ik mijn woord niet hou en nog steeds je kinky video's aan het publiek zal delen nadat je geldtransactie voltooid is.
- Geloof me, ik heb verder geen enkele behoefte om jouw leven te verneuken. Als ik echt zou willen, had ik dat namelijk allang gedaan!Laten we deze deal op een eerlijke manier afhandelen!
Oh, nog één ding...in de toekomst kun je maar beter niet meer in dit soort situaties verzeild raken!
Dus nog een laatste advies van mij - verander regelmatig al de wachtwoorden van al je accounts.
Instant automatic malware removal:
Manual threat removal might be a lengthy and complicated process that requires advanced IT skills. Combo Cleaner is a professional automatic malware removal tool that is recommended to get rid of malware. Download it by clicking the button below:
DOWNLOAD Combo CleanerBy downloading any software listed on this website you agree to our Privacy Policy and Terms of Use. To use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
Types of malicious emails:
If you opened an attachment or downloaded a file from a suspicious email, run a full system scan with Combo Cleaner. If you only received the email and didn't engage with it, you don't need to scan anything - just identify the scam and delete it. The full procedure below covers both situations and what to do if you already clicked, replied, or sent money.
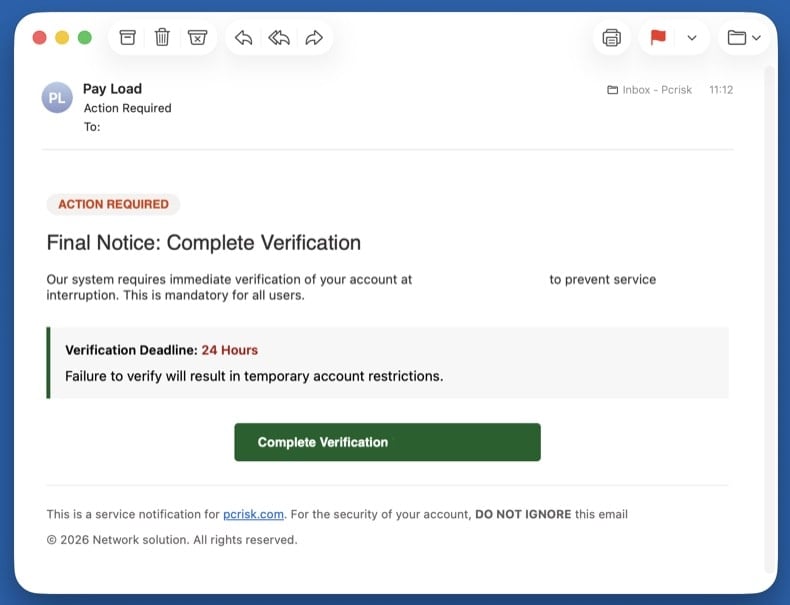
Credential theft Phishing emails
Fake login pages disguised as PayPal, Microsoft, Apple, banks, or social networks. The email pushes a link to a near-perfect copy of the real login screen. The moment you type your username and password, the attacker has them.
Common subject lines
- "Action required: confirm your account"
- "Your password expires today"
- "Unusual sign-in attempt detected"
- "Verify your billing information"
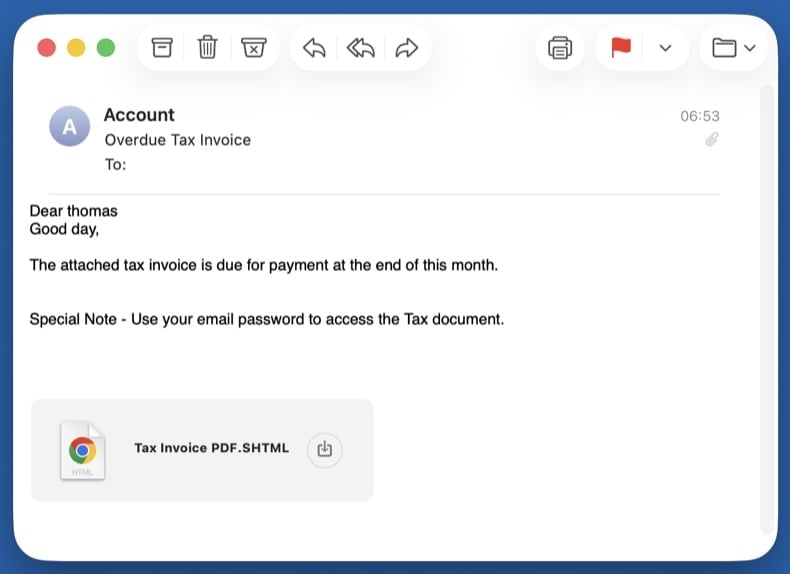
Malware delivery Emails with malicious attachments
Trojans hidden inside fake invoices, faxes, shipping confirmations, or Office documents. Opening the attachment runs the payload and infects the system - often with an info-stealer or remote-access trojan.
Common subject lines
- "Invoice INV-2026-XXXX attached"
- "Fax received - 3 pages"
- "Your shipping document is ready"
- "Voicemail from +1-XXX-XXX-XXXX"
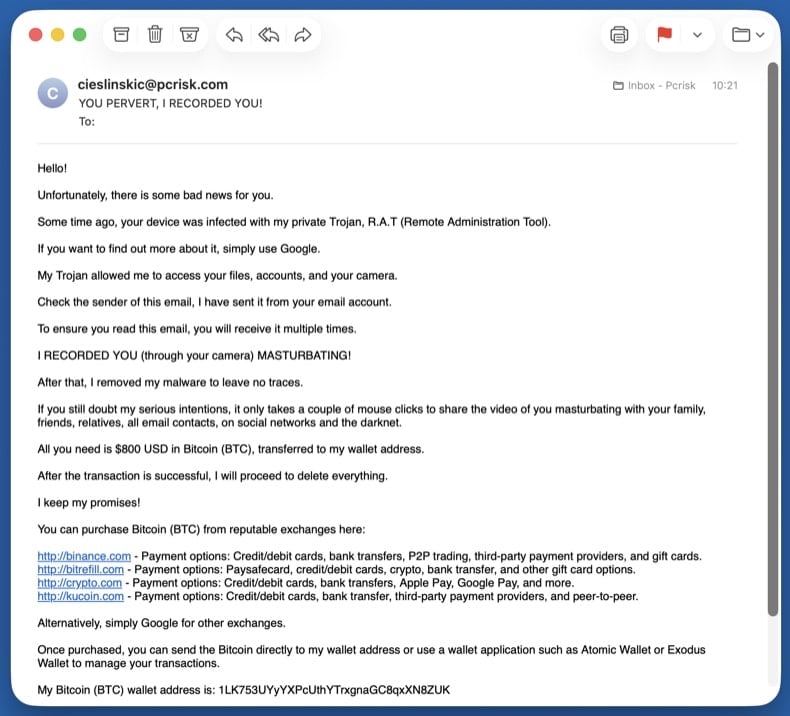
Extortion Sextortion emails
Fake claims of webcam recordings demanding cryptocurrency. Almost always a bluff: the attacker pulls a real password from an old data breach to make the threat look credible, then claims to have video of you. They have no recording and no access.
Common subject lines
- "I know your password is XXXX"
- "Your account has been hacked"
- "I have recorded you - 48 hours to pay"
- "You have been compromised"
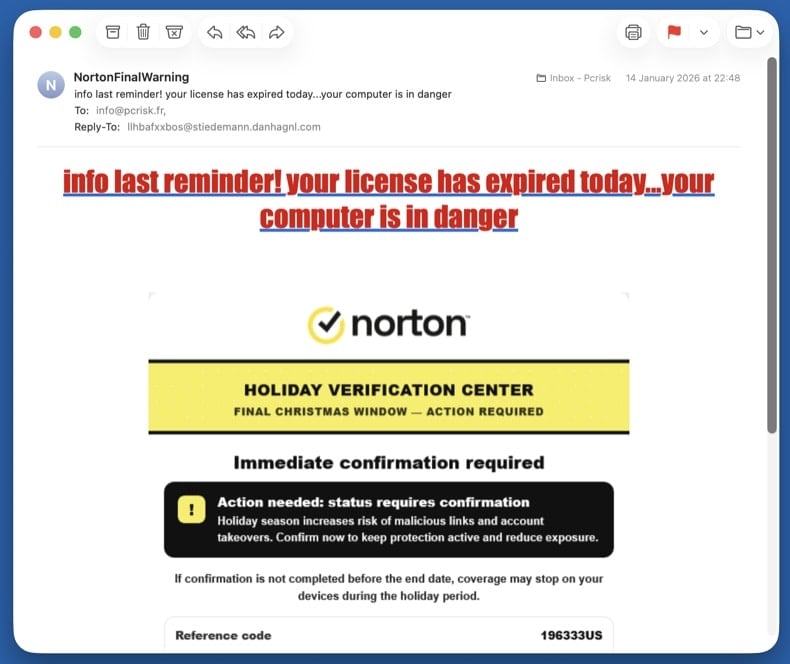
Callback fraud Refund & callback scams
"Your subscription was renewed for $499 - call to cancel." Norton, McAfee, Geek Squad, PayPal, and Wells Fargo variants are all common. There's no real subscription. The phone number in the email connects directly to the scammer, who walks you through "refunding" yourself - which is actually them stealing money from your bank.
Common subject lines
- "Norton subscription auto-renewed - $499.99"
- "McAfee Total Protection invoice"
- "Geek Squad order confirmation"
- "Your PayPal payment is being processed"
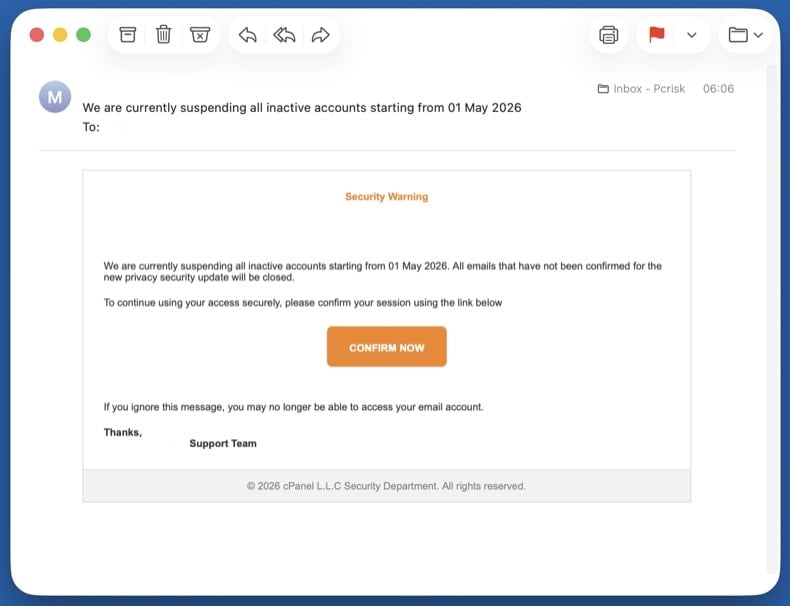
Credential theft Account suspension & verification scams
"Your account will be deleted in 24 hours - verify now." The artificial deadline is the whole point: it pressures you to click before checking details. The "verify" link goes to a phishing page styled to look like the real provider.
Common subject lines
- "Your account will be deleted in 24 hours"
- "Suspicious activity detected - verify now"
- "Final warning: account closure"
- "Action required to keep your account active"
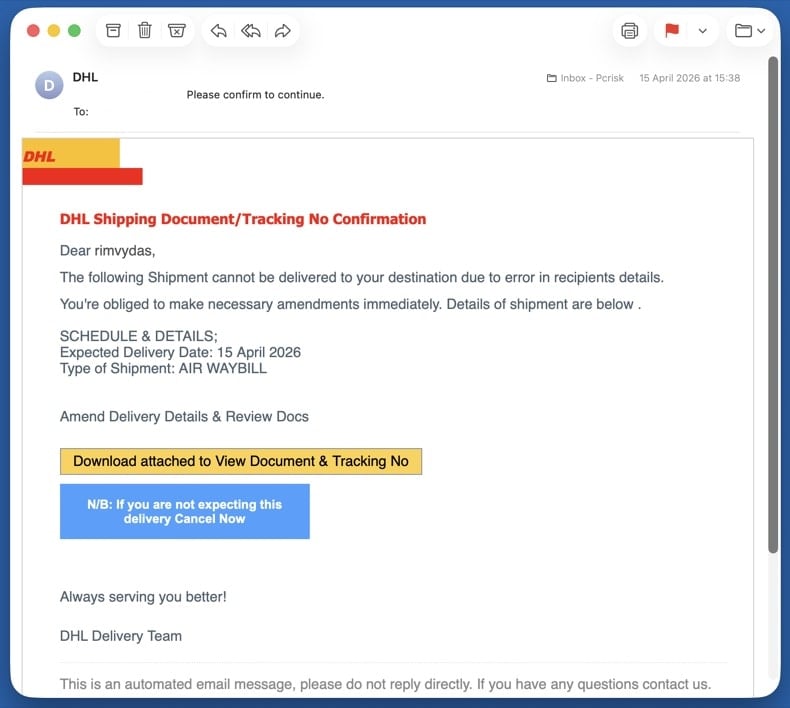
Mixed payload Delivery & package scams
Fake DHL, USPS, UPS, or FedEx tracking, customs fees, or "package undeliverable" notices. Targets anyone expecting a parcel - the timing alone catches many people. The link hides either phishing (asking for card details to "release" the package) or a malware download.
Common subject lines
- "Your DHL package is held at customs"
- "USPS - delivery attempt failed"
- "FedEx tracking update - action required"
- "Pay $2.99 redelivery fee to release your parcel"
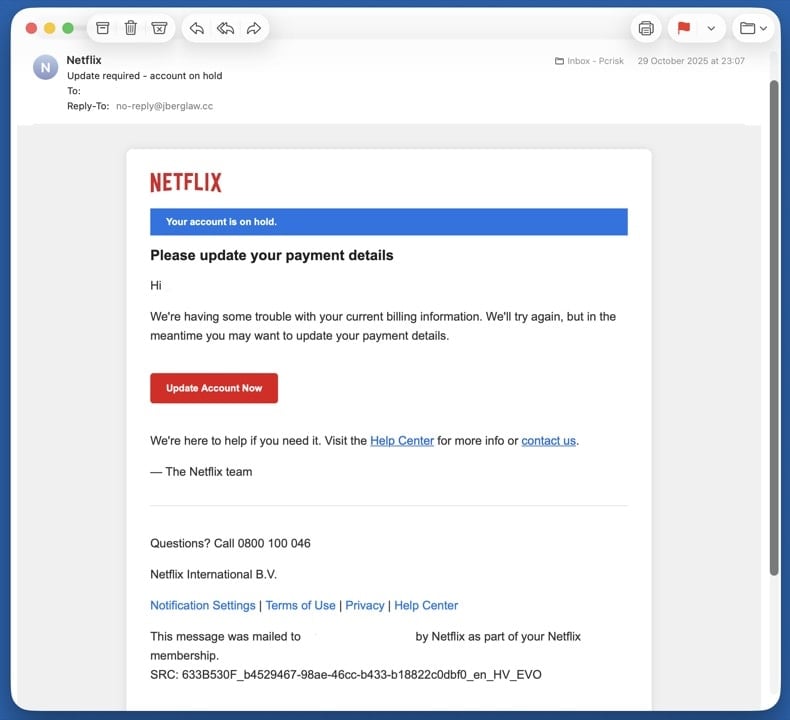
Remote access Tech support scams
Fake Microsoft, Apple, or "Windows Defender" security alerts pushing a phone number. Real Microsoft and Apple never email a phone number to call. The number connects you to a scammer who asks for remote access to "fix" the imaginary problem and then demands payment.
Common subject lines
- "Microsoft Defender expired - renew now"
- "Apple ID security alert"
- "Critical: virus detected on your PC"
- "Windows license expired - call now"
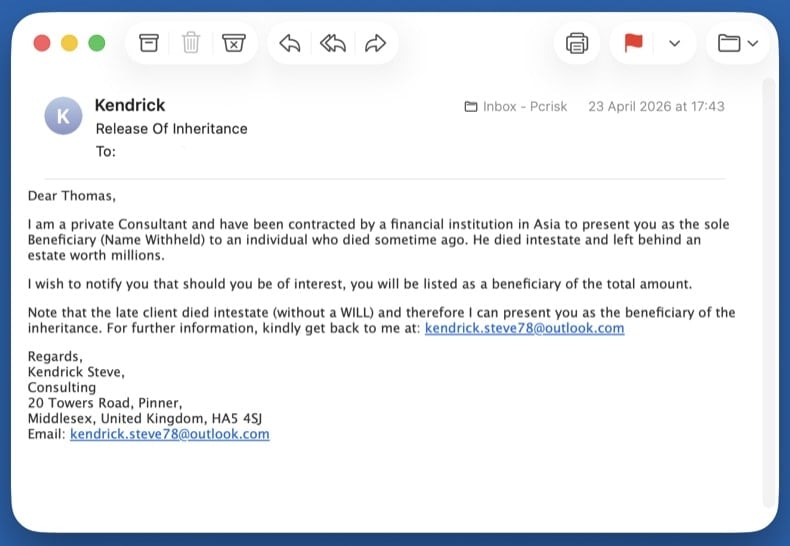
Wire fraud Advance-fee scams
Inheritance, lottery wins, romance, or business deals that ask for a small fee to release a much larger sum. The classic "Nigerian prince" 419 family of frauds. Once you pay the first fee, more fees appear (taxes, lawyer, transfer charges) until you stop paying. The promised money never exists.
Common subject lines
- "Inheritance from a relative you didn't know about"
- "You won the international lottery"
- "URGENT - business proposal worth $XX million"
- "Compensation fund release for fraud victims"
Wire fraud Business email compromise (BEC)
CEO impersonation asking employees to wire money or buy gift cards, or fake supplier invoices with newly "updated" bank details for payment redirection. The email often spoofs a real internal executive's display name and uses an external lookalike domain.
Common subject lines
- "Quick task - need you to buy gift cards"
- "Updated banking details for invoice payment"
- "Wire transfer request - urgent"
- "Are you available?" (CEO impersonation opener)
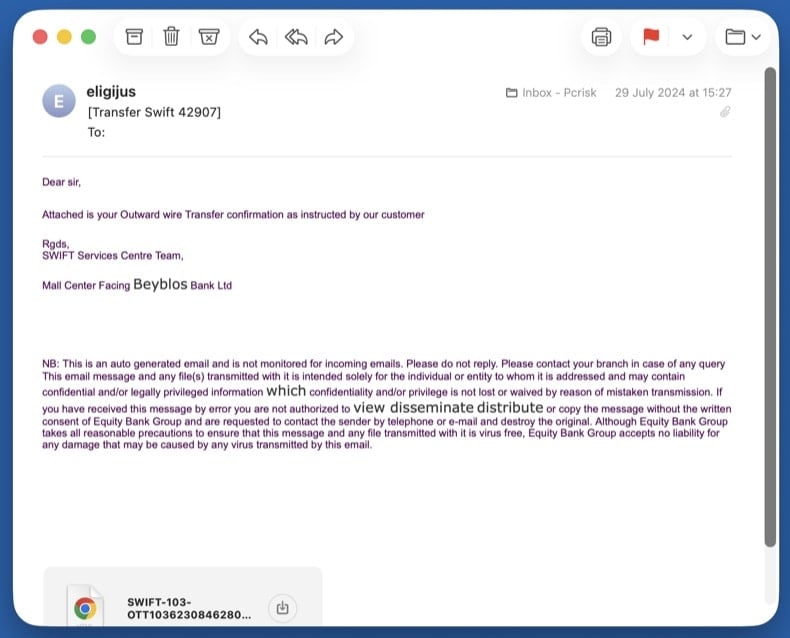
How to spot a malicious email?
Check the sender's actual address, not the display name
The display name (the human-readable part) is trivial to fake. Always check the full address that comes after it. Common red flags:
- Domain mismatch -
service@paypa1.com,support@micros0ft-help.com, look-alike domains using digits or extra hyphens - Free-email impersonation - any "official" message from a bank, courier, or platform sent from a
@gmail.com,@outlook.com, or@yahoo.comaddress - Reply-To mismatch - the From address looks legitimate but Reply-To points somewhere completely different
Real companies own their domains and send mail from them. A "DHL" message from a Gmail address is never legitimate, regardless of how convincing the body looks.
Watch for urgency, threats, and generic greetings
Scams almost always rush you. The point is to make you act before you think. Treat any of the following as a strong signal:
- "Your account will be deleted in 24 hours"
- "Final notice" / "Immediate action required"
- "Dear Customer" or "Dear User" instead of your real name
- Threats of fines, account closure, legal action, or arrest
- Promises of refunds, prizes, or money you didn't earn
- Spelling and grammar mistakes in messages claiming to come from a major brand
Hover over every link before clicking
On a desktop, hover the mouse over the link without clicking. The real destination shows in the bottom-left status bar of your browser or email client. On a phone, long-press the link to preview the URL.
- Real Microsoft, PayPal, or bank links go to those exact domains, not redirects through unrelated sites
- Shortened URLs (
bit.ly,tinyurl,t.co) hide the real destination - never click them in unsolicited mail - The visible link text and the actual URL must match - mismatches are the single biggest phishing red flag
When in doubt, don't click the link. Open a new browser tab and type the company's address yourself, then log in normally. If there really is an issue with your account, you'll see it there.
Treat unexpected attachments as hostile
If you didn't ask for the file, don't open it - even if it appears to come from someone you know. Categories that should never be opened from email without verification through another channel:
.exe,.scr,.iso,.img,.vbs,.bat- executables, never legitimate attachments.docx,.xlsx,.pptxwith "Enable macros" prompts - the macros run the malware.pdfwith "Click here to view" buttons - usually a phishing redirect, not a real document.zip,.rar,.7zarchives, especially password-protected ones - the password defeats the email scanner
If you only received the email and didn't reply, click, or open anything, the steps below are all you need. Your computer is not infected.
Don't reply, don't click "unsubscribe"
Replying confirms your address is real and monitored, which gets you added to higher-value scam lists. The "unsubscribe" link in a scam message is rarely a real opt-out - it usually leads to a phishing page or downloads a tracking pixel.
Instead, mark the message as junk or phishing inside your email client (this trains the spam filter), then block the sender.
Report the scam to your email provider and authorities
Inside your email client:
- Gmail: open the message → ⋮ menu → Report phishing
- Outlook / Outlook.com: ⋯ menu → Report → Report phishing
- Apple Mail / iCloud: Move to Junk, then forward to
reportphishing@apple.com
Forward or report to authorities:
After reporting, delete the email and empty the Trash folder so you don't accidentally open it later.
Pick the step below that matches what you did. If multiple apply, work through them in the order they appear - the steps are arranged from lowest to highest risk.
You only clicked a link (didn't enter anything or download anything)
Close the page right away. Don't enter any information, even if the page looks legitimate.
- Clear your browser cache and cookies for the last hour - → Last hour → check Cookies and Cached files
- Run a quick scan with Combo Cleaner in case the page tried to drop a file silently (drive-by download)
- Update your browser to the latest version - most drive-by exploits target outdated browsers
- Watch for new browser pop-ups, redirects, or unfamiliar notifications over the next few days
Modern browsers block most drive-by attacks, but a single click on a phishing page can still be enough on an outdated browser or unpatched plugin. A quick scan catches anything that landed silently.
You opened an attachment or downloaded a file - run a full malware scan
Opening an attachment is the most common path to actual infection. Treat the system as compromised until the scans below come back clean. Work through these sub-steps in order:
Unplug Ethernet and turn off Wi-Fi. If the attachment was an info-stealer or remote-access trojan, this stops it from sending data out or receiving commands. Keep the network off until you've booted into Safe Mode (next step) - you'll reconnect there briefly to download the scanners.
Windows 11: → Troubleshoot → Advanced options → Startup Settings → Restart → press 5 or F5.
Windows 10: hold Shift, click Power → Restart → Troubleshoot → Advanced options → Startup Settings → Restart → press F5.
Once Safe Mode has loaded, turn Wi-Fi back on and download Combo Cleaner (used in 8.4) and Microsoft Safety Scanner (used in 8.5). Safe Mode loads only minimal drivers, so most malware can't auto-run while you're getting the tools. Save both installers to your Desktop.
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts into a stripped-down environment and scans the disk before Windows fully loads - this is what catches rootkits and bootkits.
VB100 certified. Includes anti-trojan, registry/persistence scanning, and anti-spyware in one pass. The 7-day free trial is available.
Download Combo CleanerInstall Combo Cleaner and run a full system scan (not the quick scan). Let it complete fully, review what it found, and apply the recommended actions. Combo Cleaner will quarantine known trojans and remove their persistence in the registry.
Download Microsoft Safety Scanner (MSERT.exe). The binary expires every 10 days, which means every download has the latest signatures. Run a full scan after Combo Cleaner to catch anything one engine alone might miss.
Many email-borne trojans drop adware that hijacks browsers. Reset each browser you use:
Chrome: chrome://settings/reset → Restore settings to their original defaults. Then chrome://settings/content/notifications - remove unfamiliar sites.
Edge: edge://settings/reset. Then edge://settings/content/notifications.
Firefox: about:support → Refresh Firefox.
Open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all on. Then run and update browsers and applications.
If the scans keep finding new threats on each run, or files reappear after deletion, you may have a deeper compromise that needs a clean Windows reinstall. See pcrisk's full manual malware removal guide for the extended procedure (Process Explorer, Autoruns, hosts file inspection).
You entered credentials on a fake login page
Assume the attacker has your password and is using it right now. Speed matters.
- Change the password from a different, known-clean device (your phone is fine if it's not infected). Don't reuse the old password anywhere else.
- Enable two-factor authentication if you haven't already. Prefer an authenticator app or hardware key over SMS.
- Sign out of all sessions - most platforms have a "sign out everywhere" option in security settings, which kicks the attacker out.
- Review recent activity - look for unfamiliar logins, new devices, forwarding rules, or app permissions. Remove anything you don't recognize.
- Check your other accounts - if you reused that password anywhere else, change it there too. Check your exposure at haveibeenpwned.com.
- Update security questions - the attacker may have seen the answers in your account profile.
If you only have time to change one password, change your primary email password - it's the recovery hub for every other account. An attacker who controls your email can reset everything else.
You sent money or shared bank, card, or ID details
Time is the single biggest factor in recovering money. Banks can sometimes recall a wire or reverse a card transaction within the first few hours.
- Call your bank or card issuer immediately. Use the number on the back of the card, not any number from the scam email. Ask them to freeze the card, reverse the transaction if possible, and flag the account for fraud monitoring.
- If you sent a wire transfer or used a money-transfer service (Western Union, MoneyGram, Zelle, Wise), call them directly and request a recall. Some can be reversed within minutes if reported fast.
- If you sent cryptocurrency or gift cards, recovery is unlikely - but report it anyway, since law enforcement tracks these patterns.
- File a police report. You'll need the report number for any insurance, bank, or credit-bureau claim. Save the report number.
- File with the right authority for your country:
- US: ic3.gov + reportfraud.ftc.gov
- UK: reportfraud.police.uk (Report Fraud, the successor to Action Fraud; 0300 123 2040)
- Canada: antifraudcentre.ca
- Australia: scamwatch.gov.au
- EU: your national CERT or police cybercrime unit
- Set fraud alerts on all major credit bureaus if you shared any ID details. US: Equifax, Experian, TransUnion. UK: Experian, Equifax, TransUnion (Cifas Protective Registration is a stronger option).
- Save all evidence - the original email (with full headers), screenshots of the fake site, transaction records, any phone numbers or chat logs.
Final scan and startup-app check
Reconnect to the network and run one final full scan with Combo Cleaner, followed by a Windows Defender quick scan. Then open Task Manager (Ctrl + Shift + Esc) and switch to Startup apps - disable anything unfamiliar.
Make sure Windows, browsers, and any applications you use are fully up to date. The infection vector that worked on you once usually involves outdated software.
Monitor accounts and credit for 30 days
Most fraud follow-ups land in the first month. Until that window closes, keep watching:
- Bank and card statements - daily for the first week, then weekly
- Email - watch for password-reset confirmations or login alerts you didn't trigger
- Credit report - US: free at annualcreditreport.com; UK: Experian, Equifax, TransUnion all have free tiers
- Breach alerts - sign up at haveibeenpwned.com to be notified when your email appears in new leaks
If anything new appears in any of those, treat it as a continuing compromise: change passwords again, contact the bank again, and update the police report.
Important: If you didn't click anything, didn't reply, and didn't open any attachment, your computer is not infected - just delete the email and move on. If you opened an attachment or downloaded a file, run an automated scan with Combo Cleaner and Windows Defender and stop there. That path catches the vast majority of email-borne malware without the risk of breaking Windows by deleting the wrong file.
Frequently Asked Questions (FAQ)
Why did I receive this email?
Scammers behind sextortion scams (or other email scams) send the same letter to thousands of recipients. Usually, they do not target anyone in particular and use email addresses obtained from leaked databases.
Has my computer been actually hacked and does the sender have any information?
No, your computer has not been hacked, compromised, or infected. When scammers are claiming that they have hacked (or infected a computer), they are just attempting to scare victims into making a payment or performing other actions.
How did cyber criminals get my email password?
If an email contains a password, scammers have likely obtained it after a data breach. Also, scammers might have obtained a password from a phishing website where it was disclosed by other cybercriminals.
I have sent cryptocurrency to the address presented in such email, can I get my money back?
It is very unlikely. In most cases, crypto transactions are virtually untraceable, meaning that people who have been scammed cannot retrieve transferred cryptocurrency.
Is it possible to infect a computer by opening an email?
No, opening an email by itself is completely harmless. Recipients infect computers by clicking links or opening attached files.
Will Combo Cleaner remove malware infections that were present in email attachment?
Yes, Combo Cleaner can detect and eliminate almost all known malware infections. In order to remove high-end malware from infected computers, it is necessary to run a full system scan.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion