
Do not trust "Is Visiting A More Convenient Way To Reach" scam emails
Phishing/ScamAlso Known As: "Is Visiting A More Convenient Way To Reach" sextortion scam

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What kind of email is "Is Visiting A More Convenient Way To Reach"?
After reading the "Is Visiting A More Convenient Way To Reach" email, we determined that it is spam. This mail promotes a sextortion scam.
The email claims that the sender has infected the recipient's smartphone and was monitoring them. In addition to obtaining sensitive data, the sender supposedly filmed a sexually explicit video of the recipient. They threaten to leak it if they are not paid.
It must be emphasized that all the claims made by this spam mail are false. Therefore, it poses no threat to the recipients.
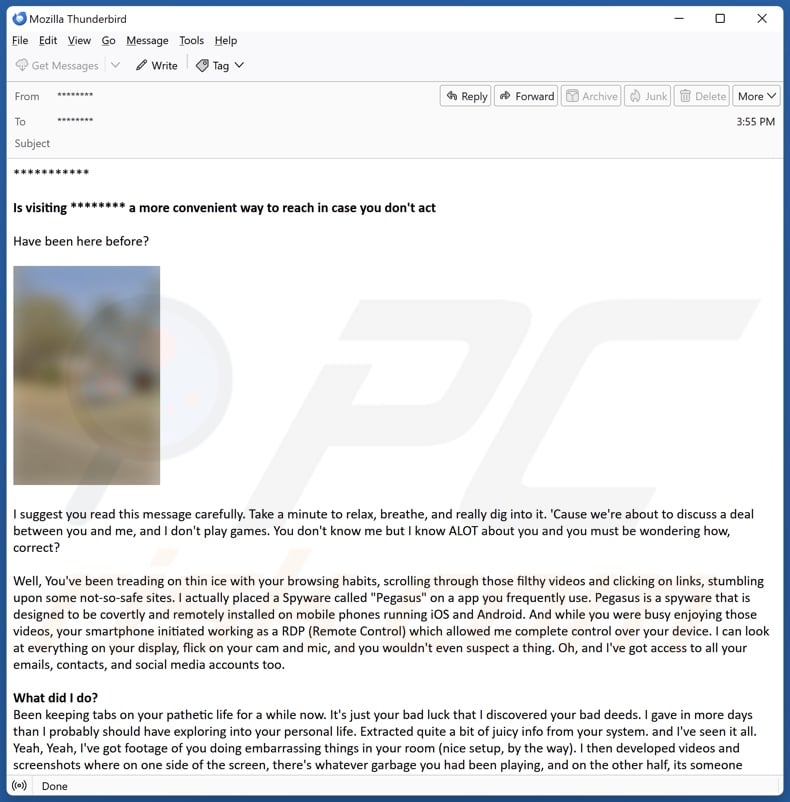
"Is Visiting A More Convenient Way To Reach" email scam overview
This spam mail accuses the recipient of having poor Internet browsing habits. The sender claims to have infected an app often used by the recipient with malware, which was then used to gain access to their Apple or Android smartphone.
The trojan was utilized to monitor the user. When they were browsing adult-oriented websites, the nonexistent malware was used to record the screen and the user.
The recipient is instructed to pay 1950 USD in Bitcoin cryptocurrency. If they refuse – the sexually explicit video of the user will be sent to their phone, email, and social media contacts. Twenty-four hours from the moment that the email was opened are given for complying with the demands.
It must be reiterated that the information in this letter is entirely false. Hence, the sender has not infected any devices with malware, nor do they have recipients' information (e.g., no videos). Therefore, all the threats made by the email are empty.
Victims of the "Is Visiting A More Convenient Way To Reach" campaign experience financial loss. Since cryptocurrency transactions are practically untraceable – they cannot be reversed, which means that victims cannot recover their funds.
| Name | "Is Visiting A More Convenient Way To Reach" sextortion scam |
| Threat Type | Phishing, Scam, Social Engineering, Fraud |
| Fake Claim | If the email sender is not paid, a sexually explicit video featuring the recipient will be sent to their contacts. |
| Cyber Criminal Cryptowallet Address | bc1q23270f3wyklqz2v2t4kh3scg7k670vd4ylw8cu, bc1qjnz6xyudwfy8f3dkprw7zjwp3tw3y9uvdz6y6j, bc1qdalm59ahv8r9hqc8cjceh6h2t0xamep04aheax, bc1qeaxp7pc44xjv68ldzxnvgel333r7xp03l640c2, 19v1ujT6yT5wpamBsHYTx7b5yVprM2pCqo, bc1qxh5zs087ls5w8fszhgl5h3ml97pcz7rjazd43a, 1NSaKPShj9t3rWVQBUit7VhBWmXUY8HHyC, 14ow9AegSM5hX7Gn8wAaF4Uhjm2Bdmk4UP, 1DeT674Vjspp377UJAdThVDjYUQPXy5TdU, 1FBdyGictLn9e25j7hsCjhzcupxQbhNwH7, 12rgJcvSswfVec6FMMmphTvXRVQNmAL6BD, 1M6Qf7LdutNL88zmfM9kE9jG2C5QWzPsBQ, 13fmUAMFGJb9mbv1zX84xcG9TwuvTxf7Hb, 1HDN178FThrkYtdnJVsfZLYUEZ7dT6UDNr, 1Pk9fyA7Ph74fX36vLKdZrHd4nNzRjcmt2 |
| Symptoms | Unauthorized online purchases, changed online account passwords, identity theft, illegal access of the computer. |
| Distribution methods | Deceptive emails, rogue online pop-up ads, search engine poisoning techniques, misspelled domains. |
| Damage | Loss of sensitive private information, monetary loss, identity theft. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
Sextortion spam campaign examples
We have written about thousands of spam campaigns; "Malware On Porn Website", "You Are One Of A Kind", "Your System Has Been Cracked", and "Internet Is A Dangerous Place" are just some of our articles on sextortion emails.
Aside from this kind of scam, spam is used to facilitate phishing, tech support, refund, inheritance, lottery, and other schemes. Deceptive mail is also used to proliferate malware.
While the commonly held belief that these emails are poorly crafted and full of grammatical/spelling errors is not untrue, it is not always the case. Spam mail can be competently crafted and even believably disguised as messages from legitimate entities (e.g., service providers, companies, institutions, authorities, etc.).
How do spam campaigns infect computers?
Spam campaigns proliferate malware by distributing malicious files. They can be attached to or linked inside the emails/messages. These files come in various formats, e.g., documents (PDF, Microsoft Office, Microsoft OneNote, etc.), archives (ZIP, RAR, etc.), executables (.exe, .run, etc.), JavaScript, and so on.
The malware download/installation chain is triggered once such a file is opened. Some formats need extra interaction to initiate system infection processes. For example, Microsoft Office files require users to enable macro commands (i.e., editing/content), while OneNote documents need them to click embedded links/files.
How to avoid installation of malware?
It is essential to exercise caution with incoming emails, DMs/PMs, SMSes, and other messages. We advise against opening attachments or links found in dubious/irrelevant mail, as they can be malicious.
It must be mentioned that malware is not spread only through spam mail. Therefore, we recommend being careful while browsing, as the Internet is rife with well-disguised fraudulent and dangerous content.
Another recommendation is to download only from official and trustworthy sources. Additionally, all programs must be activated and updated using legitimate functions/tools, as illegal product activation ("cracking") tools and third-party updaters can contain malware.
It is paramount for device integrity and user safety to have a dependable anti-virus installed and kept updated. Security software must be used to perform regular system scans and to remove threats and issues. If you've already opened malicious attachments, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate infiltrated malware.
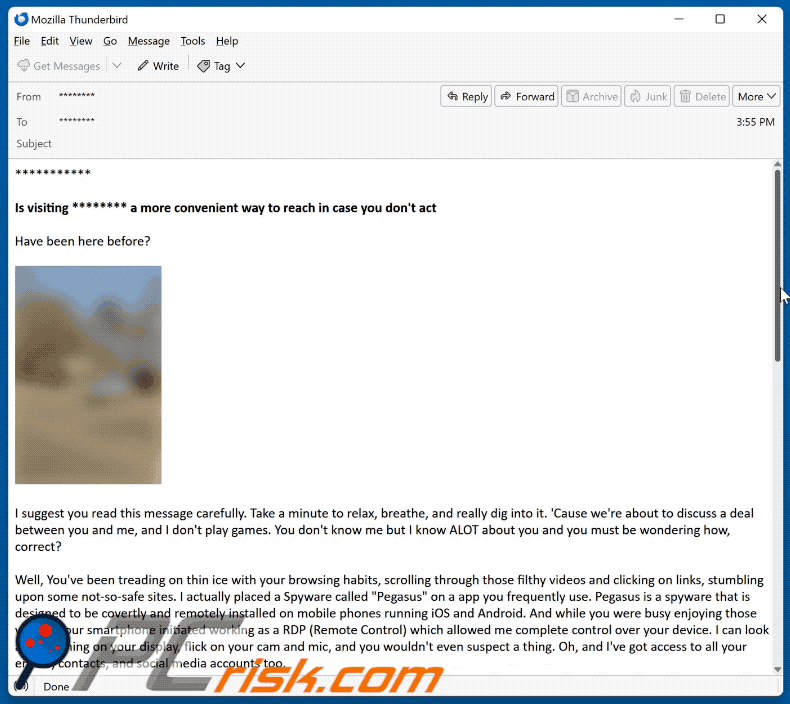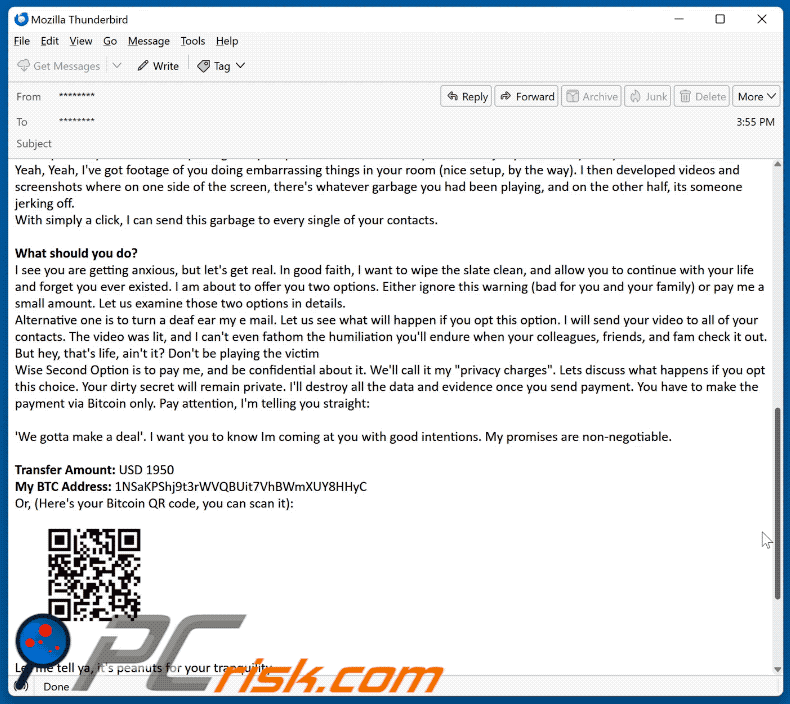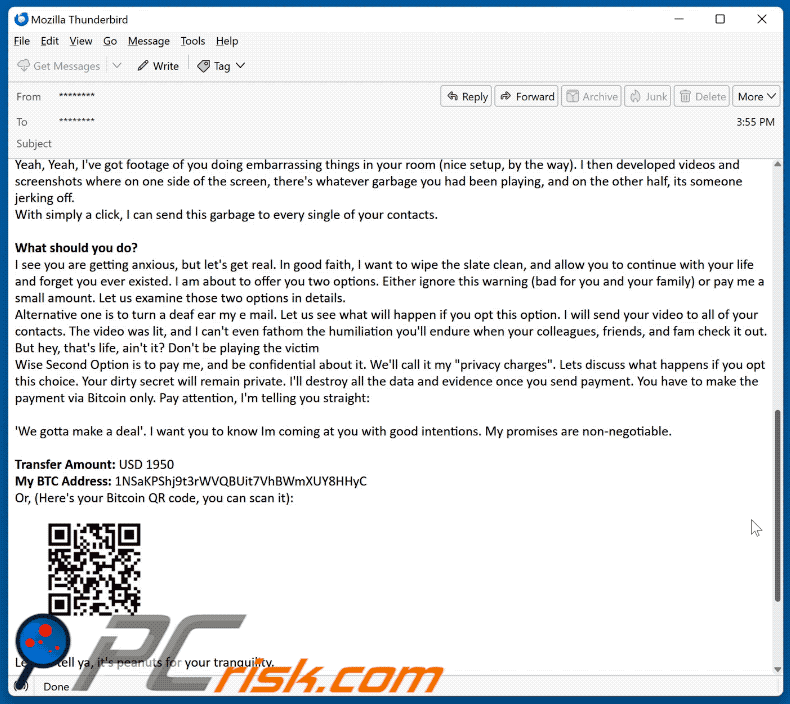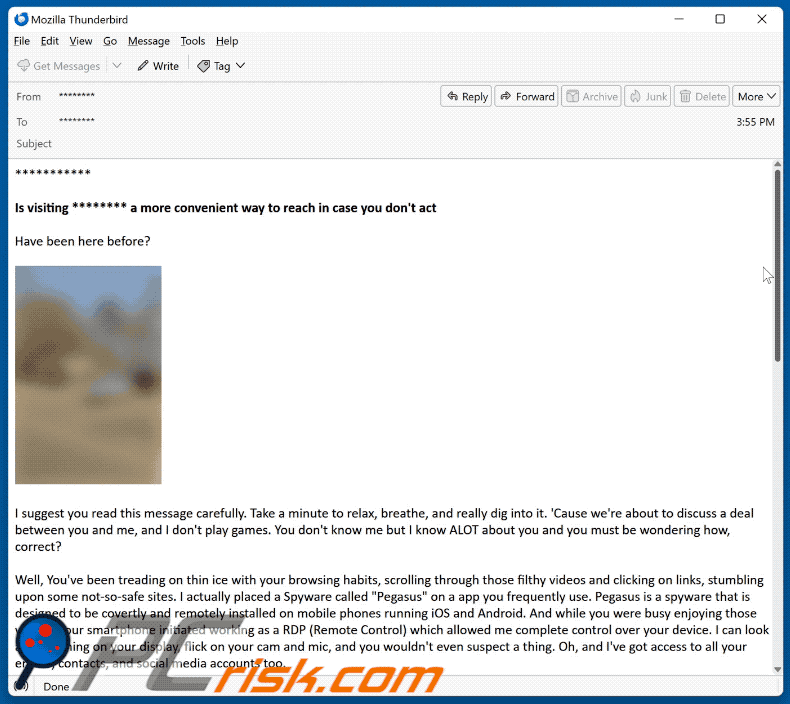
Text presented in the "Is Visiting A More Convenient Way To Reach" spam email letter:
***********
Is visiting ******** a more convenient way to reach in case you don't act
Have been here before?
I suggest you read this message carefully. Take a minute to relax, breathe, and really dig into it. 'Cause we're about to discuss a deal between you and me, and I don't play games. You don't know me but I know ALOT about you and you must be wondering how, correct?
Well, You've been treading on thin ice with your browsing habits, scrolling through those filthy videos and clicking on links, stumbling upon some not-so-safe sites. I actually placed a Spyware called "Pegasus" on a app you frequently use. Pegasus is a spyware that is designed to be covertly and remotely installed on mobile phones running iOS and Android. And while you were busy enjoying those videos, your smartphone initiated working as a RDP (Remote Control) which allowed me complete control over your device. I can look at everything on your display, flick on your cam and mic, and you wouldn't even suspect a thing. Oh, and I've got access to all your emails, contacts, and social media accounts too.
What did I do?
Been keeping tabs on your pathetic life for a while now. It's just your bad luck that I discovered your bad deeds. I gave in more days than I probably should have exploring into your personal life. Extracted quite a bit of juicy info from your system. and I've seen it all. Yeah, Yeah, I've got footage of you doing embarrassing things in your room (nice setup, by the way). I then developed videos and screenshots where on one side of the screen, there's whatever garbage you had been playing, and on the other half, its someone jerking off.
With simply a click, I can send this garbage to every single of your contacts.
What should you do?
I see you are getting anxious, but let's get real. In good faith, I want to wipe the slate clean, and allow you to continue with your life and forget you ever existed. I am about to offer you two options. Either ignore this warning (bad for you and your family) or pay me a small amount. Let us examine those two options in details.
Alternative one is to turn a deaf ear my e mail. Let us see what will happen if you opt this option. I will send your video to all of your contacts. The video was lit, and I can't even fathom the humiliation you'll endure when your colleagues, friends, and fam check it out. But hey, that's life, ain't it? Don't be playing the victim
Wise Second Option is to pay me, and be confidential about it. We'll call it my "privacy charges". Lets discuss what happens if you opt this choice. Your dirty secret will remain private. I'll destroy all the data and evidence once you send payment. You have to make the payment via Bitcoin only. Pay attention, I'm telling you straight:
'We gotta make a deal'. I want you to know Im coming at you with good intentions. My promises are non-negotiable.
Transfer Amount: USD 1950
My BTC Address: 1NSaKPShj9t3rWVQBUit7VhBWmXUY8HHyC
Or, (Here's your Bitcoin QR code, you can scan it):
Let me tell ya, it's peanuts for your tranquility.
Important: You got one day to sort this out. (I've a unique pixel within this e-mail, and right now I know that you have read this email message). My system will catch that Bitcoin payment and wipe out all the dirt I got on you. Don't even think about replying to this, it's pointless. The email and wallet are custom-made for you, untraceable. I don't make mistakes, Robert. If I suspect that you've shared or discussed this email with anyone abu, these or view is any se geting sept your contacts. And don't even think about tuming off
Honestly, those online tips about covering your camera aren't as useless as they seem.
Don't dwell on it. Take it as a little lesson and keep your guard up in the future.
Appearance of the "Is Visiting A More Convenient Way To Reach" spam email (GIF):
Other examples of emails from "Is Visiting A More Convenient Way To Reach" spam campaign:
Sample 1:
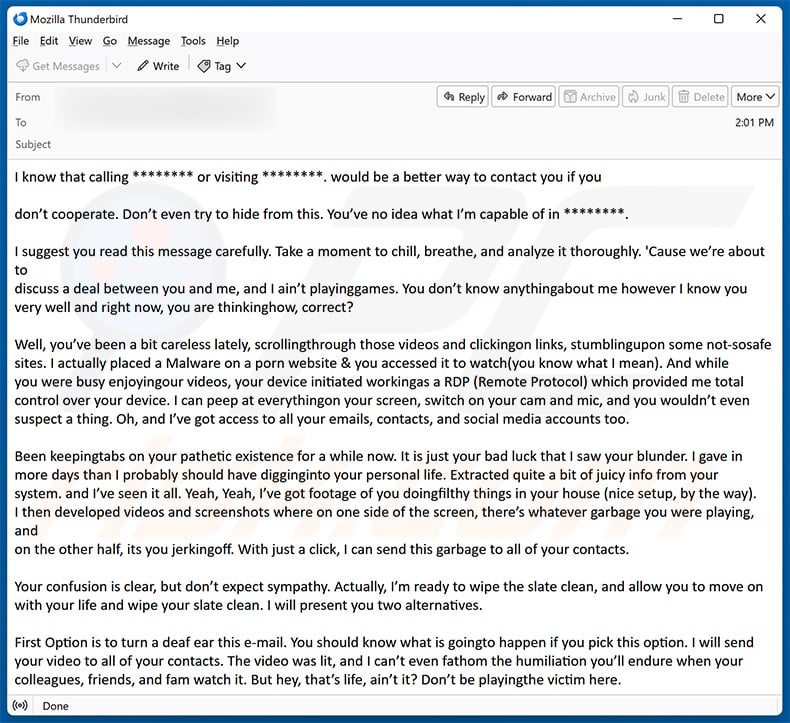
Text presented within:
I know that calling ******** or visiting ********. would be a better way to contact you if you
don’t cooperate. Don’t even try to hide from this. You’ve no idea what I’m capable of in ********.
I suggest you read this message carefully. Take a moment to chill, breathe, and analyze it thoroughly. 'Cause we’re about to
discuss a deal between you and me, and I ain’t playinggames. You don’t know anythingabout me however I know you
very well and right now, you are thinkinghow, correct?Well, you’ve been a bit careless lately, scrollingthrough those videos and clickingon links, stumblingupon some not-sosafe sites. I actually placed a Malware on a porn website & you accessed it to watch(you know what I mean). And while
you were busy enjoyingour videos, your device initiated workingas a RDP (Remote Protocol) which provided me total
control over your device. I can peep at everythingon your screen, switch on your cam and mic, and you wouldn’t even
suspect a thing. Oh, and I’ve got access to all your emails, contacts, and social media accounts too.Been keepingtabs on your pathetic existence for a while now. It is just your bad luck that I saw your blunder. I gave in
more days than I probably should have digginginto your personal life. Extracted quite a bit of juicy info from your
system. and I’ve seen it all. Yeah, Yeah, I’ve got footage of you doingfilthy things in your house (nice setup, by the way).
I then developed videos and screenshots where on one side of the screen, there’s whatever garbage you were playing, and
on the other half, its you jerkingoff. With just a click, I can send this garbage to all of your contacts.Your confusion is clear, but don’t expect sympathy. Actually, I’m ready to wipe the slate clean, and allow you to move on
with your life and wipe your slate clean. I will present you two alternatives.First Option is to turn a deaf ear this e-mail. You should know what is goingto happen if you pick this option. I will send
your video to all of your contacts. The video was lit, and I can’t even fathom the humiliation you’ll endure when your
colleagues, friends, and fam watch it. But hey, that’s life, ain’t it? Don’t be playingthe victim here.Second option is to pay me, and be confidential about it. We’ll call this my “confidentiality charges”. let me tell you what
will happen when you opt this choice. Your filthy secret remains private. I will wipe everythingclean once you send
payment. You have to make the payment via Bitcoin only. Pay attention, I’m tellingyou straight: ‘We gotta make a deal’. I
want you to know I’m comingat you with good intentions. I will keep my end of the bargain.Amount to be sent: $1950
BITCOIN ADDRESS IS: 14ow9AegSM5hX7Gn8wAaF4Uhjm2Bdmk4UPLet me tell ya, it’s peanuts for your tranquility.
Notice: You got one day to sort this out and I will only accept Bitcoins (I’ve a specific pixel within this e-mail, and right
now I know that you have read through this email message). My system will catch that Bitcoin payment and wipe out all
the dirt I got on you. Don’t even think about replyingto this or negotiating, it’s pointless. The email and wallet are
custom-made for you, untraceable. If I suspect that you’ve shared or discussed this email with anyone else, your shitty
video will instantly start gettingsent to your contacts. And don’t even think about turningoff your phone or resettingit to
factory settings. It’s pointless. I don’t make mistakes, ********.Can you notice somethinghere?
-
Honestly, those online tips about coveringyour camera aren’t as useless as they seem. I am waitingfor my payment…
Sample 2:
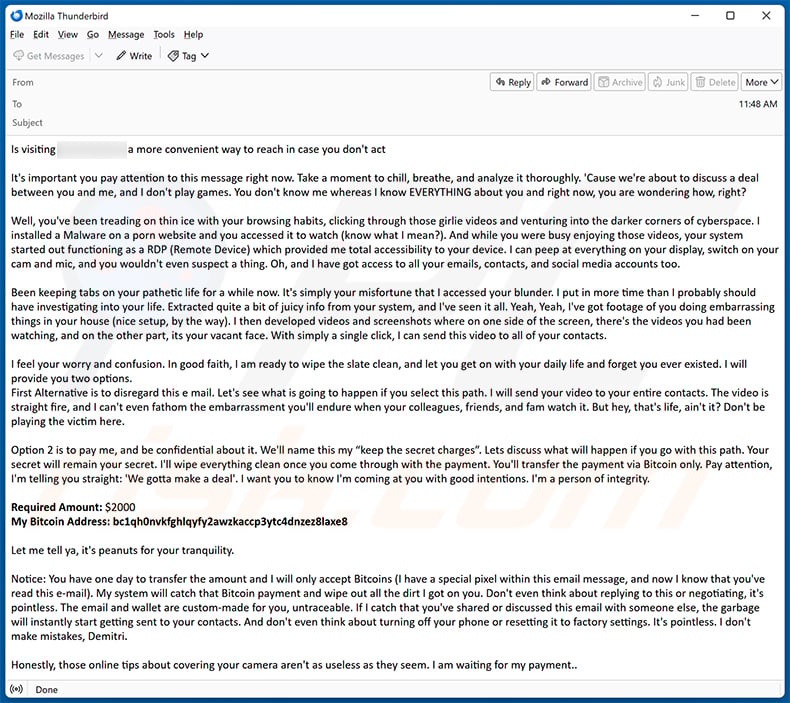
Text presented within:
Is visiting ******** a more convenient way to reach in case you don't act
It's important you pay attention to this message right now. Take a moment to chill, breathe, and analyze it thoroughly. 'Cause we're about to discuss a deal between you and me, and I don't play games. You don't know me whereas I know EVERYTHING about you and right now, you are wondering how, right?
Well, you've been treading on thin ice with your browsing habits, clicking through those girlie videos and venturing into the darker corners of cyberspace. I installed a Malware on a porn website and you accessed it to watch (know what I mean?). And while you were busy enjoying those videos, your system started out functioning as a RDP (Remote Device) which provided me total accessibility to your device. I can peep at everything on your display, switch on your cam and mic, and you wouldn't even suspect a thing. Oh, and I have got access to all your emails, contacts, and social media accounts too.
Been keeping tabs on your pathetic life for a while now. It's simply your misfortune that I accessed your blunder. I put in more time than I probably should have investigating into your life. Extracted quite a bit of juicy info from your system, and I've seen it all. Yeah, Yeah, I've got footage of you doing embarrassing things in your house (nice setup, by the way). I then developed videos and screenshots where on one side of the screen, there's the videos you had been watching, and on the other part, its your vacant face. With simply a single click, I can send this video to all of your contacts.
I feel your worry and confusion. In good faith, I am ready to wipe the slate clean, and let you get on with your daily life and forget you ever existed. I will provide you two options.
First Alternative is to disregard this e mail. Let's see what is going to happen if you select this path. I will send your video to your entire contacts. The video is straight fire, and I can't even fathom the embarrassment you'll endure when your colleagues, friends, and fam watch it. But hey, that's life, ain't it? Don't be playing the victim here.
Option 2 is to pay me, and be confidential about it. We'll name this my “keep the secret charges”. Lets discuss what will happen if you go with this path. Your secret will remain your secret. I'll wipe everything clean once you come through with the payment. You'll transfer the payment via Bitcoin only. Pay attention, I'm telling you straight: 'We gotta make a deal'. I want you to know I'm coming at you with good intentions. I'm a person of integrity.
Required Amount: $2000
My Bitcoin Address: bc1qh0nvkfghlqyfy2awzkaccp3ytc4dnzez8laxe8
Let me tell ya, it's peanuts for your tranquility.
Notice: You have one day to transfer the amount and I will only accept Bitcoins (I have a special pixel within this email message, and now I know that you've read this e-mail). My system will catch that Bitcoin payment and wipe out all the dirt I got on you. Don't even think about replying to this or negotiating, it's pointless. The email and wallet are custom-made for you, untraceable. If I catch that you've shared or discussed this email with someone else, the garbage will instantly start getting sent to your contacts. And don't even think about turning off your phone or resetting it to factory settings. It's pointless. I don't make mistakes, -.
Honestly, those online tips about covering your camera aren't as useless as they seem. I am waiting for my payment..
Sample 3:
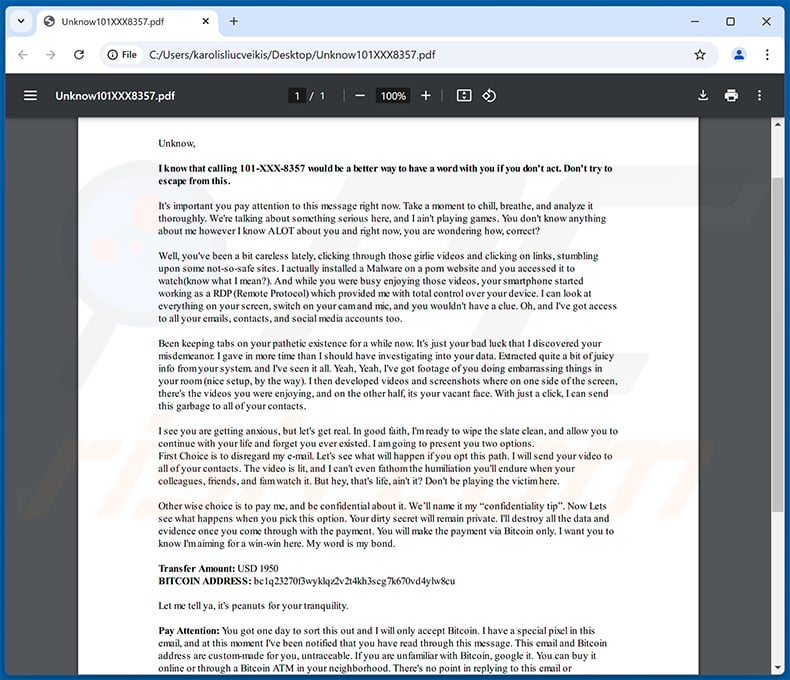
Text presented within:
Unknow,
I knowthat calling 101-XXX-8357 would be a better way to have a wordwith you if you don't act. Don't try to
escape from this.
It's important you pay attention to this message right now. Take a moment to chill, breathe, and analyze it
thoroughly. We're talking about something serious here, and I ain't playing games. You don't know anything
about me however I know ALOT about you and right now, you are wondering how, correct?
Well, you've been a bit careless lately, clicking through those girlie videos and clicking on links, stumbling
upon some not-so-safe sites. I actually installed a Malware on a porn website and you accessed it to
watch(know what I mean?). And while you were busy enjoying those videos, your smartphone started
working as a RDP (Remote Protocol) which provided me with total control over your device. I can look at
everything on your screen, switch on your camand mic, and you wouldn't have a clue. Oh, and I've got access
to all your emails, contacts, and social media accounts too.
Been keeping tabs on your pathetic existence for a while now. It's just your bad luck that I discovered your
misdemeanor. I gave in more time than I should have investigating into your data. Extracted quite a bit of juicy
info fromyour system. and I've seen it all. Yeah, Yeah, I've got footage of you doing embarrassing things in
your room(nice setup, by the way). I then developed videos and screenshots where on one side of the screen,
there's the videos you were enjoying, and on the other half, its your vacant face. With just a click, I can send
this garbage to all of your contacts.
I see you are getting anxious, but let's get real. In good faith, I'mready to wipe the slate clean, and allow you to
continue with your life and forget you ever existed. I amgoing to present you two options.
First Choice is to disregard my e-mail. Let's see what will happen if you opt this path. I willsend your video to
all of your contacts. The video is lit, and I can't even fathomthe humiliation you'll endure when your
colleagues, friends, and famwatch it. But hey, that's life, ain't it? Don't be playing the victimhere.
Other wise choice is to pay me, and be confidential about it. We’ll name it my “confidentiality tip”. Now Lets
see what happens when you pick this option. Your dirty secret will remain private. I'll destroy all the data and
evidence once you come through with the payment. You will make the payment via Bitcoin only. I want you to
know I'maiming for a win-win here. My word is my bond.
Transfer Amount: USD 1950
BITCOIN ADDRESS: bc1q23270f3wyklqz2v2t4kh3scg7k670vd4ylw8cu
Let me tell ya, it's peanuts for your tranquility.
Pay Attention: You got one day to sort this out and I will only accept Bitcoin. I have a special pixel in this
email, and at this moment I've been notified that you have read through this message. This email and Bitcoin
address are custom-made for you, untraceable. If you are unfamiliar with Bitcoin, google it. You can buy it
online or through a Bitcoin ATM in your neighborhood. There's no point in replying to this email or
negotiating, it's pointless my price is fixed. As soon as you send the complete payment, my systemwill inform
me and I will wipe out all the dirt I got on you. Remember if I notice that you've shared or discussed this
message with someone else, the sh**y video will instantly start getting sent to your contacts and I will post a
physical tape to all of your neighborhood next week. And don't even think about turning off your phone or
resetting it to factory settings, I already have all your data. I don't make mistakes, Unknow.
Honestly, those online tips about covering your camera aren't as useless as they seem. Now, I amwaiting for
my payment..
Instant automatic malware removal:
Manual threat removal might be a lengthy and complicated process that requires advanced IT skills. Combo Cleaner is a professional automatic malware removal tool that is recommended to get rid of malware. Download it by clicking the button below:
DOWNLOAD Combo CleanerBy downloading any software listed on this website you agree to our Privacy Policy and Terms of Use. To use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
Types of malicious emails:
If you opened an attachment or downloaded a file from a suspicious email, run a full system scan with Combo Cleaner. If you only received the email and didn't engage with it, you don't need to scan anything - just identify the scam and delete it. The full procedure below covers both situations and what to do if you already clicked, replied, or sent money.
Credential theft Phishing emails
Fake login pages disguised as PayPal, Microsoft, Apple, banks, or social networks. The email pushes a link to a near-perfect copy of the real login screen. The moment you type your username and password, the attacker has them.
Common subject lines
- "Action required: confirm your account"
- "Your password expires today"
- "Unusual sign-in attempt detected"
- "Verify your billing information"
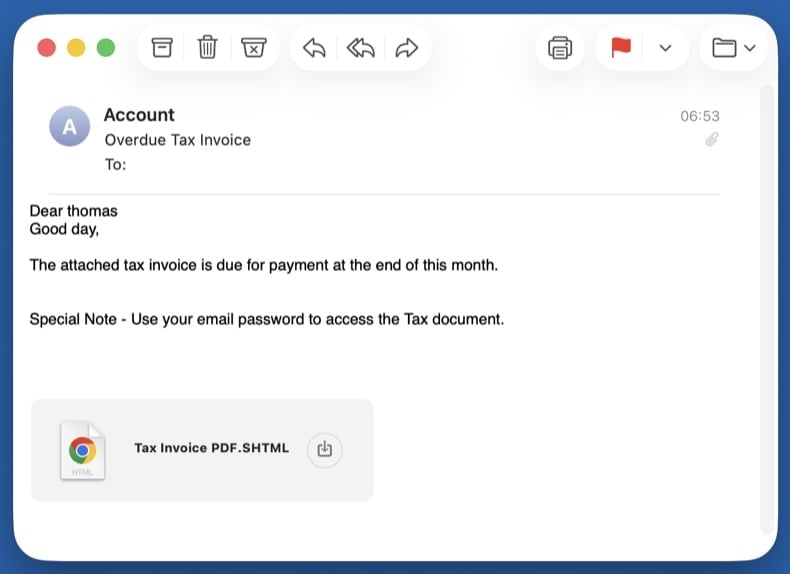
Malware delivery Emails with malicious attachments
Trojans hidden inside fake invoices, faxes, shipping confirmations, or Office documents. Opening the attachment runs the payload and infects the system - often with an info-stealer or remote-access trojan.
Common subject lines
- "Invoice INV-2026-XXXX attached"
- "Fax received - 3 pages"
- "Your shipping document is ready"
- "Voicemail from +1-XXX-XXX-XXXX"
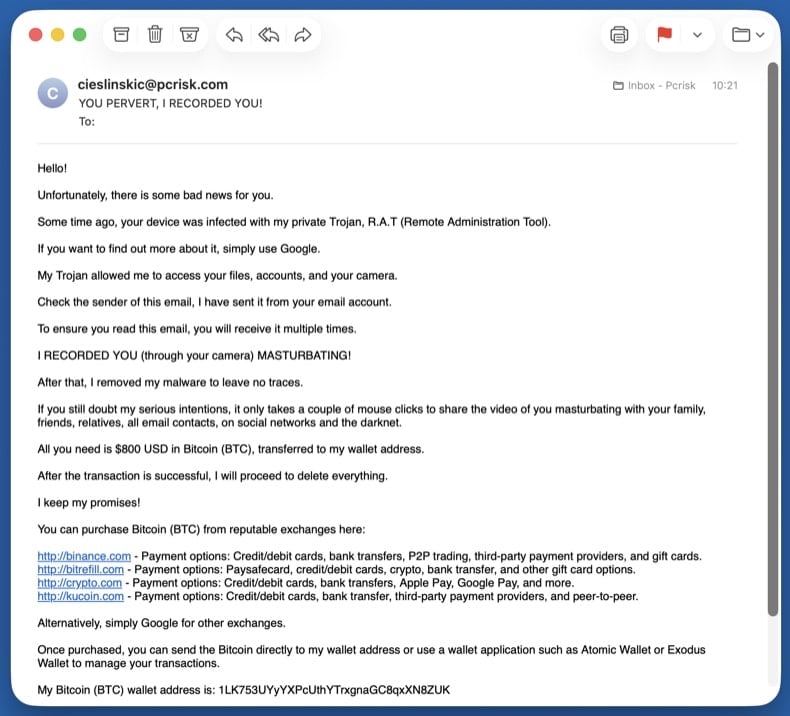
Extortion Sextortion emails
Fake claims of webcam recordings demanding cryptocurrency. Almost always a bluff: the attacker pulls a real password from an old data breach to make the threat look credible, then claims to have video of you. They have no recording and no access.
Common subject lines
- "I know your password is XXXX"
- "Your account has been hacked"
- "I have recorded you - 48 hours to pay"
- "You have been compromised"
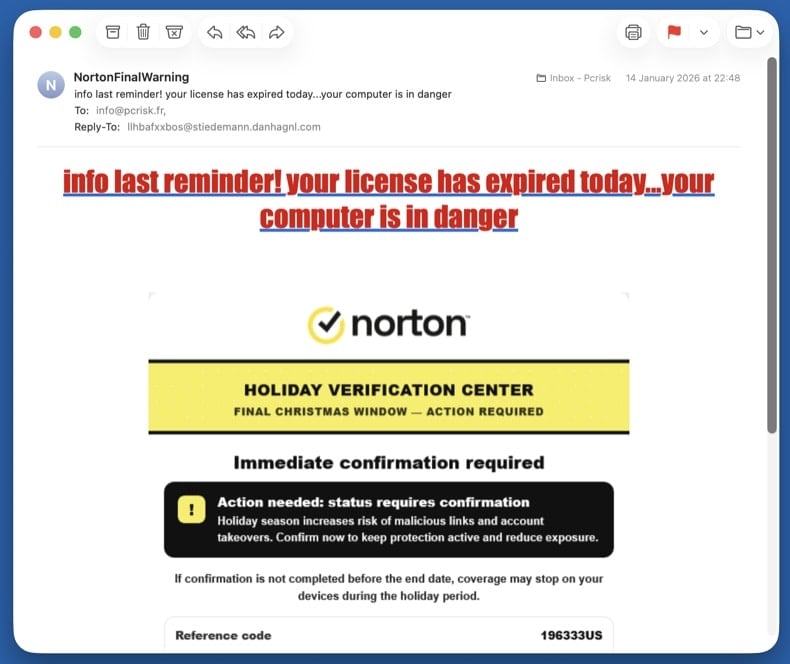
Callback fraud Refund & callback scams
"Your subscription was renewed for $499 - call to cancel." Norton, McAfee, Geek Squad, PayPal, and Wells Fargo variants are all common. There's no real subscription. The phone number in the email connects directly to the scammer, who walks you through "refunding" yourself - which is actually them stealing money from your bank.
Common subject lines
- "Norton subscription auto-renewed - $499.99"
- "McAfee Total Protection invoice"
- "Geek Squad order confirmation"
- "Your PayPal payment is being processed"
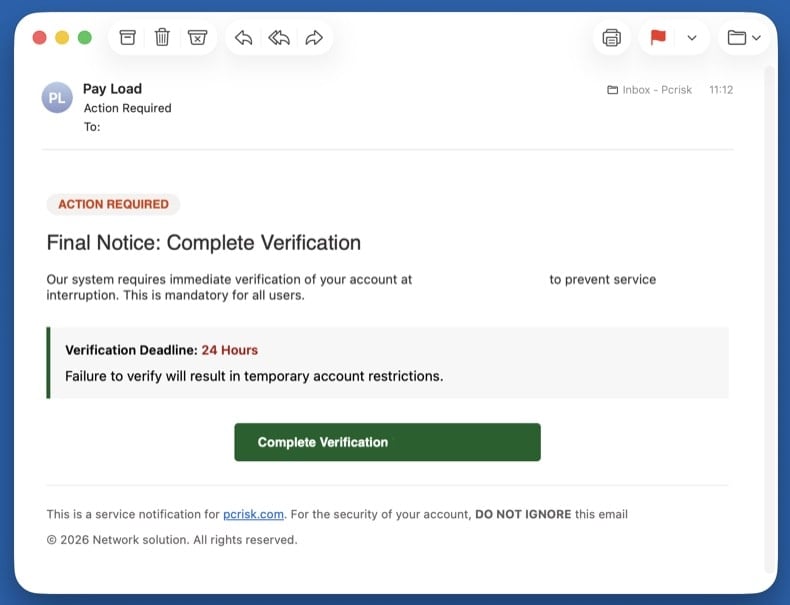
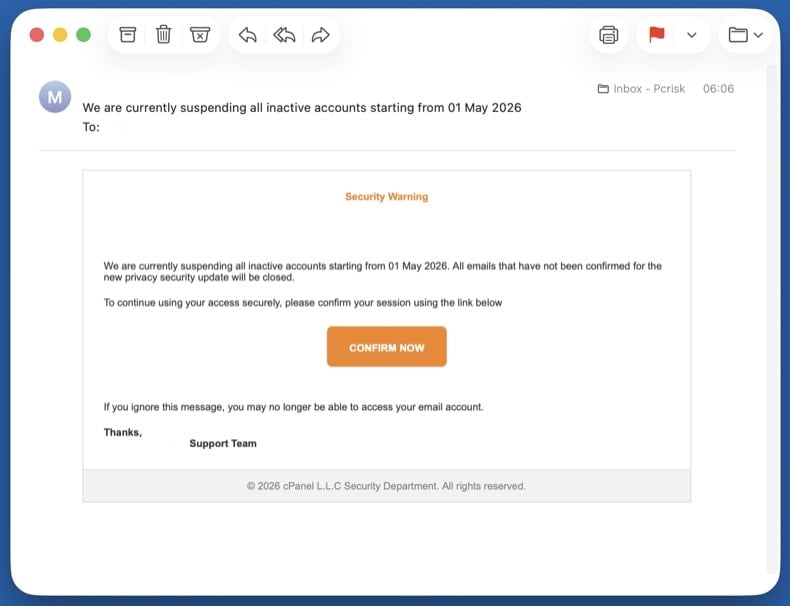
Credential theft Account suspension & verification scams
"Your account will be deleted in 24 hours - verify now." The artificial deadline is the whole point: it pressures you to click before checking details. The "verify" link goes to a phishing page styled to look like the real provider.
Common subject lines
- "Your account will be deleted in 24 hours"
- "Suspicious activity detected - verify now"
- "Final warning: account closure"
- "Action required to keep your account active"
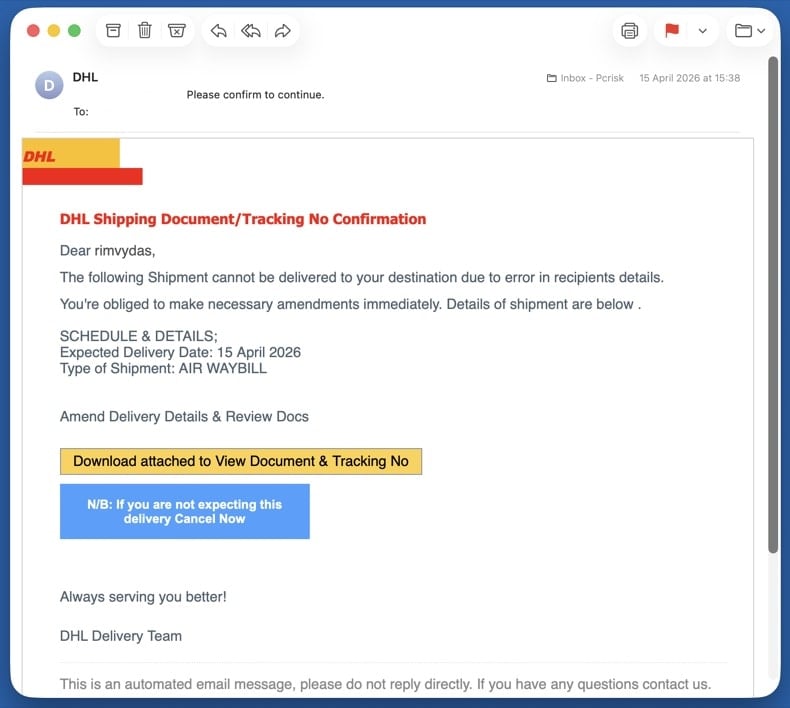
Mixed payload Delivery & package scams
Fake DHL, USPS, UPS, or FedEx tracking, customs fees, or "package undeliverable" notices. Targets anyone expecting a parcel - the timing alone catches many people. The link hides either phishing (asking for card details to "release" the package) or a malware download.
Common subject lines
- "Your DHL package is held at customs"
- "USPS - delivery attempt failed"
- "FedEx tracking update - action required"
- "Pay $2.99 redelivery fee to release your parcel"
Remote access Tech support scams
Fake Microsoft, Apple, or "Windows Defender" security alerts pushing a phone number. Real Microsoft and Apple never email a phone number to call. The number connects you to a scammer who asks for remote access to "fix" the imaginary problem and then demands payment.
Common subject lines
- "Microsoft Defender expired - renew now"
- "Apple ID security alert"
- "Critical: virus detected on your PC"
- "Windows license expired - call now"
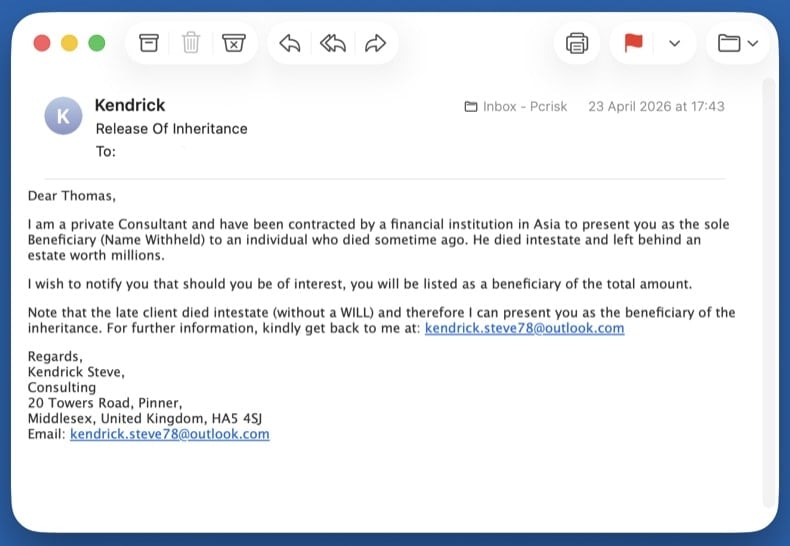
Wire fraud Advance-fee scams
Inheritance, lottery wins, romance, or business deals that ask for a small fee to release a much larger sum. The classic "Nigerian prince" 419 family of frauds. Once you pay the first fee, more fees appear (taxes, lawyer, transfer charges) until you stop paying. The promised money never exists.
Common subject lines
- "Inheritance from a relative you didn't know about"
- "You won the international lottery"
- "URGENT - business proposal worth $XX million"
- "Compensation fund release for fraud victims"
Wire fraud Business email compromise (BEC)
CEO impersonation asking employees to wire money or buy gift cards, or fake supplier invoices with newly "updated" bank details for payment redirection. The email often spoofs a real internal executive's display name and uses an external lookalike domain.
Common subject lines
- "Quick task - need you to buy gift cards"
- "Updated banking details for invoice payment"
- "Wire transfer request - urgent"
- "Are you available?" (CEO impersonation opener)
How to spot a malicious email?
Check the sender's actual address, not the display name
The display name (the human-readable part) is trivial to fake. Always check the full address that comes after it. Common red flags:
- Domain mismatch -
service@paypa1.com,support@micros0ft-help.com, look-alike domains using digits or extra hyphens - Free-email impersonation - any "official" message from a bank, courier, or platform sent from a
@gmail.com,@outlook.com, or@yahoo.comaddress - Reply-To mismatch - the From address looks legitimate but Reply-To points somewhere completely different
Real companies own their domains and send mail from them. A "DHL" message from a Gmail address is never legitimate, regardless of how convincing the body looks.
Watch for urgency, threats, and generic greetings
Scams almost always rush you. The point is to make you act before you think. Treat any of the following as a strong signal:
- "Your account will be deleted in 24 hours"
- "Final notice" / "Immediate action required"
- "Dear Customer" or "Dear User" instead of your real name
- Threats of fines, account closure, legal action, or arrest
- Promises of refunds, prizes, or money you didn't earn
- Spelling and grammar mistakes in messages claiming to come from a major brand
Hover over every link before clicking
On a desktop, hover the mouse over the link without clicking. The real destination shows in the bottom-left status bar of your browser or email client. On a phone, long-press the link to preview the URL.
- Real Microsoft, PayPal, or bank links go to those exact domains, not redirects through unrelated sites
- Shortened URLs (
bit.ly,tinyurl,t.co) hide the real destination - never click them in unsolicited mail - The visible link text and the actual URL must match - mismatches are the single biggest phishing red flag
When in doubt, don't click the link. Open a new browser tab and type the company's address yourself, then log in normally. If there really is an issue with your account, you'll see it there.
Treat unexpected attachments as hostile
If you didn't ask for the file, don't open it - even if it appears to come from someone you know. Categories that should never be opened from email without verification through another channel:
.exe,.scr,.iso,.img,.vbs,.bat- executables, never legitimate attachments.docx,.xlsx,.pptxwith "Enable macros" prompts - the macros run the malware.pdfwith "Click here to view" buttons - usually a phishing redirect, not a real document.zip,.rar,.7zarchives, especially password-protected ones - the password defeats the email scanner
If you only received the email and didn't reply, click, or open anything, the steps below are all you need. Your computer is not infected.
Don't reply, don't click "unsubscribe"
Replying confirms your address is real and monitored, which gets you added to higher-value scam lists. The "unsubscribe" link in a scam message is rarely a real opt-out - it usually leads to a phishing page or downloads a tracking pixel.
Instead, mark the message as junk or phishing inside your email client (this trains the spam filter), then block the sender.
Report the scam to your email provider and authorities
Inside your email client:
- Gmail: open the message → ⋮ menu → Report phishing
- Outlook / Outlook.com: ⋯ menu → Report → Report phishing
- Apple Mail / iCloud: Move to Junk, then forward to
reportphishing@apple.com
Forward or report to authorities:
After reporting, delete the email and empty the Trash folder so you don't accidentally open it later.
Pick the step below that matches what you did. If multiple apply, work through them in the order they appear - the steps are arranged from lowest to highest risk.
You only clicked a link (didn't enter anything or download anything)
Close the page right away. Don't enter any information, even if the page looks legitimate.
- Clear your browser cache and cookies for the last hour - → Last hour → check Cookies and Cached files
- Run a quick scan with Combo Cleaner in case the page tried to drop a file silently (drive-by download)
- Update your browser to the latest version - most drive-by exploits target outdated browsers
- Watch for new browser pop-ups, redirects, or unfamiliar notifications over the next few days
Modern browsers block most drive-by attacks, but a single click on a phishing page can still be enough on an outdated browser or unpatched plugin. A quick scan catches anything that landed silently.
You opened an attachment or downloaded a file - run a full malware scan
Opening an attachment is the most common path to actual infection. Treat the system as compromised until the scans below come back clean. Work through these sub-steps in order:
Unplug Ethernet and turn off Wi-Fi. If the attachment was an info-stealer or remote-access trojan, this stops it from sending data out or receiving commands. Keep the network off until you've booted into Safe Mode (next step) - you'll reconnect there briefly to download the scanners.
Windows 11: → Troubleshoot → Advanced options → Startup Settings → Restart → press 5 or F5.
Windows 10: hold Shift, click Power → Restart → Troubleshoot → Advanced options → Startup Settings → Restart → press F5.
Once Safe Mode has loaded, turn Wi-Fi back on and download Combo Cleaner (used in 8.4) and Microsoft Safety Scanner (used in 8.5). Safe Mode loads only minimal drivers, so most malware can't auto-run while you're getting the tools. Save both installers to your Desktop.
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts into a stripped-down environment and scans the disk before Windows fully loads - this is what catches rootkits and bootkits.
VB100 certified. Includes anti-trojan, registry/persistence scanning, and anti-spyware in one pass. The 7-day free trial is available.
Download Combo CleanerInstall Combo Cleaner and run a full system scan (not the quick scan). Let it complete fully, review what it found, and apply the recommended actions. Combo Cleaner will quarantine known trojans and remove their persistence in the registry.
Download Microsoft Safety Scanner (MSERT.exe). The binary expires every 10 days, which means every download has the latest signatures. Run a full scan after Combo Cleaner to catch anything one engine alone might miss.
Many email-borne trojans drop adware that hijacks browsers. Reset each browser you use:
Chrome: chrome://settings/reset → Restore settings to their original defaults. Then chrome://settings/content/notifications - remove unfamiliar sites.
Edge: edge://settings/reset. Then edge://settings/content/notifications.
Firefox: about:support → Refresh Firefox.
Open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all on. Then run and update browsers and applications.
If the scans keep finding new threats on each run, or files reappear after deletion, you may have a deeper compromise that needs a clean Windows reinstall. See pcrisk's full manual malware removal guide for the extended procedure (Process Explorer, Autoruns, hosts file inspection).
You entered credentials on a fake login page
Assume the attacker has your password and is using it right now. Speed matters.
- Change the password from a different, known-clean device (your phone is fine if it's not infected). Don't reuse the old password anywhere else.
- Enable two-factor authentication if you haven't already. Prefer an authenticator app or hardware key over SMS.
- Sign out of all sessions - most platforms have a "sign out everywhere" option in security settings, which kicks the attacker out.
- Review recent activity - look for unfamiliar logins, new devices, forwarding rules, or app permissions. Remove anything you don't recognize.
- Check your other accounts - if you reused that password anywhere else, change it there too. Check your exposure at haveibeenpwned.com.
- Update security questions - the attacker may have seen the answers in your account profile.
If you only have time to change one password, change your primary email password - it's the recovery hub for every other account. An attacker who controls your email can reset everything else.
You sent money or shared bank, card, or ID details
Time is the single biggest factor in recovering money. Banks can sometimes recall a wire or reverse a card transaction within the first few hours.
- Call your bank or card issuer immediately. Use the number on the back of the card, not any number from the scam email. Ask them to freeze the card, reverse the transaction if possible, and flag the account for fraud monitoring.
- If you sent a wire transfer or used a money-transfer service (Western Union, MoneyGram, Zelle, Wise), call them directly and request a recall. Some can be reversed within minutes if reported fast.
- If you sent cryptocurrency or gift cards, recovery is unlikely - but report it anyway, since law enforcement tracks these patterns.
- File a police report. You'll need the report number for any insurance, bank, or credit-bureau claim. Save the report number.
- File with the right authority for your country:
- US: ic3.gov + reportfraud.ftc.gov
- UK: reportfraud.police.uk (Report Fraud, the successor to Action Fraud; 0300 123 2040)
- Canada: antifraudcentre.ca
- Australia: scamwatch.gov.au
- EU: your national CERT or police cybercrime unit
- Set fraud alerts on all major credit bureaus if you shared any ID details. US: Equifax, Experian, TransUnion. UK: Experian, Equifax, TransUnion (Cifas Protective Registration is a stronger option).
- Save all evidence - the original email (with full headers), screenshots of the fake site, transaction records, any phone numbers or chat logs.
Final scan and startup-app check
Reconnect to the network and run one final full scan with Combo Cleaner, followed by a Windows Defender quick scan. Then open Task Manager (Ctrl + Shift + Esc) and switch to Startup apps - disable anything unfamiliar.
Make sure Windows, browsers, and any applications you use are fully up to date. The infection vector that worked on you once usually involves outdated software.
Monitor accounts and credit for 30 days
Most fraud follow-ups land in the first month. Until that window closes, keep watching:
- Bank and card statements - daily for the first week, then weekly
- Email - watch for password-reset confirmations or login alerts you didn't trigger
- Credit report - US: free at annualcreditreport.com; UK: Experian, Equifax, TransUnion all have free tiers
- Breach alerts - sign up at haveibeenpwned.com to be notified when your email appears in new leaks
If anything new appears in any of those, treat it as a continuing compromise: change passwords again, contact the bank again, and update the police report.
Important: If you didn't click anything, didn't reply, and didn't open any attachment, your computer is not infected - just delete the email and move on. If you opened an attachment or downloaded a file, run an automated scan with Combo Cleaner and Windows Defender and stop there. That path catches the vast majority of email-borne malware without the risk of breaking Windows by deleting the wrong file.
Frequently Asked Questions (FAQ)
Why did I receive this email?
Spam emails are not personal, even if they include details relevant to the recipients. If such information is present, it is likely to have been acquired through publicly available sources or phishing scams. Cyber criminals distribute this mail in large-scale campaigns – hence, thousands of users receive identical (or incredibly similar) emails.
Was my computer actually hacked and does the sender have any information?
No, all the claims made by the "Is Visiting A More Convenient Way To Reach" email are false. This means that your devices were not infected by the sender, nor do they have any of your information (including any compromising recordings). Therefore, this email poses no threat.
How did cyber criminals get my email password?
In some cases, cyber criminals use recipients' own email accounts to send them scam messages – this is to create an impression of legitimacy for their false claims. The account passwords are most commonly obtained via phishing scams. It is less likely for this data to have been acquired through a data breach on your or a service provider's end.
I have sent cryptocurrency to the address presented in this email, can I get my money back?
No, cryptocurrency transactions cannot be reversed because of their nearly untraceable nature. Hence, victims of scams like this "Is Visiting A More Convenient Way To Reach" email cannot recover their funds.
I have provided my personal information when tricked by a spam email, what should I do?
If you have provided your log-in credentials – change the passwords of all potentially compromised accounts and inform their official support without delay. And if the disclosed information was of a different personal nature (e.g., ID card details, credit card numbers, etc.) – immediately contact the appropriate authorities.
I have read a spam email but didn't open the attachment, is my computer infected?
No, opening/reading an email poses no infection threat. Devices are infected when malicious attachments or links are opened/clicked.
I have downloaded and opened a file attached to a spam email, is my computer infected?
If the opened file was an executable (.exe, .run, etc.) – most likely, yes – your device was compromised. However, you might have avoided the infection if it was a document (.doc, .xls, .one, .pdf, etc.). These formats may need additional user interaction to initiate system infection processes (e.g., enabling macros, clicking embedded content, etc.).
Will Combo Cleaner remove malware infections present in email attachments?
Yes, Combo Cleaner is capable of detecting and removing practically all known malware infections. It must be stressed that running a complete system scan is essential since high-end malicious programs typically hide deep within systems.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion