
How to remove malware spread by malicious Microsoft OneNote files
TrojanAlso Known As: Microsoft OneNote virus

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What is Microsoft OneNote malware?
Microsoft OneNote malware – refers to malicious software distributed using trojanized OneNote (.one) files. The legitimate format documents are modified for malware proliferation by being embedded with virulent content, which triggers the malware's download/installation process when interacted with.
The rise of infectious OneNote files coincides with Microsoft's decision to automatically block macros from the Internet on MS Office documents. For many years, cyber criminals had relied on malicious macro commands to distribute malware; however, these new developments had closed this avenue and likely gave rise to the use of OneNote files.
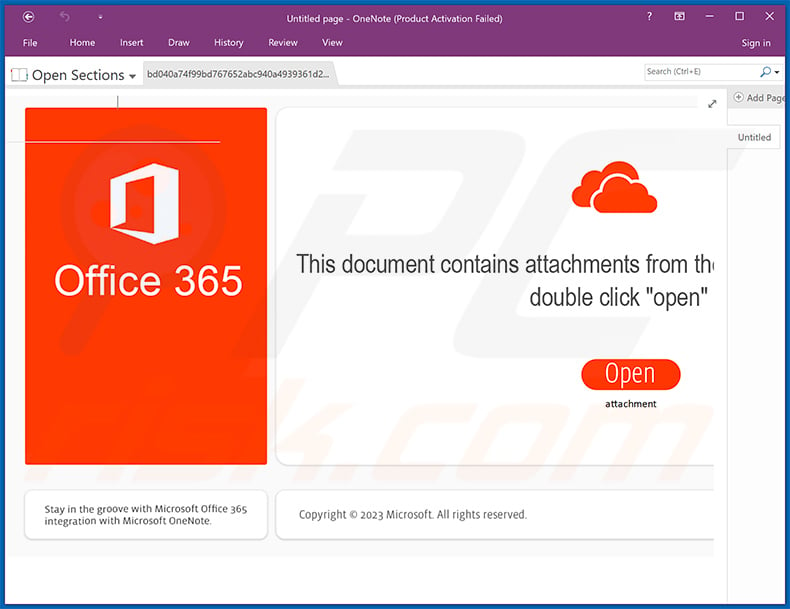
Microsoft OneNote malware overview
In most cases, malicious OneNote files are promoted through spam campaigns. These files are distributed either as attachments or via download links.
At the time of writing, two malicious programs have been observed being proliferated in this manner – the Qakbot banking trojan that targets finance-related information and is capable of causing chain infections (i.e., installing additional trojans, ransomware, cryptominers, etc.), and the RedLine Stealer that is designed to extract a variety of sensitive data from infected devices.
The researched campaigns carrying Qakbot targeted victims at random or used stolen email accounts and replied to all participants on an existing email thread. The spam letters themselves tended to be impersonal, with the only personal detail being the recipient's last name written in the subject line for some of the emails.
The inspected virulent OneNote files had an HTML application (HTA file) embedded into them, which (after being clicked) leveraged a legitimate app to download/install the malware (in this instance, Qakbot). However, almost any type of file can be embedded into OneNote.
Document formats often require additional user interaction to jumpstart infection chains (i.e., malware download/installation does not begin upon opening), and this applies to malicious OneNote files.
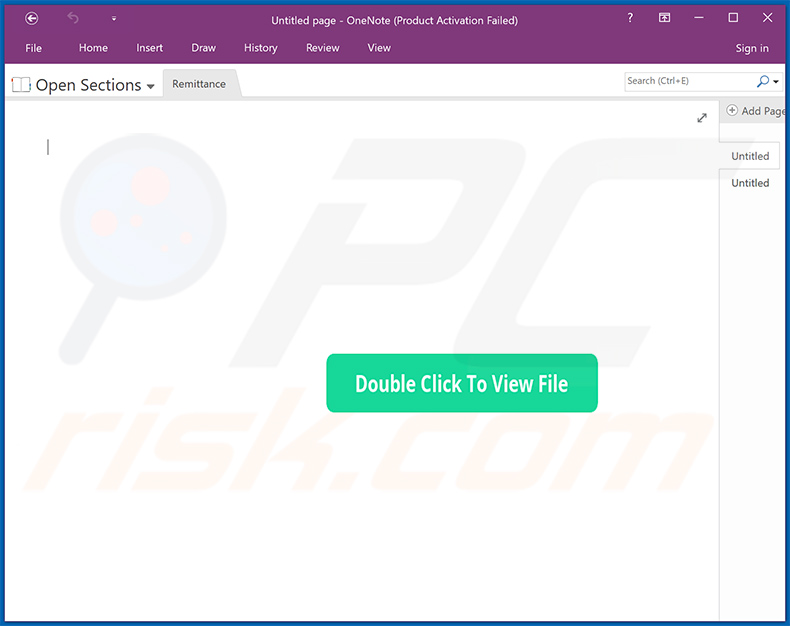
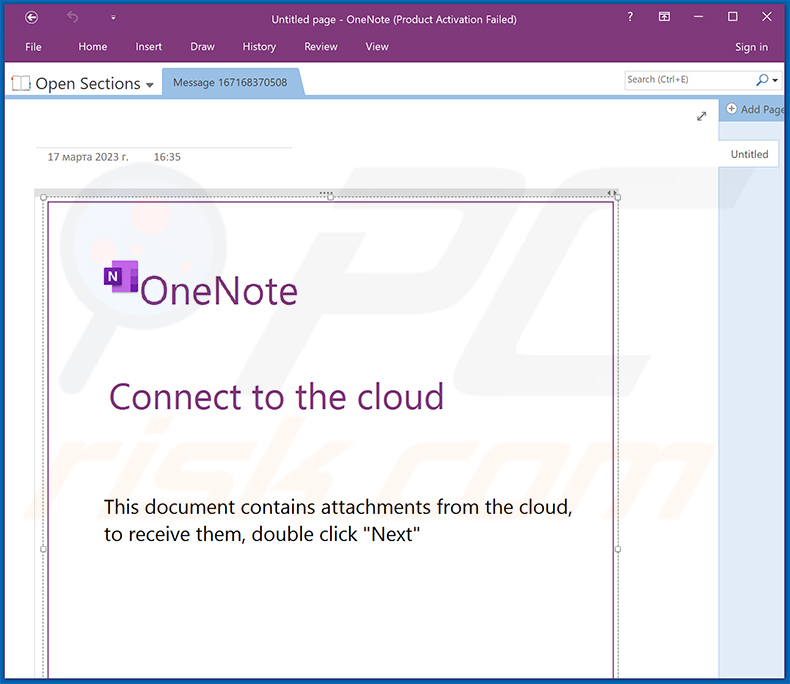
Infectious Microsoft Office documents require users to allow their macro commands (i.e., enable editing/content), while OneNote files need users to click the embedded content. To achieve this, cyber criminals typically resort to social engineering. For example, the analyzed OneNote files contained fake buttons like "Open" that supposedly downloads the file from cloud storage, or "Double Click To View File" – implies access to whatever nonexistent content.
In theory, virulent OneNote files could be used to proliferate any and all types of malware. The threats posed by an infection depend on the program's capabilities and the cyber criminals' aims.
Generally, malware infections can result in decreased system performance or failure, data loss, hardware damage, severe privacy issues, financial losses, and identity theft.
If you believe that your device is already infected – we strongly recommend using an anti-virus to perform a complete system scan and to remove detected threats without delay.
| Name | Microsoft OneNote virus |
| Threat Type | Trojan, password-stealing virus, banking malware, spyware. |
| Detection Names (spreading Qakbot) | Avast (Other:Malware-gen [Trj]), Combo Cleaner (Trojan.GenericKD.65264047), ESET-NOD32 (Multiple Detections), Kaspersky (Trojan.Script.Agent.jr), Microsoft (TrojanDownloader:O97M/Qakbot.SS!MTB), Full List Of Detections (VirusTotal) |
| Detection Names (spreading RedLine) | Avast (Other:Malware-gen [Trj]), Combo Cleaner (Trojan.Generic.33194109), ESET-NOD32 (BAT/Agent.PLI), Kaspersky (Trojan.Script.Agent.jq), Microsoft (Trojan:Win32/Leonem), Full List Of Detections (VirusTotal) |
| Payload | Qakbot, RedLine |
| Symptoms | Trojans are designed to stealthily infiltrate the victim's computer and remain silent, and thus no particular symptoms are clearly visible on an infected machine. |
| Distribution methods | Infected email attachments, malicious online advertisements, social engineering. |
| Damage | Stolen passwords and banking information, identity theft, the victim's computer added to a botnet. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
Malware in general
Trojanized OneNote files can be used to distribute just about any malware. Malicious software can have a broad range of functionalities and uses.
Popular types include: backdoors/loaders (cause chain infections), stealers (steal data/content), spyware (take screenshots, record keystrokes, audio/video, etc.), clippers (replace clipboard data), ransomware (encrypt data/ lock device's screen for ransom purposes), cryptominers (abuse system resources to generate cryptocurrency), and so on.
However, regardless of how malware operates – its presence on a system endangers device/user safety. Therefore, it is paramount to eliminate all threats immediately upon detection.
How did Microsoft OneNote malware infiltrate my computer?
Malicious OneNote files are most commonly distributed via email spam campaigns, as attachments or through download links. These emails can be variously disguised, often as messages from legitimate companies, service providers, institutions, authorities, and other entities.
The infection process is triggered when the content embedded into the OneNote file is clicked. Social engineering can be used to deceive users into doing so (e.g., requests to click a button to download/open a file, etc.).
However, it is possible for infectious OneNote files to be distributed employing other methods. Users can be tricked into downloading such a file through search engine poisoning or malvertising techniques, wherein the malicious file is presented as ordinary content. Various online scams could also be used to proliferate virulent OneNote files.
How to avoid installation of malware?
We highly recommend exercising caution with incoming emails, PMs/DMs, SMSes, and other messages. The attachments or links found in suspicious/irrelevant mail must not be opened, as they can be infectious.
The same vigilance must be extended to browsing since fraudulent and malicious online content usually appears legitimate and harmless.
We advise downloading only from official and verified channels. Furthermore, all programs must be activated and updated using functions/tools provided by genuine developers, as illegal activation tools ("cracks") and third-party updates may contain malware.
It is paramount to have a reputable anti-virus installed and kept updated. Security software must be used to run regular system scans and to remove detected threats and issues. If you believe that your computer is already infected, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate infiltrated malware.
Screenshot of a malicious OneNote file spreading the RedLine Stealer:
Screenshot of a spam email distributing a malicious OneNote file:
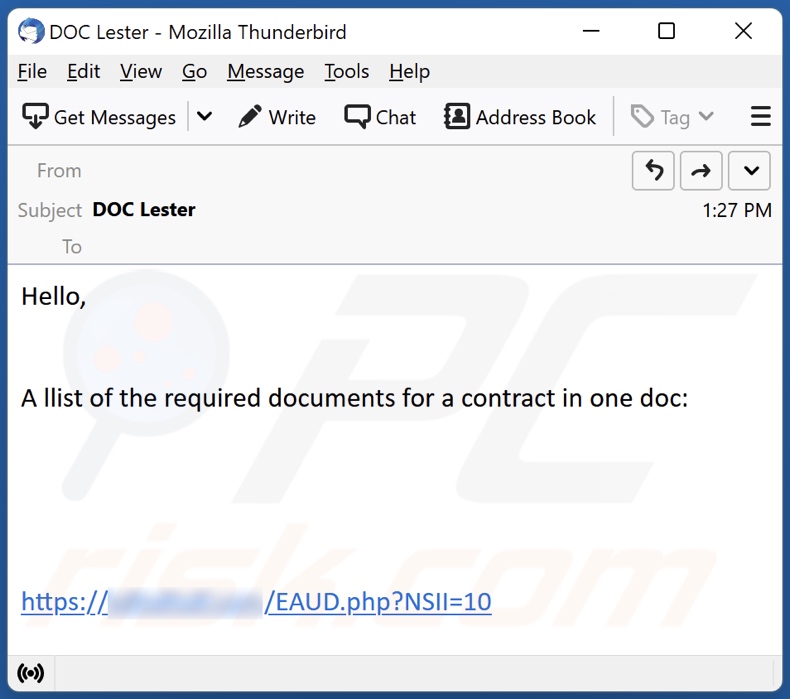
Text presented in this email:
Subject: DOC Lester
Hello,
A llist of the required documents for a contract in one doc:-
Screenshot of yet another spam email distributing a malicious OneNote file:
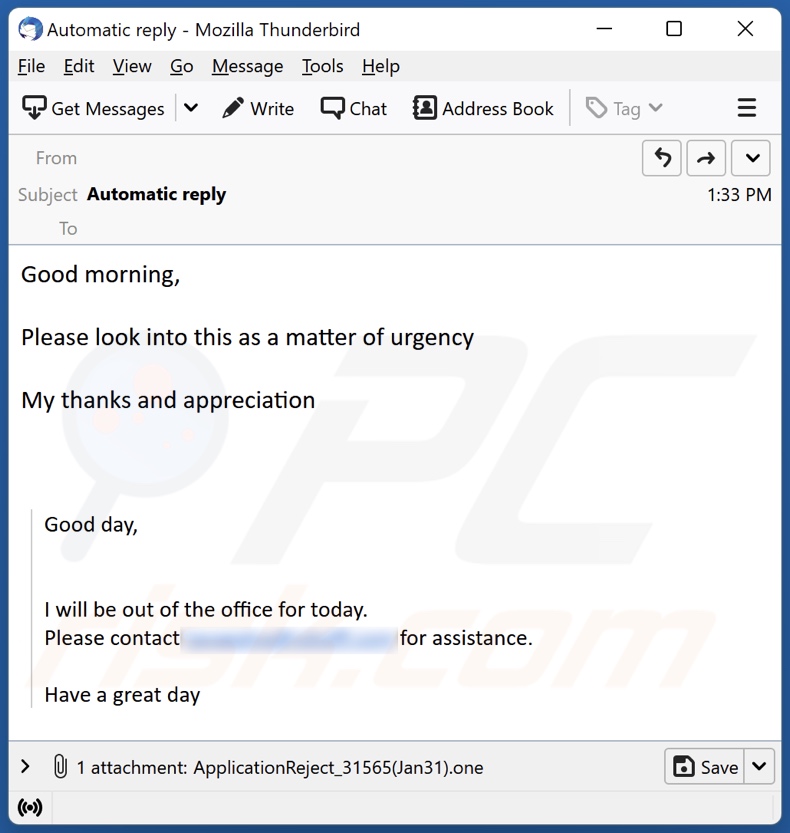
Text presented in this email:
Subject: Automatic reply
Good morning,
Please look into this as a matter of urgency
My thanks and appreciation
Good day,
I will be out of the office for today.
Please contact - for assistance.
Have a great day
Example of a malicious OneNote document spreading Emotet malware:
How to remove malware manually?
Most trojan infections can be removed by running a full system scan with Combo Cleaner. The full manual procedure below is for cases where automatic removal failed, where you want to verify a scan caught everything, or where the threat has multiple persistence points.
Disconnect from the network
Unplug your Ethernet cable and turn off Wi-Fi. If you're on a laptop, the airplane-mode key works fastest.
Many trojans exfiltrate data - saved browser passwords, banking sessions, screenshots - and accept remote commands. Cutting the network stops both immediately. Keep it disconnected until Phase 4.
Boot into Safe Mode with Networking
Safe Mode loads a minimal set of drivers and stops most malware from auto-running. "With Networking" lets you download tools - re-enable Wi-Fi only after you've booted in.
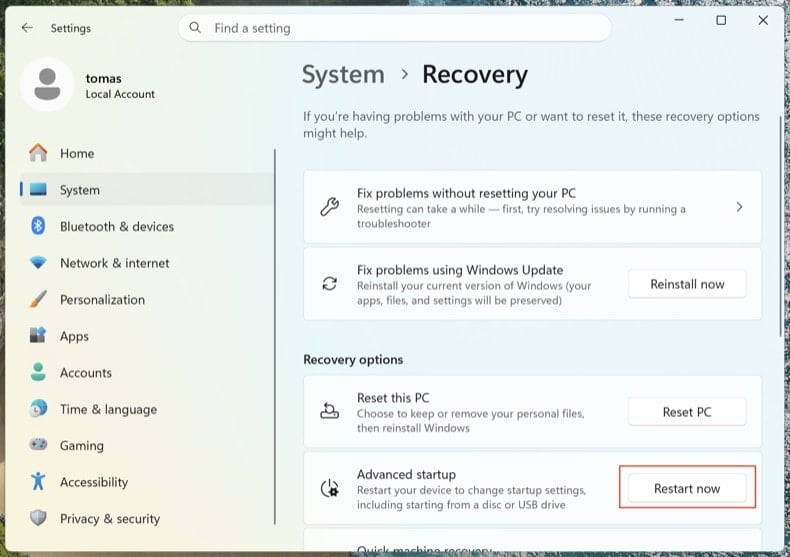
Open . Click Restart now next to Advanced startup.
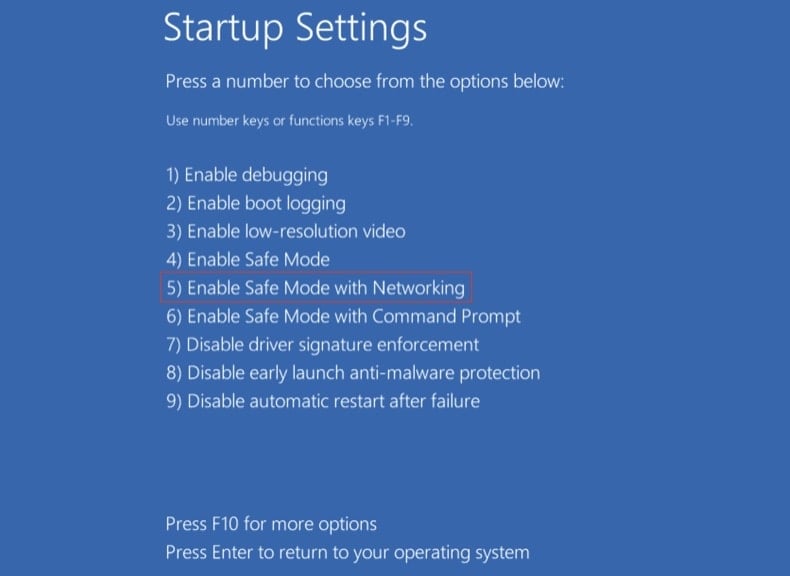
Your computer will restart into the "Choose an option" menu. Click . After the second reboot, press 5 or F5.
Click the Windows logo, hold Shift, click the Power icon and choose Restart. In the Choose an option screen, click . Press F5.
Windows 8
Go to the Start Screen, type Advanced, select Settings → Advanced startup options → Restart now → Troubleshoot → Advanced options → Startup settings → Restart → F5.
Note: Windows 8 reached end-of-life in January 2023 - running on it puts you at much higher risk of reinfection.
Windows 7
Click Start → Shut Down → Restart → OK. As the system boots, press F8 repeatedly until the Windows Advanced Options menu appears, then choose Safe Mode with Networking.
Note: Windows 7 reached end-of-life in January 2020 - running on it puts you at much higher risk of reinfection.
Inspect running processes with Process Explorer
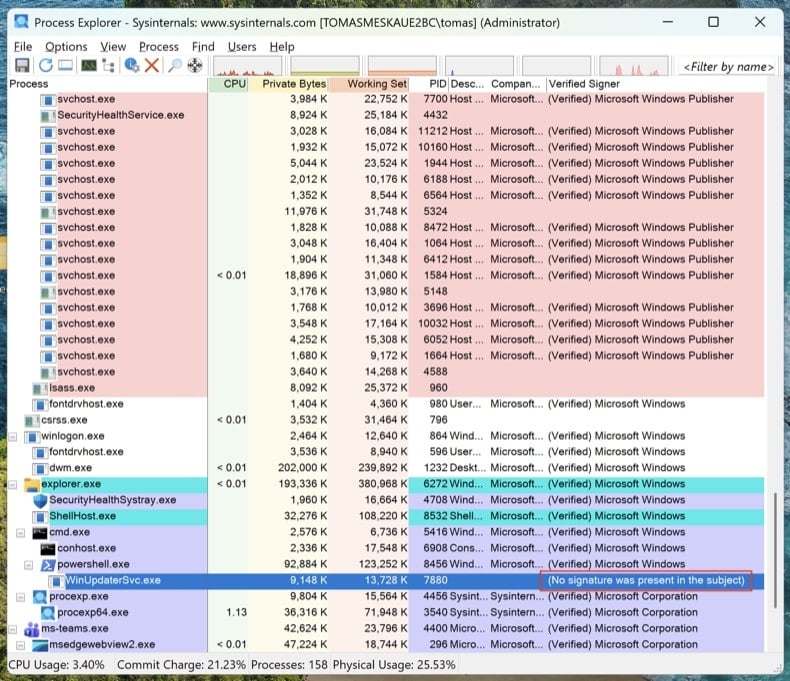
Download Process Explorer from Microsoft Sysinternals. Run it as Administrator. Click and .
Sort by "Verified Signer." Anything unsigned running from %AppData%, %LocalAppData%, %Temp%, or %ProgramData% is suspicious. Right-click → Properties to see the full image path. Right-click → "Search Online" to look up unfamiliar process names.
Task Manager hides full file paths, doesn't show digital signatures, and groups processes in ways that make malware easy to miss. Process Explorer is the same tool Microsoft engineers use.
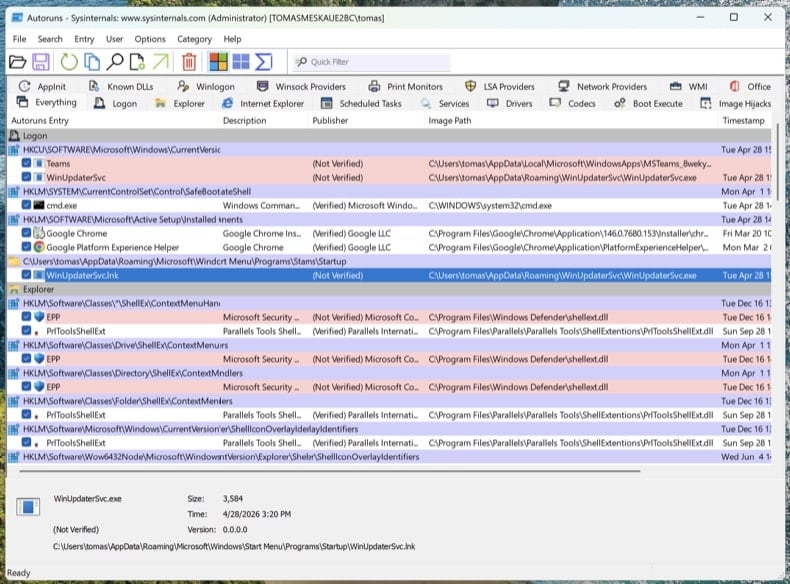
Map every persistence point with Autoruns
Download Autoruns. Right-click Autoruns.exe and choose Run as administrator - without elevation, Autoruns can't inspect protected registry hives.
In the menu, open and , then click Refresh.
Modern trojans don't just live in startup. Walk through these tabs and look for unsigned or unfamiliar entries:
- Logon - classic Run/RunOnce keys
- Scheduled Tasks - frequent hiding spot, especially tasks with PowerShell, MSHTA, or rundll32 actions
- Services - unsigned services in non-Microsoft folders
- WMI - Event Subscriptions are a stealthy persistence mechanism (MITRE T1546.003)
- Image Hijacks - Image File Execution Options "Debugger" abuse
- AppInit - DLLs loaded into every GUI process
- Browser plug-ins - unsigned add-ons across all installed browsers
Right-click any suspicious entry → "Jump to Image" to see the actual file. Right-click → "Search Online" opens VirusTotal for the file hash. Don't delete yet - just write down the file paths and entry names. We'll remove them after the scans.
Check the hosts file and DNS settings
Trojans often redirect bank, antivirus, and update domains to attacker-controlled servers by editing the hosts file or DNS settings.
Hosts file: Open Notepad as Administrator and open C:\Windows\System32\drivers\etc\hosts. Legitimate entries are commented with #. Any uncommented IP-to-domain mapping is suspicious - especially redirects for microsoft.com, windowsupdate, or your bank.
DNS settings: Open Command Prompt as Administrator and run ipconfig /all. Confirm your DNS servers point to your ISP, your router, or a known public resolver (Cloudflare 1.1.1.1, Google 8.8.8.8). Then open and verify both DNS and DNS over HTTPS (DoH) settings haven't been hijacked.
A clean PC with hijacked DNS is still a compromised PC. You'll think you're at chase.com and you'll be at the attacker's clone.
No single antivirus catches everything. The order below is intentional: offline scan first (catches rootkits before Windows fully loads), then on-demand scanners on the running system, then manual cleanup of anything they missed.
Run Microsoft Defender Offline
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. Your computer will restart into a stripped-down environment and scan before the full operating system loads.
Rootkits and bootkits hide from any scanner running on the same Windows session that's already infected. A pre-boot offline scan sees the disk before the malware can hide itself.
VB100 certified. Includes anti-trojan, registry/persistence scanning, anti-spyware in one pass. The 7-day free trial is available.
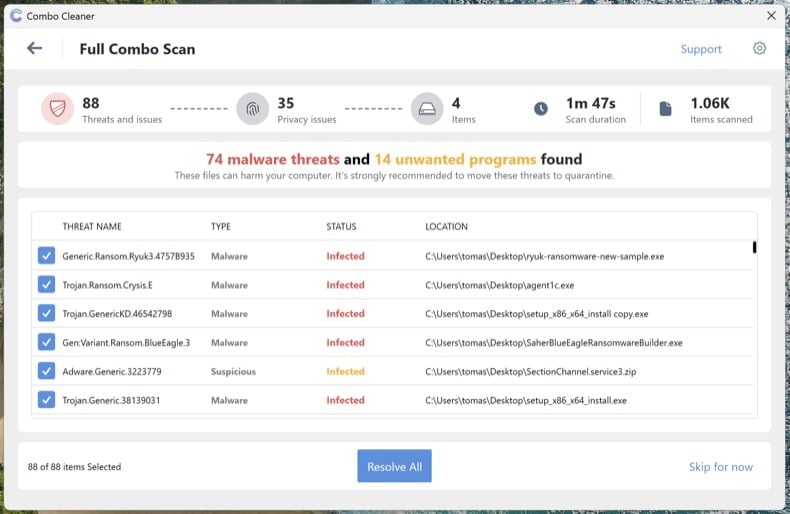
Download Combo CleanerRun Combo Cleaner full system scan
Install Combo Cleaner and run a full system scan (not the quick scan). Let it complete fully, review the detected threats, and apply the recommended actions. Combo Cleaner will quarantine known trojans and registry persistence.
Run Microsoft Safety Scanner as a second-opinion scan
Download Microsoft Safety Scanner (MSERT.exe), Microsoft's free on-demand tool. The binary expires every 10 days, which means every download has the latest signatures. Run a full scan after Combo Cleaner to catch anything one engine alone might miss.
Different scanning engines catch different threats. Running an additional Microsoft scan after Combo Cleaner is the single most underused verification step in malware removal.
Manually remove anything still listed in Autoruns
Reopen Autoruns. Anything you flagged in Step 4 that's still present hasn't been caught by the automated scans. For each remaining suspicious entry: right-click → Delete in Autoruns (this removes the persistence registration), then navigate to the file path and delete the actual file. Empty the Recycle Bin.
Some malware files reappear after deletion because something else on the system recreates them. If you delete a file and it returns within minutes, you have a remaining persistence point that Autoruns didn't show - usually a service or scheduled task running under SYSTEM. Re-run the scans from Steps 6-8 or proceed to a clean install (see end of guide).
Reset browsers and clear notification permissions
Trojans and adware frequently hijack browsers - change the default search engine, install rogue extensions, or grant themselves notification permissions to keep displaying scam pop-ups even after the malware is gone.
- Chrome: visit
chrome://settings/resetand click "Restore settings to their original defaults." Then visitchrome://settings/content/notificationsand remove any unfamiliar sites. - Edge: visit
edge://settings/reset. Then checkedge://settings/content/notifications. - Firefox: open
about:supportand click Refresh Firefox (Firefox uses "Refresh," not "Reset"). Then check Settings → Privacy & Security → Permissions → Notifications.
Review installed extensions in each browser and remove anything you don't recognize, especially extensions you didn't install yourself.
Re-enable Defender, Tamper Protection, and update everything
Many trojans disable security software. Open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all turned on. Tamper Protection prevents malware from disabling Defender silently.
Then run Windows Update () and update your browsers and applications. The infection vector that let the trojan in originally usually involves outdated software.
Change passwords from a clean device
If the trojan was an info-stealer (Lumma, RedLine, Vidar, and similar are extremely common), assume every password saved in your browser is compromised. Change them from a different, known-clean device - your phone is fine if it's not infected.
Recommended order:
- Primary email first - it's the recovery hub for everything else
- Banking and financial accounts
- Password manager master password (if you use one)
- Social media, shopping, and remaining accounts
Where available, enable phishing-resistant multi-factor authentication (passkeys / FIDO2 hardware keys / authenticator apps) - SMS-based MFA is bypassable by sophisticated attackers.
Verify the clean and monitor for 7 days
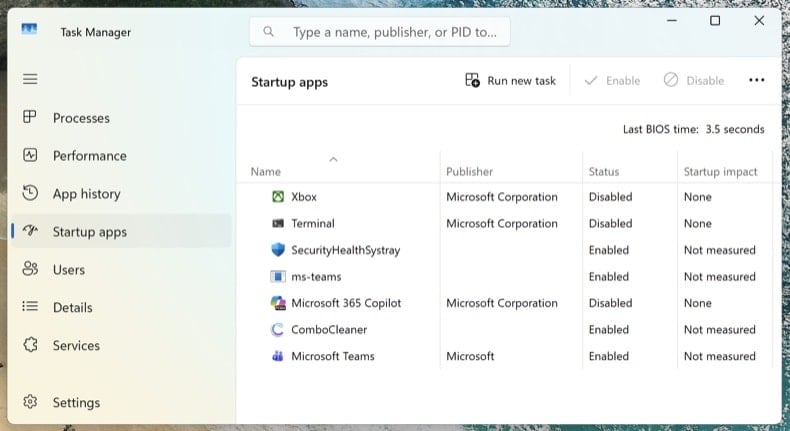
Reconnect to the network and run one final full scan with Combo Cleaner. Open Task Manager (Ctrl + Shift + Esc) and switch to the Startup apps tab - confirm nothing suspicious has reappeared.
Over the next 7 days, watch for symptom recurrence: unexpected high CPU usage, unknown processes returning, browser redirects, or pop-ups. If anything returns, you missed a persistence point and the procedure needs to be repeated - or you may have a deeper compromise that requires a clean install.
When to clean install Windows instead
Manual removal isn't always the right answer. Reinstalling Windows from scratch is the only way to be 100% certain when:
- The malware reappears after every removal attempt
- A bootkit or UEFI rootkit was detected (this class of threat sits below the operating system and survives a normal Windows reinstall)
- A confirmed credential-theft trojan ran with administrator privileges (Lumma, RedLine, Vidar) - the system likely has multiple unknown payloads
- The PC is used for online banking, business email, or anything where partial doubt isn't acceptable
A clean install is a 30-60 minute process: Windows 11 reinstall via . Back up documents to external storage first, scan the backup with Combo Cleaner before restoring it, and reinstall applications fresh - never restore them from a backup of the infected system.
Important: Manual removal requires advanced computer skills. If you're not confident identifying system files from malicious files, run an automated scan with Combo Cleaner and Windows Defender and stop there - that path catches the vast majority of consumer trojans without the risk of breaking Windows by deleting the wrong file.
Frequently Asked Questions (FAQ)
What is the purpose of malicious OneNote files?
The legitimate OneNote file format can be trojanized by cyber criminals to infect victims' devices with malware. These infectious files can be used to proliferate just about any kind of malicious program. The malware download/installation is triggered when the victim interacts with content embedded in the OneNote file.
What are the biggest issues that OneNote malware can cause?
The threats posed by an infection depend on the malware's capabilities and the cyber criminals' modus operandi. As mentioned in the previous answer, virulent OneNote files can be used to spread various types of malware, e.g., trojans, ransomware, cryptominers, etc. Generally, high-risk infections can result in diminished system performance or failure, severe privacy issues, data loss, hardware damage, financial losses, and identity theft.
How did OneNote malware infiltrate my computer?
Malicious OneNote files are primarily distributed as attachments or through download links in spam emails. However, these files might also be spread using search engine poisoning techniques, malvertising, online scams, and others.
I have read a spam email but didn't open the OneNote file, is my computer infected?
No, merely reading an email will not initiate any malware download/installation processes. Devices are infected when malicious attachments or links found in spam mail are opened/clicked, and this applies to malicious OneNote files.
I have downloaded and opened the OneNote file promoted by a spam email, is my computer infected?
Malicious OneNote files begin downloading/installing malware when the content embedded into them (e.g., files like HTA, LNK, VBS, etc.) is clicked. Keep in mind that these files often contain deceptive instructions intended to trick users into interacting with the content.
Will Combo Cleaner protect me from malware?
Yes, Combo Cleaner can scan systems and detect as well as eliminate practically all known malware infections. It must be stressed that running a complete system scan is paramount since sophisticated malicious programs usually hide deep within systems.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion