
How to get rid of RemControl android banking trojan
TrojanAlso Known As: RemControl banking malware

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What kind of malware is RemControl?
RemControl is an Android banking trojan and Remote Access Trojan (RAT) targeting retail banking customers across Western Europe, the Middle East, and Canada. It operates as a Malware-as-a-Service (MaaS) platform. According to research published by Group-IB, the malware was first identified in July 2026, with its infrastructure active since May 2026.
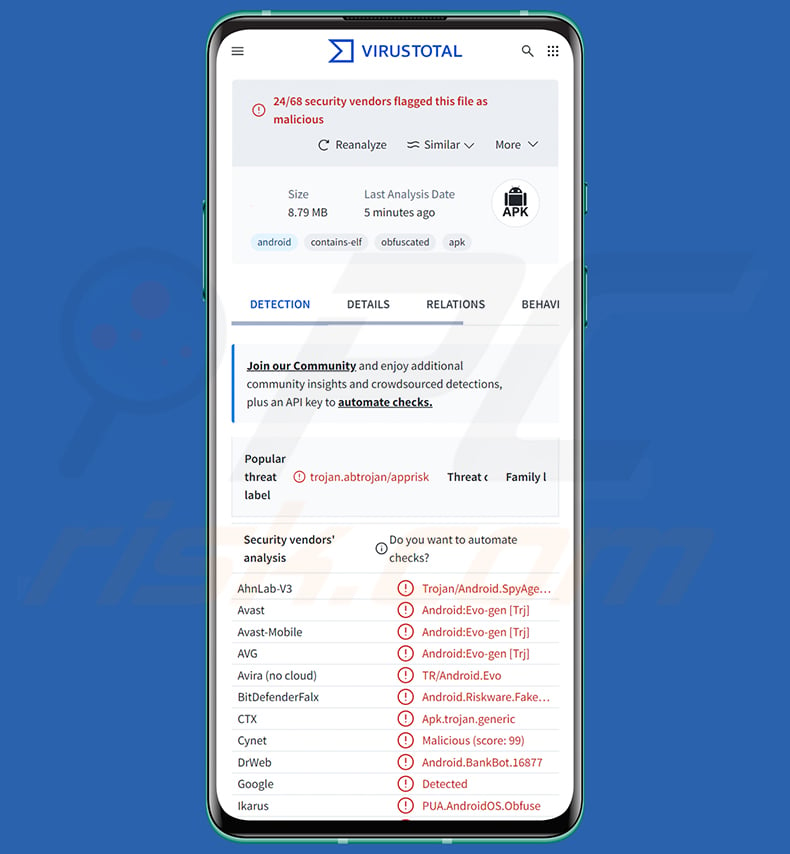
RemControl banking trojan overview
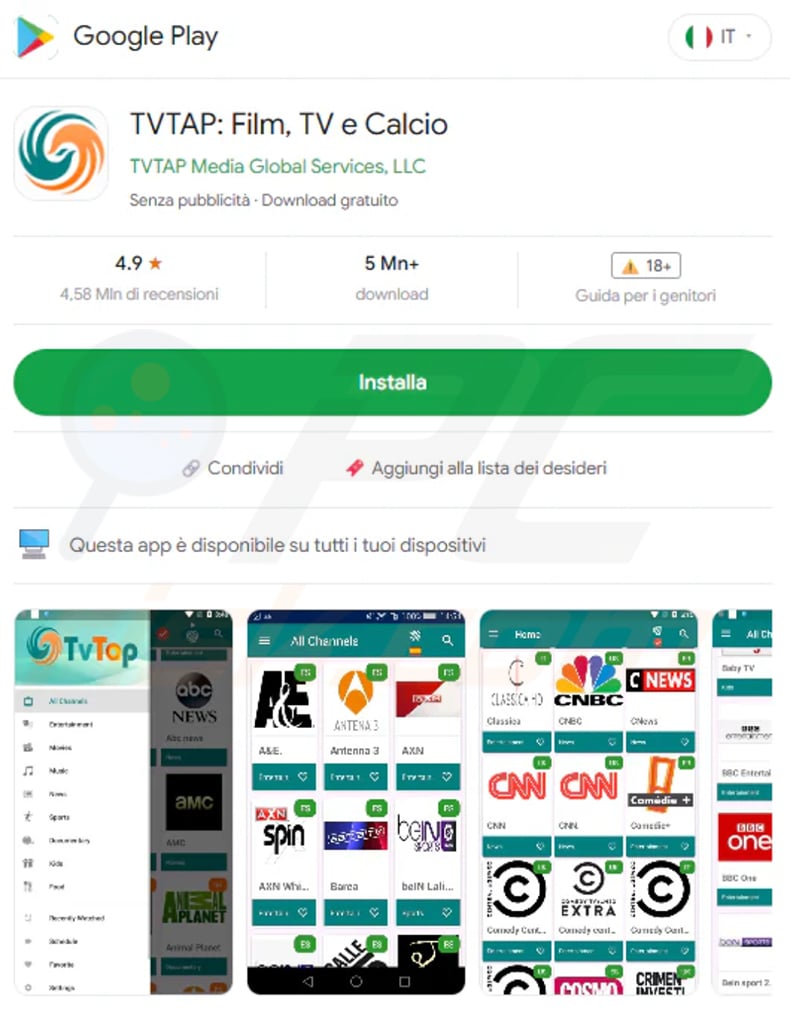
RemControl is distributed through fake Google Play Store pages impersonating TVTap, a popular IPTV app for watching live TV channels. The fake pages show a 4.9-star rating and over 5 million downloads to look trustworthy, and victims are lured there through malvertising on Meta's advertising platform.
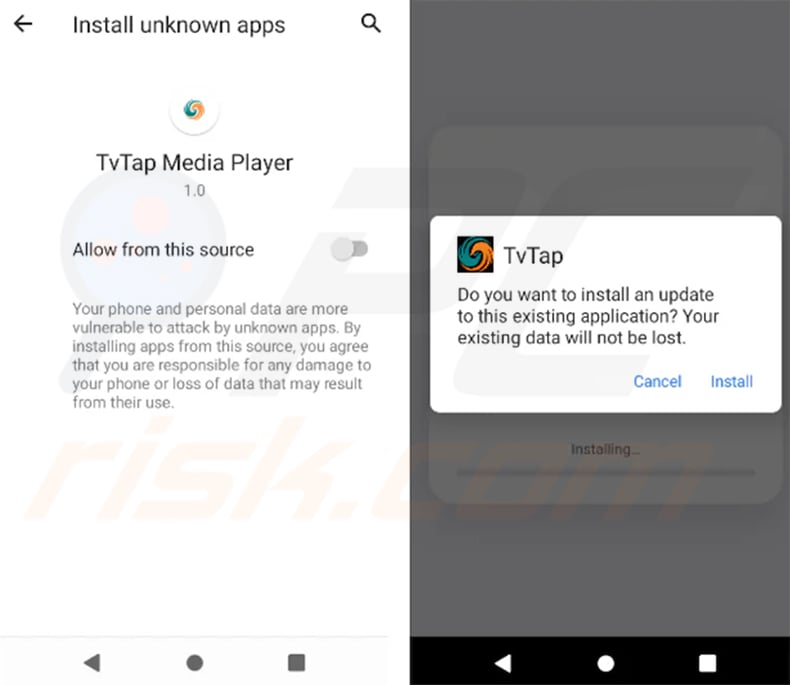
When opened, the dropper shows a fake "Update TVTap" screen and asks permission to set up a VPN connection. This VPN is not there to protect the victim - it cuts the Google Play Store off from the internet, so Google Play Protect cannot scan the malware while it installs.
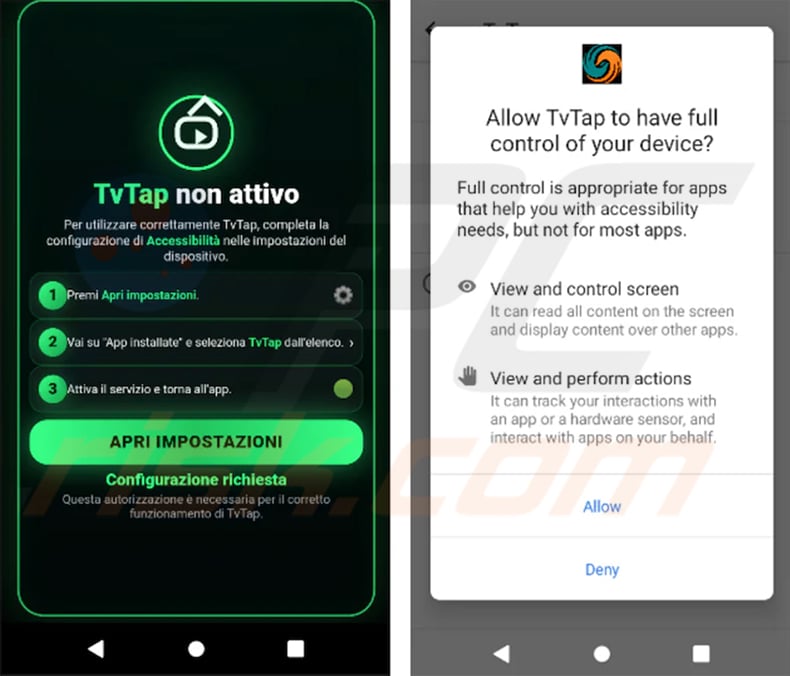
Every installed copy is also signed differently, making it harder for security tools to recognize. Once installed, the payload claims TVTap is not active and guides the victim to enable Accessibility in the settings, which gives the malware full control of the device.
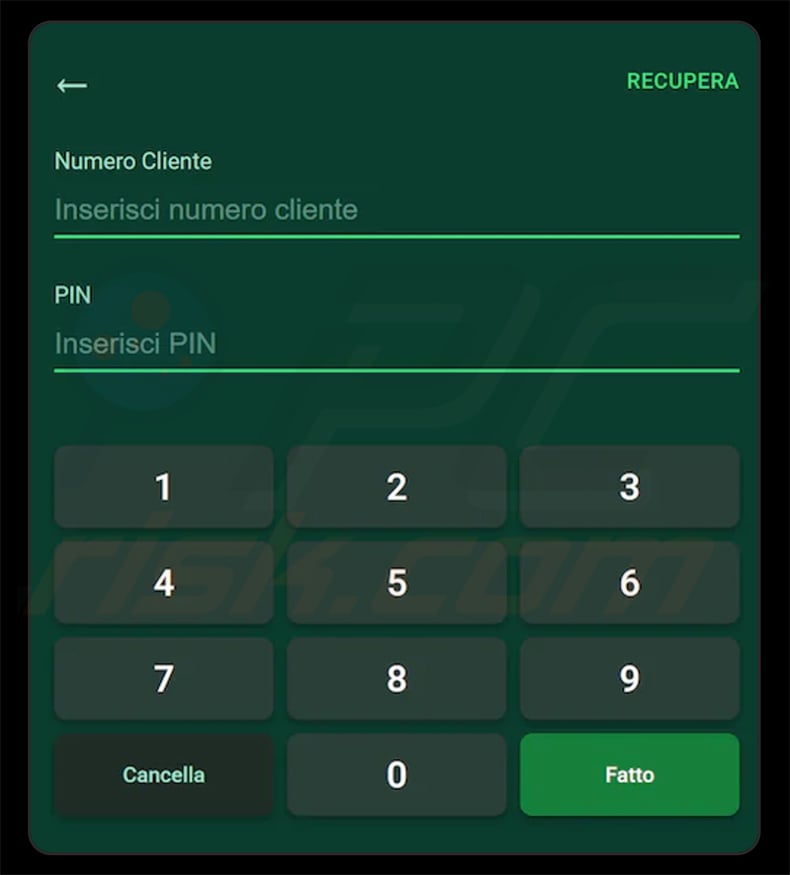
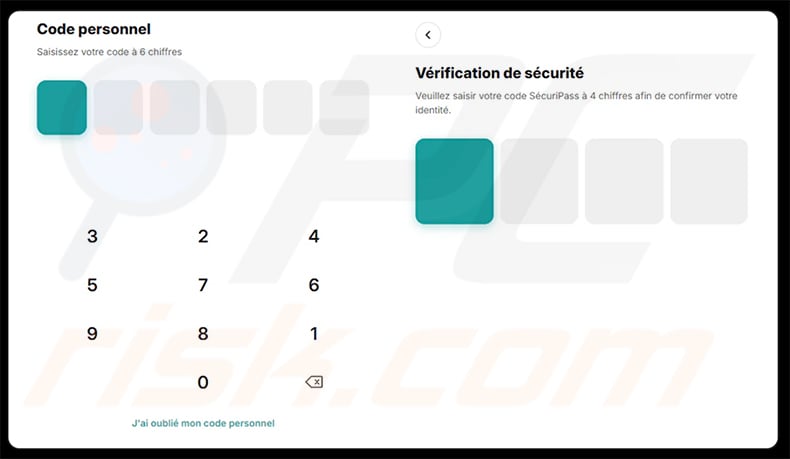
From that point, RemControl watches which app is open. When the victim launches one of more than 30 targeted banking apps, it covers it with a fake login screen asking for details such as a customer number, PIN, or security code. After the details are submitted, the fake screen closes and the real app reappears.
The operator can also watch the device screen live and control it remotely - tapping, swiping, and typing as if holding the phone. RemControl can record keystrokes (keylogging), capture the screen unlock pattern, and read clipboard contents, which may expose copied passwords or codes.
The unlock pattern capture works on lock screens from many popular phone makers, including Samsung, Xiaomi, Huawei, OPPO, and OnePlus, as well as standard Android.
To make removal harder, the malware blocks access to settings screens used for uninstalling apps, managing Accessibility, or performing a factory reset by instantly backing out of them. It also finds its server address through a Telegram dead-drop, so attackers can change servers without updating the malware.
Group-IB found that RemControl is rented out to other cybercriminals as a service, with a panel for building new versions, managing infected devices, and editing fake login screens. Notably, parts of it were built with AI assistance - one live phishing page even contained a leftover AI chatbot response beneath its login form.
In summary, the presence of RemControl on a device can lead to serious privacy violations, financial losses, unauthorized banking transactions, and identity theft. Malware developers often improve their software, so future versions of RemControl could have additional or different features.
| Name | RemControl banking malware |
| Threat Type | Android malware, malicious application, banking trojan, Remote Access Trojan, RAT. |
| Detection Names | Avast-Mobile (Android:Evo-gen [Trj]), Combo Cleaner (Android.Riskware.FakeApp.AHY), Kaspersky (HEUR:Trojan-Banker.AndroidOS.Agent.aeh), McAfee Scanner (Ti!AF2DECF5C5CB), Full List (VirusTotal) |
| Symptoms | The device is running slow, system settings are modified without user's permission, questionable applications appear, data and battery usage is increased significantly, browsers redirect to questionable websites, intrusive advertisements are delivered. |
| Distribution methods | Fake Google Play Store pages impersonating the TVTap IPTV application, malvertising campaigns. |
| Damage | Stolen personal information (private messages, logins/passwords, banking credentials, etc.), decreased device performance, battery is drained quickly, decreased Internet speed, huge data losses, monetary losses, stolen identity (malicious apps might abuse communication apps). |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
Android banking trojan examples
RemControl joins a growing list of Android banking trojans that abuse the Accessibility Service to steal banking credentials through phishing overlays, intercept SMS-based one-time codes, and give operators real-time remote control over infected devices. Other examples of similar Android banking trojans include Rokarolla, OverlayPhantom, and PhantomCard/NFCShare.
Regardless of how exactly a given piece of malware behaves, the end result is the same: it is a serious threat to the device and its owner. Practicing safe habits and using reputable security software are the most effective ways to stay protected.
How did RemControl infiltrate my device?
RemControl is distributed through fake Google Play Store pages impersonating the TVTap IPTV application. Since TVTap is not available on the official store, users are already conditioned to download it from unofficial sources, making it an ideal lure.
Group-IB confirmed the operator uses malvertising campaigns on Meta's advertising platform to drive victim traffic to these fake pages. The pages check the visitor's browser type and geolocation before serving the malicious APK, targeting only mobile users from specific countries.
In general, Android malware is also commonly spread through third-party app stores, phishing pages mimicking banks or service providers, malicious links shared via social media or messaging apps, and fake software update prompts.
How to avoid installation of malware?
Download applications only from official sources such as the Google Play Store or the developer's official website. Be especially wary of any site or advertisement directing you to download an app outside of the official store.
Before installing any app, review its permissions. Be particularly suspicious of apps requesting Accessibility Service access, as this permission is rarely needed by legitimate apps and gives an application near-complete control over the device.
Keep your device's operating system and all installed applications updated. Use reputable mobile security software and be cautious with links received via email, SMS, or social media, as these are common delivery channels for mobile malware.
Fake Google Play Store page impersonating TVTap, used to distribute RemControl (in Italian, source: Group-IB):
RemControl dropper displaying a fake TVTap update screen (source: Group-IB):
RemControl requesting Accessibility Service access (full control of the device, source: Group-IB):
Examples of phishing overlays displayed by RemControl over banking apps:
Screenshot of a one-step authentication overlay (source: Group-IB):
Screenshot of a two-step authentication overlay (source: Group-IB):
Quick menu:
- Introduction
- How to delete browsing history from the Chrome web browser?
- How to disable browser notifications in the Chrome web browser?
- How to reset the Chrome web browser?
- How to delete browsing history from the Firefox web browser?
- How to disable browser notifications in the Firefox web browser?
- How to reset the Firefox web browser?
- How to uninstall potentially unwanted and/or malicious applications?
- How to boot the Android device in "Safe Mode"?
- How to check the battery usage of various applications?
- How to check the data usage of various applications?
- How to install the latest software updates?
- How to reset the system to its default state?
- How to disable applications that have administrator privileges?
Delete browsing history from the Chrome web browser:
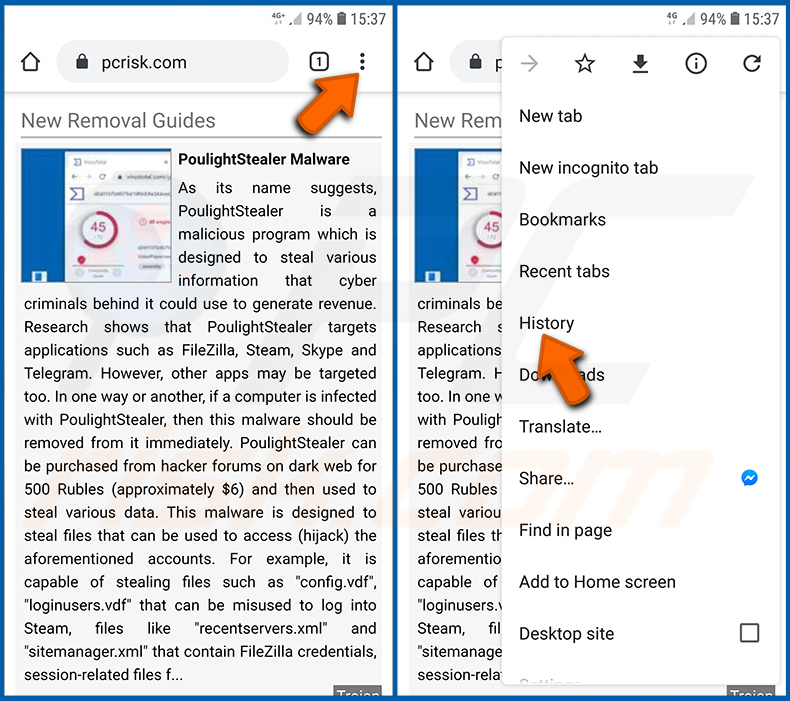
Tap the "Menu" button (three dots on the right-upper corner of the screen) and select "History" in the opened dropdown menu.
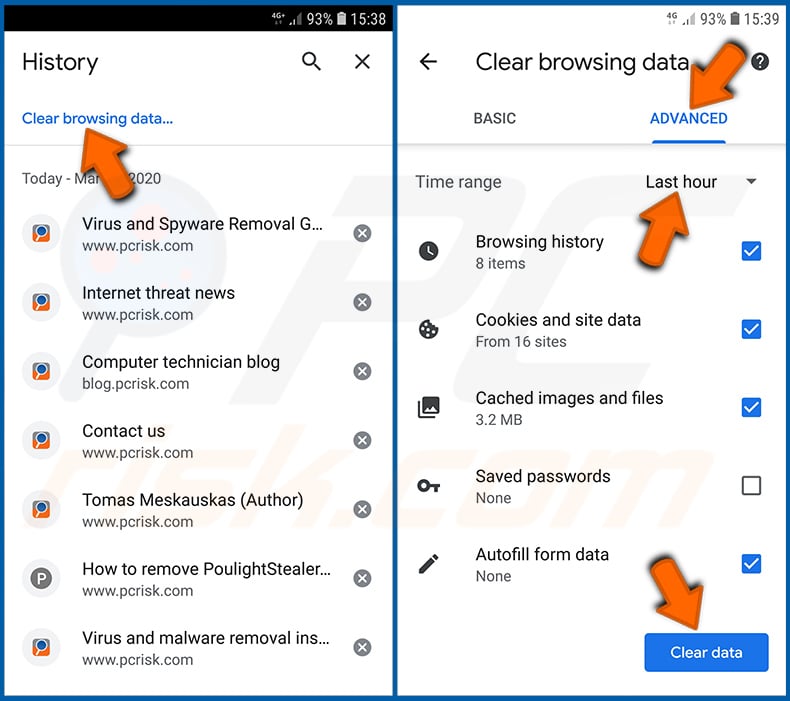
Tap "Clear browsing data", select "ADVANCED" tab, choose the time range and data types you want to delete and tap "Clear data".
Disable browser notifications in the Chrome web browser:
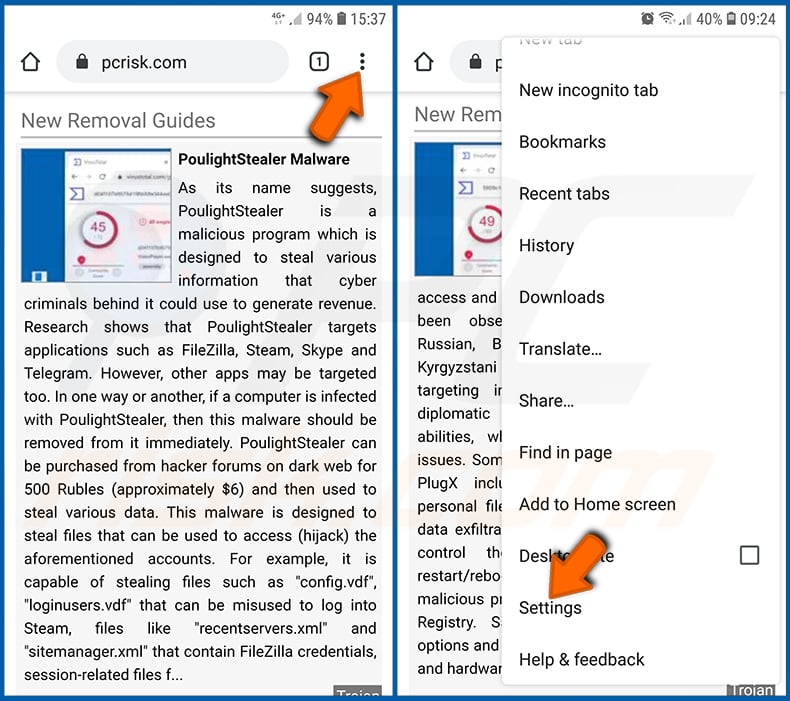
Tap the "Menu" button (three dots on the right-upper corner of the screen) and select "Settings" in the opened dropdown menu.
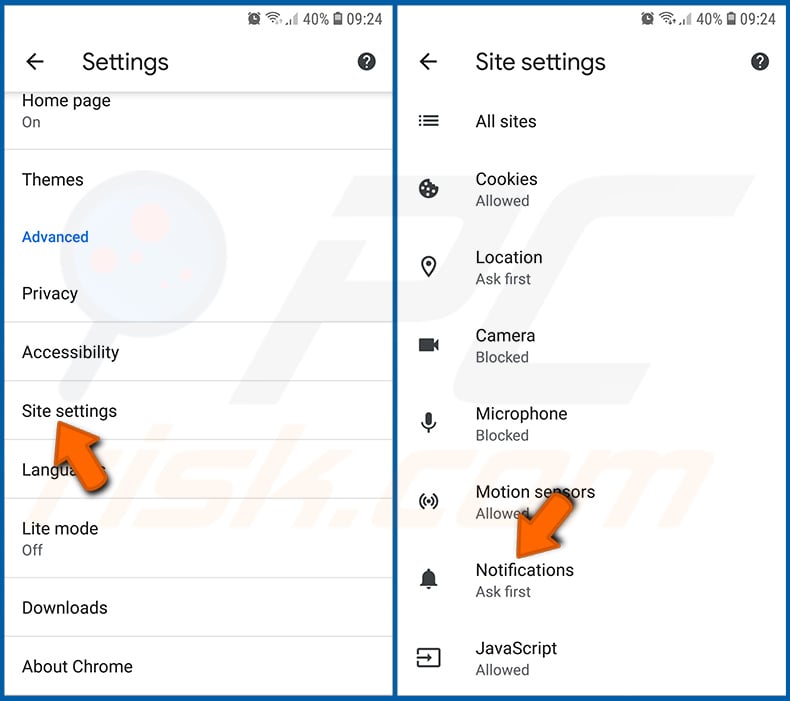
Scroll down until you see "Site settings" option and tap it. Scroll down until you see "Notifications" option and tap it.
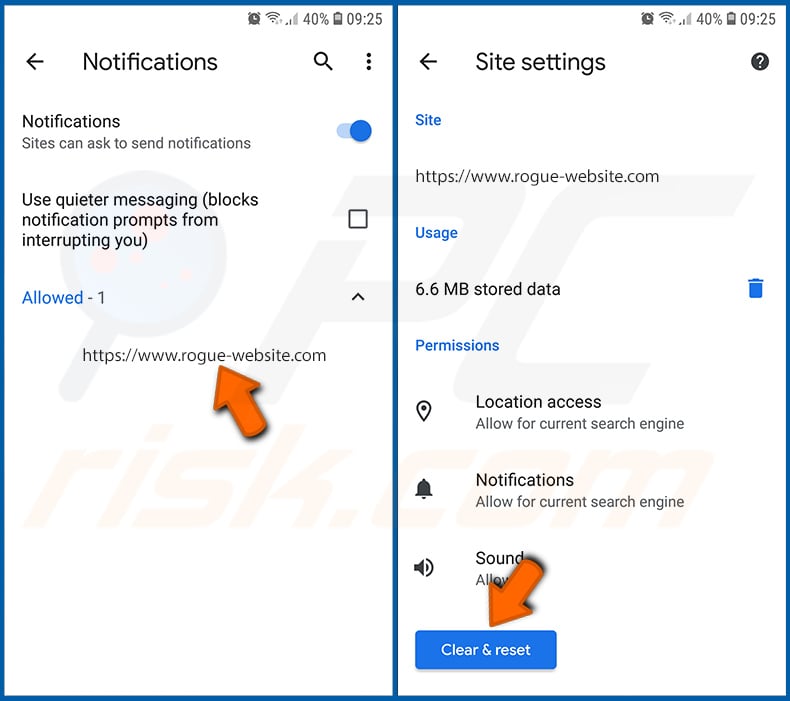
Find the websites that deliver browser notifications, tap on them and click "Clear & reset". This will remove permissions granted for these websites to deliver notifications. However, once you visit the same site again, it may ask for a permission again. You can choose whether to give these permissions or not (if you choose to decline the website will go to "Blocked" section and will no longer ask you for the permission).
Reset the Chrome web browser:
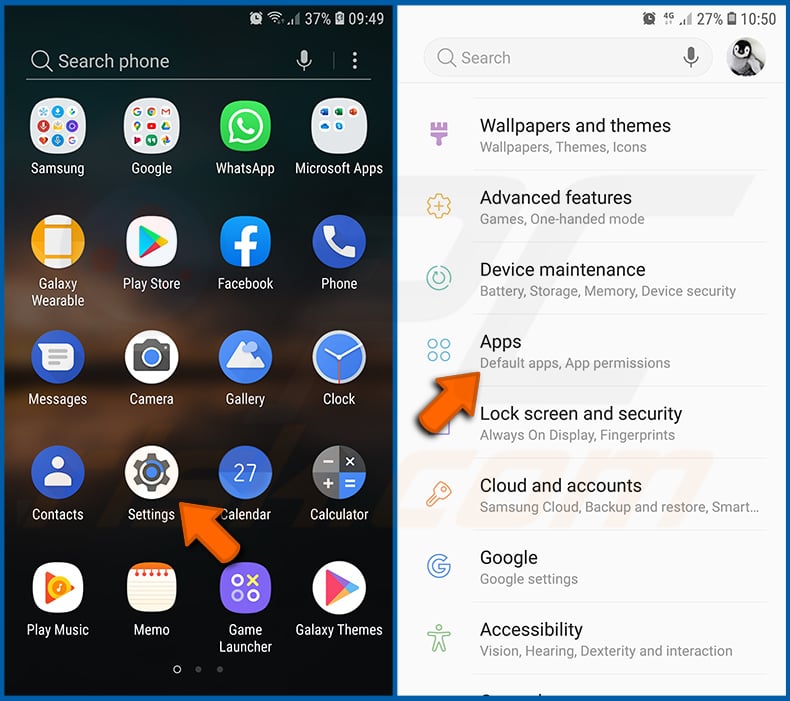
Go to "Settings", scroll down until you see "Apps" and tap it.
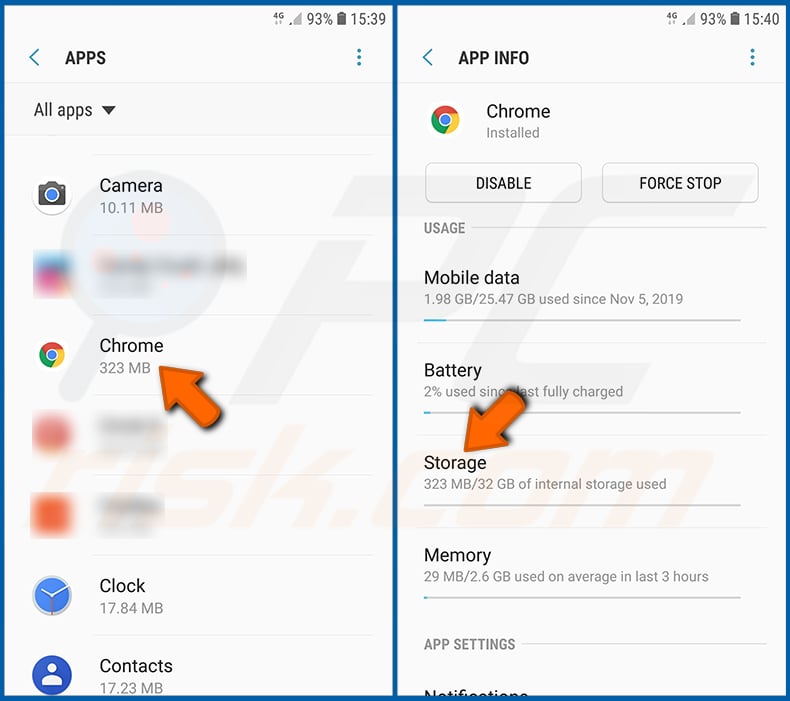
Scroll down until you find "Chrome" application, select it and tap "Storage" option.
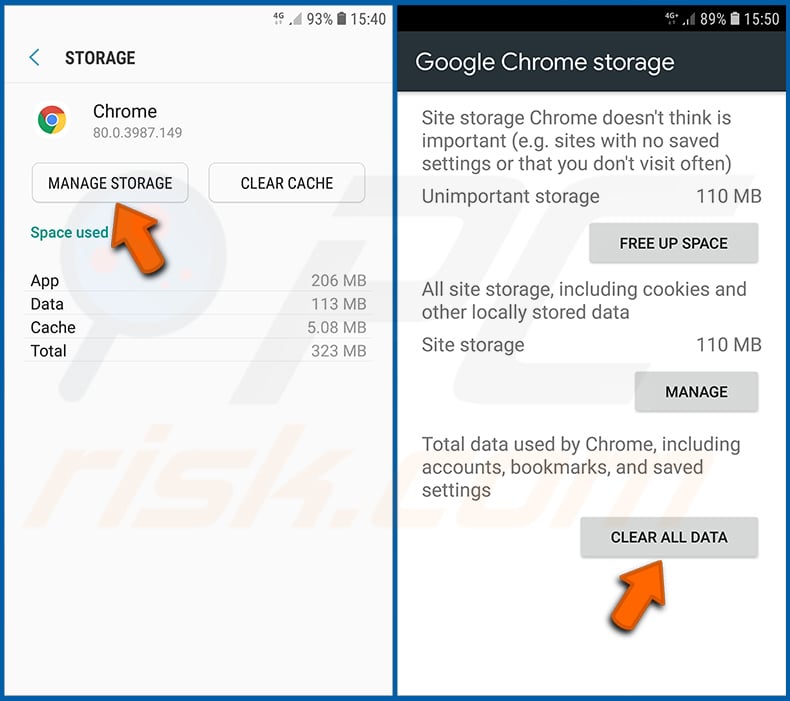
Tap "MANAGE STORAGE", then "CLEAR ALL DATA" and confirm the action by taping "OK". Note that resetting the browser will eliminate all data stored within. This means that all saved logins/passwords, browsing history, non-default settings and other data will be deleted. You will also have to re-login into all websites as well.
Delete browsing history from the Firefox web browser:
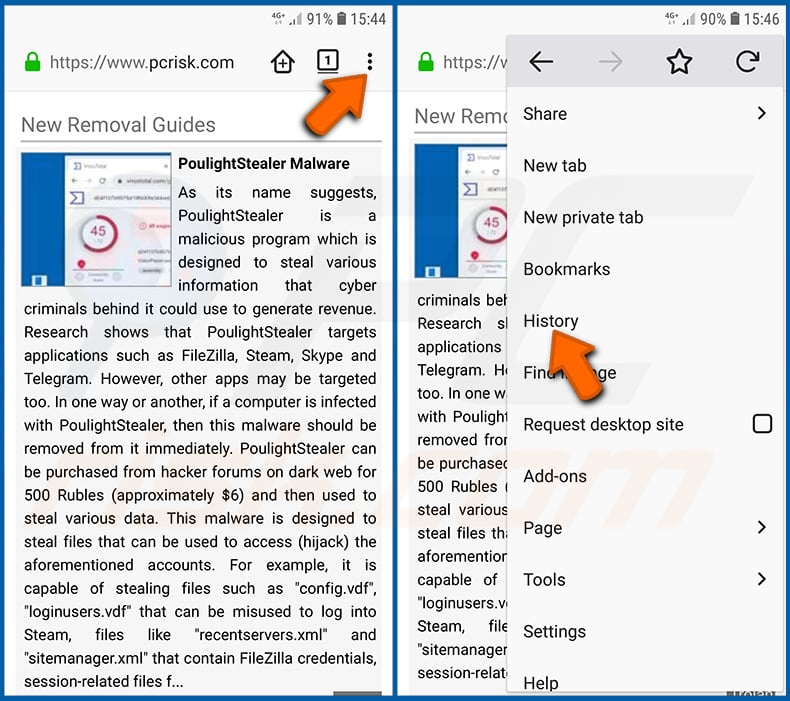
Tap the "Menu" button (three dots on the right-upper corner of the screen) and select "History" in the opened dropdown menu.
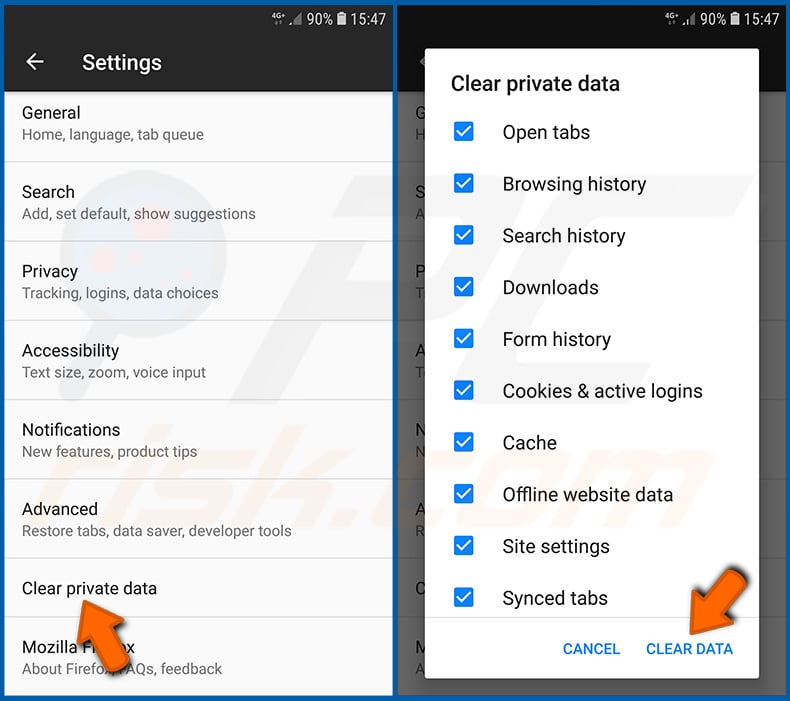
Scroll down until you see "Clear private data" and tap it. Select data types you want to remove and tap "CLEAR DATA".
Disable browser notifications in the Firefox web browser:
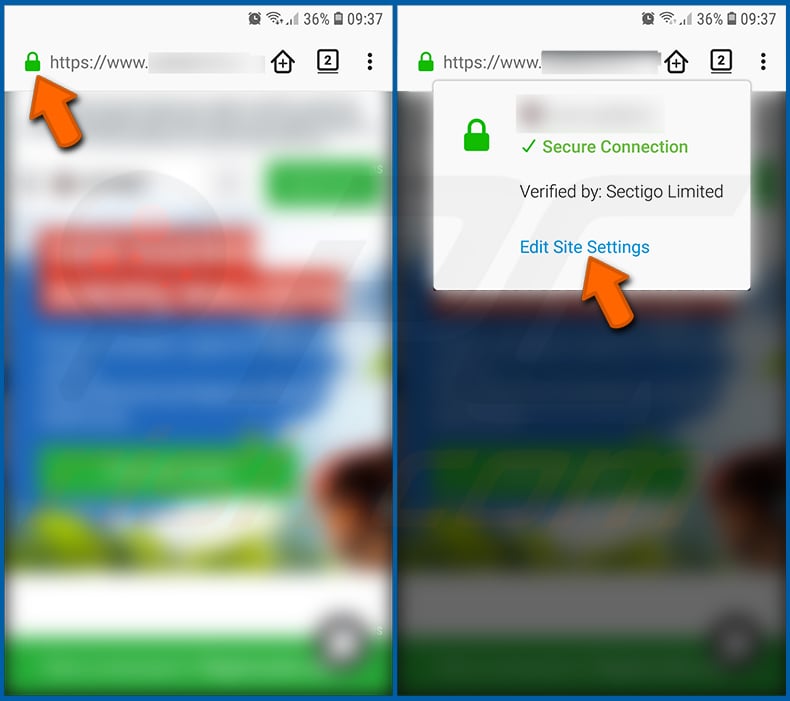
Visit the website that is delivering browser notifications, tap the icon displayed on the left of URL bar (the icon will not necessarily be a "Lock") and select "Edit Site Settings".
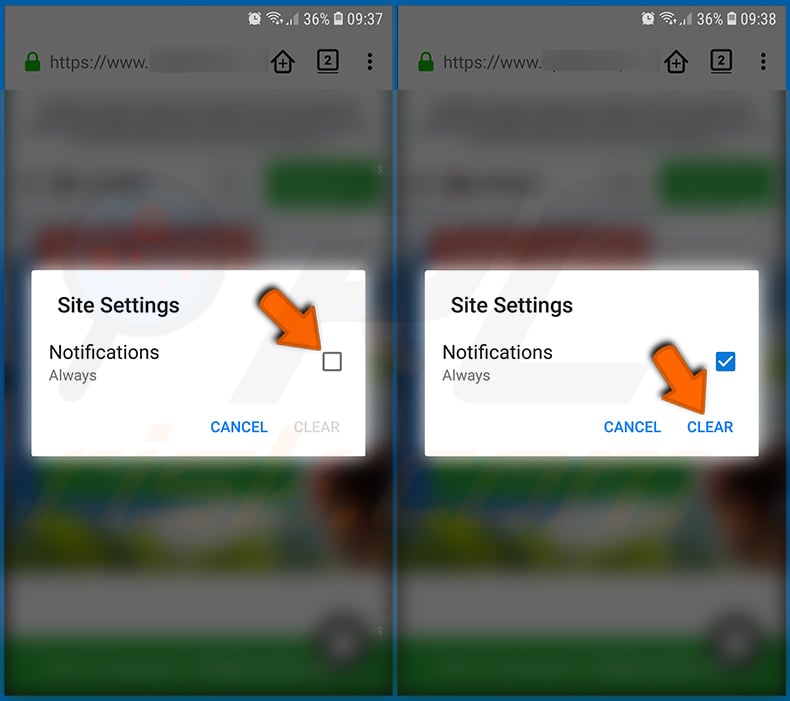
In the opened pop-up opt-in the "Notifications" option and tap "CLEAR".
Reset the Firefox web browser:
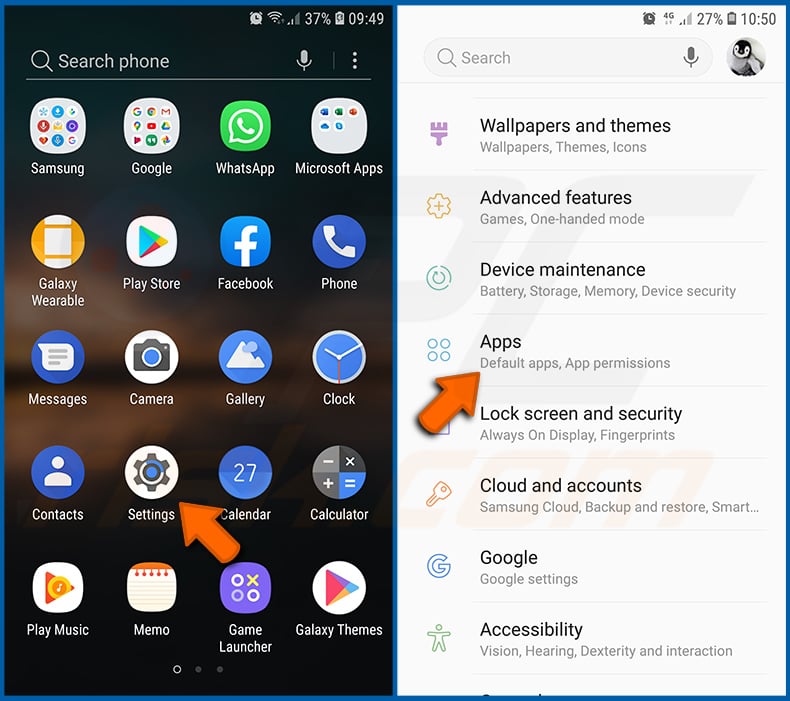
Go to "Settings", scroll down until you see "Apps" and tap it.
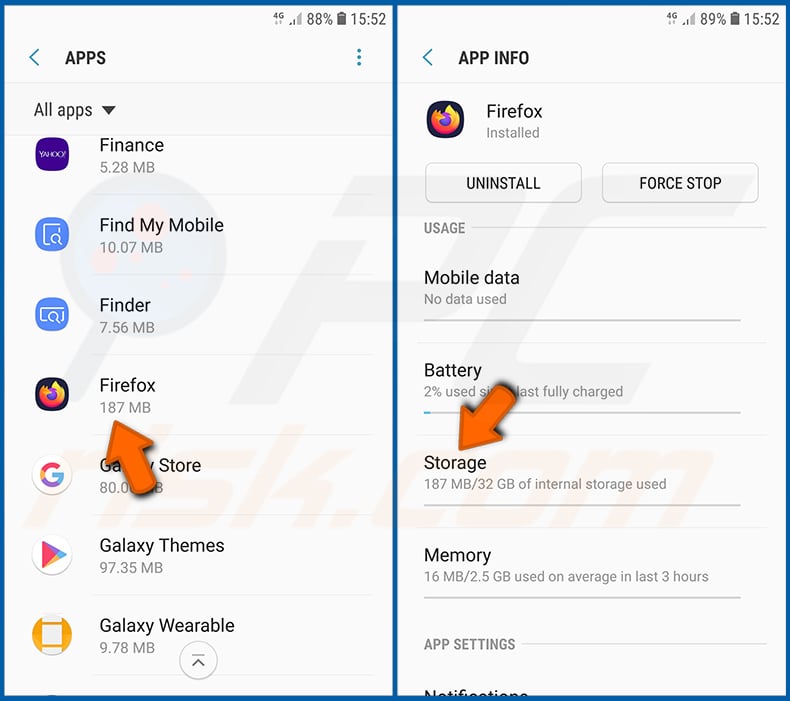
Scroll down until you find "Firefox" application, select it and tap "Storage" option.
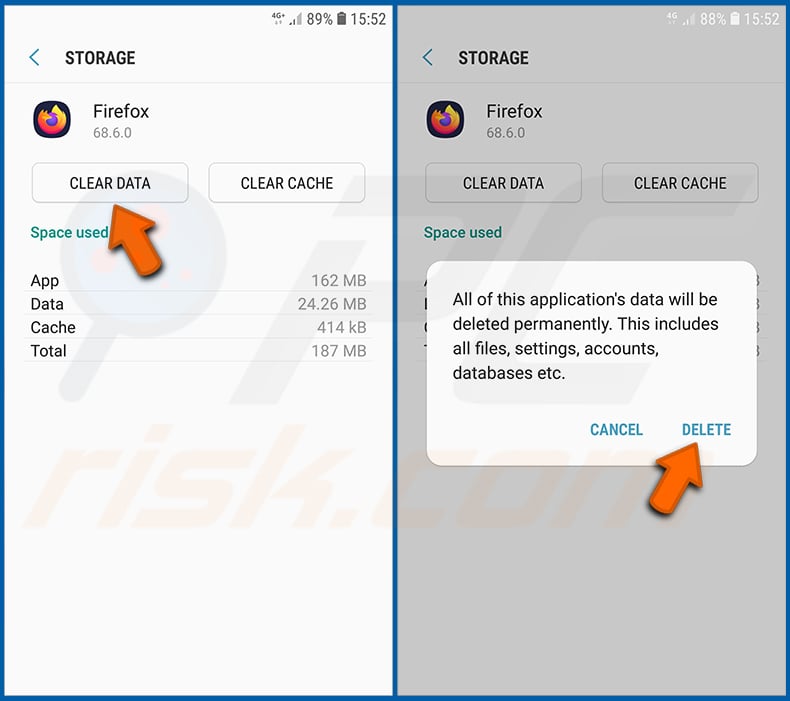
Tap "CLEAR DATA" and confirm the action by taping "DELETE". Note that resetting the browser will eliminate all data stored within. This means that all saved logins/passwords, browsing history, non-default settings and other data will be deleted. You will also have to re-login into all websites as well.
Uninstall potentially unwanted and/or malicious applications:
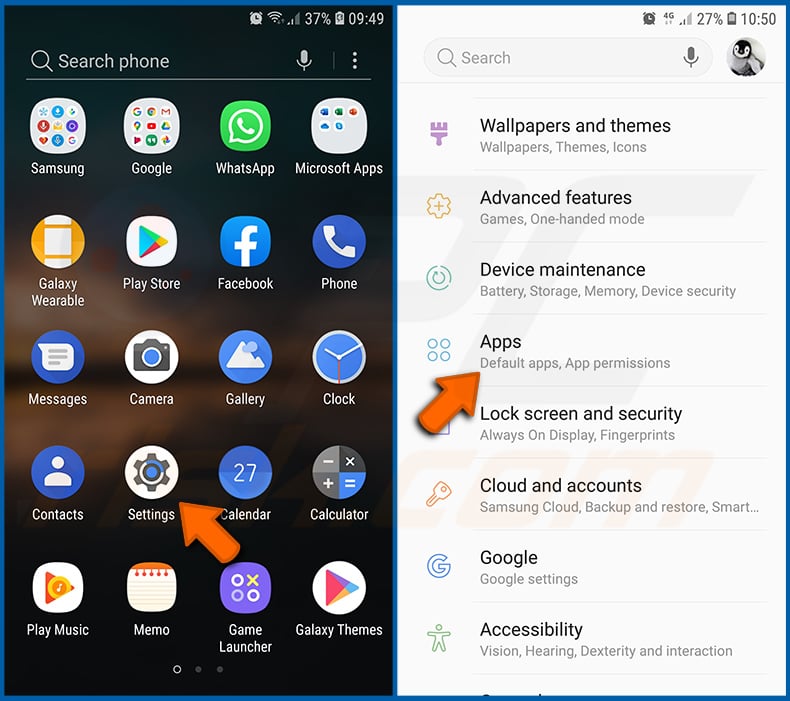
Go to "Settings", scroll down until you see "Apps" and tap it.
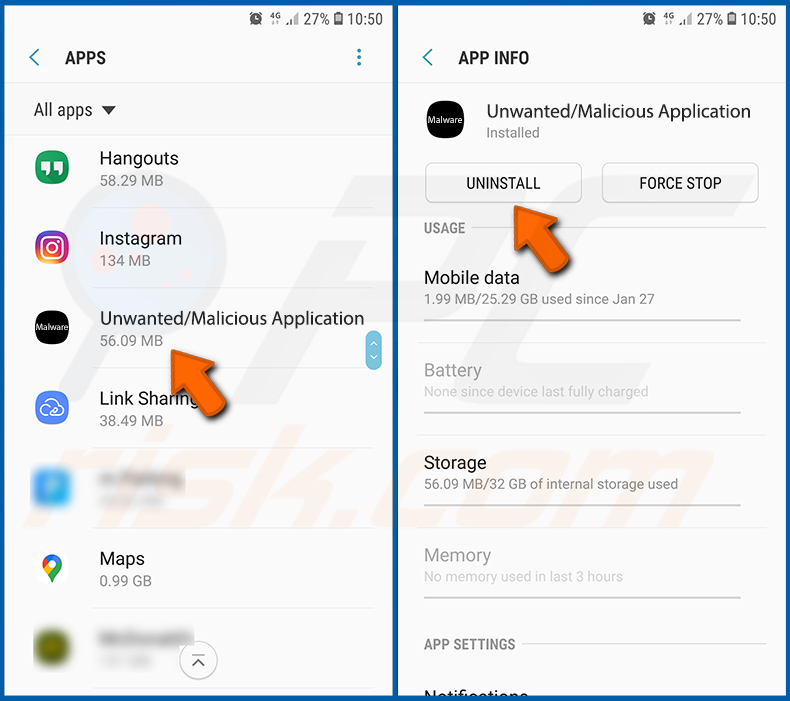
Scroll down until you see a potentially unwanted and/or malicious application, select it and tap "Uninstall". If, for some reason, you are unable to remove the selected app (e.g., you are prompted with an error message), you should try using the "Safe Mode".
Boot the Android device in "Safe Mode":
The "Safe Mode" in Android operating system temporarily disables all third-party applications from running. Using this mode is a good way to diagnose and solve various issues (e.g., remove malicious applications that prevent users you from doing so when the device is running "normally").
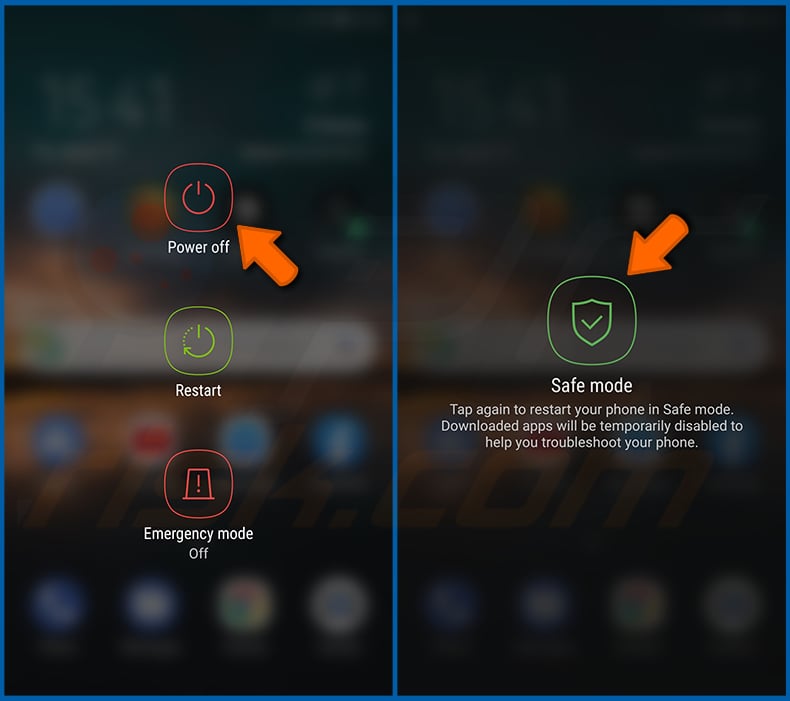
Push the "Power" button and hold it until you see the "Power off" screen. Tap the "Power off" icon and hold it. After a few seconds the "Safe Mode" option will appear and you'll be able run it by restarting the device.
Check the battery usage of various applications:
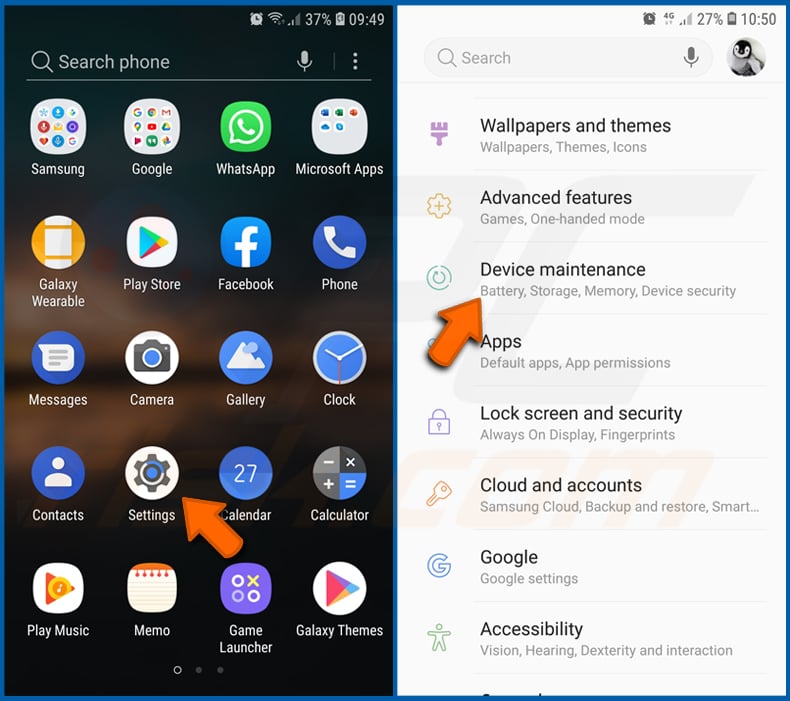
Go to "Settings", scroll down until you see "Device maintenance" and tap it.
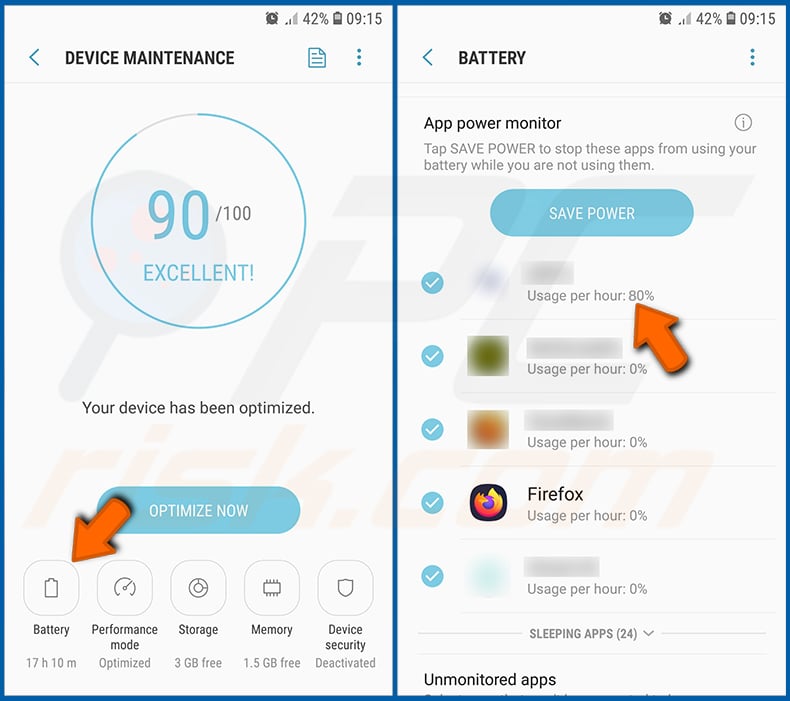
Tap "Battery" and check the usage of each application. Legitimate/genuine applications are designed to use as low energy as possible in order to provide the best user experience and to save power. Therefore, high battery usage may indicate that the application is malicious.
Check the data usage of various applications:
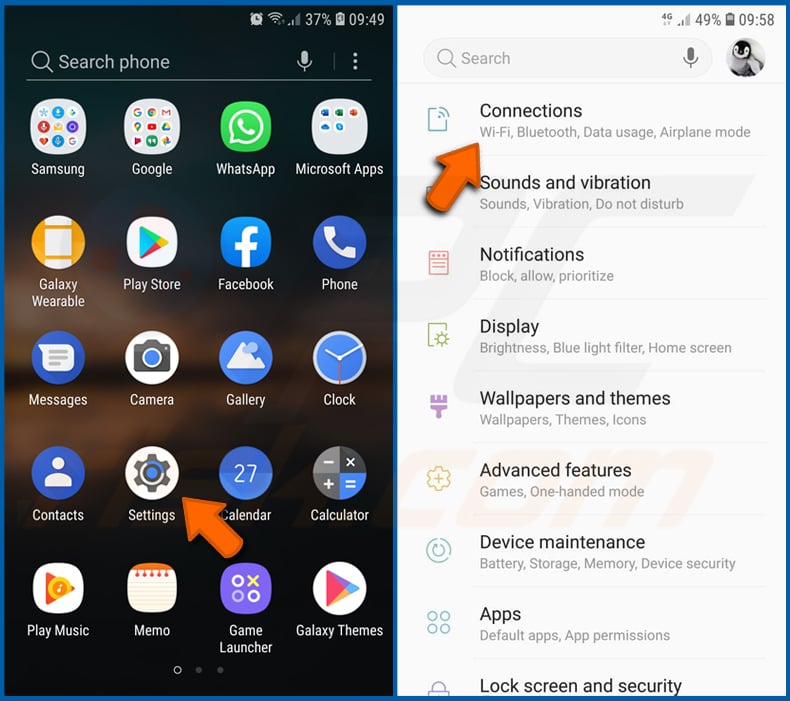
Go to "Settings", scroll down until you see "Connections" and tap it.
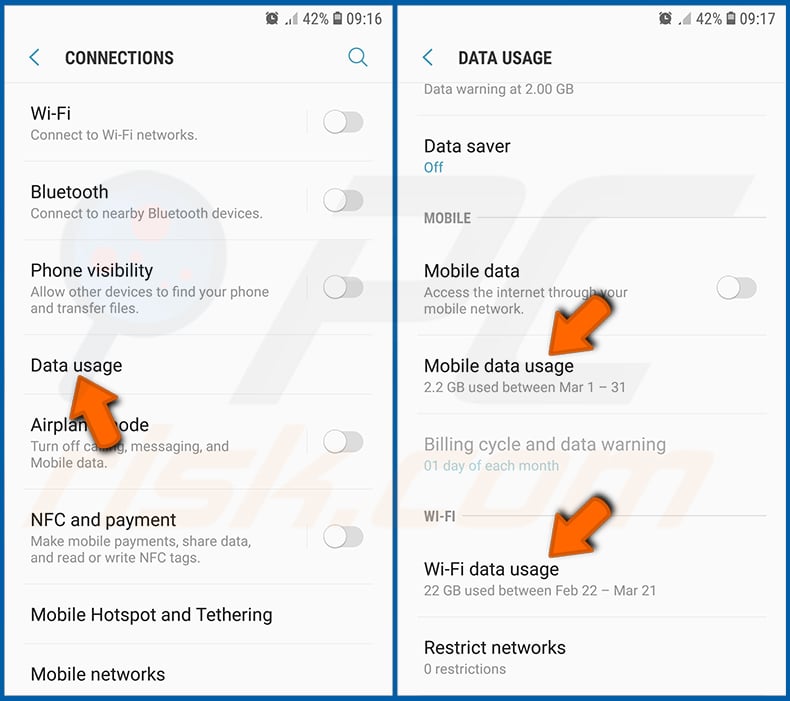
Scroll down until you see "Data usage" and select this option. As with battery, legitimate/genuine applications are designed to minimize data usage as much as possible. This means that huge data usage may indicate presence of malicious application. Note that some malicious applications might be designed to operate when the device is connected to wireless network only. For this reason, you should check both Mobile and Wi-Fi data usage.
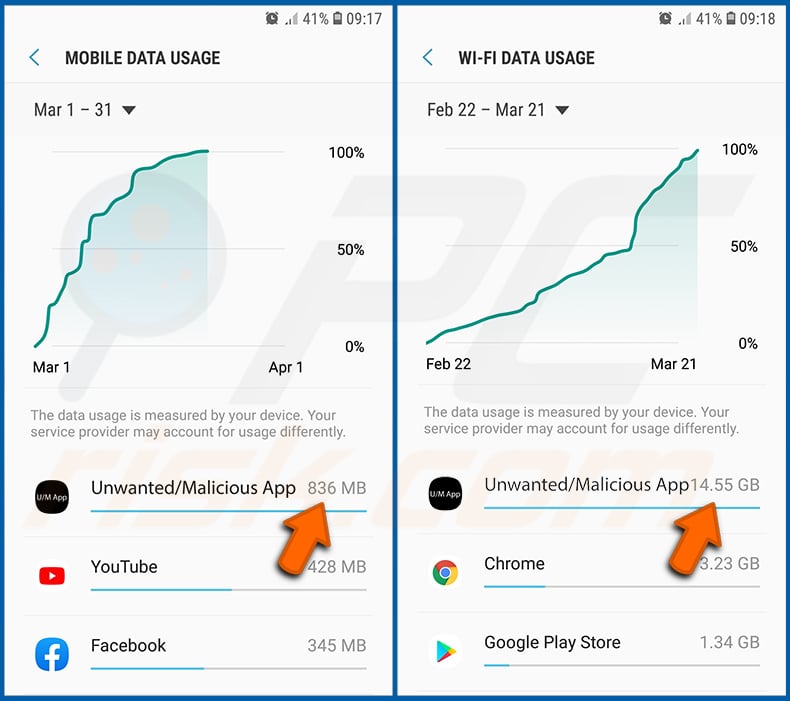
If you find an application that uses a lot of data even though you never use it, then we strongly advise you to uninstall it as soon as possible.
Install the latest software updates:
Keeping the software up-to-date is a good practice when it comes to device safety. The device manufacturers are continually releasing various security patches and Android updates in order to fix errors and bugs that can be abused by cybercriminals. An outdated system is way more vulnerable, which is why you should always be sure that your device's software is up-to-date.
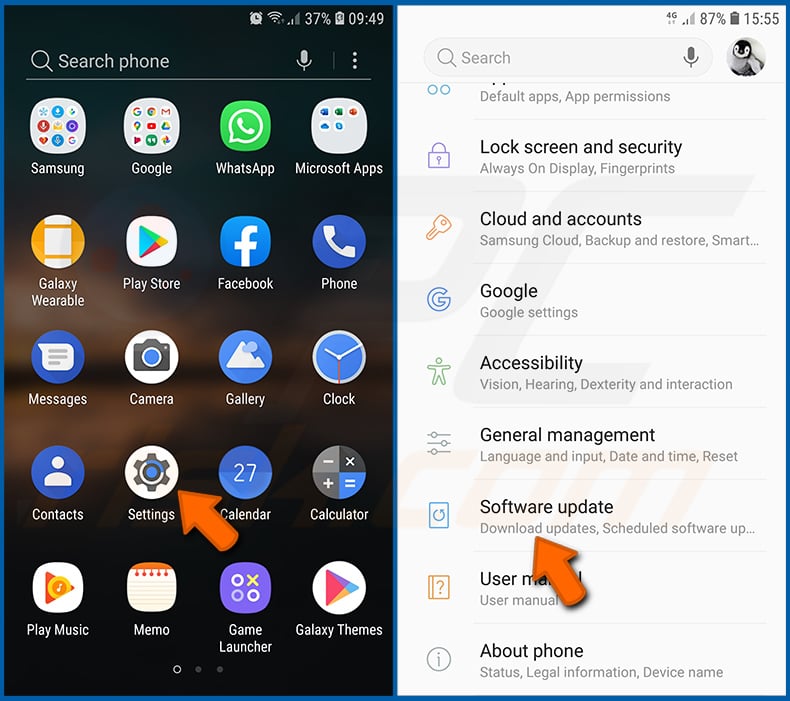
Go to "Settings", scroll down until you see "Software update" and tap it.
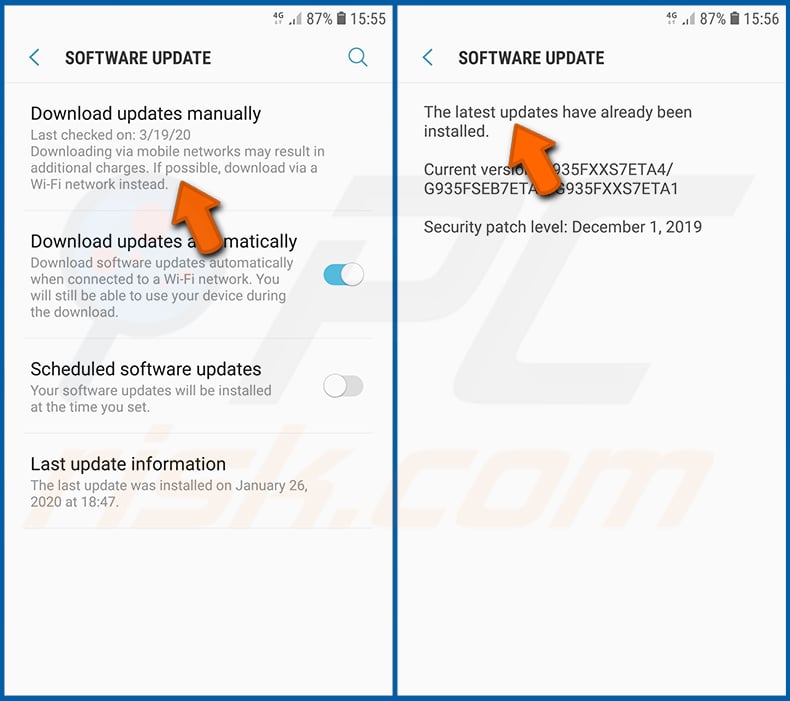
Tap "Download updates manually" and check if there are any updates available. If so, install them immediately. We also recommend to enable the "Download updates automatically" option - it will enable the system to notify you once an update is released and/or install it automatically.
Reset the system to its default state:
Performing a "Factory Reset" is a good way to remove all unwanted applications, restore system's settings to default and clean the device in general. However, you must keep in mind that all data within the device will be deleted, including photos, video/audio files, phone numbers (stored within the device, not the SIM card), SMS messages, and so forth. In other words, the device will be restored to its primal state.
You can also restore the basic system settings and/or simply network settings as well.
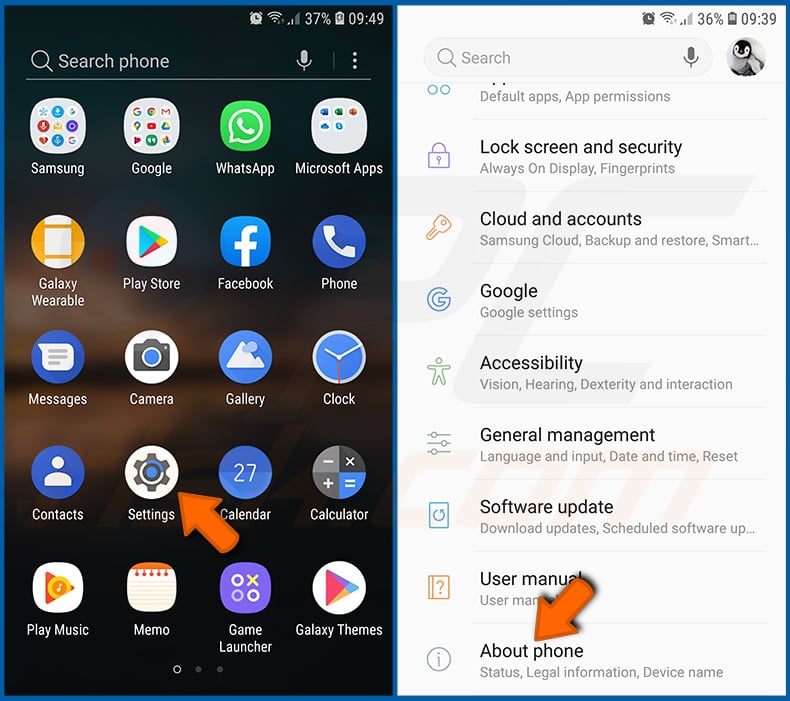
Go to "Settings", scroll down until you see "About phone" and tap it.
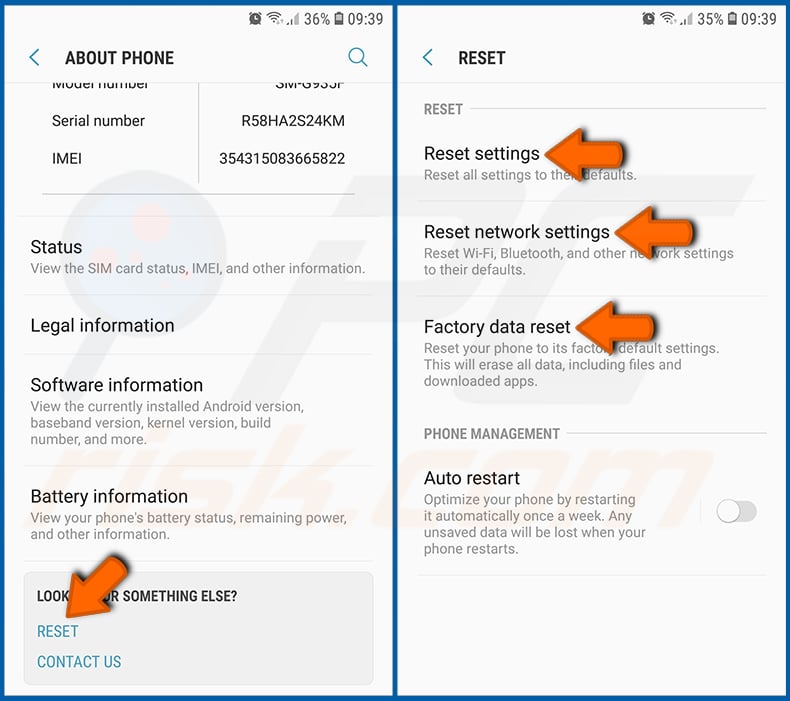
Scroll down until you see "Reset" and tap it. Now choose the action you want to perform:
"Reset settings" - restore all system settings to default;
"Reset network settings" - restore all network-related settings to default;
"Factory data reset" - reset the entire system and completely delete all stored data;
Disable applications that have administrator privileges:
If a malicious application gets administrator-level privileges it can seriously damage the system. To keep the device as safe as possible you should always check what apps have such privileges and disable the ones that shouldn't.
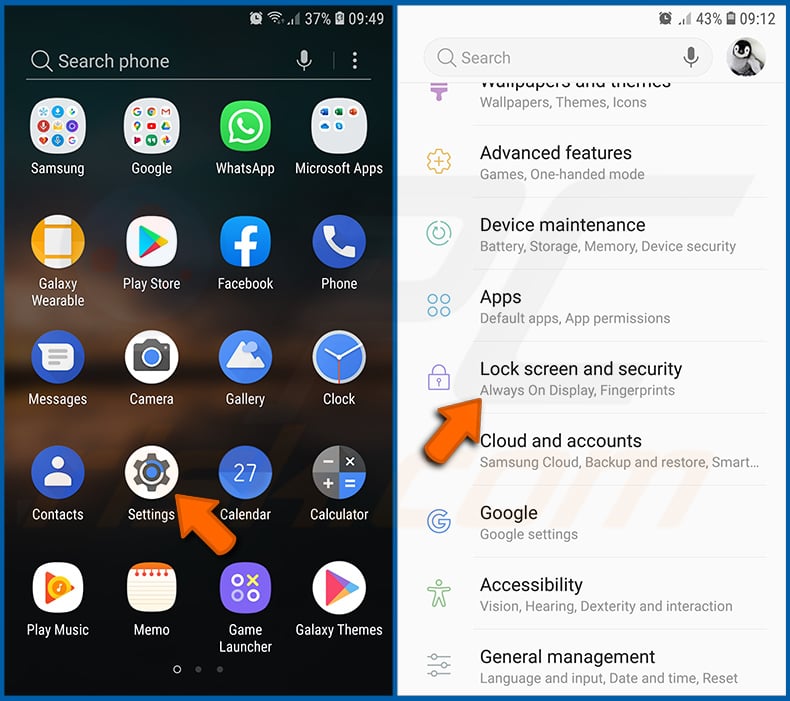
Go to "Settings", scroll down until you see "Lock screen and security" and tap it.
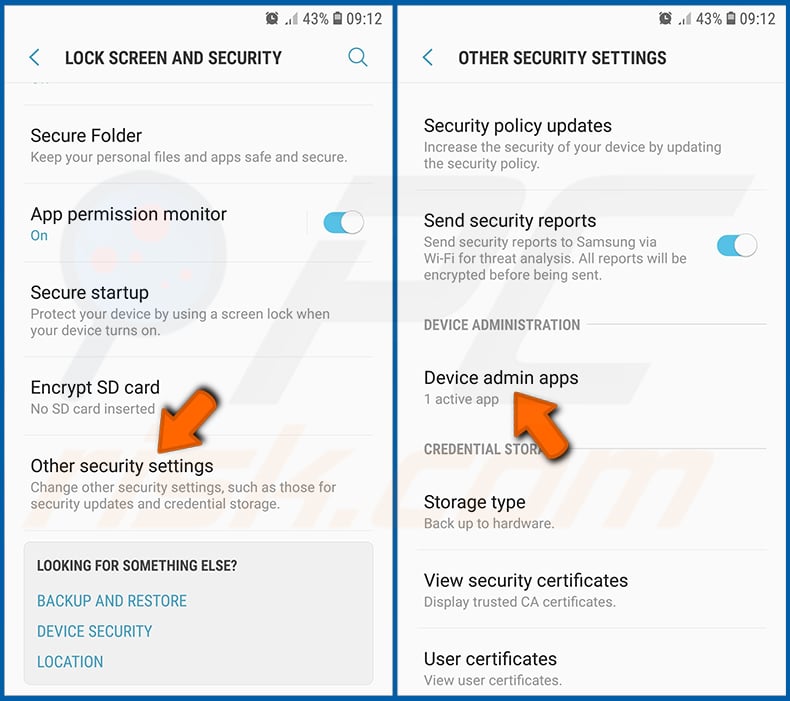
Scroll down until you see "Other security settings", tap it and then tap "Device admin apps".
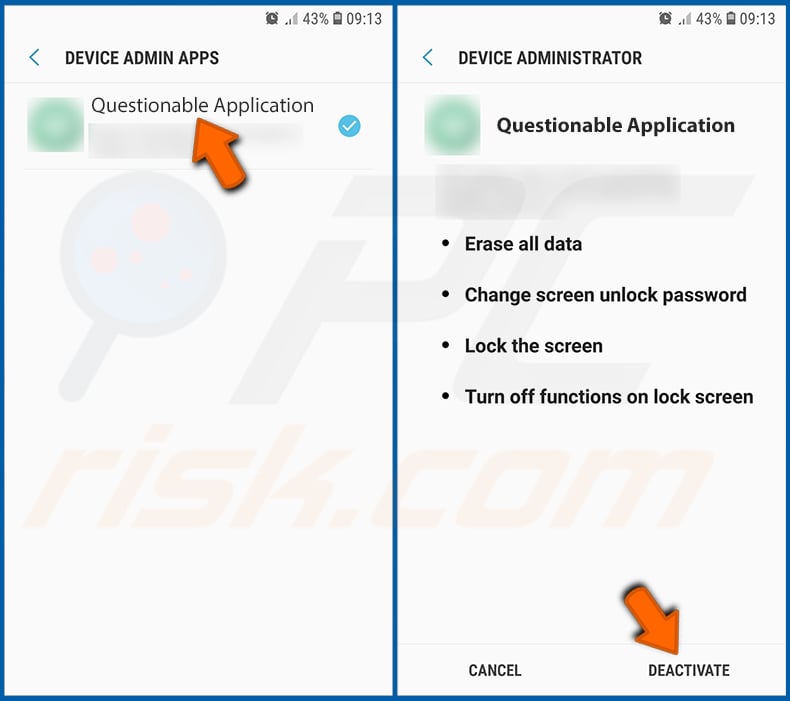
Identify applications that should not have administrator privileges, tap them and then tap "DEACTIVATE".
Frequently Asked Questions (FAQ)
My Android device is infected with RemControl malware, should I format my storage device to get rid of it?
Formatting is typically not necessary for removing RemControl. Running reputable mobile security software like Combo Cleaner should be sufficient to detect and eliminate the malware from your device.
What are the biggest issues that RemControl malware can cause?
RemControl can overlay fake banking login screens on top of your legitimate banking apps, stealing PINs, mobile banking codes, and card details.
It also streams your screen in real time to the operator, logs every tap and keystroke, captures your device unlock pattern, and blocks you from opening settings or factory resetting the phone. The end result can be unauthorized banking transactions, total loss of account access, and identity theft.
What is the purpose of RemControl malware?
RemControl is primarily designed for banking fraud. Its operator uses it to steal banking credentials and take remote control of infected devices to carry out unauthorized transactions. That said, cybercriminals may also be motivated by personal grudges, hacktivism, or geopolitical interests in some cases.
How did RemControl malware infiltrate my Android device?
RemControl is distributed through fake Google Play Store pages impersonating the TVTap IPTV application, promoted via malvertising campaigns on Meta's platform.
Android malware is also commonly spread through third-party app stores, phishing links shared by SMS or social media, and fake software update prompts. Always download apps exclusively from the official Google Play Store.
Will Combo Cleaner protect me from malware?
Combo Cleaner is capable of detecting and eliminating nearly all known malware infections. Remember that performing a complete system scan is essential, as sophisticated threats like RemControl typically embed themselves deep within the system to avoid easy removal.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion