Step-by-Step Malware Removal Instructions

TRIPAUL3 RAT
Trojan

TRIPAUL3 RAT

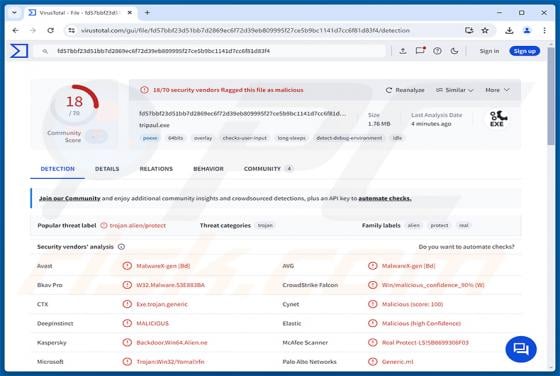
TRIPAUL3 is a modular Remote Access Trojan (RAT) for 64-bit Windows, written in C++, that gives attackers extensive remote control over infected machines. The malware stores its configuration and six encrypted plugins inside the executable's overlay - a region of the file that sits beyond the sta
Xaman Airdrop Scam
Phishing/Scam

Xaman Airdrop Scam

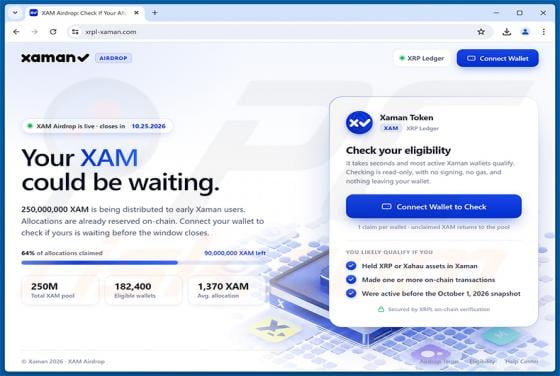
Upon examining xrpl-xaman[.]com, our researchers found it masquerades as an official Xaman wallet airdrop portal. The site claims to distribute 250,000,000 XAM tokens to early users, but it is a fraudulent page designed to drain cryptocurrency from anyone who connects their wallet. IMPORTANT

Inbound Message Rejection Report Email Scam
Phishing/Scam

Inbound Message Rejection Report Email Scam

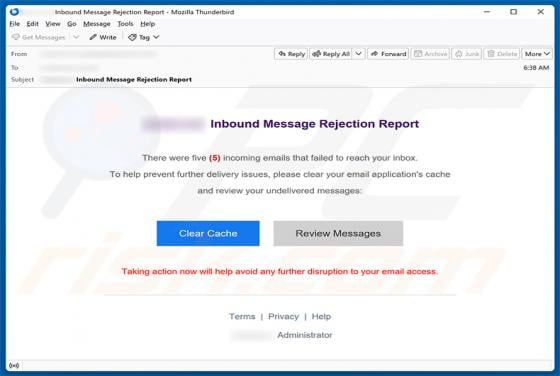
We have examined this email and concluded it is a phishing scam. It is disguised as an automated alert from the recipient's email administrator, falsely claiming that several incoming messages could not be delivered. The aim is to lure recipients into entering their email login credentials on a fa

Progress Claim For Review And Certification Email Virus
Phishing/Scam

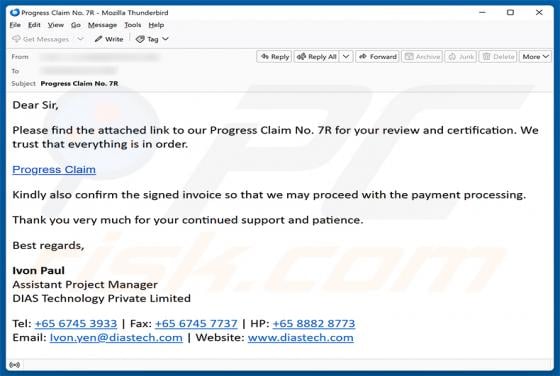
Progress Claim For Review And Certification Email Virus

We have inspected this email and determined that it is malspam. The message poses as a routine business communication requesting document review, but its real purpose is to trick recipients into downloading malware. It should be ignored and deleted. The email carries the subject "Progress

Encrypted Message From Human Resource Email Scam
Phishing/Scam

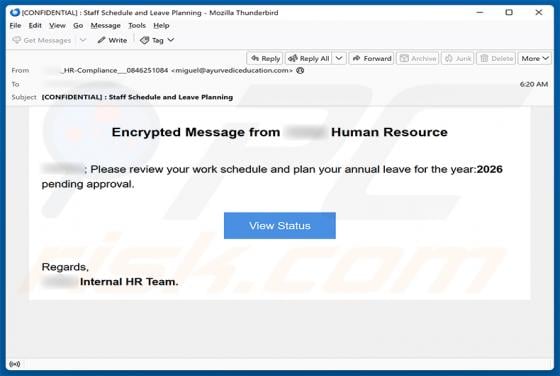
Encrypted Message From Human Resource Email Scam

We examined this email and determined it is a phishing scam. The message poses as a confidential HR notification about staff scheduling and annual leave planning, and contains a link leading to a fake Zoho credential verification page. It should be ignored to avoid having login credentials stolen.

Penumbra Stealer
Trojan

Penumbra Stealer

Penumbra Stealer is an information stealer that silently harvests credentials, session data, and sensitive files from infected Windows computers. It targets saved passwords, browser cookies, messaging platform tokens, gaming accounts, and system-level authentication data. The stealer supports 13

Nyxar Stealer
Trojan

Nyxar Stealer

Nyxar Stealer is an information stealer sold to cybercriminals as a subscription service. It harvests saved credentials and session data from web browsers, messaging apps, cryptocurrency wallets, and gaming platforms, and sends the stolen information to the attacker. Besides stealing data, Nyxar

Webmail Redesigned Email Scam
Phishing/Scam

Webmail Redesigned Email Scam

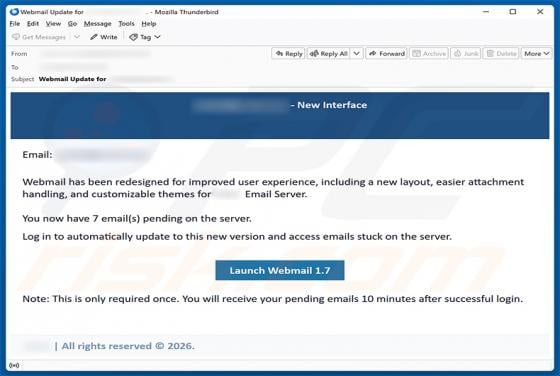
We have examined this email and determined it is a phishing scam. It is disguised as an official notification about a webmail interface redesign, urging recipients to log in and retrieve emails supposedly stuck on the server. The goal is to steal email account credentials through a fake login page

cPanel Needs More Disk Space Email Scam
Phishing/Scam

cPanel Needs More Disk Space Email Scam

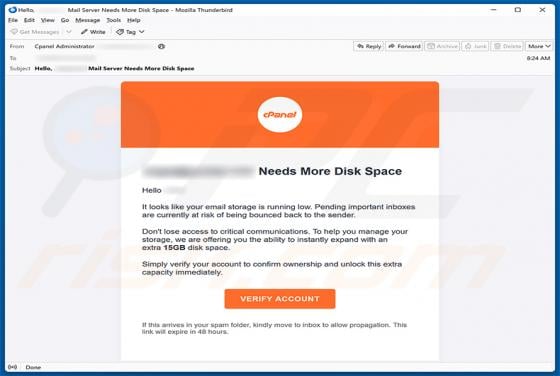
We have inspected this email and determined that it is a phishing scam. The message is disguised as an official notification from cPanel, falsely claiming that the recipient's email storage is nearly full. Its goal is to trick users into visiting a fraudulent website and handing over their email l

Coffin Locker Ransomware
Ransomware

Coffin Locker Ransomware

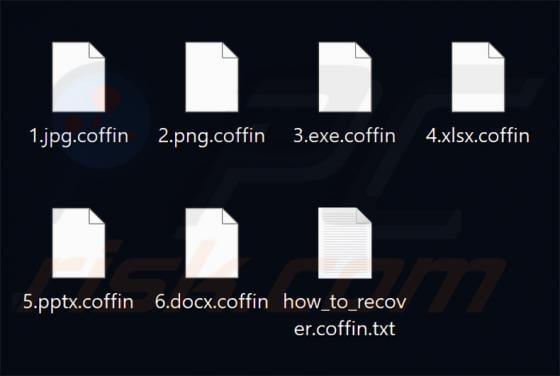
Coffin Locker is ransomware our research team found while inspecting new submissions on VirusTotal. It encrypts victim files, appends the .coffin extension, drops a ransom note text file in every directory, and replaces the desktop wallpaper. On our test machine, Coffin Locker encrypted files and