Step-by-Step Malware Removal Instructions

XRP Ledger Airdrop Scam
Phishing/Scam

XRP Ledger Airdrop Scam

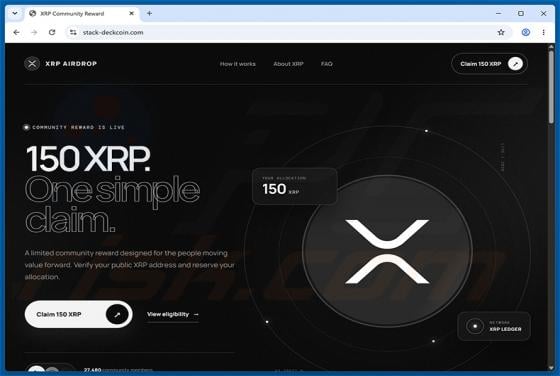
While examining suspicious websites, our researchers identified stack-deckcoin[.]com, a fraudulent page promoting a fake XRP community reward. The site falsely claims visitors are eligible to claim 150 XRP tokens for free, but its actual purpose is to steal cryptocurrency by tricking users into co
Citrus Ransomware
Ransomware

Citrus Ransomware

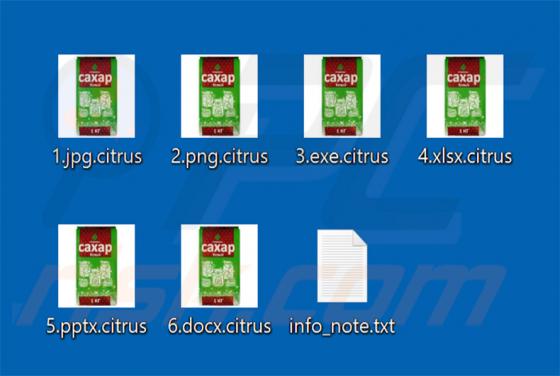
Citrus Ransomware is ransomware our research team discovered while examining new file submissions to the VirusTotal website. It encrypts victims' files to make them inaccessible and demands payment in exchange for a decryption tool. Beyond encrypting files, Citrus ransomware changes the desktop w

Become Secured Sender Email Scam
Phishing/Scam

Become Secured Sender Email Scam

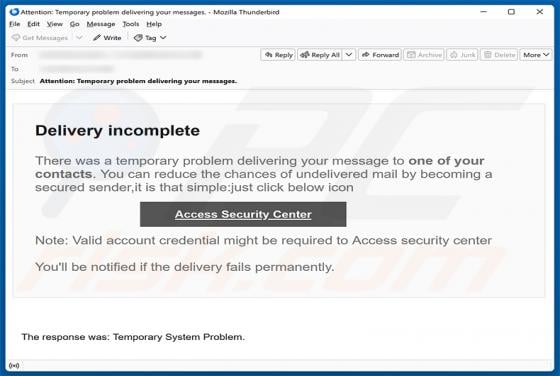
After examining this email, we concluded it is a phishing scam. The message poses as an automated notification from an email service provider, warning of a temporary delivery problem and urging the recipient to click a link to become a "secured sender." The goal is to steal email login credentials

Security-Related Issue Email Scam
Phishing/Scam

Security-Related Issue Email Scam

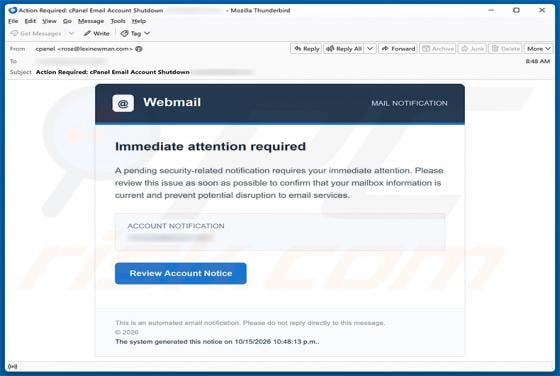
We have inspected this email and found that it is a phishing scam. The message is disguised as an urgent notification from cPanel, falsely claiming that the recipient's email account is about to be shut down due to a security-related issue. It is designed to trick recipients into entering their em

AgtaBackup RAT
Trojan

AgtaBackup RAT

AgtaBackup RAT is a Remote Access Trojan (RAT) built on the .NET 8.0 platform. Once installed, it gives attackers complete, hidden control over the infected computer and can also steal saved passwords, cookies, and other sensitive data. According to research published by Unit 42 (Palo Alto Networ

AvisLoader Malware
Trojan

AvisLoader Malware

AvisLoader is a Windows malware loader - a program whose main job is to get a foothold on a computer and then download and run other malicious software on it. It was described by Varonis Threat Labs after researchers came across an exposed staging server holding the loader, its helper tools, a fak

Hirudo Banking Trojan (Android)
Trojan

Hirudo Banking Trojan (Android)

Hirudo is an Android banking trojan with remote access capabilities. According to research published by ThreatFabric's Mobile Threat Intelligence team, it combines on-device credential theft with live remote control of the infected device. Hirudo is distributed through lure apps disguised as shopp

Hexsomeware Ransomware
Ransomware

Hexsomeware Ransomware

Hexsomeware is ransomware our research team identified while examining new malware samples submitted to VirusTotal. It encrypts files, appends a .hexsomeware extension to filenames, and presents ransom demands through a full-screen pop-up and a dropped text file. On our test machine, every encryp

Has Ransomware
Ransomware

Has Ransomware

Has is a ransomware-type program and a member of the Dharma ransomware family. Our research team identified it while analyzing new malware submissions on VirusTotal. It encrypts victim files and demands payment for decryption, also threatening to leak data it claims to have stolen. On our test ma

Lunex Stealer
Trojan

Lunex Stealer

Lunex Stealer is an information stealer that grabs saved passwords, cookies, credit card details, and cryptocurrency wallet data from infected Windows computers. It is part of the Lunex platform, which is sold to cybercriminals as Malware-as-a-Service, meaning different criminal groups rent the sa