

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What is Torrent Movies Virus?
Torrent Movies Virus is the generic name of malware that disguises itself as a video format file. In fact, it is a Windows shortcut. Cyber criminals proliferate the virus via The Pirate Bay torrent tracker, which is notorious for distribution of malware and potentially unwanted applications (PUAs).
Torrent Movies Virus is a high-risk virus that poses a significant threat to your privacy, finances, and computer safety.
As mentioned above, the Torrent Movies Virus is distributed using a Windows shortcut (.LNK file), which appears to be a video file.
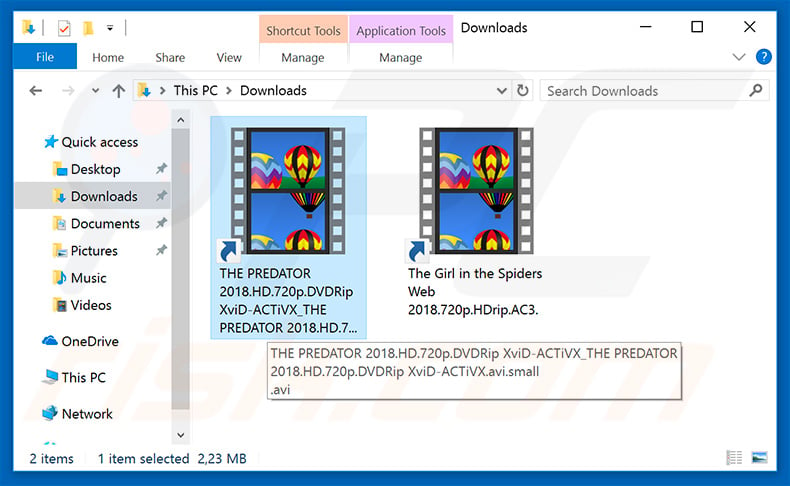
Cyber criminals disguise the malicious shortcut by adding a legitimate file name (for example, at time of research, two names used were "The Girl in the Spiders Web 2018.720p.HDrip.AC3.lnk" and "THE PREDATOR 2018.HD.720p.DVDRip XviD-ACTiVX_THE PREDATOR 2018.HD.720p.DVDRip XviD-ACTiVX.avi.small.lnk).
Many users do not notice that the downloaded 'movie' extension is .LNK, rather than an .avi, .mp4, or other video format. Once opened, the shortcut executes a number of PowerShell commands that infect the system. The downloaded malware performs malicious actions. Firstly, it injects web browsers and visited websites with JavaScript scripts that modify displayed content.
The Google and Yandex web search engines are just a few examples of these modified sites. The injected script displays intrusive advertisements and changes the displayed search results by delivering those determined by cyber criminals. Therefore, users are fed with false search results.
This is typically done to make users visit malicious websites (which will lead to even more computer infections) and to promote various websites and generate revenue via affiliate programs and/or advertising. In addition, Torrent Movies Virus modifies the content of the Wikipedia website. This malware inserts a message onto the site asking for a donation.
The message essentially states that Wikipedia is a non-profit organization, and thus never feeds users with advertisements. The website supposedly "survives" on donations only and receives very low income. Therefore, users are asked to donate to help developers take care of the site. The donation must be transferred to a Bitcoin or Ethereum cryptocurrency wallet.
Again, this is a scam - criminals attempt to trick users by appealing to their credulity and generosity. Torrent Movies Virus also contains another high-risk feature: it detects when the user is visiting cryptowallet websites used to transfer cryptocurrency. It steals cryptocurrency by changing the recipient wallet's address to one belonging to cyber criminals.
Cryptocurrency wallet addresses are long strings of random characters and digits, and thus users are unlikely to notice any changes (all this is performed immediately the user attempts to paste a copied cryptowallet address). In summary, users end up transferring cryptocurrency to cyber criminals, rather than their intended recipient.
Ultimately, the presence of this malware can lead to various issues: users' computers might be infected with even more viruses, the browsing experience is diminished (they encounter intrusive advertisements, false search results, pop-ups, etc.), and their money (cryptocurrency) might be stolen. Therefore, eliminating Torrent Movies Virus is paramount.
If you have recently downloaded movies using The Pirate Bay or another torrent tracker, we strongly advise you to scan the system with a reputable anti-virus/anti-spyware suite and eliminate all detected threats. Be aware that these download sources are often used to proliferate viruses.
Furthermore, this type of piracy is considered to be a cyber crime - it violates copyright law. Therefore, never download any illegal copies of media (music, movies, eBooks, etc.) or cracked software/games using torrents and other unofficial software download sources. In doing so, you simply steal from the copyright owner and put your system at risk.
| Name | Torrent Movies malware |
| Threat Type | Trojan, Password stealing virus, Banking malware, Spyware |
| Symptoms | Trojans are designed to stealthily infiltrate victim's computer and remain silent thus no particular symptoms are clearly visible on an infected machine. |
| Distribution methods | Infected email attachments, malicious online advertisements, social engineering, software cracks. |
| Damage | Stolen banking information, passwords, identity theft, victim's computer added to a botnet. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
There are dozens of viruses that steal information, deliver advertisements, cause unwanted redirects, inject additional malware, and perform other malicious actions. The list of examples includes (but is not limited to) Vidar, Hancitor, TrickBot, FormBook, Adwind, and AZORult.
These viruses are developed by different cyber criminals and their behavior may also differ slightly. Nevertheless, they all pose a significant threat to your privacy and browsing safety. For this reason, eliminate them immediately.
How did Torrent Movies Virus infiltrate my computer?
As mentioned above, Torrent Movies Virus is mainly distributed using The Pirate Bay torrent tracker, however, using peer-to-peer (P2P) networks to proliferate these viruses is one of many popular methods used by cyber criminals. The malware is also proliferated using spam email campaigns, trojans, fake software update tools, and various unofficial download sources.
Spam emails deliver malicious attachments (executables, archives, MS Office documents, PDFs, and so on) that, once opened, download and install malware. Trojans cause so-called "chain infections". They essentially infiltrate the system and continue to inject other malware.
Fake updaters infect computers by exploiting old software bugs/flaws or simply downloading and installing malware rather than updates.
Unofficial download sources (free file hosting websites, freeware download websites, and so on) present malicious executables as legitimate, thereby tricking users into downloading and installing malware. In summary, the main reasons for computer infections are poor knowledge of these threats and careless behavior.
How to avoid installation of malware?
The key to computer safety is caution. Therefore, pay attention when browsing the internet and downloading, installing, and updating software. Think twice before opening email attachments. If the file seems irrelevant or the sender's email address is suspicious/unrecognizable, do not open any file.
Furthermore, download your programs from official sources only, using direct download links. Third party downloaders/installers often include rogue apps, and thus these tools should never be used. The same applies to software updates.
It is important to keep installed applications updated, however, this should be achieved using implemented functions or tools provided by the official developer.
Having a reputable anti-virus/anti-spyware suite installed and running is also essential, since these tools can detect and eliminate malware before it does any harm. If you believe that your computer is already infected, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate infiltrated malware.
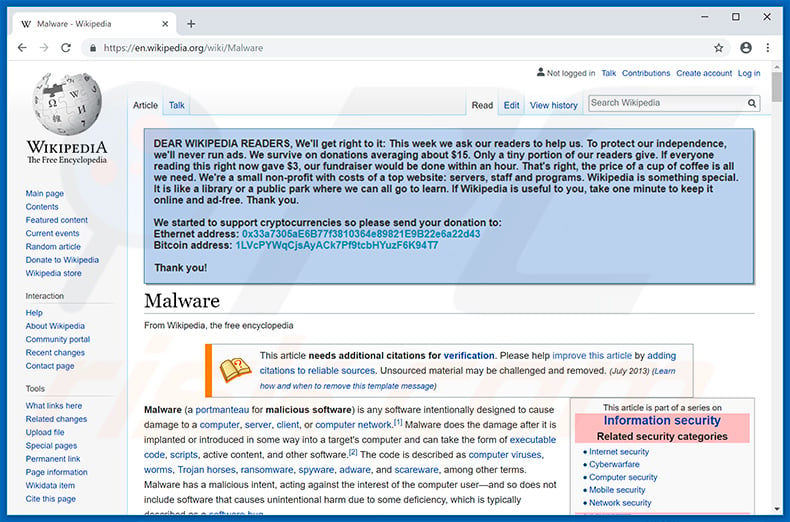
A quote of scam message asking for a donation in Wikipedia website:
DEAR WIKIPEDIA READERS, We'll get right to it: This week we ask our readers to help us. To protect our independence, we'll never run ads. We survive on donations averaging about $15. Only a tiny portion of our readers give. If everyone reading this right now gave $3, our fundraiser would be done within an hour. That's right, the price of a cup of coffe is all we need. We're a small non-profit with costs of a top website: servers, staff and programs. Wikipedia is something special. It is like a library or a public park where we can all go to learn. If Wikipedia is useful to you, take one minute to keep it online and ad-free. Thank you.
We started to support cryptocurrencies so please send your donation to:
Ethernet: 0x33a7305aE6B77f3810364e89821E9B22e6a22d43
Bitcoin: 1LVcPYWqCjsAyACk7Pf9tcbHYuzF6K94T7Thank you!
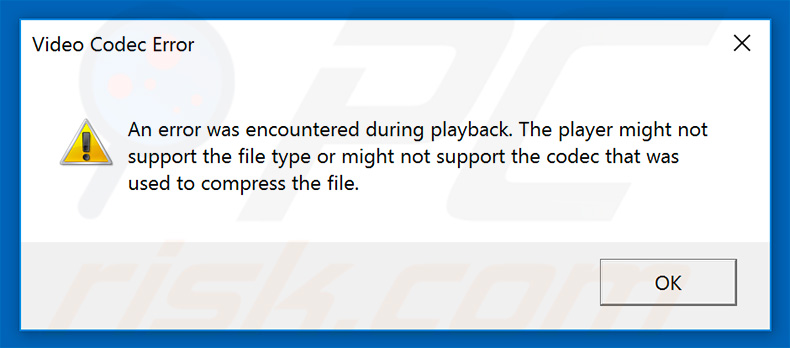
Once opened, the malicious .LNK file displays a fake error message stating that the "video file" cannot be opened because it is not supported:
Examples of malicious .LNK files used to spread Torrent Movies Virus:
How to remove malware manually?
Most trojan infections can be removed by running a full system scan with Combo Cleaner. The full manual procedure below is for cases where automatic removal failed, where you want to verify a scan caught everything, or where the threat has multiple persistence points.
Disconnect from the network
Unplug your Ethernet cable and turn off Wi-Fi. If you're on a laptop, the airplane-mode key works fastest.
Many trojans exfiltrate data - saved browser passwords, banking sessions, screenshots - and accept remote commands. Cutting the network stops both immediately. Keep it disconnected until Phase 4.
Boot into Safe Mode with Networking
Safe Mode loads a minimal set of drivers and stops most malware from auto-running. "With Networking" lets you download tools - re-enable Wi-Fi only after you've booted in.
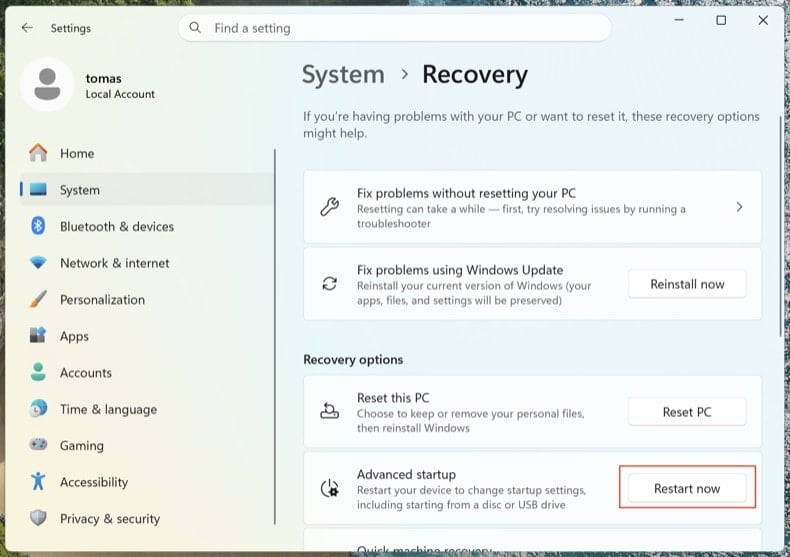
Open . Click Restart now next to Advanced startup.
Your computer will restart into the "Choose an option" menu. Click . After the second reboot, press 5 or F5.
Click the Windows logo, hold Shift, click the Power icon and choose Restart. In the Choose an option screen, click . Press F5.
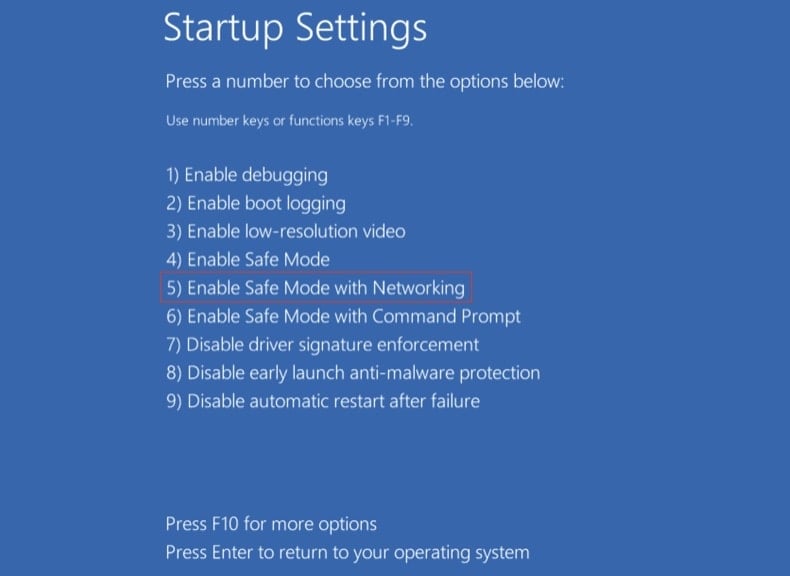
Windows 8
Go to the Start Screen, type Advanced, select Settings → Advanced startup options → Restart now → Troubleshoot → Advanced options → Startup settings → Restart → F5.
Note: Windows 8 reached end-of-life in January 2023 - running on it puts you at much higher risk of reinfection.
Windows 7
Click Start → Shut Down → Restart → OK. As the system boots, press F8 repeatedly until the Windows Advanced Options menu appears, then choose Safe Mode with Networking.
Note: Windows 7 reached end-of-life in January 2020 - running on it puts you at much higher risk of reinfection.
Inspect running processes with Process Explorer
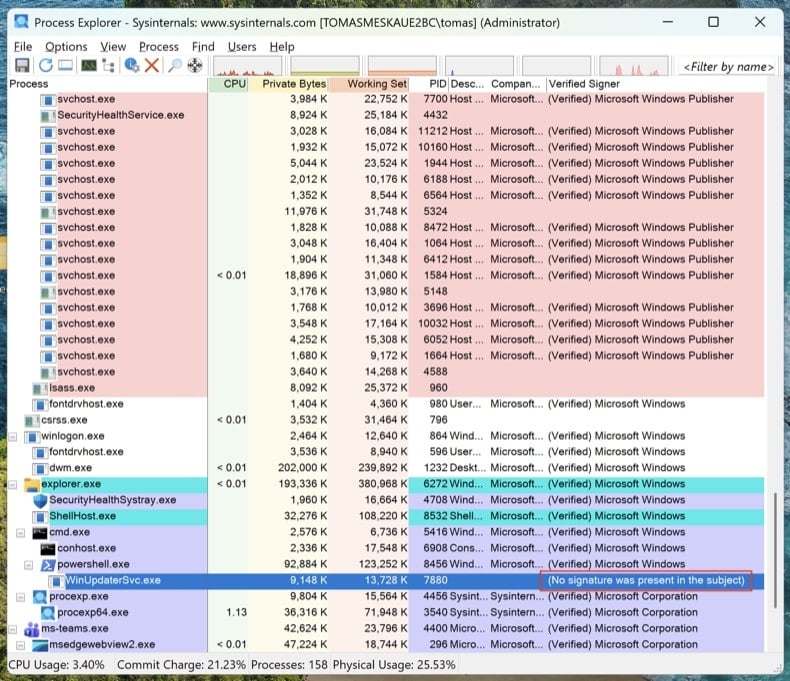
Download Process Explorer from Microsoft Sysinternals. Run it as Administrator. Click and .
Sort by "Verified Signer." Anything unsigned running from %AppData%, %LocalAppData%, %Temp%, or %ProgramData% is suspicious. Right-click → Properties to see the full image path. Right-click → "Search Online" to look up unfamiliar process names.
Task Manager hides full file paths, doesn't show digital signatures, and groups processes in ways that make malware easy to miss. Process Explorer is the same tool Microsoft engineers use.
Map every persistence point with Autoruns
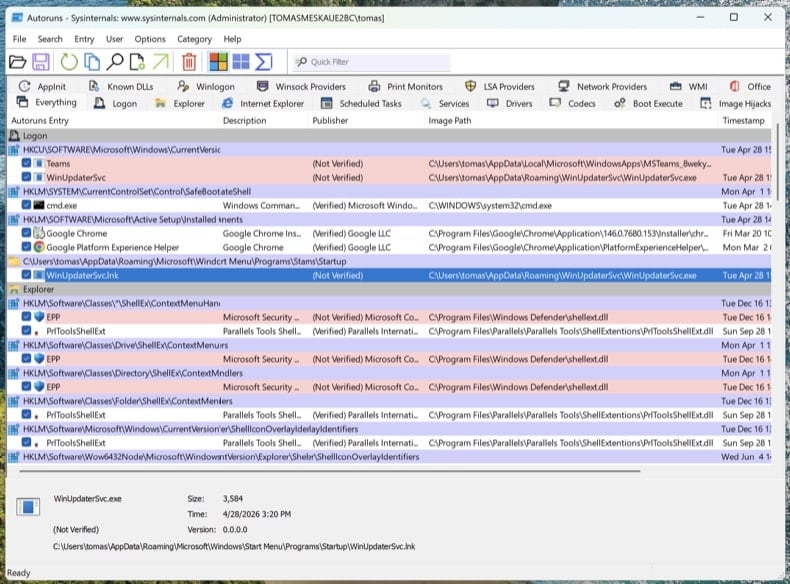
Download Autoruns. Right-click Autoruns.exe and choose Run as administrator - without elevation, Autoruns can't inspect protected registry hives.
In the menu, open and , then click Refresh.
Modern trojans don't just live in startup. Walk through these tabs and look for unsigned or unfamiliar entries:
- Logon - classic Run/RunOnce keys
- Scheduled Tasks - frequent hiding spot, especially tasks with PowerShell, MSHTA, or rundll32 actions
- Services - unsigned services in non-Microsoft folders
- WMI - Event Subscriptions are a stealthy persistence mechanism (MITRE T1546.003)
- Image Hijacks - Image File Execution Options "Debugger" abuse
- AppInit - DLLs loaded into every GUI process
- Browser plug-ins - unsigned add-ons across all installed browsers
Right-click any suspicious entry → "Jump to Image" to see the actual file. Right-click → "Search Online" opens VirusTotal for the file hash. Don't delete yet - just write down the file paths and entry names. We'll remove them after the scans.
Check the hosts file and DNS settings
Trojans often redirect bank, antivirus, and update domains to attacker-controlled servers by editing the hosts file or DNS settings.
Hosts file: Open Notepad as Administrator and open C:\Windows\System32\drivers\etc\hosts. Legitimate entries are commented with #. Any uncommented IP-to-domain mapping is suspicious - especially redirects for microsoft.com, windowsupdate, or your bank.
DNS settings: Open Command Prompt as Administrator and run ipconfig /all. Confirm your DNS servers point to your ISP, your router, or a known public resolver (Cloudflare 1.1.1.1, Google 8.8.8.8). Then open and verify both DNS and DNS over HTTPS (DoH) settings haven't been hijacked.
A clean PC with hijacked DNS is still a compromised PC. You'll think you're at chase.com and you'll be at the attacker's clone.
No single antivirus catches everything. The order below is intentional: offline scan first (catches rootkits before Windows fully loads), then on-demand scanners on the running system, then manual cleanup of anything they missed.
Run Microsoft Defender Offline
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. Your computer will restart into a stripped-down environment and scan before the full operating system loads.
Rootkits and bootkits hide from any scanner running on the same Windows session that's already infected. A pre-boot offline scan sees the disk before the malware can hide itself.
VB100 certified. Includes anti-trojan, registry/persistence scanning, anti-spyware in one pass. The 7-day free trial is available.
Download Combo CleanerRun Combo Cleaner full system scan
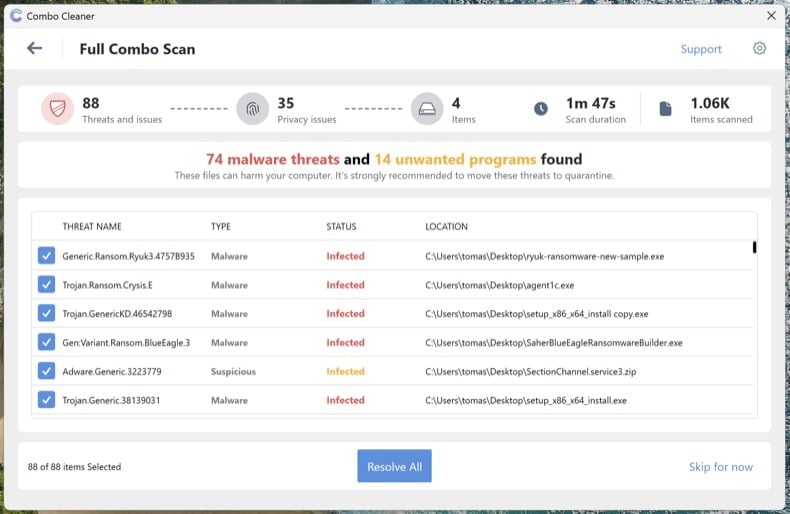
Install Combo Cleaner and run a full system scan (not the quick scan). Let it complete fully, review the detected threats, and apply the recommended actions. Combo Cleaner will quarantine known trojans and registry persistence.
Run Microsoft Safety Scanner as a second-opinion scan
Download Microsoft Safety Scanner (MSERT.exe), Microsoft's free on-demand tool. The binary expires every 10 days, which means every download has the latest signatures. Run a full scan after Combo Cleaner to catch anything one engine alone might miss.
Different scanning engines catch different threats. Running an additional Microsoft scan after Combo Cleaner is the single most underused verification step in malware removal.
Manually remove anything still listed in Autoruns
Reopen Autoruns. Anything you flagged in Step 4 that's still present hasn't been caught by the automated scans. For each remaining suspicious entry: right-click → Delete in Autoruns (this removes the persistence registration), then navigate to the file path and delete the actual file. Empty the Recycle Bin.
Some malware files reappear after deletion because something else on the system recreates them. If you delete a file and it returns within minutes, you have a remaining persistence point that Autoruns didn't show - usually a service or scheduled task running under SYSTEM. Re-run the scans from Steps 6-8 or proceed to a clean install (see end of guide).
Reset browsers and clear notification permissions
Trojans and adware frequently hijack browsers - change the default search engine, install rogue extensions, or grant themselves notification permissions to keep displaying scam pop-ups even after the malware is gone.
- Chrome: visit
chrome://settings/resetand click "Restore settings to their original defaults." Then visitchrome://settings/content/notificationsand remove any unfamiliar sites. - Edge: visit
edge://settings/reset. Then checkedge://settings/content/notifications. - Firefox: open
about:supportand click Refresh Firefox (Firefox uses "Refresh," not "Reset"). Then check Settings → Privacy & Security → Permissions → Notifications.
Review installed extensions in each browser and remove anything you don't recognize, especially extensions you didn't install yourself.
Re-enable Defender, Tamper Protection, and update everything
Many trojans disable security software. Open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all turned on. Tamper Protection prevents malware from disabling Defender silently.
Then run Windows Update () and update your browsers and applications. The infection vector that let the trojan in originally usually involves outdated software.
Change passwords from a clean device
If the trojan was an info-stealer (Lumma, RedLine, Vidar, and similar are extremely common), assume every password saved in your browser is compromised. Change them from a different, known-clean device - your phone is fine if it's not infected.
Recommended order:
- Primary email first - it's the recovery hub for everything else
- Banking and financial accounts
- Password manager master password (if you use one)
- Social media, shopping, and remaining accounts
Where available, enable phishing-resistant multi-factor authentication (passkeys / FIDO2 hardware keys / authenticator apps) - SMS-based MFA is bypassable by sophisticated attackers.
Verify the clean and monitor for 7 days
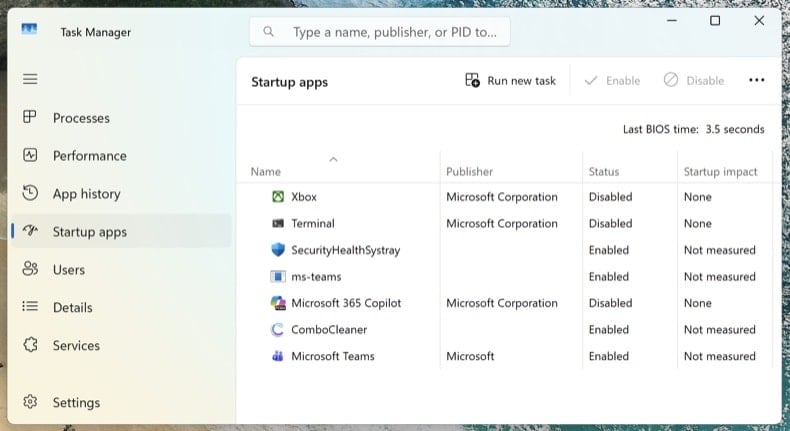
Reconnect to the network and run one final full scan with Combo Cleaner. Open Task Manager (Ctrl + Shift + Esc) and switch to the Startup apps tab - confirm nothing suspicious has reappeared.
Over the next 7 days, watch for symptom recurrence: unexpected high CPU usage, unknown processes returning, browser redirects, or pop-ups. If anything returns, you missed a persistence point and the procedure needs to be repeated - or you may have a deeper compromise that requires a clean install.
When to clean install Windows instead
Manual removal isn't always the right answer. Reinstalling Windows from scratch is the only way to be 100% certain when:
- The malware reappears after every removal attempt
- A bootkit or UEFI rootkit was detected (this class of threat sits below the operating system and survives a normal Windows reinstall)
- A confirmed credential-theft trojan ran with administrator privileges (Lumma, RedLine, Vidar) - the system likely has multiple unknown payloads
- The PC is used for online banking, business email, or anything where partial doubt isn't acceptable
A clean install is a 30-60 minute process: Windows 11 reinstall via . Back up documents to external storage first, scan the backup with Combo Cleaner before restoring it, and reinstall applications fresh - never restore them from a backup of the infected system.
Important: Manual removal requires advanced computer skills. If you're not confident identifying system files from malicious files, run an automated scan with Combo Cleaner and Windows Defender and stop there - that path catches the vast majority of consumer trojans without the risk of breaking Windows by deleting the wrong file.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion