

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What kind of malware is Corp MDM Spyware?
Corp MDM is Android spyware that targets employees of logistics companies. It silently intercepts SMS messages and redirects calls to steal authentication codes. According to research by Have I Been Squatted, the campaign is linked to cargo theft operations.
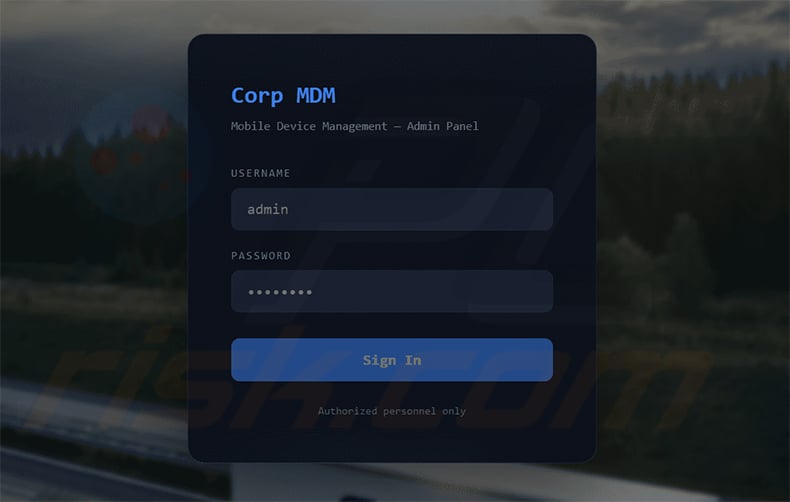
Corp MDM Spyware overview
Corp MDM presents itself as an app named System Service, complete with a fake system configuration loader that cycles through messages like Initializing system... for about ten seconds before requesting permissions. This delay mimics a genuine device setup process, making users more likely to grant the access the malware needs.
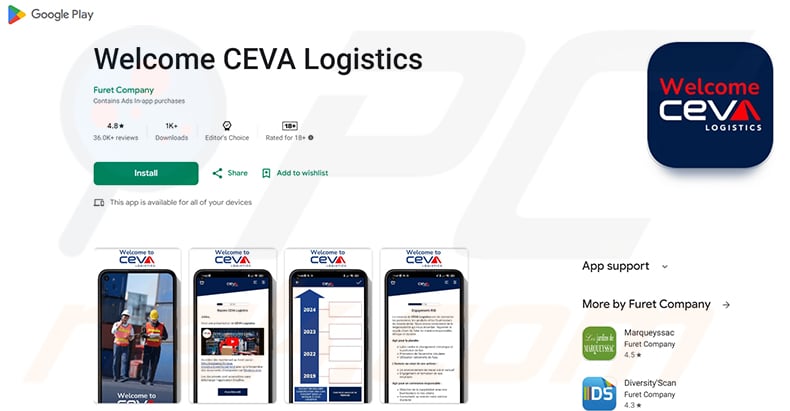
The malware is distributed through fake Google Play Store pages that impersonate CEVA Logistics and TKW Logistics. These pages faithfully copy Play Store navigation, ratings, reviews, and data-safety sections to look legitimate. Visitors are then instructed to sideload the APK and allow installs from unknown sources.
Once installed, Corp MDM intercepts every incoming SMS message in real time, capturing the sender, message body, and timestamp alongside a unique device identifier. This makes it effective at stealing one-time passwords used for two-factor authentication, allowing attackers to bypass security checks on banking apps and other services.
The malware can also silently activate unconditional call forwarding on the device, redirecting all incoming calls to a number the attackers control. This is carried out using a standard carrier code sent in the background, with no visible sign to the victim. Combined with SMS interception, it gives the attacker full control over the victim's incoming communications.
Corp MDM communicates with a command-and-control server over unencrypted HTTP, sending device details such as manufacturer, model, and battery level alongside stolen SMS data. The operator panel supports commands to toggle call forwarding, request SMS sync, and trigger a self-destruct routine that stops the service and clears app data.
Researchers assessed the threat actor behind Corp MDM likely has an Armenian or Russian nexus, based partly on a default +374 country code found in the operator panel. The implant also shows signs of AI-assisted development, including bugs that leave some advertised features - such as location tracking and device locking - without any working implementation in the client.
It has to be mentioned that malware developers often improve upon their software and methodologies. Hence, potential future iterations of Corp MDM could have additional or different functionalities and features.
In summary, the presence of software like Corp MDM on devices can lead to serious privacy issues, stolen authentication codes, unauthorized call rerouting, financial losses, and identity theft.
| Name | Corp MDM malware |
| Threat Type | Android malware, malicious application, spyware. |
| Symptoms | The device is running slow, system settings are modified without user's permission, questionable applications appear, data and battery usage is increased significantly, browsers redirect to questionable websites, intrusive advertisements are delivered. |
| Distribution methods | Fake Google Play Store pages impersonating legitimate logistics company applications, third-party websites. |
| Damage | Stolen SMS messages and two-factor authentication codes, unauthorized call forwarding, monetary losses, identity theft, decreased device performance. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
Android spyware examples
Corp MDM is a focused tool designed to support cargo theft by quietly monitoring the communications of logistics employees. The combination of SMS interception and call forwarding gives attackers persistent access to authentication codes, making it particularly damaging for victims whose accounts are tied to the compromised phone number.
Similar Android spyware and malware threats include RedWing, ResidentBat, and Landfall. Keep in mind that while their capabilities may differ, the general risks - privacy invasion, financial loss, and identity theft - remain consistent across these kinds of threats.
How did Corp MDM Spyware infiltrate my device?
Corp MDM spreads primarily through fake Google Play Store pages impersonating CEVA Logistics and TKW Logistics. These pages are hosted on lookalike domains and designed to look like official app listings, complete with fabricated ratings and reviews. Visitors are guided to download an APK file directly and enable installs from unknown sources, a step the real Play Store never requires.
In general, Android malware also reaches victims through third-party app stores, phishing links sent by email or messaging apps, fake software update prompts, and malicious advertisements. Downloading apps only from the official Google Play Store and verifying the developer before installing are the most reliable protections.
How to avoid installation of malware?
Always install apps from official sources, and be wary of any website that asks you to download an APK file directly. Pages that imitate the Play Store layout but are not hosted on google.com or play.google.com are almost certainly fraudulent. Check the URL carefully before tapping any download button.
Avoid clicking links in unsolicited emails, text messages, or social media posts that offer app downloads. Review the permissions an app requests during installation - a system-style app asking for SMS access and call capabilities is a serious warning sign. Keeping your device updated and running reputable security software adds an important extra layer of protection.
Screenshot of the fake Google Play Store used to spread Corp MDM spyware (source: haveibeensquatted.com):
Quick menu:
- Introduction
- How to delete browsing history from the Chrome web browser?
- How to disable browser notifications in the Chrome web browser?
- How to reset the Chrome web browser?
- How to delete browsing history from the Firefox web browser?
- How to disable browser notifications in the Firefox web browser?
- How to reset the Firefox web browser?
- How to uninstall potentially unwanted and/or malicious applications?
- How to boot the Android device in "Safe Mode"?
- How to check the battery usage of various applications?
- How to check the data usage of various applications?
- How to install the latest software updates?
- How to reset the system to its default state?
- How to disable applications that have administrator privileges?
Delete browsing history from the Chrome web browser:
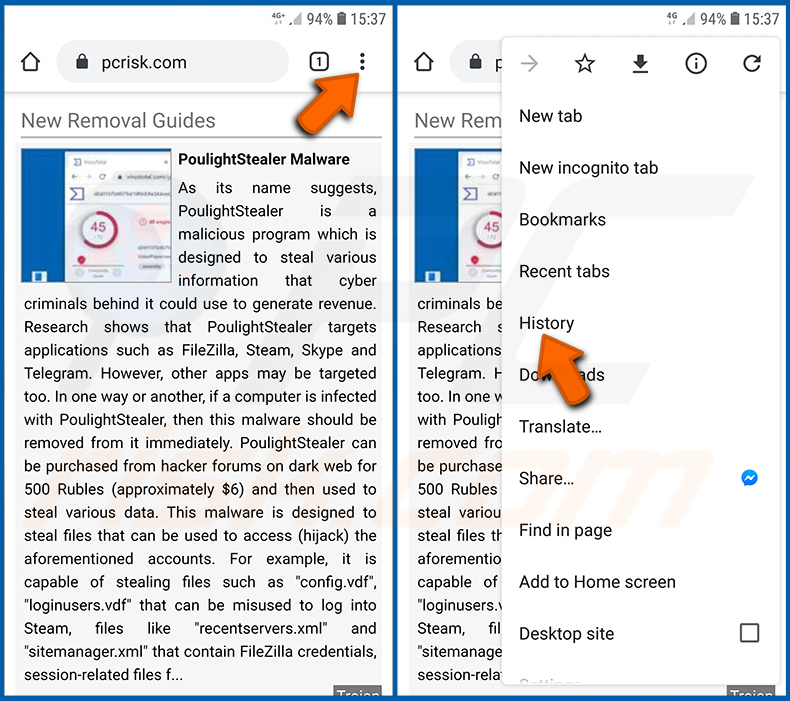
Tap the "Menu" button (three dots on the right-upper corner of the screen) and select "History" in the opened dropdown menu.
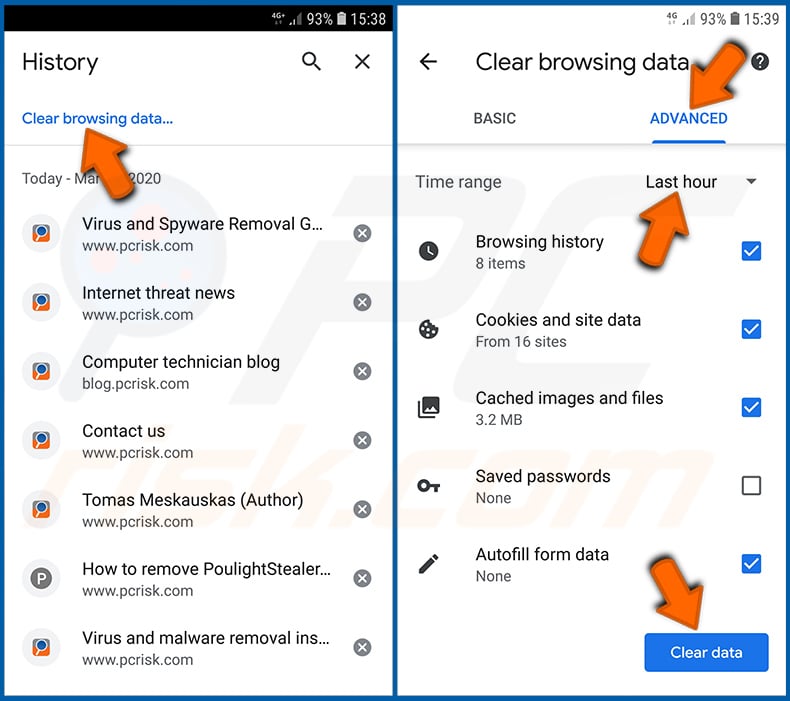
Tap "Clear browsing data", select "ADVANCED" tab, choose the time range and data types you want to delete and tap "Clear data".
Disable browser notifications in the Chrome web browser:
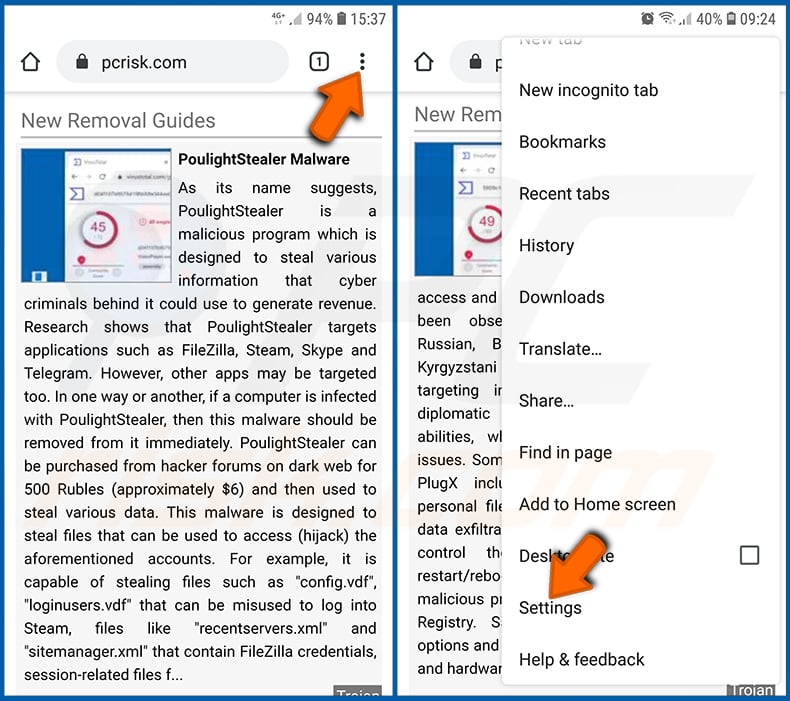
Tap the "Menu" button (three dots on the right-upper corner of the screen) and select "Settings" in the opened dropdown menu.
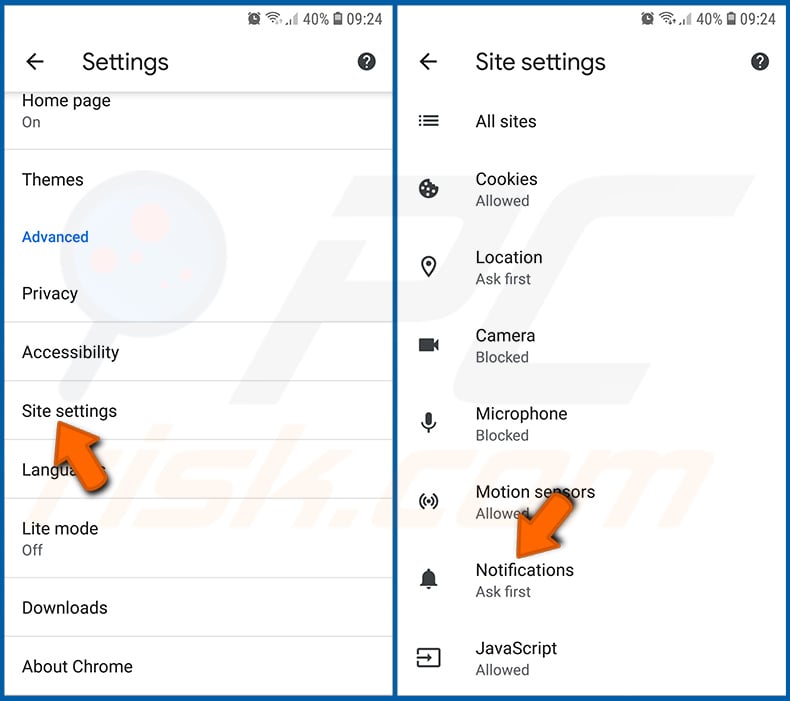
Scroll down until you see "Site settings" option and tap it. Scroll down until you see "Notifications" option and tap it.
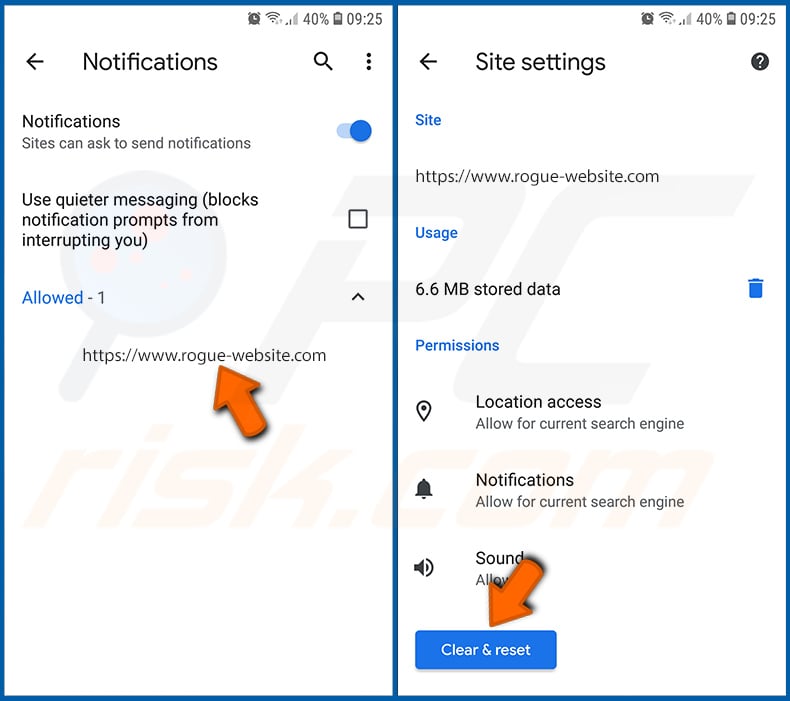
Find the websites that deliver browser notifications, tap on them and click "Clear & reset". This will remove permissions granted for these websites to deliver notifications. However, once you visit the same site again, it may ask for a permission again. You can choose whether to give these permissions or not (if you choose to decline the website will go to "Blocked" section and will no longer ask you for the permission).
Reset the Chrome web browser:
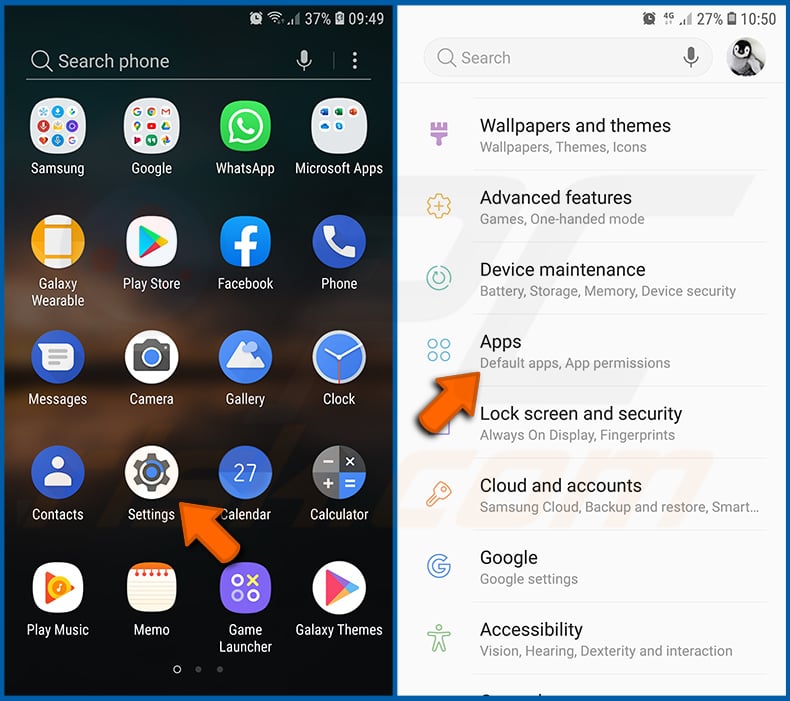
Go to "Settings", scroll down until you see "Apps" and tap it.
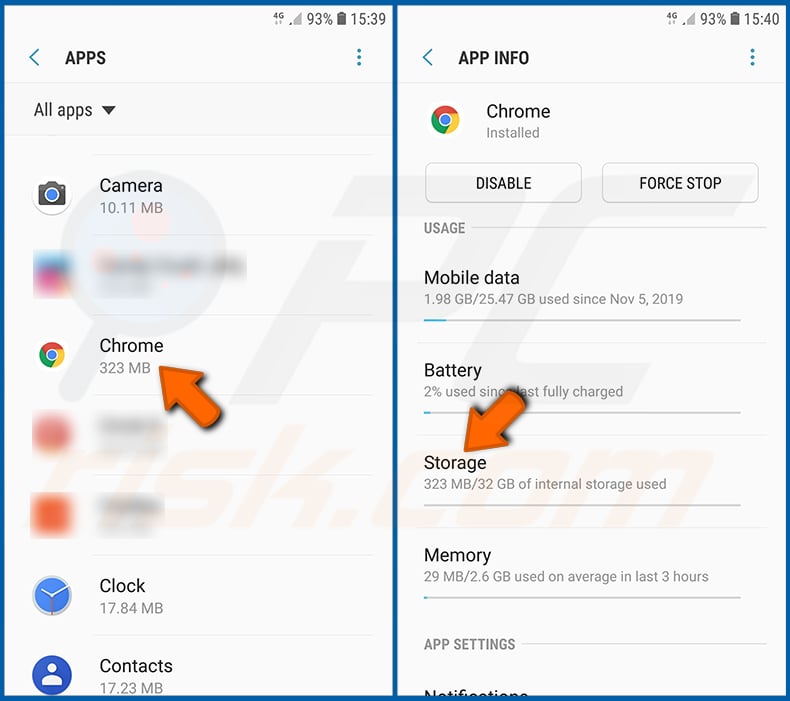
Scroll down until you find "Chrome" application, select it and tap "Storage" option.
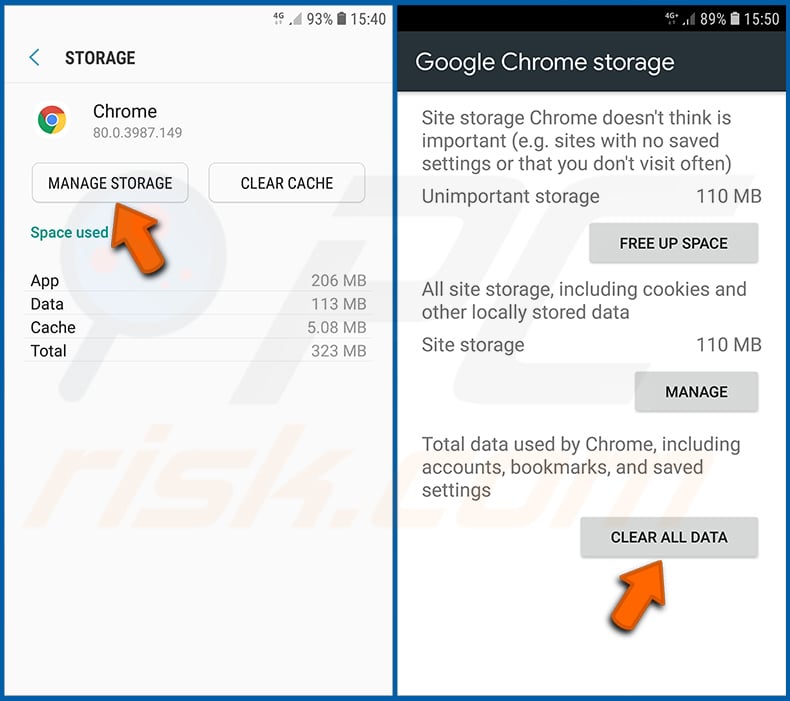
Tap "MANAGE STORAGE", then "CLEAR ALL DATA" and confirm the action by taping "OK". Note that resetting the browser will eliminate all data stored within. This means that all saved logins/passwords, browsing history, non-default settings and other data will be deleted. You will also have to re-login into all websites as well.
Delete browsing history from the Firefox web browser:
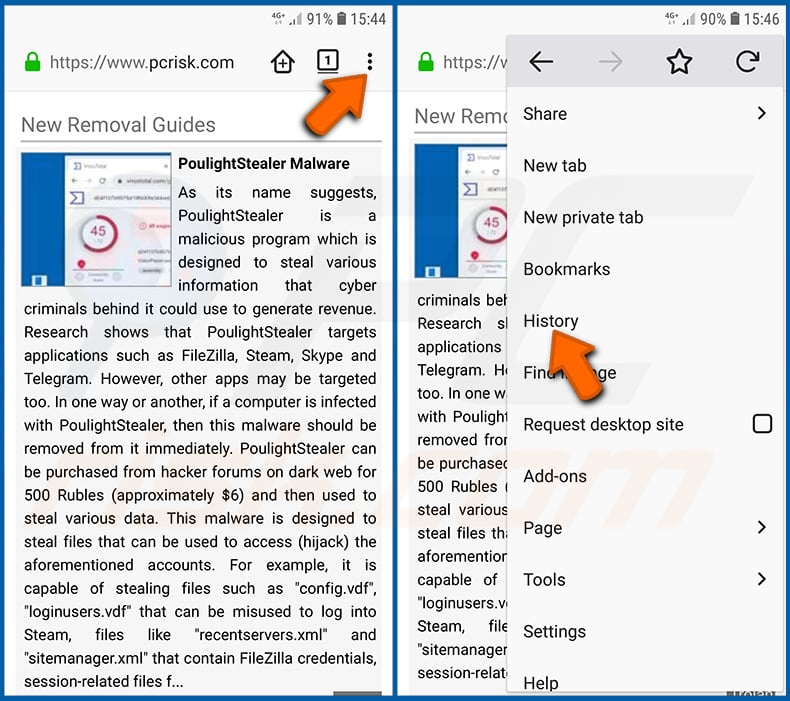
Tap the "Menu" button (three dots on the right-upper corner of the screen) and select "History" in the opened dropdown menu.
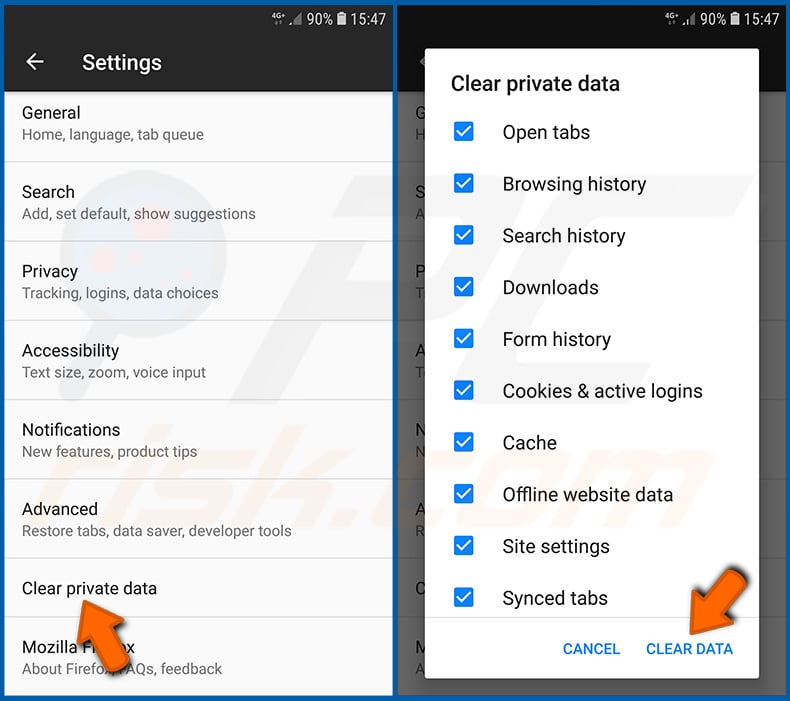
Scroll down until you see "Clear private data" and tap it. Select data types you want to remove and tap "CLEAR DATA".
Disable browser notifications in the Firefox web browser:
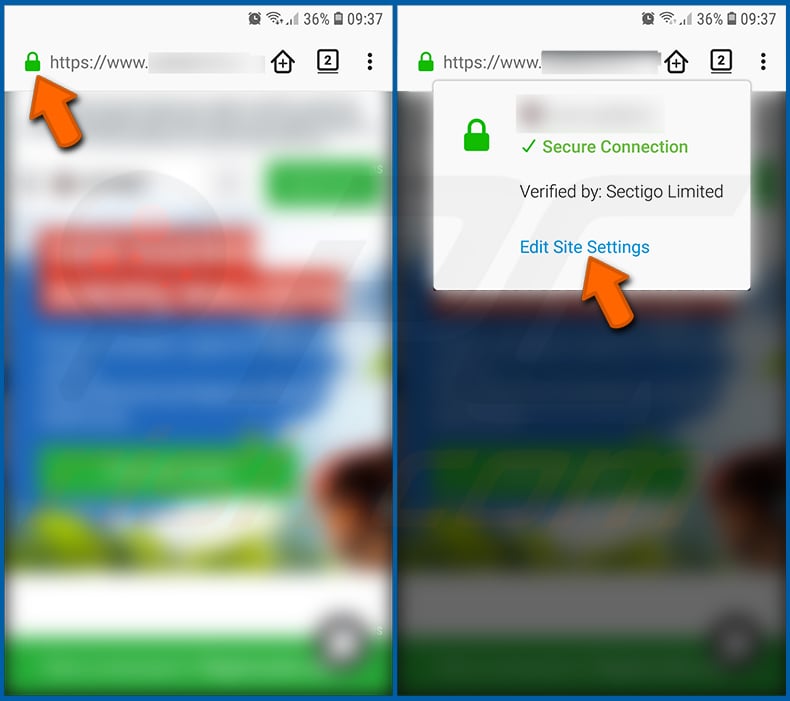
Visit the website that is delivering browser notifications, tap the icon displayed on the left of URL bar (the icon will not necessarily be a "Lock") and select "Edit Site Settings".
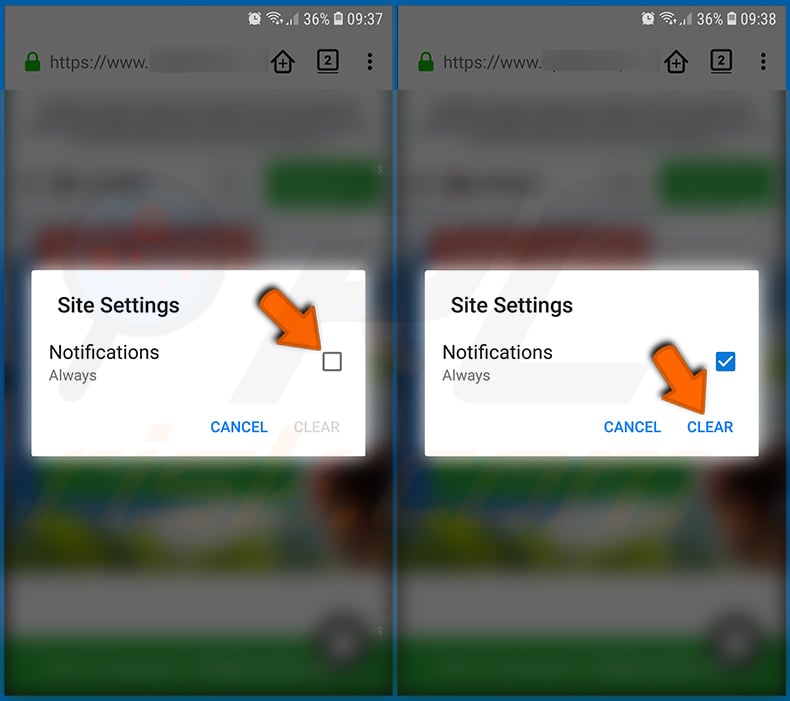
In the opened pop-up opt-in the "Notifications" option and tap "CLEAR".
Reset the Firefox web browser:
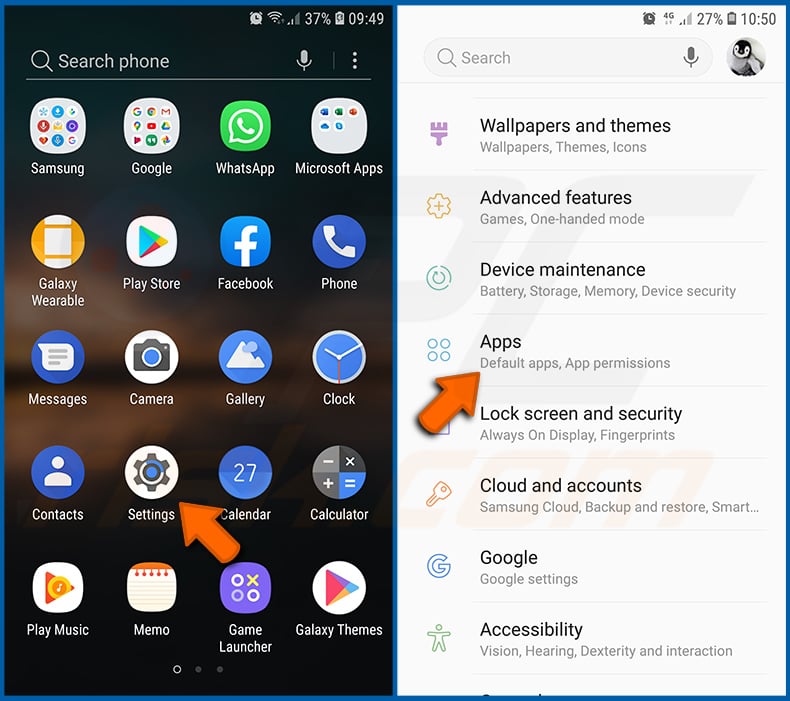
Go to "Settings", scroll down until you see "Apps" and tap it.
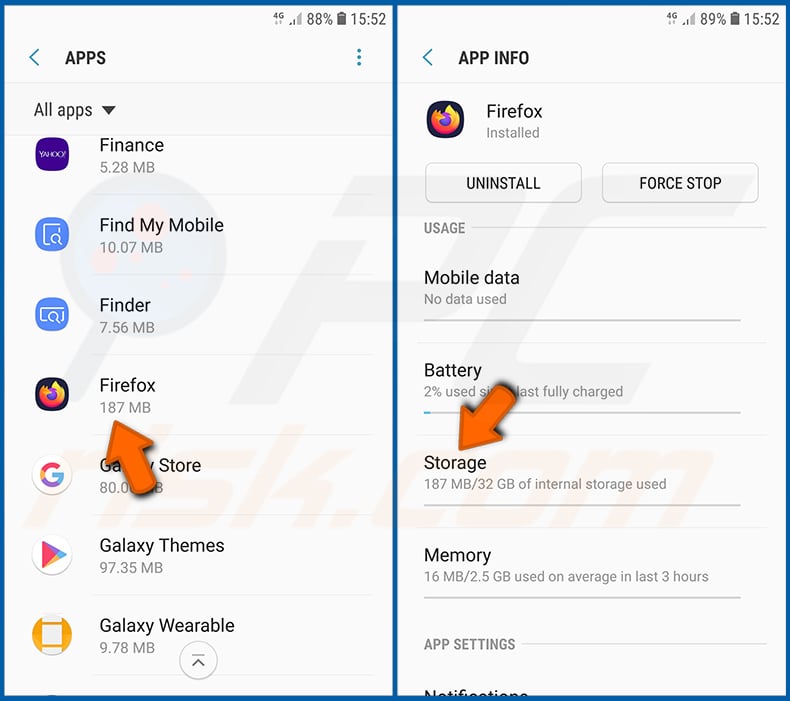
Scroll down until you find "Firefox" application, select it and tap "Storage" option.
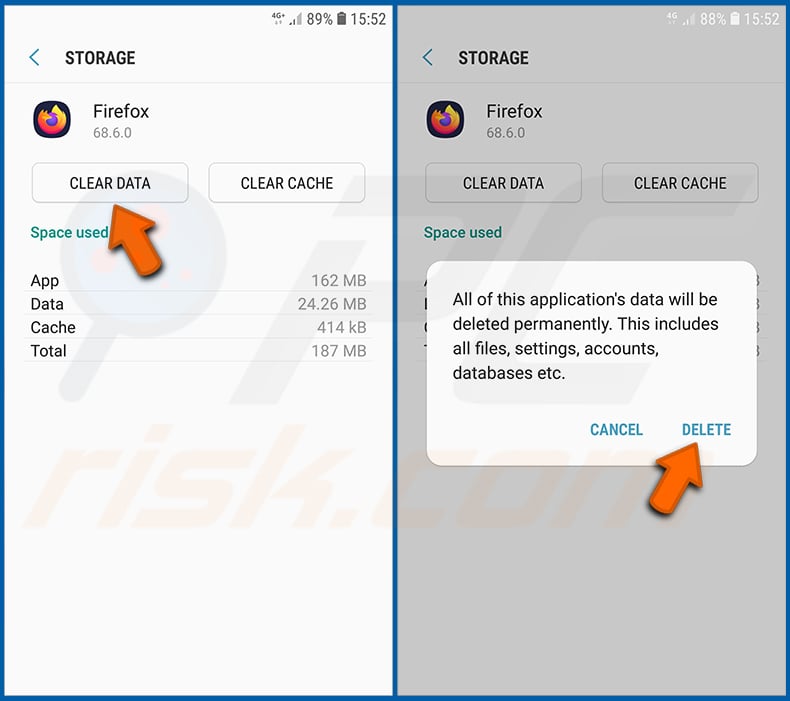
Tap "CLEAR DATA" and confirm the action by taping "DELETE". Note that resetting the browser will eliminate all data stored within. This means that all saved logins/passwords, browsing history, non-default settings and other data will be deleted. You will also have to re-login into all websites as well.
Uninstall potentially unwanted and/or malicious applications:
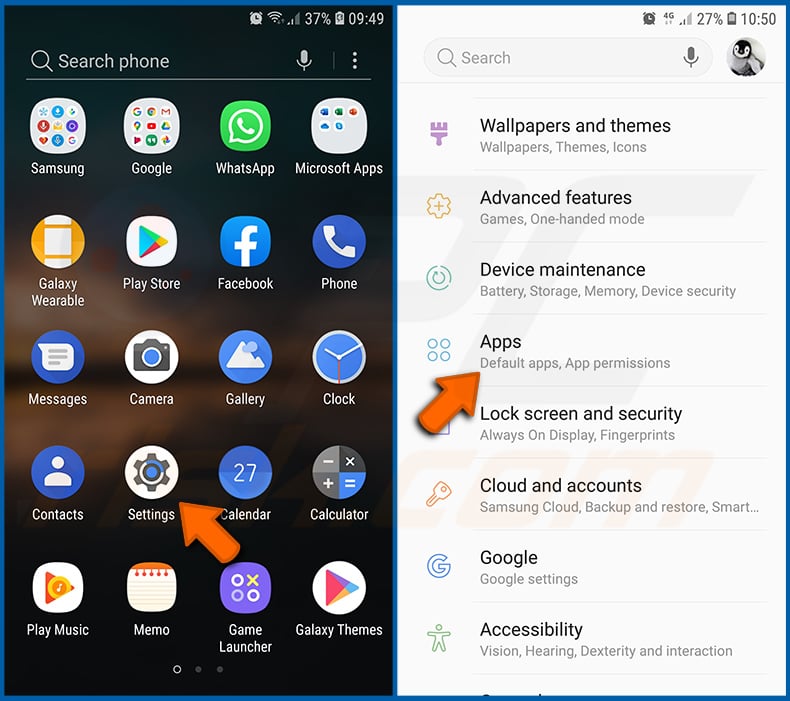
Go to "Settings", scroll down until you see "Apps" and tap it.
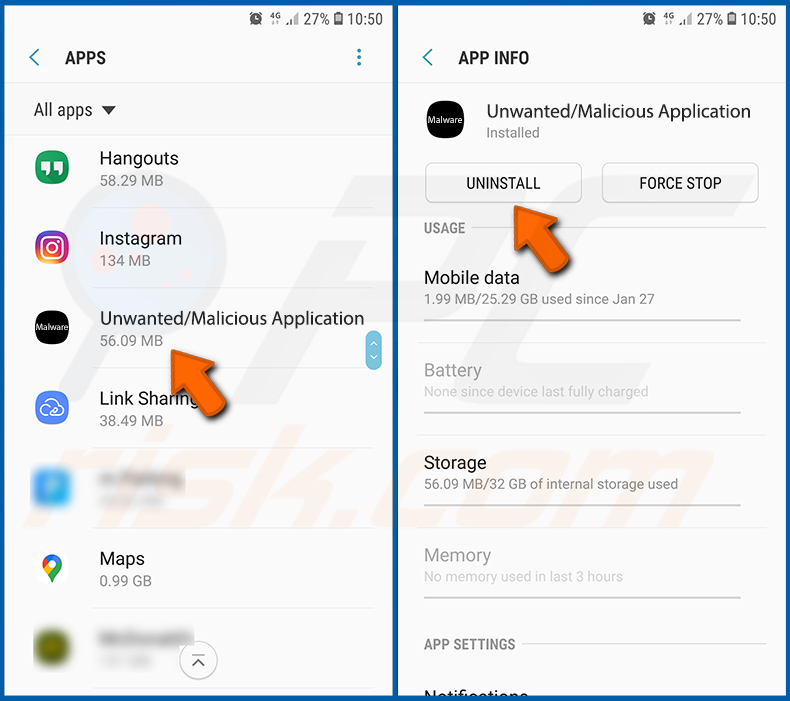
Scroll down until you see a potentially unwanted and/or malicious application, select it and tap "Uninstall". If, for some reason, you are unable to remove the selected app (e.g., you are prompted with an error message), you should try using the "Safe Mode".
Boot the Android device in "Safe Mode":
The "Safe Mode" in Android operating system temporarily disables all third-party applications from running. Using this mode is a good way to diagnose and solve various issues (e.g., remove malicious applications that prevent users you from doing so when the device is running "normally").
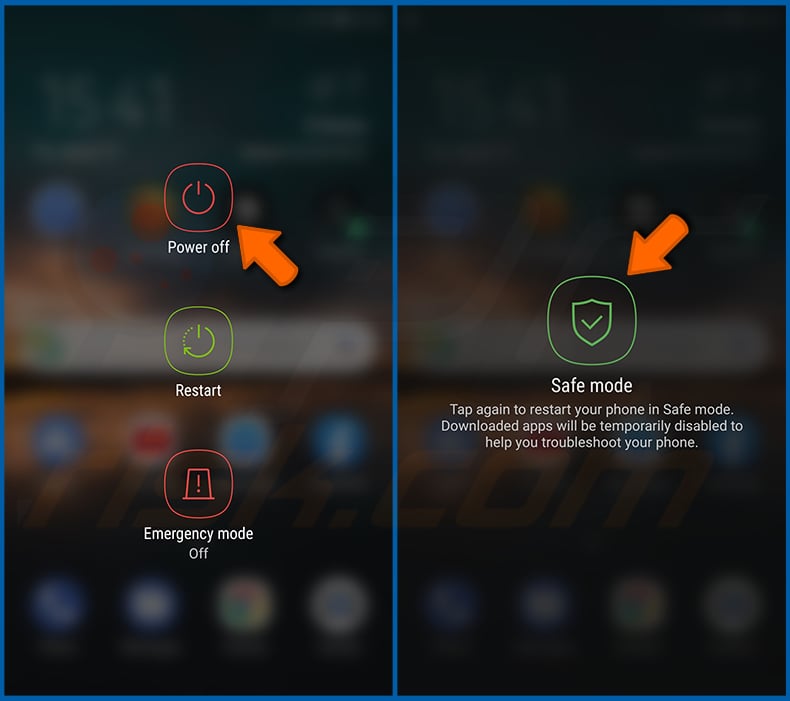
Push the "Power" button and hold it until you see the "Power off" screen. Tap the "Power off" icon and hold it. After a few seconds the "Safe Mode" option will appear and you'll be able run it by restarting the device.
Check the battery usage of various applications:
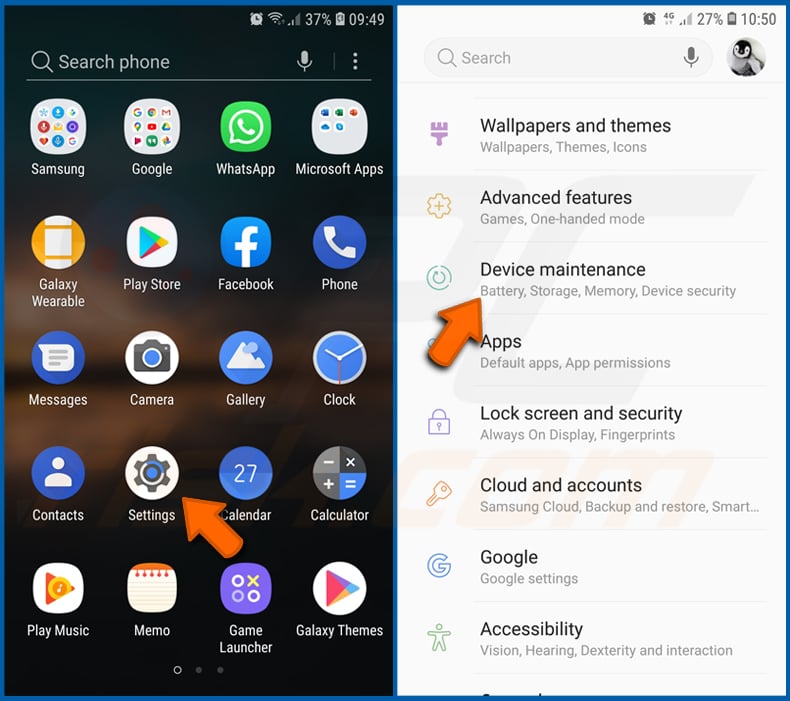
Go to "Settings", scroll down until you see "Device maintenance" and tap it.
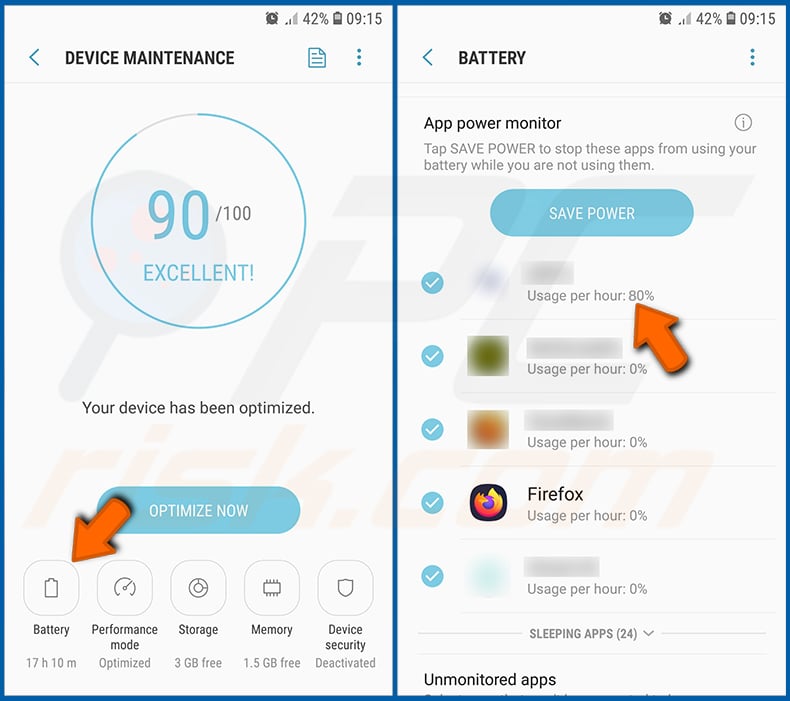
Tap "Battery" and check the usage of each application. Legitimate/genuine applications are designed to use as low energy as possible in order to provide the best user experience and to save power. Therefore, high battery usage may indicate that the application is malicious.
Check the data usage of various applications:
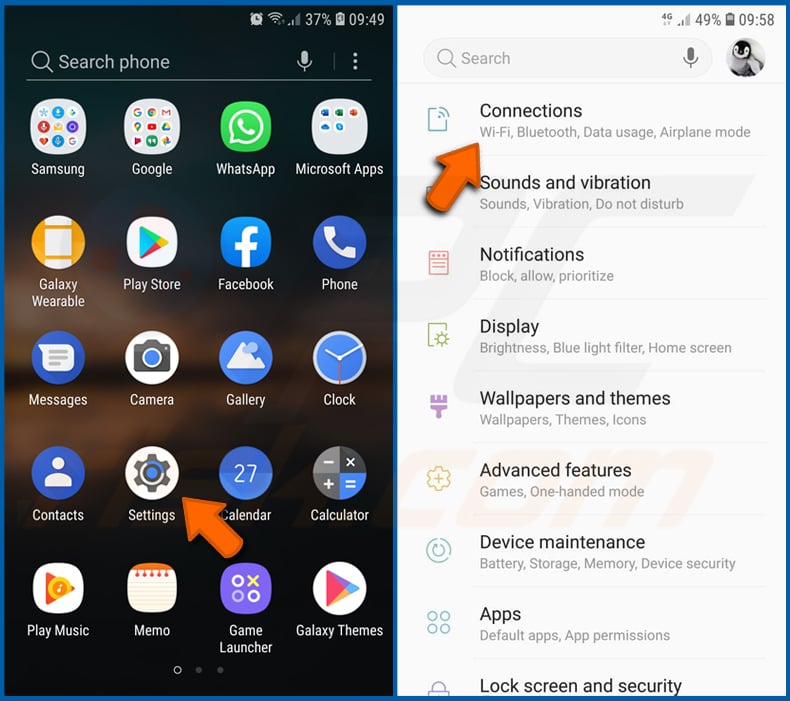
Go to "Settings", scroll down until you see "Connections" and tap it.
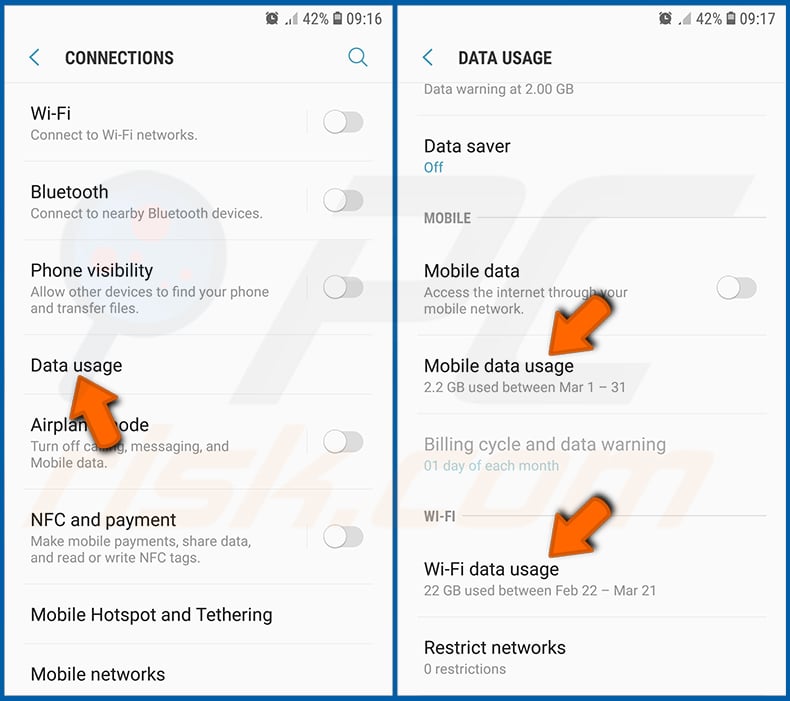
Scroll down until you see "Data usage" and select this option. As with battery, legitimate/genuine applications are designed to minimize data usage as much as possible. This means that huge data usage may indicate presence of malicious application. Note that some malicious applications might be designed to operate when the device is connected to wireless network only. For this reason, you should check both Mobile and Wi-Fi data usage.
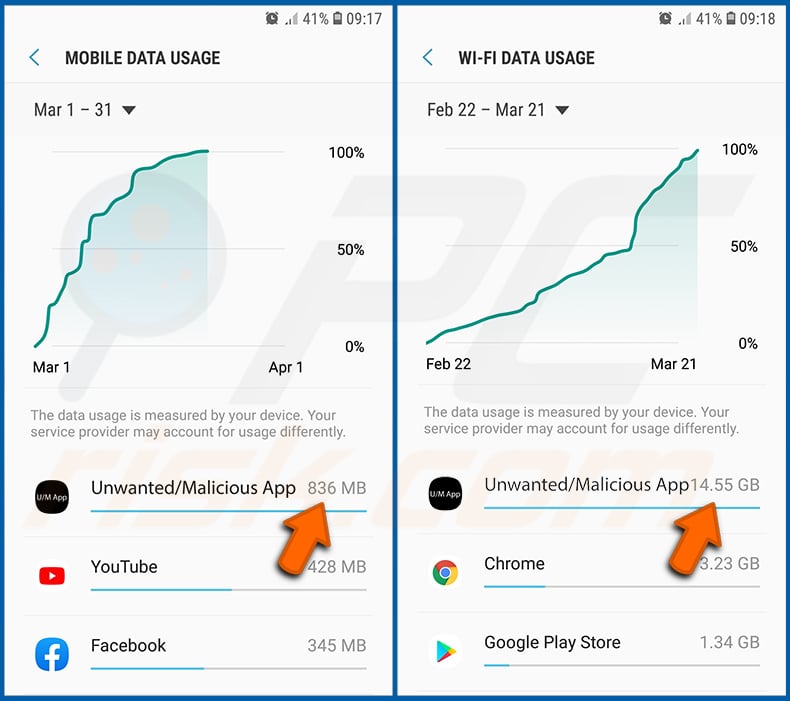
If you find an application that uses a lot of data even though you never use it, then we strongly advise you to uninstall it as soon as possible.
Install the latest software updates:
Keeping the software up-to-date is a good practice when it comes to device safety. The device manufacturers are continually releasing various security patches and Android updates in order to fix errors and bugs that can be abused by cybercriminals. An outdated system is way more vulnerable, which is why you should always be sure that your device's software is up-to-date.
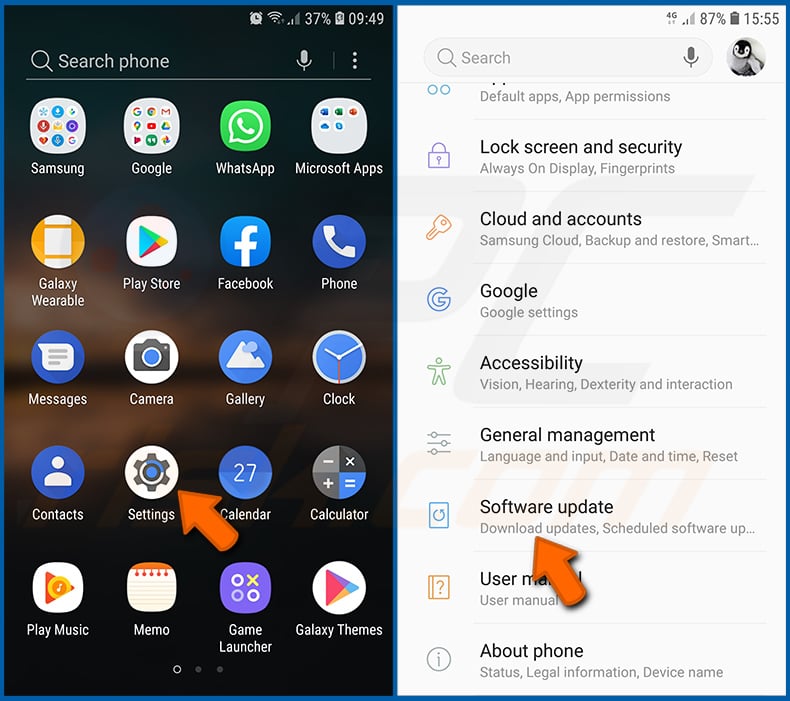
Go to "Settings", scroll down until you see "Software update" and tap it.
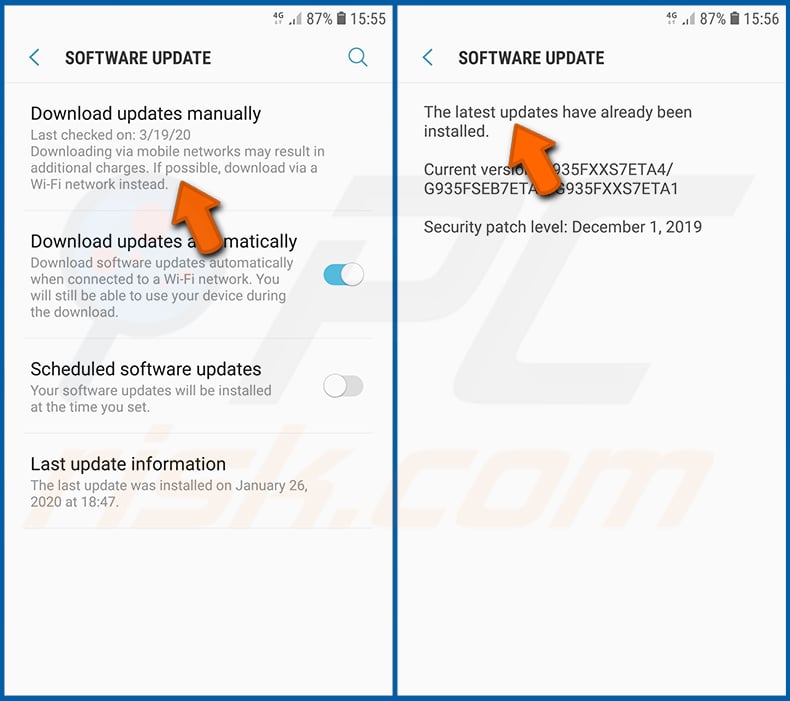
Tap "Download updates manually" and check if there are any updates available. If so, install them immediately. We also recommend to enable the "Download updates automatically" option - it will enable the system to notify you once an update is released and/or install it automatically.
Reset the system to its default state:
Performing a "Factory Reset" is a good way to remove all unwanted applications, restore system's settings to default and clean the device in general. However, you must keep in mind that all data within the device will be deleted, including photos, video/audio files, phone numbers (stored within the device, not the SIM card), SMS messages, and so forth. In other words, the device will be restored to its primal state.
You can also restore the basic system settings and/or simply network settings as well.
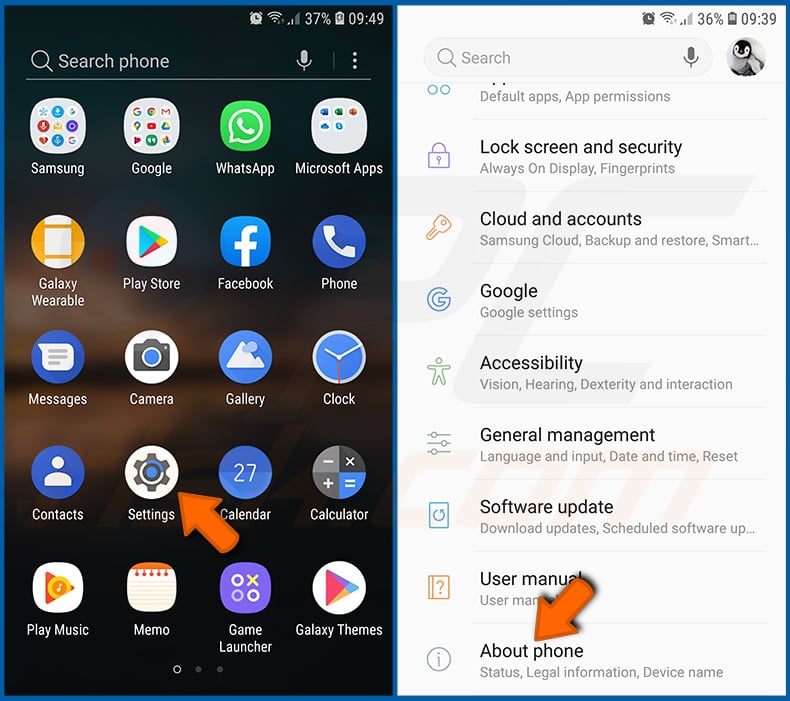
Go to "Settings", scroll down until you see "About phone" and tap it.
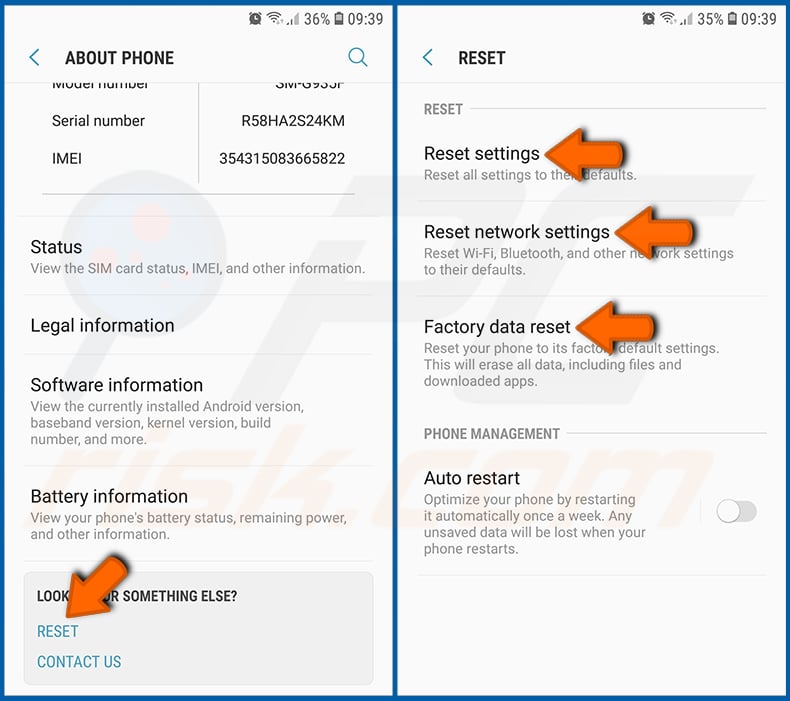
Scroll down until you see "Reset" and tap it. Now choose the action you want to perform:
"Reset settings" - restore all system settings to default;
"Reset network settings" - restore all network-related settings to default;
"Factory data reset" - reset the entire system and completely delete all stored data;
Disable applications that have administrator privileges:
If a malicious application gets administrator-level privileges it can seriously damage the system. To keep the device as safe as possible you should always check what apps have such privileges and disable the ones that shouldn't.
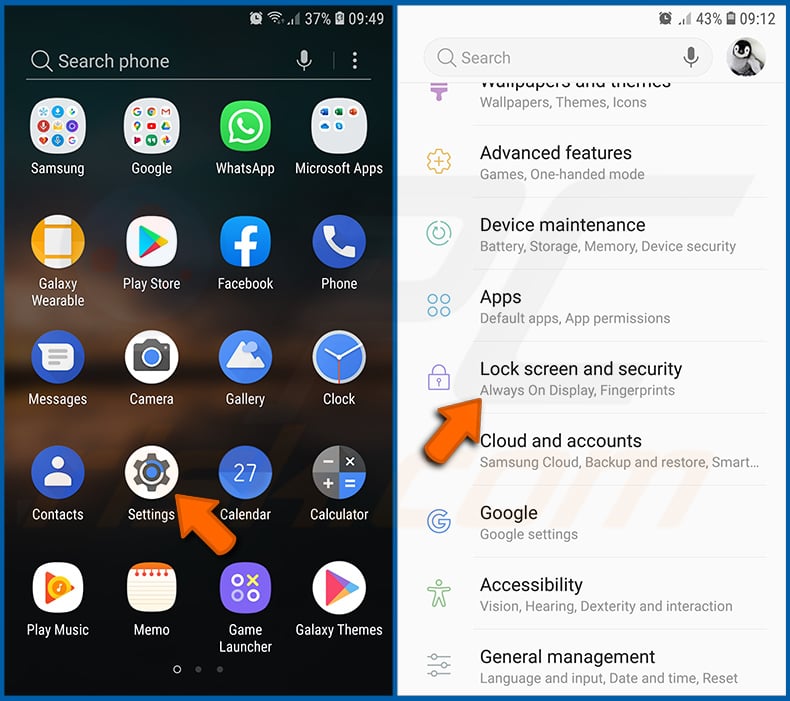
Go to "Settings", scroll down until you see "Lock screen and security" and tap it.
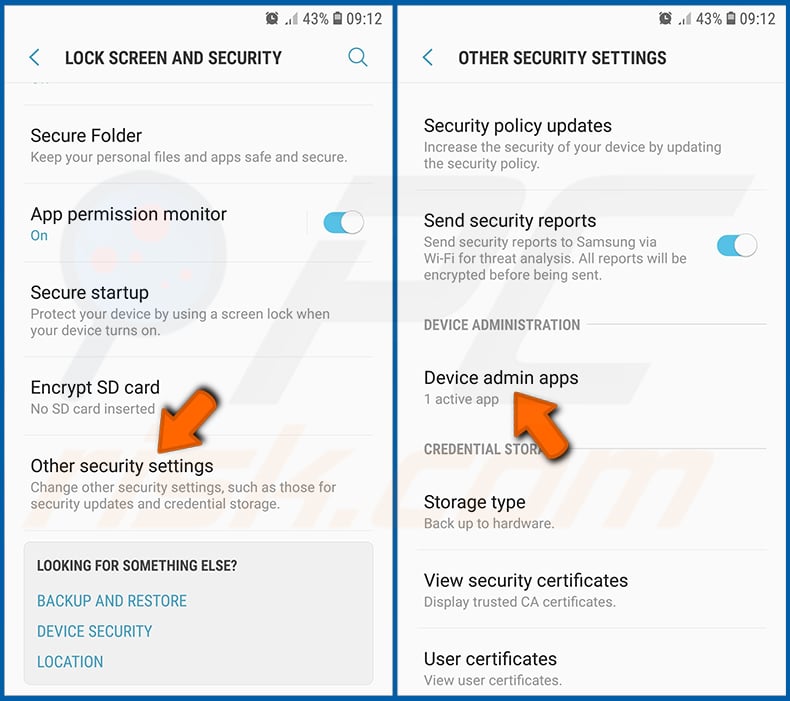
Scroll down until you see "Other security settings", tap it and then tap "Device admin apps".
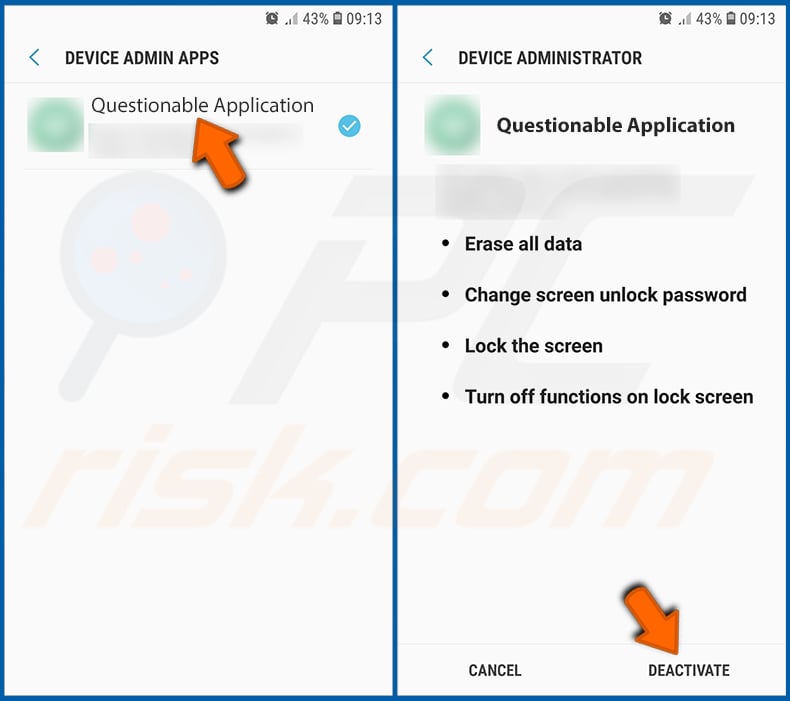
Identify applications that should not have administrator privileges, tap them and then tap "DEACTIVATE".
Frequently Asked Questions (FAQ)
My Android device is infected with Corp MDM Spyware, should I format my storage device to get rid of it?
Formatting is generally not necessary for malware removal. Running reputable mobile security software like Combo Cleaner should be sufficient to detect and remove Corp MDM from your device.
What are the biggest issues that Corp MDM Spyware can cause?
Corp MDM intercepts every incoming SMS message in real time, meaning attackers can collect one-time passwords used for two-factor authentication and gain access to bank accounts, email, and any service tied to the victim's phone number.
The malware can also redirect all incoming calls to a number the attackers control. Together, these capabilities make unauthorized account access and financial theft very realistic outcomes for affected users.
What is the purpose of Corp MDM Spyware?
Corp MDM appears designed primarily to support cargo theft by compromising the communications of logistics employees. Most cyberattacks are profit-driven, though attackers may also be motivated by espionage, personal grudges, disruption, or broader criminal activity.
How did Corp MDM Spyware infiltrate my Android device?
Corp MDM spreads through fake Google Play Store pages posing as apps for CEVA Logistics and TKW Logistics. Victims are directed to download an APK directly and sideload it. Android malware also commonly spreads via phishing links, third-party app stores, and fake software update prompts.
Will Combo Cleaner protect me from malware?
Combo Cleaner can detect and eliminate nearly all known malware infections. A complete system scan is essential, as sophisticated threats tend to embed themselves deep within the device to avoid detection.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion