
What kind of scam is the fake “Rabby Airdrop”?
Phishing/ScamAlso Known As: Rabby Airdrop crypto drainer

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What is the "Rabby Airdrop Scam"?
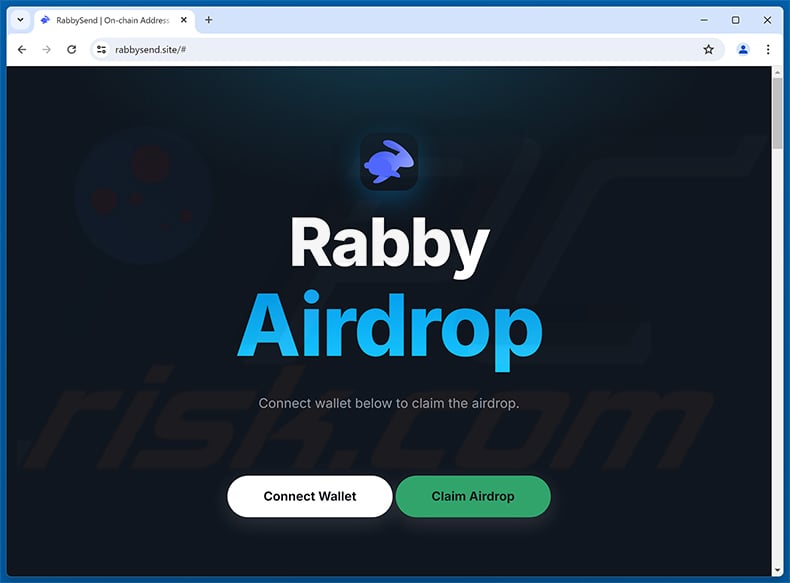
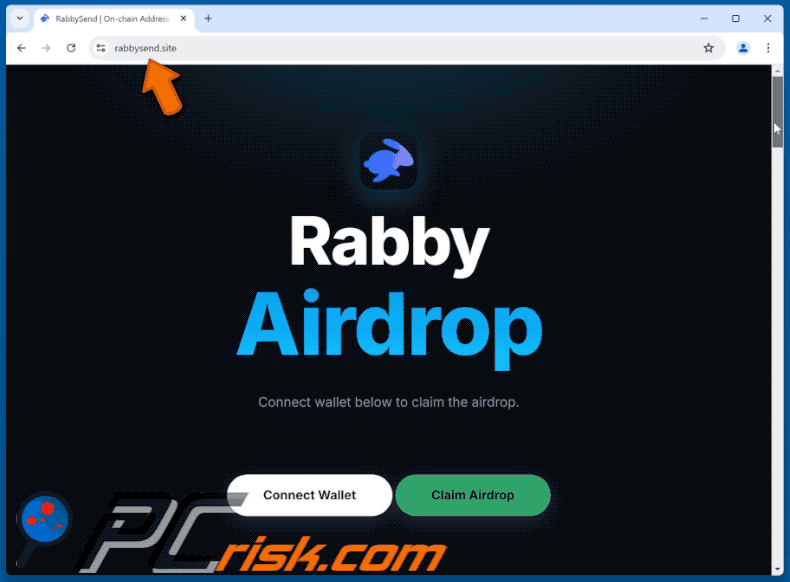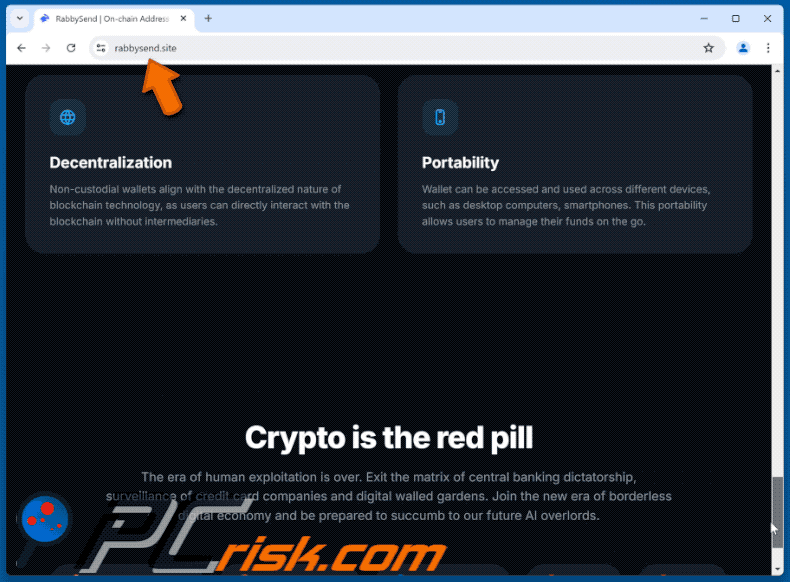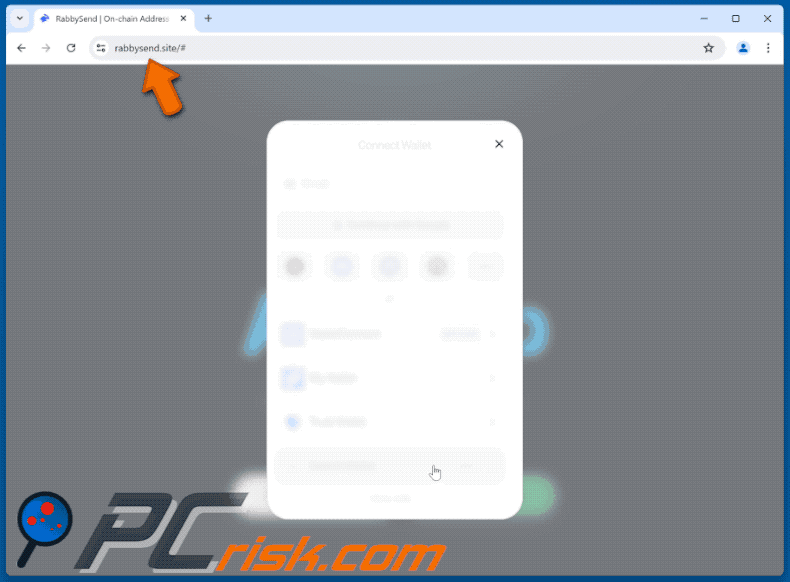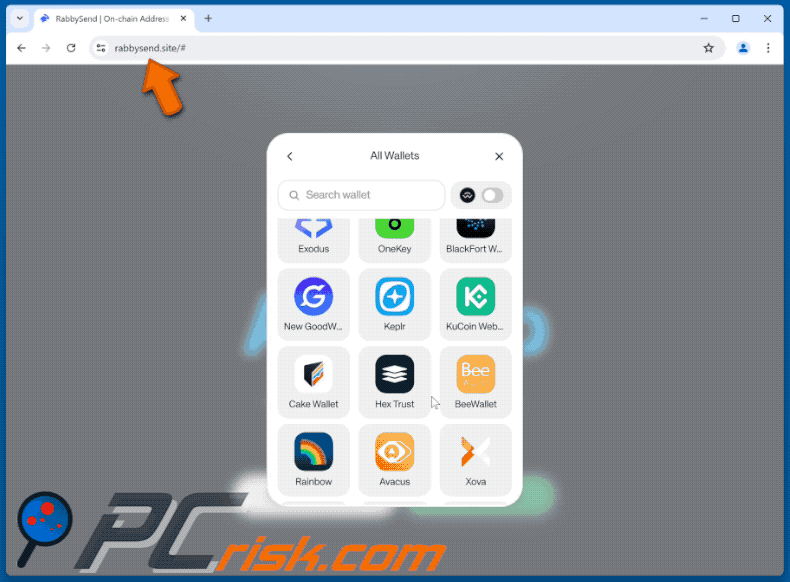
While investigating dubious websites, our researchers came across rabbysend[.]site, a page promoting a fake airdrop using the Rabby Wallet brand. The site is designed to deceive visitors into connecting their cryptocurrency wallets, after which a drainer tool empties the victim's funds without their knowledge.
IMPORTANT NOTE: We do not review crypto projects, please do your own research when investing money.
Federal Trade Commission (FTC) states that since the start of 2021, more than 46,000 people have reported losing over $1 billion in crypto to scams – that's about one out of every four dollars reported lost, more than any other payment method.
"Rabby Airdrop Scam" in detail
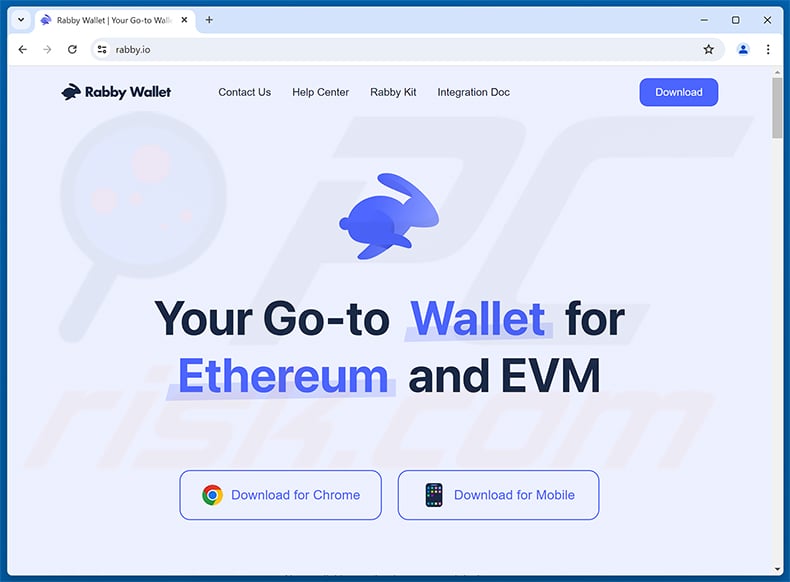
The legitimate Rabby Wallet (rabby.io) is a browser extension and mobile cryptocurrency wallet built for Ethereum and EVM-compatible networks. It lets users manage digital assets, review pending transactions, and interact with decentralized applications.
Rabbysend[.]site impersonates this platform using its logo and visual style. The page presents a simple "Rabby Airdrop" offer, with two call-to-action buttons: Connect Wallet and Claim Airdrop. Visitors are told to connect a wallet below in order to claim the airdrop.
Clicking either button opens a wallet connection dialog with support for over 550 options, including WalletConnect, MetaMask, Trust Wallet, Binance, SafePal, and many others. The broad selection is deliberate - it maximizes the number of visitors who can be targeted regardless of which wallet they use.
Once a wallet is connected, a cryptocurrency drainer is activated. This tool automatically transfers the victim's funds to an address controlled by the scammers. The process happens instantly, and victims often do not realize anything is wrong until the balance is already gone.
Blockchain transactions cannot be reversed. Any cryptocurrency stolen through this drainer is permanently lost - there is no mechanism to recall or refund it. Users should always confirm a website's legitimacy before connecting a wallet or engaging with any airdrop offer.
| Name | Rabby Airdrop crypto drainer |
| Threat Type | Scam, Social Engineering, Fraud, Cryptocurrency Drainer |
| Fake Claim | Participants can claim free tokens through an official Rabby Wallet airdrop |
| Disguise | Legitimate Rabby Wallet airdrop |
| Related Domain(s) | rabbysend[.]site |
| Threat Status (rabbysend[.]site) | PCrisk Website Scanner Results |
| Symptoms | Unofficial domain, lack of official verification, unrealistic claims, too good-to-be-true promises |
| Distribution methods | Fake social media accounts, deceptive websites, rogue online advertisements |
| Damage | Cryptocurrency theft |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
Cryptocurrency drainer scam examples
Rabbysend[.]site is a fraudulent page with no connection to the real Rabby Wallet project. It falsely promotes an airdrop to lure visitors into connecting their wallets, then uses a drainer to transfer their cryptocurrency to the scammers' address. The legitimate Rabby Wallet (rabby.io) is not associated with this site in any way.
Pages like rabbysend[.]site are widespread and typically copy the branding of well-known crypto projects to appear credible. Those who fall for these offers risk losing their digital assets permanently. Some examples of similar scams are "Xaman Airdrop", "ShareX Airdrop", and "XRP Ledger Airdrop".
How did I open a scam website?
Fake cryptocurrency pages are frequently distributed through stolen or fabricated social media accounts on platforms like X (formerly Twitter) and Discord. Scammers often use accounts impersonating well-known figures, official project profiles, or reputable companies to post links that look like legitimate airdrop announcements.
Users may also land on such pages through misleading ads on unreliable websites, deceptive pop-ups, phishing emails containing links, or notifications pushed by rogue pages. Adware installed on a device can also generate redirects to fraudulent crypto sites without the user taking any deliberate action.
How to avoid visiting scam pages?
Keep your operating system and all installed software up to date. Only download applications from official developer websites, verified app stores, or other trusted sources. Be cautious with unexpected emails or messages that contain links or attachments, and avoid interacting with ads or pop-ups on dubious websites.
Before connecting a wallet to any platform, double-check that the domain matches the project's official website. Do not grant notification permissions to unfamiliar pages. If your computer is already infected with unwanted apps, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate them.
The appearance of "Rabby Airdrop Scam" scam (GIF):
The official Rabby Wallet website (rabby.io):
Instant automatic malware removal:
Manual threat removal might be a lengthy and complicated process that requires advanced IT skills. Combo Cleaner is a professional automatic malware removal tool that is recommended to get rid of malware. Download it by clicking the button below:
DOWNLOAD Combo CleanerBy downloading any software listed on this website you agree to our Privacy Policy and Terms of Use. To use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
Quick menu:
- What is Rabby Airdrop crypto drainer?
- How to identify a pop-up scam?
- How do pop-up scams work?
- How to remove fake pop-ups?
- How to prevent fake pop-ups?
- What to do if you fell for a pop-up scam?
How to identify a pop-up scam?
Pop-up windows with various fake messages are a common type of lures cybercriminals use. They collect sensitive personal data, trick Internet users into calling fake tech support numbers, subscribe to useless online services, invest in shady cryptocurrency schemes, etc.
While in the majority of cases these pop-ups don't infect users' devices with malware, they can cause direct monetary loss or could result in identity theft.
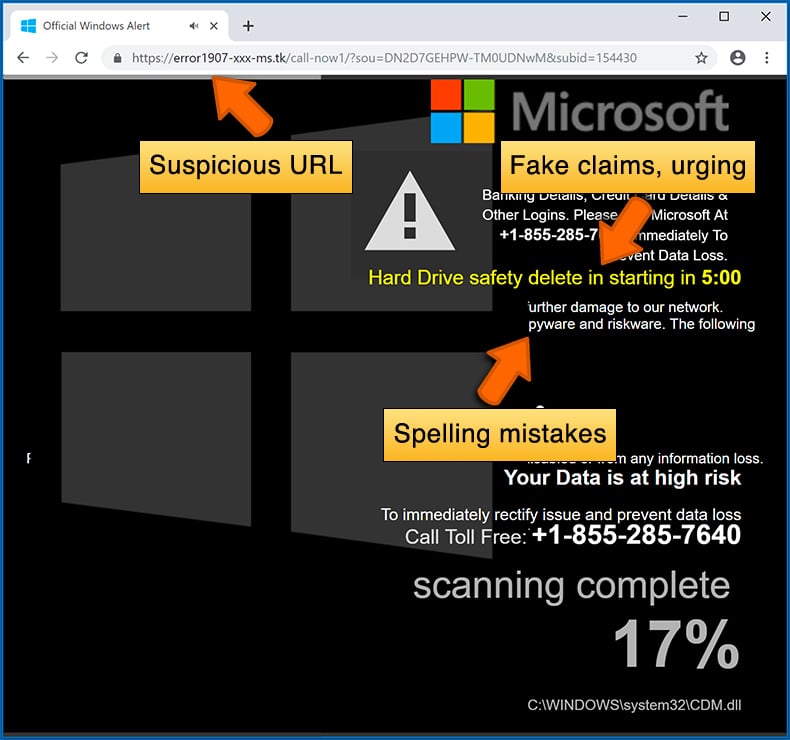
Cybercriminals strive to create their rogue pop-up windows to look trustworthy, however, scams typically have the following characteristics:
- Spelling mistakes and non-professional images - Closely inspect the information displayed in a pop-up. Spelling mistakes and unprofessional images could be a sign of a scam.
- Sense of urgency - Countdown timer with a couple of minutes on it, asking you to enter your personal information or subscribe to some online service.
- Statements that you won something - If you haven't participated in a lottery, online competition, etc., and you see a pop-up window stating that you won.
- Computer or mobile device scan - A pop-up window that scans your device and informs of detected issues - is undoubtedly a scam; webpages cannot perform such actions.
- Exclusivity - Pop-up windows stating that only you are given secret access to a financial scheme that can quickly make you rich.
Example of a pop-up scam:
How do pop-up scams work?
Cybercriminals and deceptive marketers usually use various advertising networks, search engine poisoning techniques, and shady websites to generate traffic to their pop-ups. Users land on their online lures after clicking on fake download buttons, using a torrent website, or simply clicking on an Internet search engine result.
Based on users' location and device information, they are presented with a scam pop-up. Lures presented in such pop-ups range from get-rich-quick schemes to fake virus scans.
How to remove fake pop-ups?
In most cases, pop-up scams do not infect users' devices with malware. If you encountered a scam pop-up, simply closing it should be enough. In some cases scam, pop-ups may be hard to close; in such cases - close your Internet browser and restart it.
In extremely rare cases, you might need to reset your Internet browser. For this, use our instructions explaining how to reset Internet browser settings.
How to prevent fake pop-ups?
To prevent seeing pop-up scams, you should visit only reputable websites. Torrent, Crack, free online movie streaming, YouTube video download, and other websites of similar reputation commonly redirect Internet users to pop-up scams.
To minimize the risk of encountering pop-up scams, you should keep your Internet browsers up-to-date and use reputable anti-malware application. For this purpose, we recommend Combo Cleaner Antivirus for Windows.
What to do if you fell for a pop-up scam?
This depends on the type of scam that you fell for. Most commonly, pop-up scams try to trick users into sending money, giving away personal information, or giving access to one's device.
- If you sent money to scammers: You should contact your financial institution and explain that you were scammed. If informed promptly, there's a chance to get your money back.
- If you gave away your personal information: You should change your passwords and enable two-factor authentication in all online services that you use. Visit Federal Trade Commission to report identity theft and get personalized recovery steps.
- If you let scammers connect to your device: You should scan your computer with reputable anti-malware (we recommend Combo Cleaner Antivirus for Windows) - cyber criminals could have planted trojans, keyloggers, and other malware, don't use your computer until removing possible threats.
- Help other Internet users: report Internet scams to Federal Trade Commission.
Frequently Asked Questions (FAQ)
What is a fake crypto airdrop?
A fake crypto airdrop is a fraudulent page that promises free tokens or cryptocurrency to visitors. These pages copy the look and branding of legitimate projects to appear official, but their only goal is to steal funds from anyone who interacts with them.
What is the purpose of a crypto scam?
The goal is to steal cryptocurrency. Scams like this trick visitors into connecting their wallets, then activate a drainer that moves the victim's funds to the scammers' address automatically. The theft typically occurs within seconds, and the stolen assets cannot be recovered.
Why do I encounter fake websites?
Fraudulent pages are spread through hacked or fake social media accounts, phishing emails, rogue advertising networks, and deceptive pop-ups or links on unreliable websites. In some cases, adware installed on a device can silently redirect users to scam pages.
Will Combo Cleaner protect me from scams?
Combo Cleaner can scan websites you visit and identify suspicious or malicious pages, including cryptocurrency scam sites. When a dangerous page is detected, it warns you and blocks access, helping you avoid connecting your wallet to fraudulent platforms.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion