
How to remove the uCreator remote access trojan from Android
TrojanAlso Known As: uCreator remote access trojan

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What kind of malware is uCreator RAT?
uCreator RAT (sold by its developer under the name YingGai) is a sophisticated Android spyware platform and remote access trojan. It uses app virtualization to silently instrument legitimate messaging and payment applications on infected devices. According to research published by 0x0v1, it targets users of WeChat, Telegram, GCash, and over a dozen other messaging and financial apps.
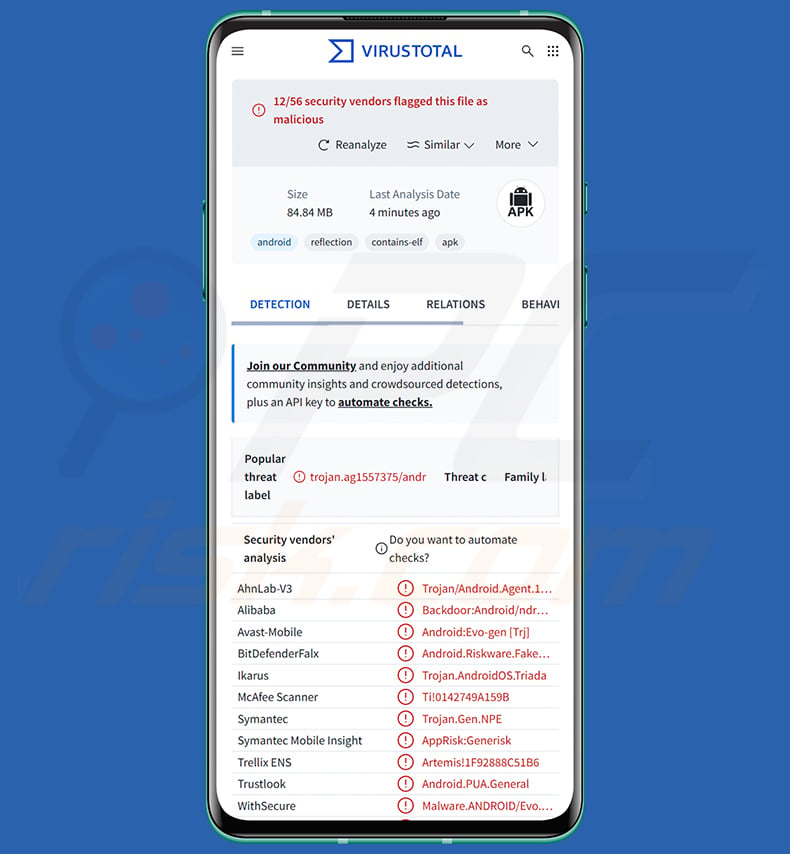
uCreator RAT malware overview
uCreator RAT is not a traditional standalone malicious application. It is a commercial surveillance platform sold under the name YingGai, built around the concept of "mass control." The platform combines an app virtualization engine, per-target hook modules, a cloud-based control infrastructure, and a Windows operator console used to manage compromised devices.
The platform gains access to legitimate apps using tools like LSPatch and Pine, built on the Xposed hooking framework. These tools load the target app's code inside a controlled process without requiring root access to the device. The target app appears to work normally while the malware runs invisibly within its own process space.
uCreator RAT is built to attack messaging and financial apps popular across China and Southeast Asia. Confirmed targets include WeChat, WeCom, QQ, Telegram, WhatsApp, LINE, Zalo, KakaoTalk, Viber, MoMo, and GCash. Evidence recovered from a C2 server indicates victims have been located in China and the United States.
The Telegram module is the most invasive component discovered. Rather than copying database files from the device, it issues live SQL queries against Telegram's own active internal SQLite database, reading message history with the app's own permissions and handles.
The same module also hooks into Telegram's two-factor authentication routine to capture the account password in plaintext, before it is ever hashed or transmitted. With that password in hand, an operator can enumerate active sessions and remove trusted devices from the authorized list.
The platform also includes dedicated code for locking the legitimate owner out of their own account entirely. This account lockout capability is an intentional, named feature, not an accidental side effect. In the worst case, an attacker could take full control of a Telegram account and prevent the victim from recovering it.
Each hooked application exposes a local HTTP command server with roughly 40 numbered handlers. These cover contact retrieval, SMS harvesting, database queries, message sending, and session manipulation. Commands arrive over a Redis message bus and run inside the target app's process with the target's own identity and permissions.
Beyond messaging apps, the platform includes a camera spoofing capability intended to defeat know-your-customer (KYC) liveness checks used by financial services. The WeChat module focuses on account cloning: harvesting login credentials and contact lists, then backing up full account data to the operator's cloud storage.
A leaked GitLab instance exposed the platform's full backend source code, including a multi-tenant operator console rented by downstream customers. The commit history identified roughly three dozen developers in Changsha, China, with commits landing as recently as autumn 2026. The infrastructure supports multiple operators simultaneously, each targeting their own fleet of victim devices.
It has to be mentioned that malware developers often improve upon their software and methodologies. Future versions of uCreator RAT could expand its target application roster or introduce additional capabilities. In summary, the presence of software like uCreator RAT on a device can lead to account takeover, serious privacy violations, financial losses, and identity theft.
| Name | uCreator remote access trojan |
| Threat Type | Android malware, malicious application, Remote Access Trojan, Remote Administration Tool, RAT, spyware. |
| Detection Names | Avast-Mobile (Android:Evo-gen [Trj]), Combo Cleaner (ndroid.Riskware.FakeApp.ABE), McAfee Scanner (Ti!0142749A159B), Full List (VirusTotal) |
| Symptoms | The device is running slow, system settings are modified without user's permission, questionable applications appear, data and battery usage is increased significantly, browsers redirect to questionable websites, intrusive advertisements are delivered. |
| Distribution methods | Repackaged legitimate applications, sideloading, social engineering. |
| Damage | Stolen personal information (private messages, contacts, passwords, two-factor authentication codes), account takeover on messaging and financial applications, monetary losses, identity theft, decreased device performance. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
Remote access trojan examples
uCreator RAT stands out among Android threats for its use of on-device app virtualization. This approach makes it especially hard for security tools to detect, since the malware operates inside a legitimate app's process rather than running as a standalone suspicious application.
Other examples of Android-targeting remote access trojans include RatHat, Night Dragon, and Flying Eagle. Malware of this type is commonly used to steal personal data, conduct financial fraud, and spy on victims without their knowledge.
Regardless of the specific threat, cybercriminals continually develop new tools to target mobile users. Staying cautious about app installation sources and keeping security software active are the most reliable defenses available to everyday users.
How did uCreator RAT infiltrate my device?
uCreator RAT reaches devices through repackaged copies of legitimate applications. Researchers found modified Telegram builds distributed through sideloading, where users are directed to install APK files manually outside the official Google Play Store. A dedicated distribution domain served these modified APKs, though it has since been taken offline.
The platform also distributes through a container app called Onion Box, which hosts target apps inside the virtualization environment. Victims are typically approached through social engineering, likely via messaging platforms or phishing links. Because repackaged apps look and behave identically to the originals, most users have no indication anything is wrong.
How to avoid installation of malware?
The safest way to avoid this type of threat is to download apps only from the official Google Play Store. App files shared through messaging apps, social media, or unfamiliar websites are a common delivery mechanism for modified malware. Check the developer's name and read user reviews before installing anything, even if the app appears familiar.
Keep your device's operating system and all installed apps up to date, since updates frequently include important security patches. Avoid clicking on suspicious links sent via SMS, messaging apps, or email. Installing reputable security software such as Combo Cleaner can detect and block malicious applications before they cause harm.
Quick menu:
- Introduction
- How to delete browsing history from the Chrome web browser?
- How to disable browser notifications in the Chrome web browser?
- How to reset the Chrome web browser?
- How to delete browsing history from the Firefox web browser?
- How to disable browser notifications in the Firefox web browser?
- How to reset the Firefox web browser?
- How to uninstall potentially unwanted and/or malicious applications?
- How to boot the Android device in "Safe Mode"?
- How to check the battery usage of various applications?
- How to check the data usage of various applications?
- How to install the latest software updates?
- How to reset the system to its default state?
- How to disable applications that have administrator privileges?
Delete browsing history from the Chrome web browser:
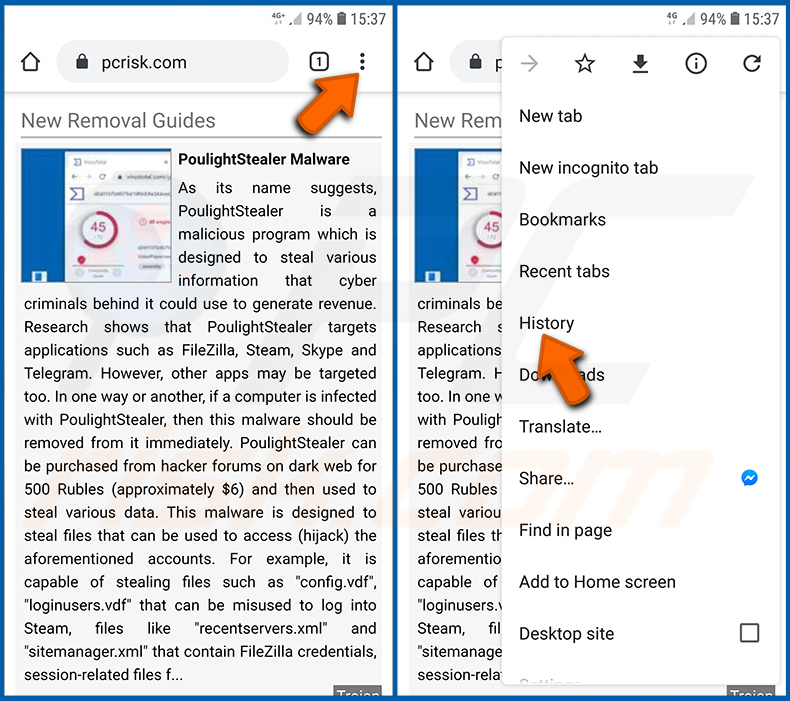
Tap the "Menu" button (three dots on the right-upper corner of the screen) and select "History" in the opened dropdown menu.
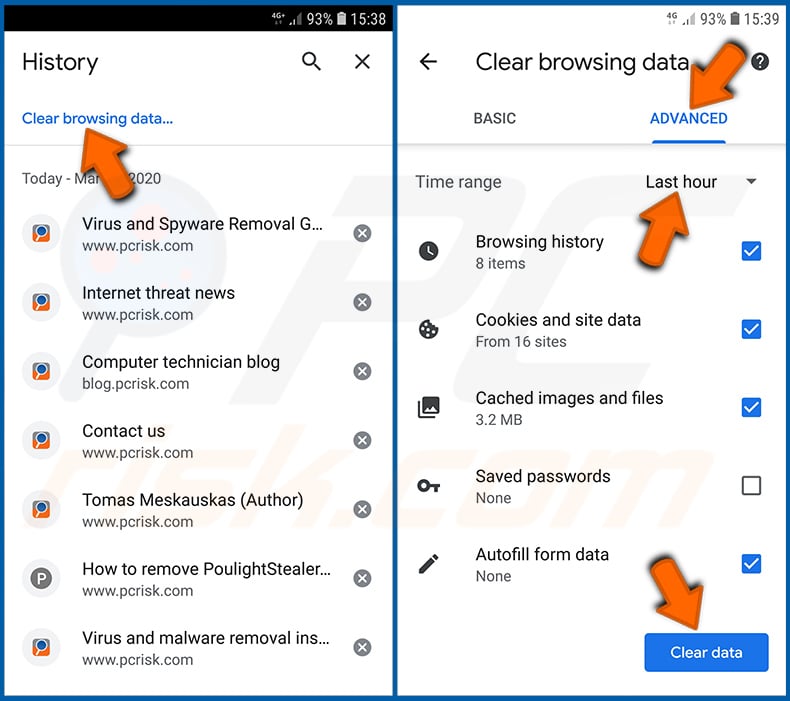
Tap "Clear browsing data", select "ADVANCED" tab, choose the time range and data types you want to delete and tap "Clear data".
Disable browser notifications in the Chrome web browser:
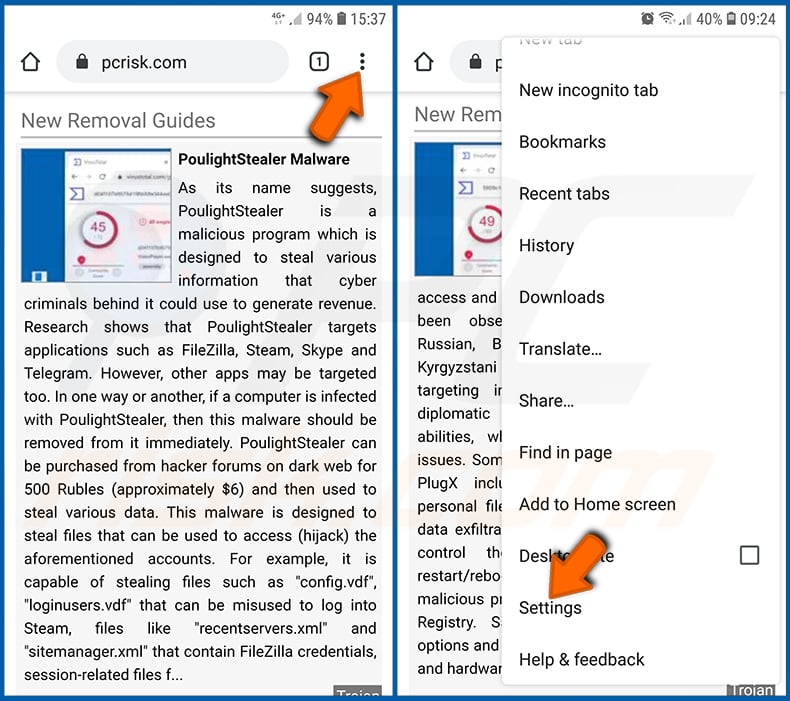
Tap the "Menu" button (three dots on the right-upper corner of the screen) and select "Settings" in the opened dropdown menu.
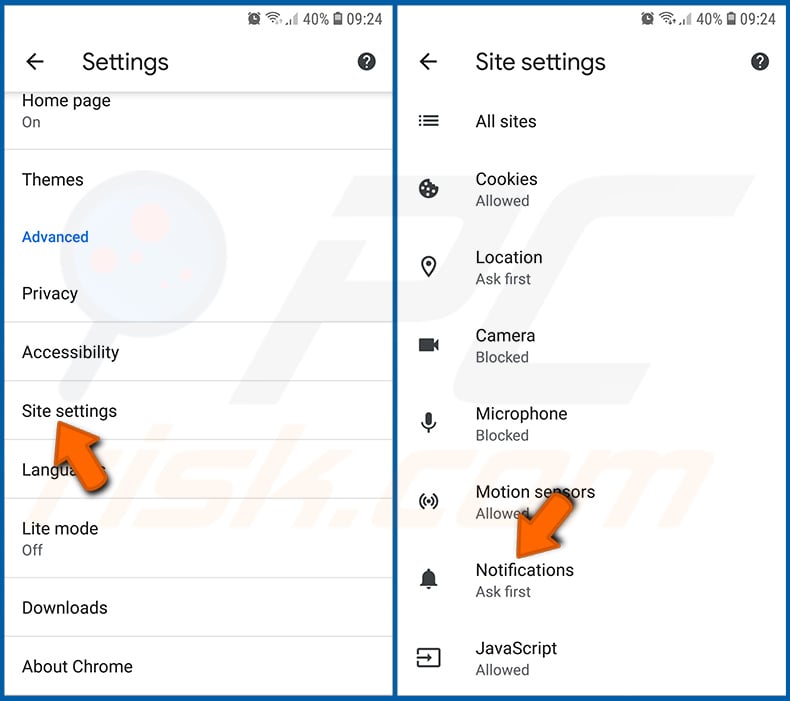
Scroll down until you see "Site settings" option and tap it. Scroll down until you see "Notifications" option and tap it.
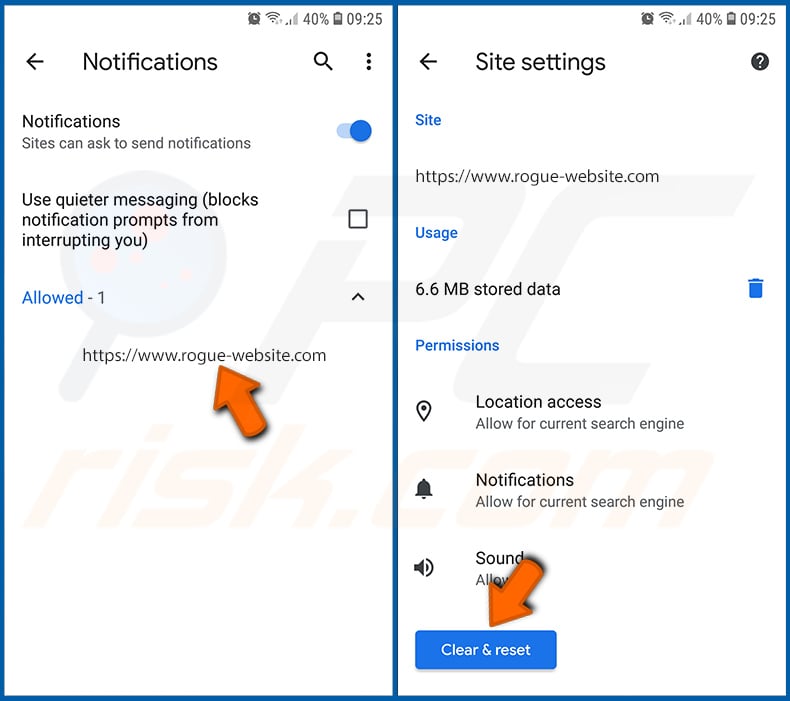
Find the websites that deliver browser notifications, tap on them and click "Clear & reset". This will remove permissions granted for these websites to deliver notifications. However, once you visit the same site again, it may ask for a permission again. You can choose whether to give these permissions or not (if you choose to decline the website will go to "Blocked" section and will no longer ask you for the permission).
Reset the Chrome web browser:
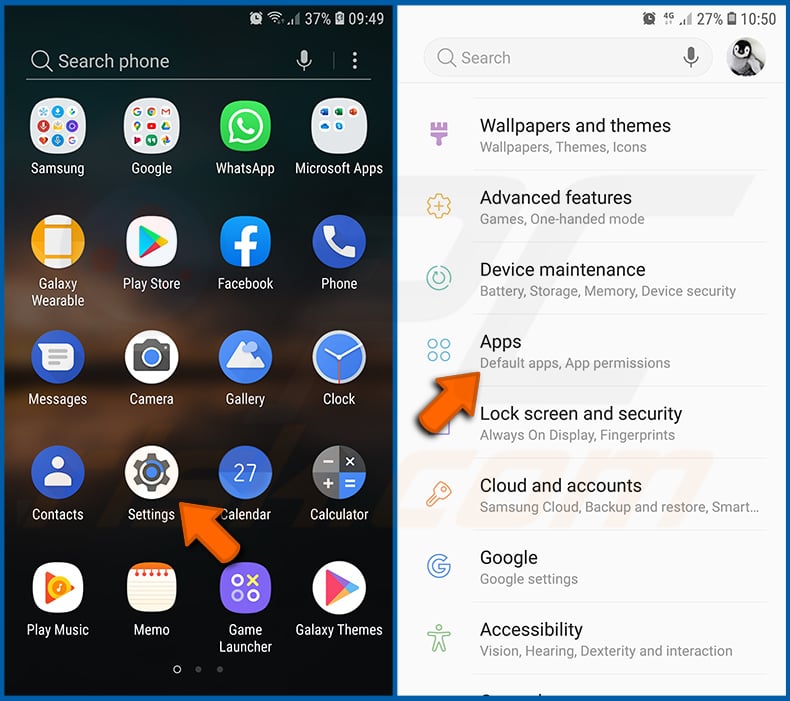
Go to "Settings", scroll down until you see "Apps" and tap it.
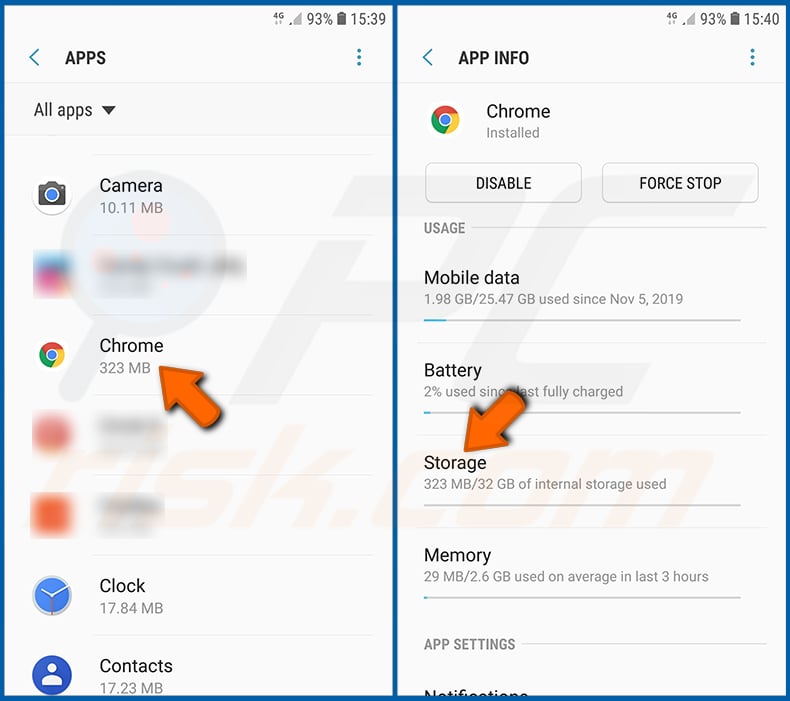
Scroll down until you find "Chrome" application, select it and tap "Storage" option.
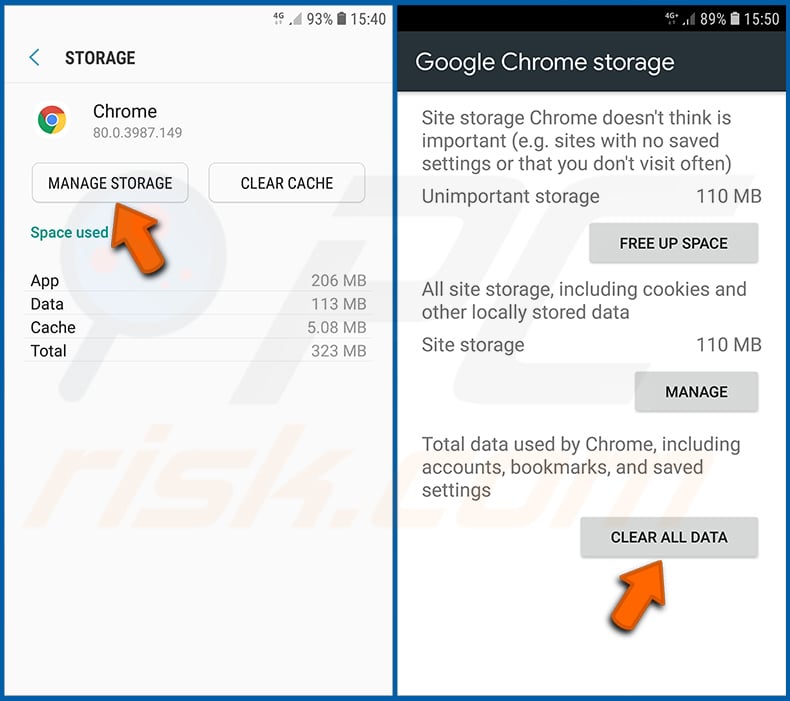
Tap "MANAGE STORAGE", then "CLEAR ALL DATA" and confirm the action by taping "OK". Note that resetting the browser will eliminate all data stored within. This means that all saved logins/passwords, browsing history, non-default settings and other data will be deleted. You will also have to re-login into all websites as well.
Delete browsing history from the Firefox web browser:
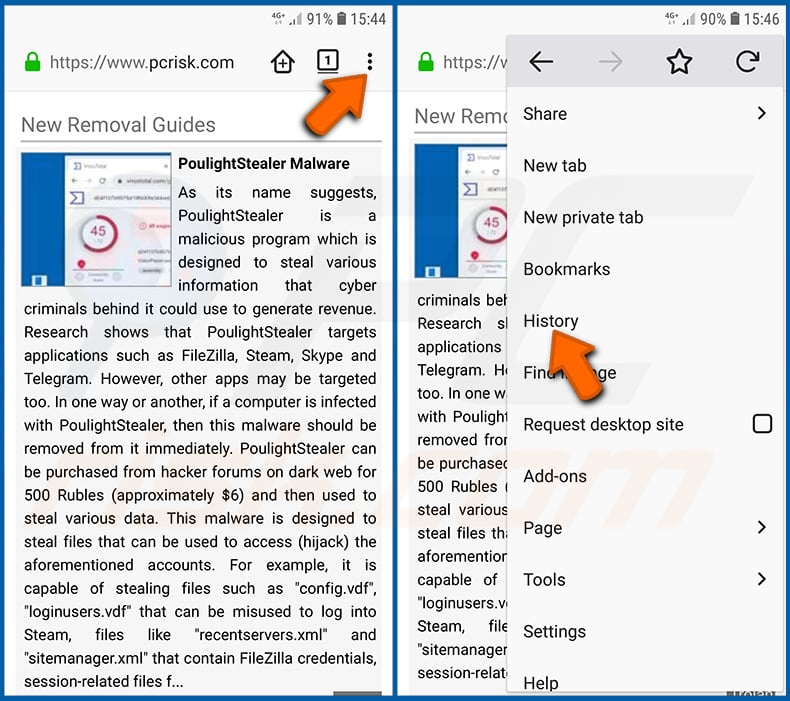
Tap the "Menu" button (three dots on the right-upper corner of the screen) and select "History" in the opened dropdown menu.
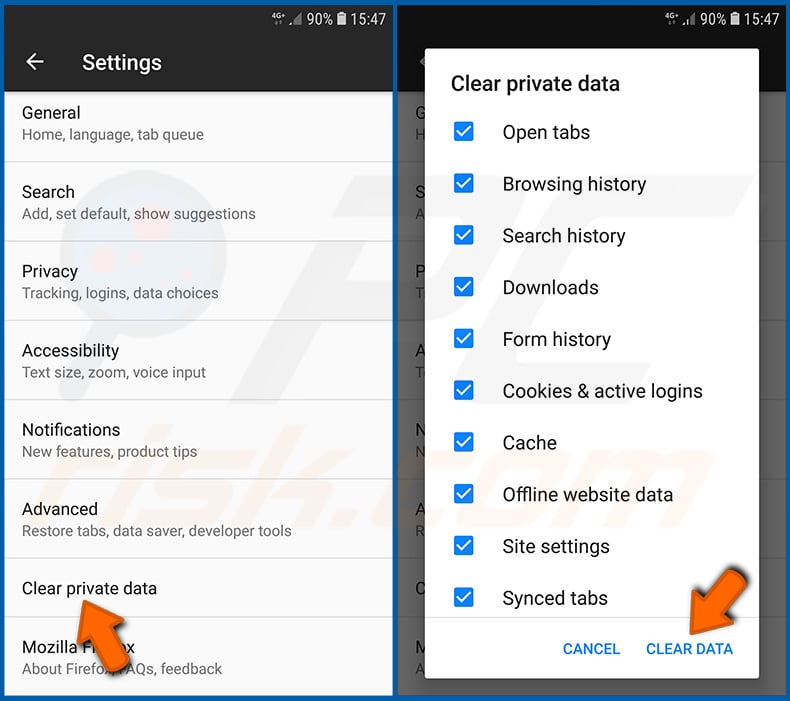
Scroll down until you see "Clear private data" and tap it. Select data types you want to remove and tap "CLEAR DATA".
Disable browser notifications in the Firefox web browser:
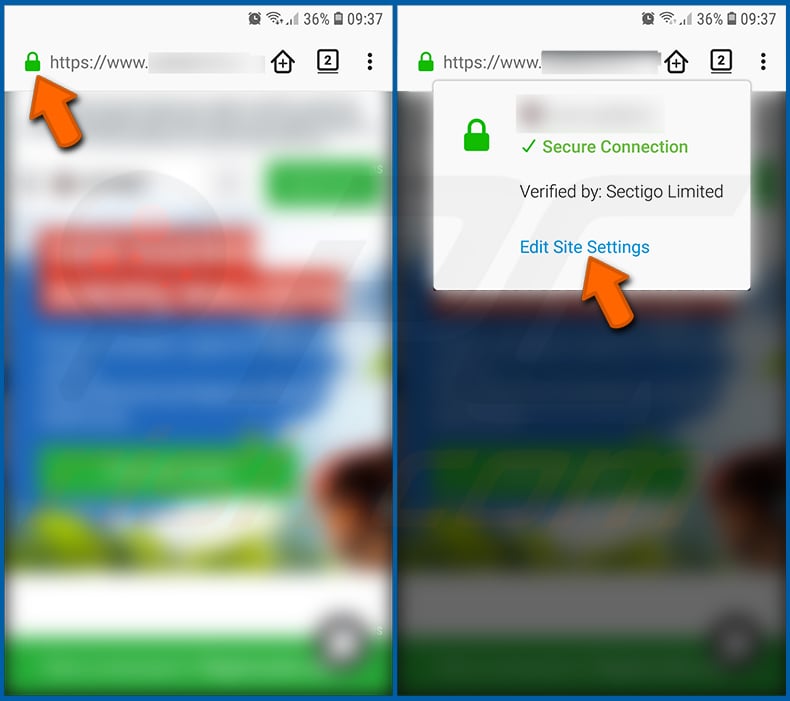
Visit the website that is delivering browser notifications, tap the icon displayed on the left of URL bar (the icon will not necessarily be a "Lock") and select "Edit Site Settings".
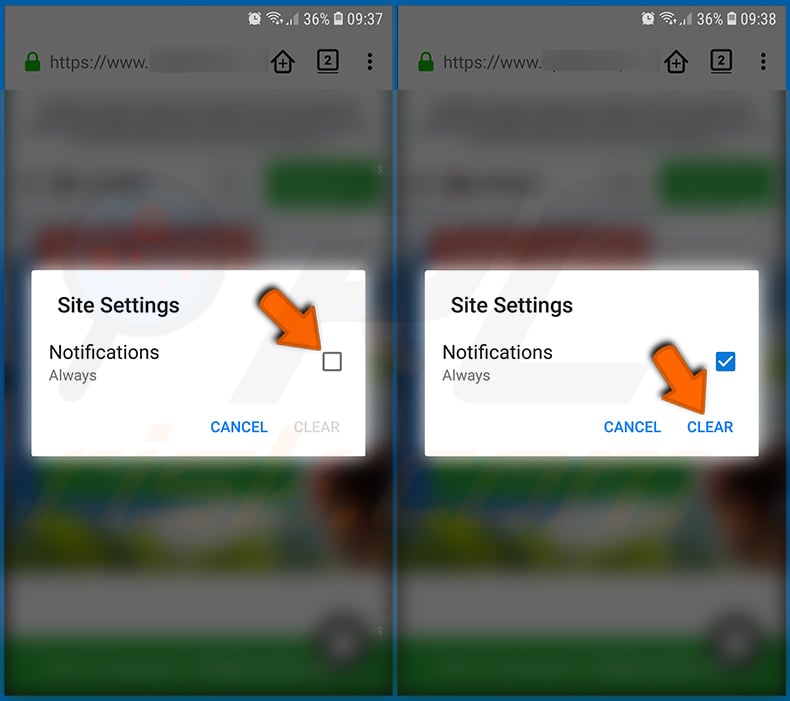
In the opened pop-up opt-in the "Notifications" option and tap "CLEAR".
Reset the Firefox web browser:
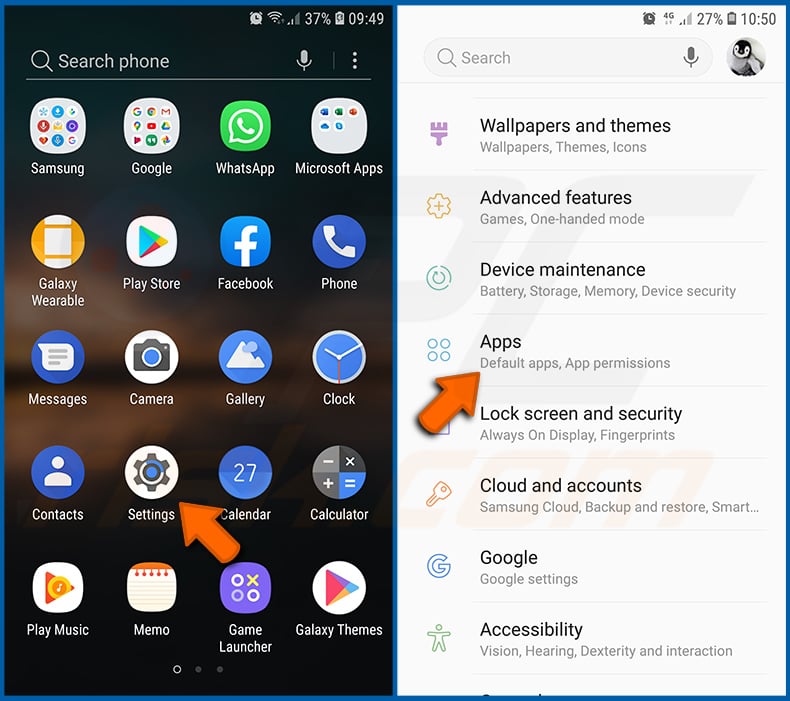
Go to "Settings", scroll down until you see "Apps" and tap it.
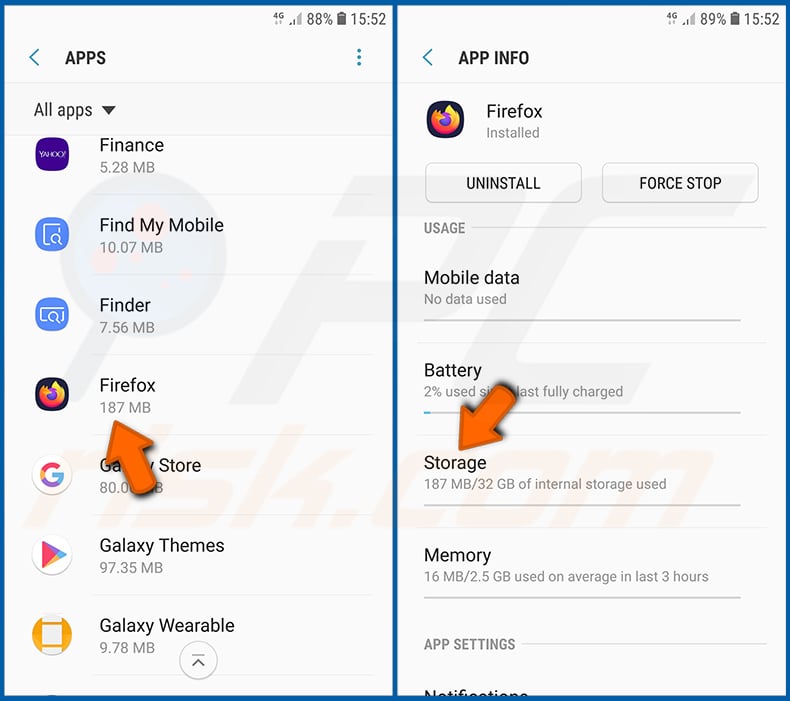
Scroll down until you find "Firefox" application, select it and tap "Storage" option.
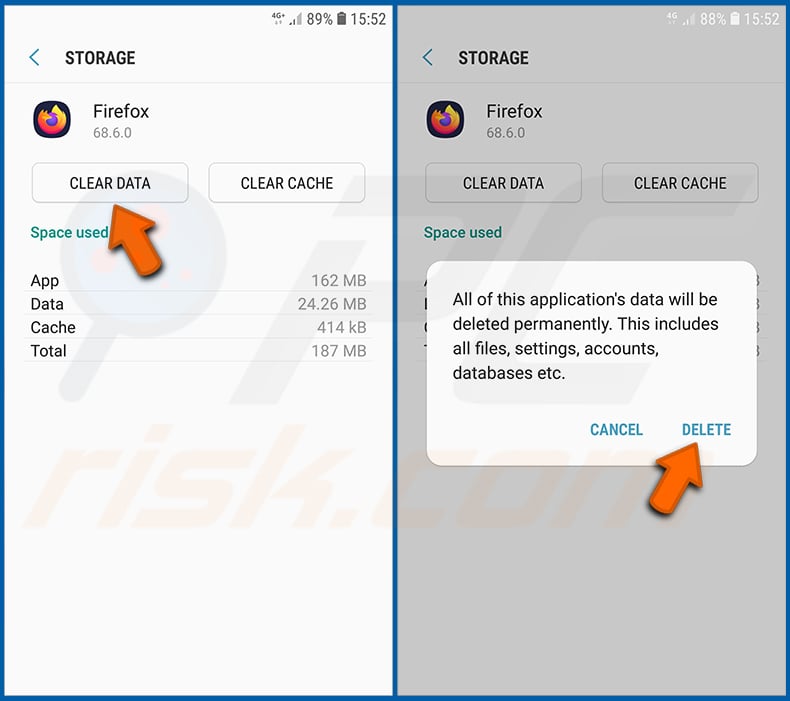
Tap "CLEAR DATA" and confirm the action by taping "DELETE". Note that resetting the browser will eliminate all data stored within. This means that all saved logins/passwords, browsing history, non-default settings and other data will be deleted. You will also have to re-login into all websites as well.
Uninstall potentially unwanted and/or malicious applications:
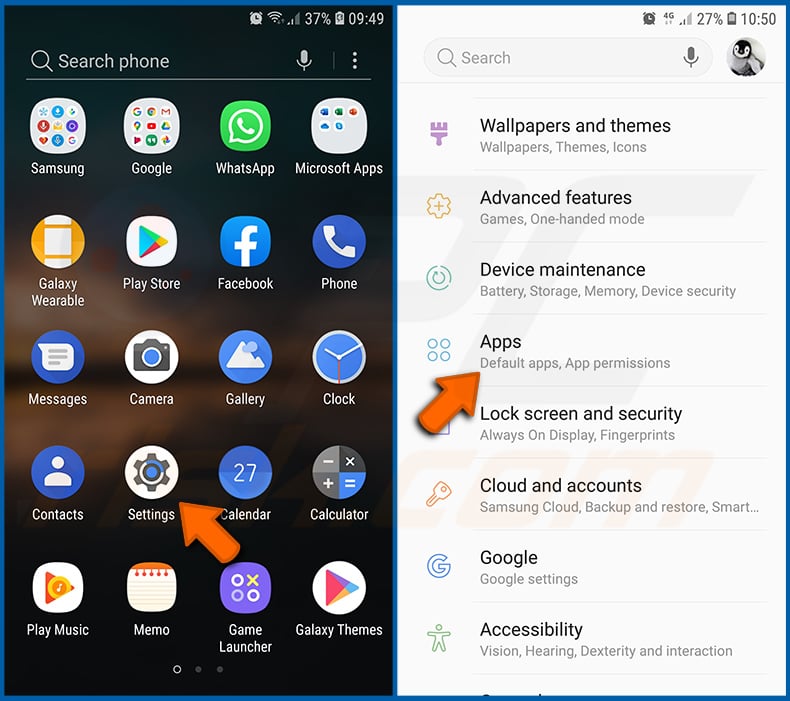
Go to "Settings", scroll down until you see "Apps" and tap it.
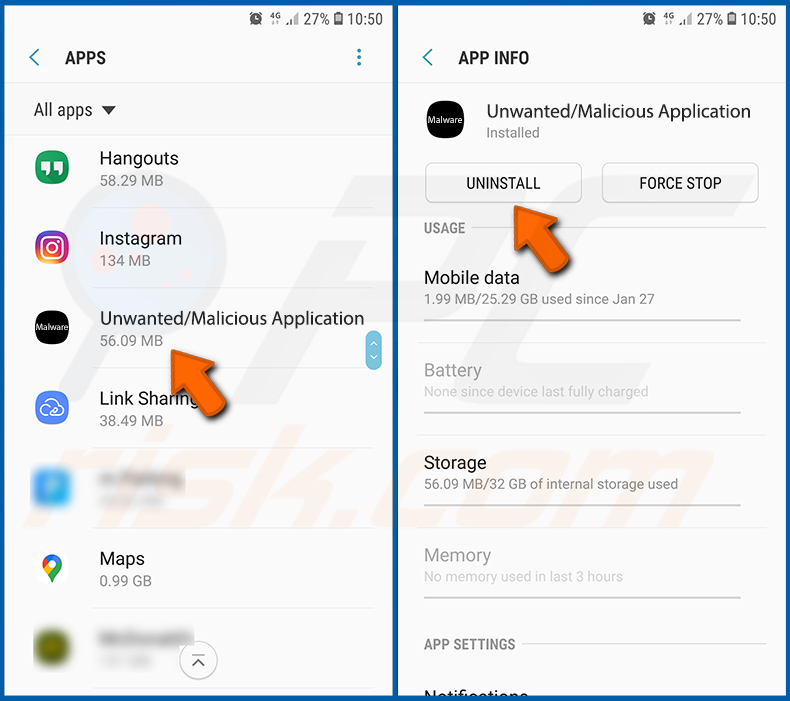
Scroll down until you see a potentially unwanted and/or malicious application, select it and tap "Uninstall". If, for some reason, you are unable to remove the selected app (e.g., you are prompted with an error message), you should try using the "Safe Mode".
Boot the Android device in "Safe Mode":
The "Safe Mode" in Android operating system temporarily disables all third-party applications from running. Using this mode is a good way to diagnose and solve various issues (e.g., remove malicious applications that prevent users you from doing so when the device is running "normally").
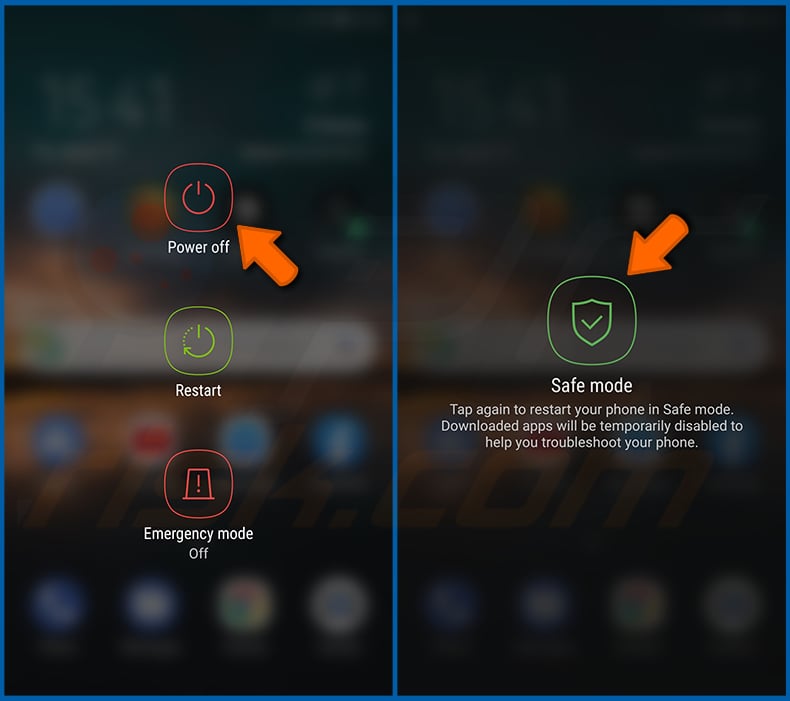
Push the "Power" button and hold it until you see the "Power off" screen. Tap the "Power off" icon and hold it. After a few seconds the "Safe Mode" option will appear and you'll be able run it by restarting the device.
Check the battery usage of various applications:
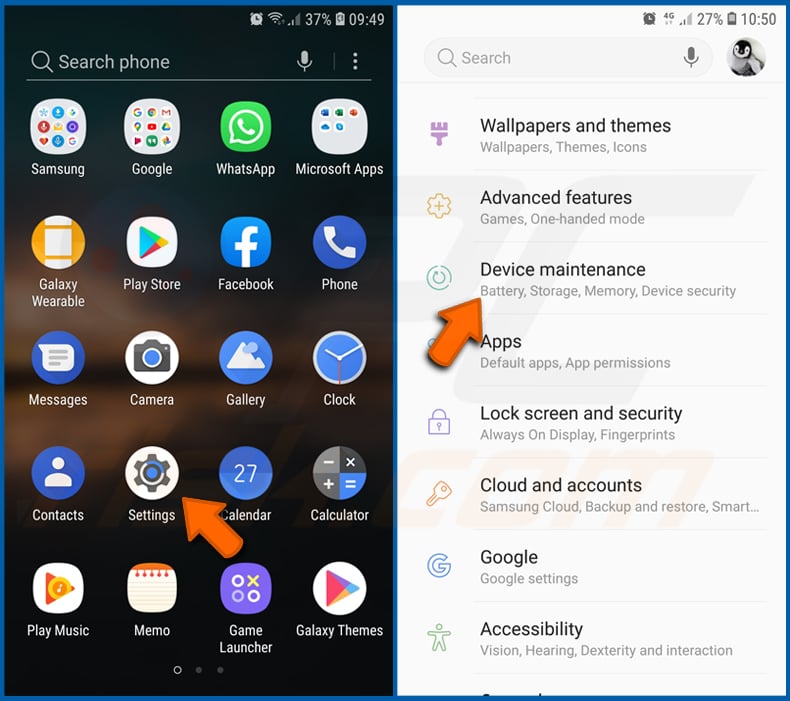
Go to "Settings", scroll down until you see "Device maintenance" and tap it.
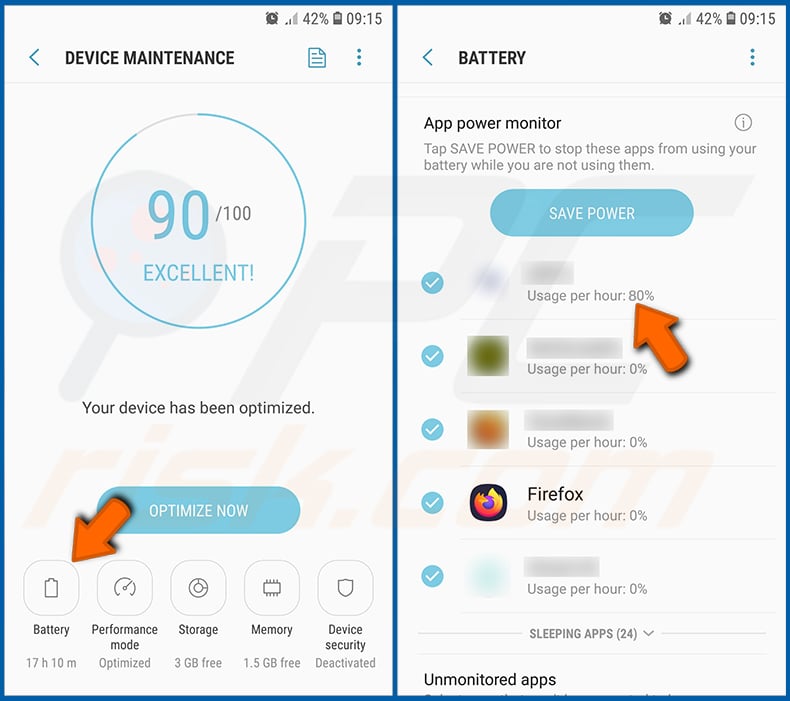
Tap "Battery" and check the usage of each application. Legitimate/genuine applications are designed to use as low energy as possible in order to provide the best user experience and to save power. Therefore, high battery usage may indicate that the application is malicious.
Check the data usage of various applications:
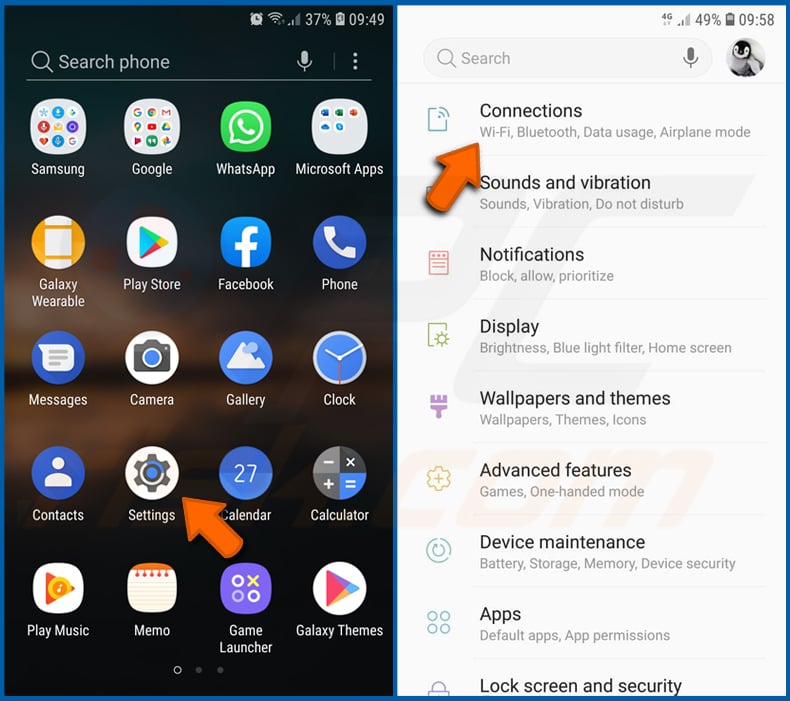
Go to "Settings", scroll down until you see "Connections" and tap it.
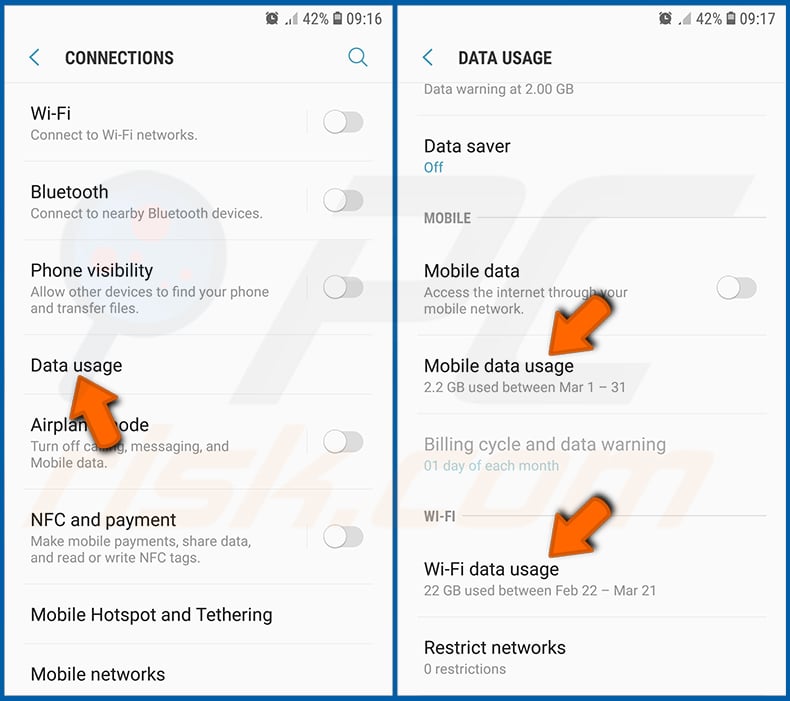
Scroll down until you see "Data usage" and select this option. As with battery, legitimate/genuine applications are designed to minimize data usage as much as possible. This means that huge data usage may indicate presence of malicious application. Note that some malicious applications might be designed to operate when the device is connected to wireless network only. For this reason, you should check both Mobile and Wi-Fi data usage.
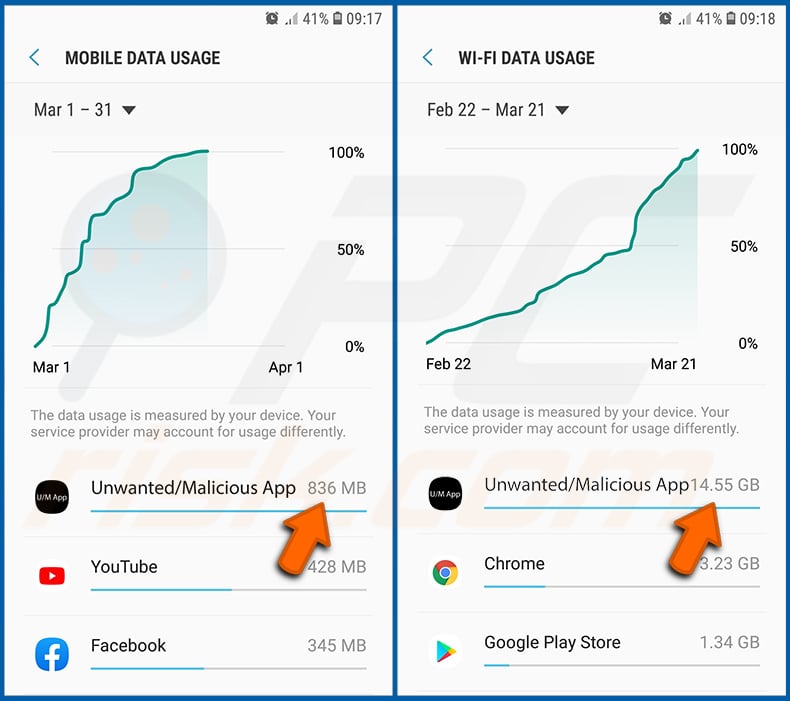
If you find an application that uses a lot of data even though you never use it, then we strongly advise you to uninstall it as soon as possible.
Install the latest software updates:
Keeping the software up-to-date is a good practice when it comes to device safety. The device manufacturers are continually releasing various security patches and Android updates in order to fix errors and bugs that can be abused by cybercriminals. An outdated system is way more vulnerable, which is why you should always be sure that your device's software is up-to-date.
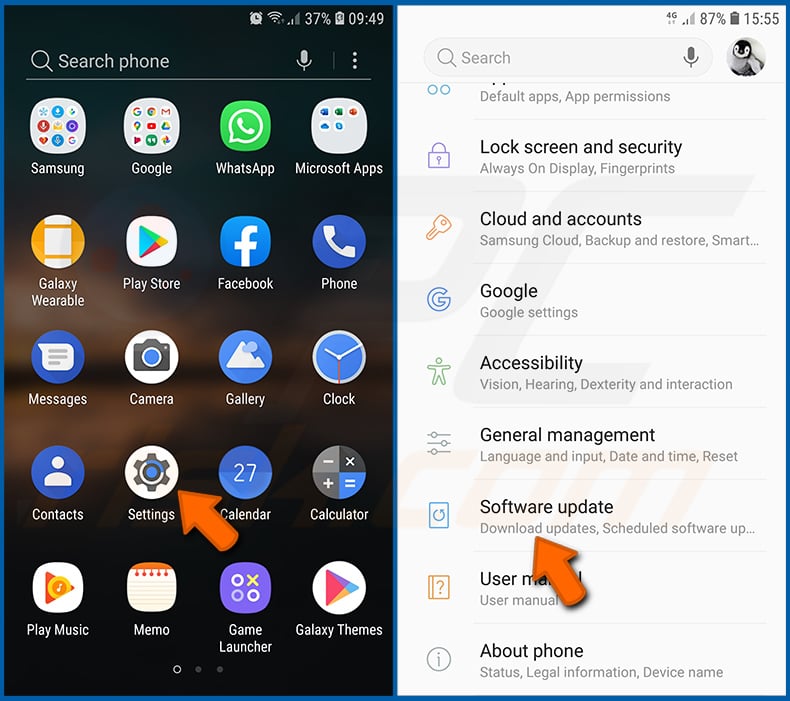
Go to "Settings", scroll down until you see "Software update" and tap it.
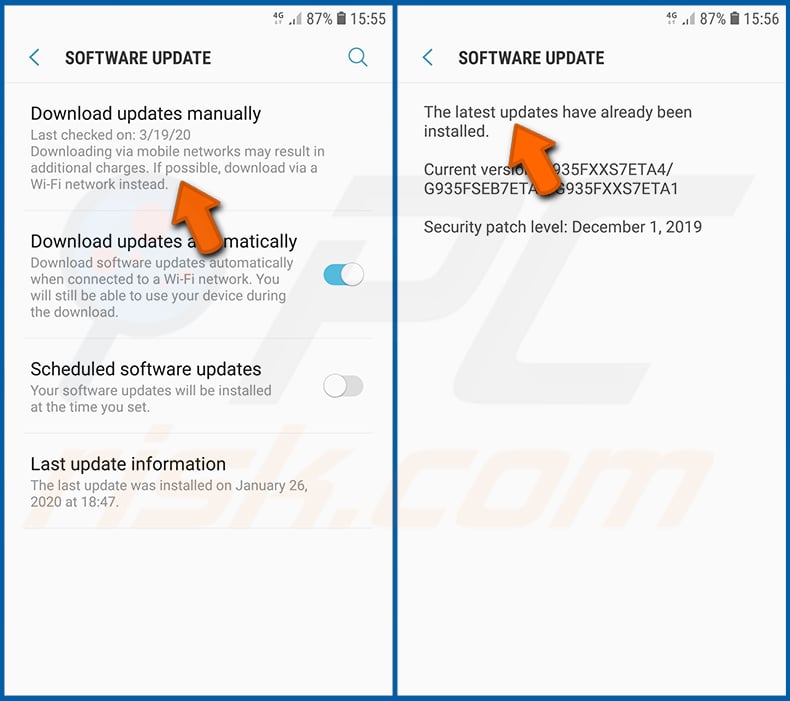
Tap "Download updates manually" and check if there are any updates available. If so, install them immediately. We also recommend to enable the "Download updates automatically" option - it will enable the system to notify you once an update is released and/or install it automatically.
Reset the system to its default state:
Performing a "Factory Reset" is a good way to remove all unwanted applications, restore system's settings to default and clean the device in general. However, you must keep in mind that all data within the device will be deleted, including photos, video/audio files, phone numbers (stored within the device, not the SIM card), SMS messages, and so forth. In other words, the device will be restored to its primal state.
You can also restore the basic system settings and/or simply network settings as well.
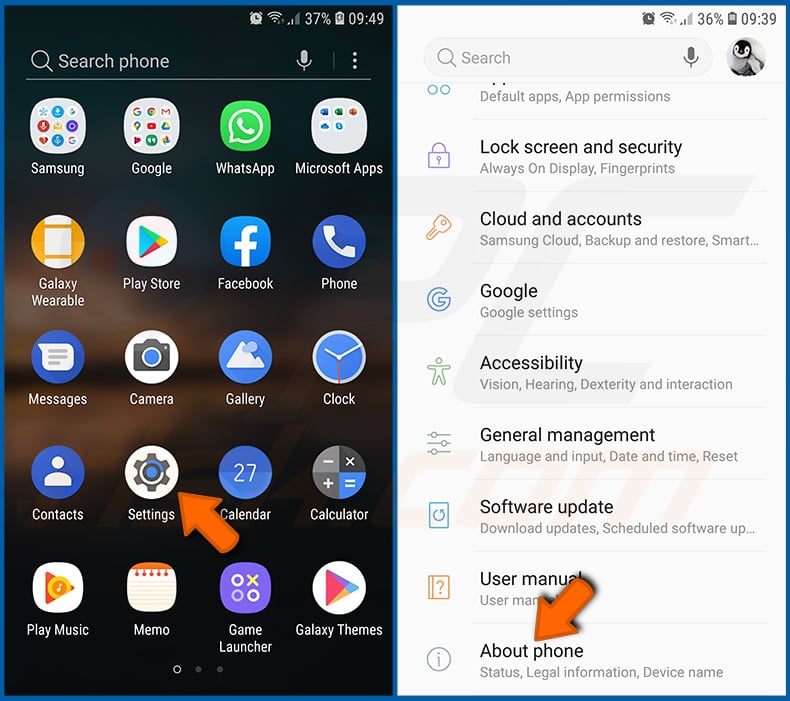
Go to "Settings", scroll down until you see "About phone" and tap it.
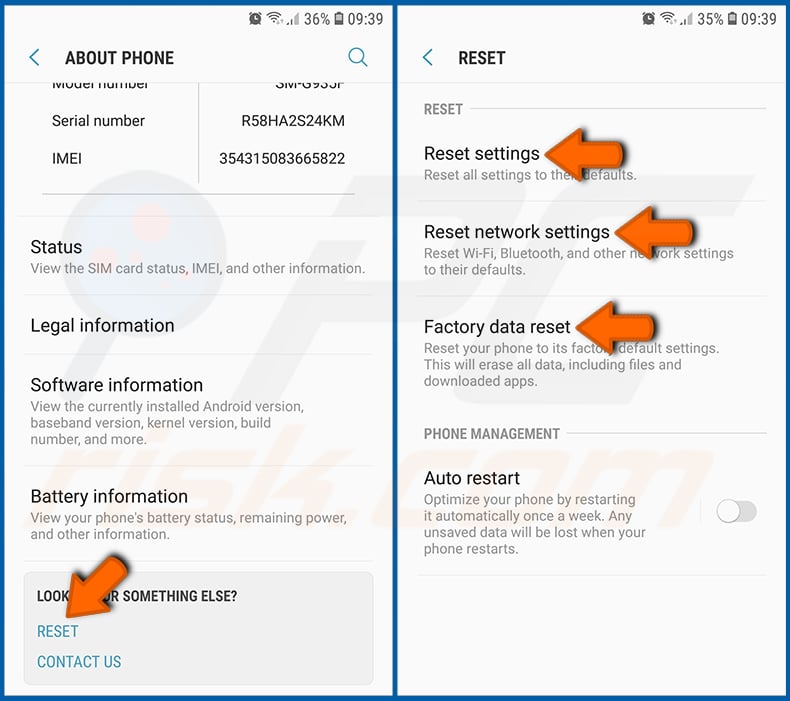
Scroll down until you see "Reset" and tap it. Now choose the action you want to perform:
"Reset settings" - restore all system settings to default;
"Reset network settings" - restore all network-related settings to default;
"Factory data reset" - reset the entire system and completely delete all stored data;
Disable applications that have administrator privileges:
If a malicious application gets administrator-level privileges it can seriously damage the system. To keep the device as safe as possible you should always check what apps have such privileges and disable the ones that shouldn't.
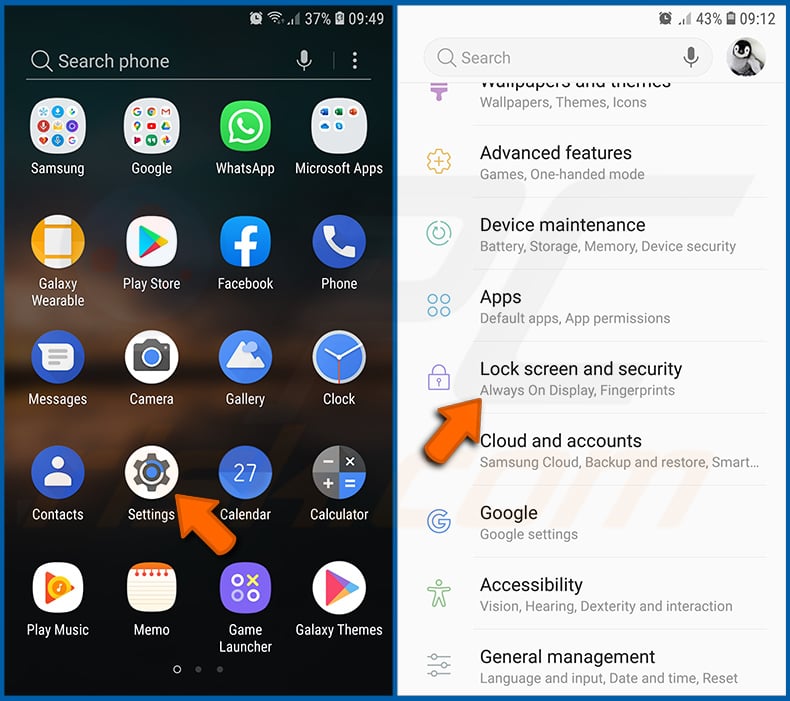
Go to "Settings", scroll down until you see "Lock screen and security" and tap it.
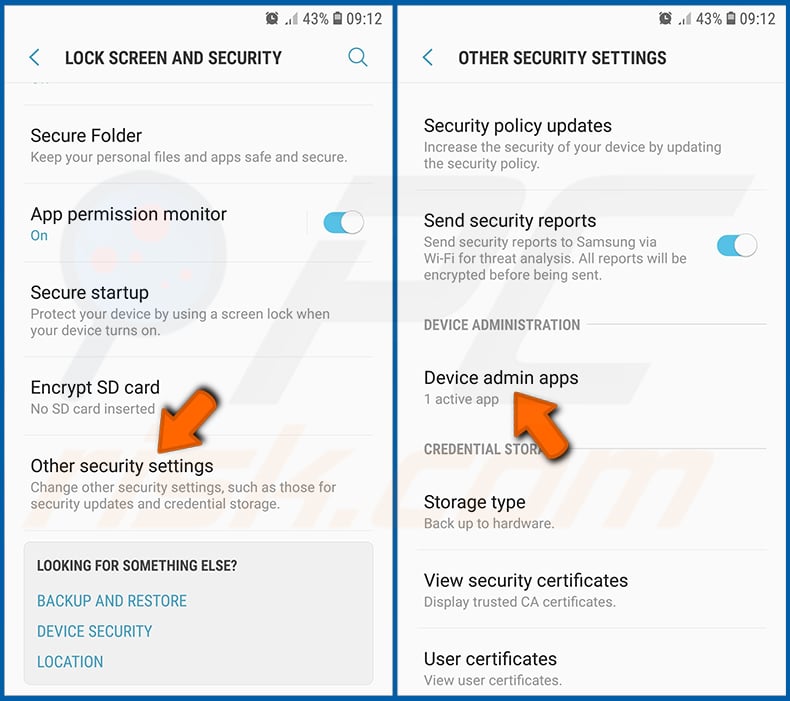
Scroll down until you see "Other security settings", tap it and then tap "Device admin apps".
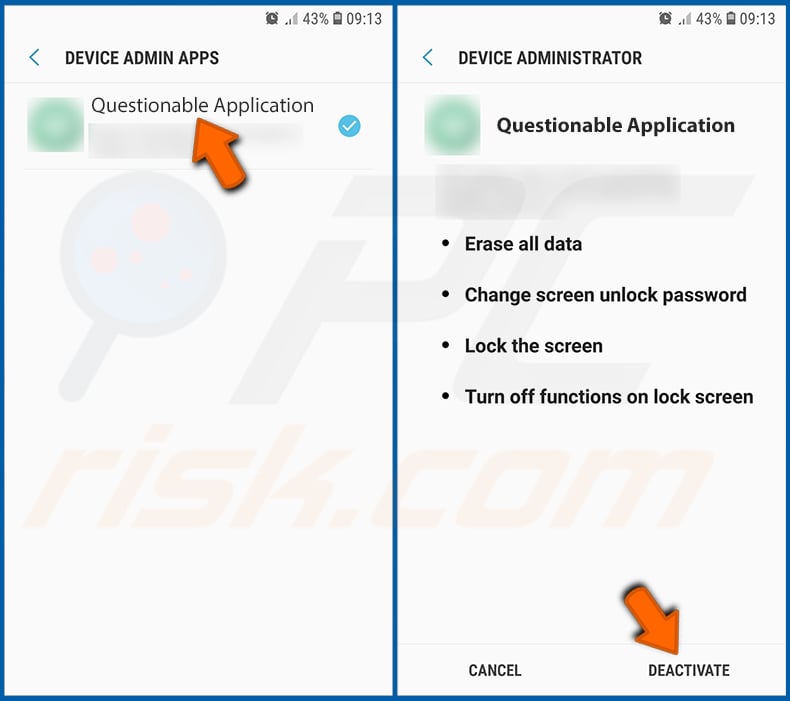
Identify applications that should not have administrator privileges, tap them and then tap "DEACTIVATE".
Frequently Asked Questions (FAQ)
My Android device is infected with uCreator RAT malware, should I format my storage device to get rid of it?
Formatting is rarely necessary for malware removal and would result in permanent data loss. It is advisable to run reputable mobile antivirus software like Combo Cleaner to scan and remove uCreator RAT, which should be sufficient in most cases.
What are the biggest issues that uCreator RAT malware can cause?
uCreator RAT can fully take over Telegram and WeChat accounts, including bypassing two-factor authentication to lock the legitimate owner out. It can extract complete message histories, harvest contact lists, and capture login credentials for financial apps like GCash.
These capabilities can lead to identity theft, financial fraud, and permanent loss of access to affected accounts. Because the platform is sold to multiple operators, a compromised device may be targeted by more than one actor at the same time.
What is the purpose of uCreator RAT malware?
Most malware attacks are driven by financial gain, and uCreator RAT is no exception. It is sold as a commercial platform to operators who use it for account fraud, financial theft, and contact harvesting at scale. The platform's infrastructure also suggests it can be used for targeted surveillance of specific individuals.
How did uCreator RAT malware infiltrate my Android device?
uCreator RAT is distributed through repackaged versions of legitimate apps like Telegram and WeChat. Victims are typically directed to install a modified APK file outside the official app store, often through phishing links or social engineering via messaging platforms. The repackaged apps look identical to the originals, making them difficult to identify.
Will Combo Cleaner protect me from malware?
Combo Cleaner is capable of detecting and eliminating the vast majority of known malware infections, including remote access trojans. Performing a complete system scan is essential, as sophisticated threats like uCreator RAT are designed to embed themselves deeply within the system.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion