

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What kind of malware is ChainScript RAT?
ChainScript is a Remote Access Trojan (RAT) written in Node.js that lets attackers secretly control infected Windows computers. It can run commands, handle files, take screenshots, look for cryptocurrency wallets, and install other malware.
The RAT was documented in September 2026 by the Adversary Pursuit Group at Blackpoint Cyber. According to their research, ChainScript is delivered via ClickFix lures and fake installers posing as Spotify, Zoom Workplace, and Microsoft Teams.
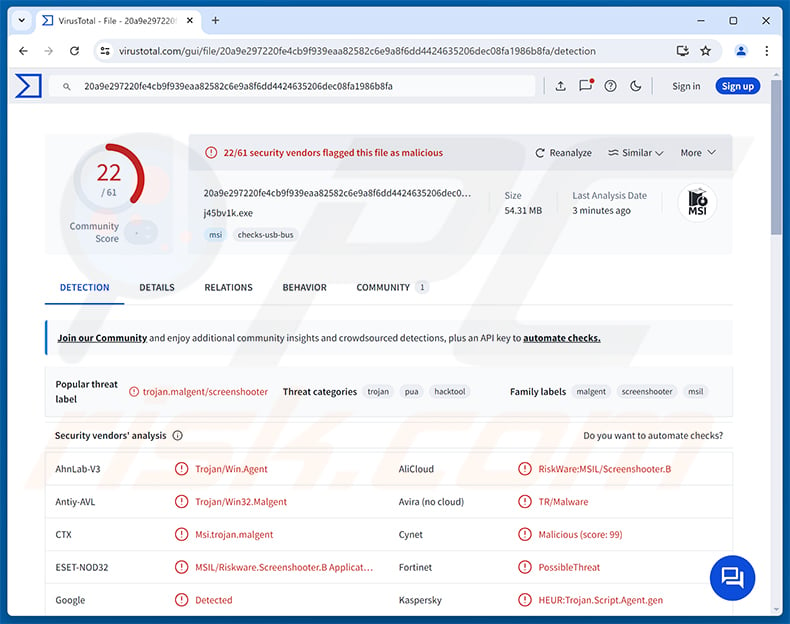
ChainScript RAT overview
The infection starts with a Windows installer (MSI file). Once launched, it runs a hidden PowerShell script that scatters the malware's components (including its own copy of Node.js) across folders with Microsoft-themed names, so they look like ordinary system files at a glance.
A small VBScript file then starts the main agent, which quietly runs in the background. It is worth noting that the installer runs under the current user's account. In other words, it does not need administrator permission and does not trigger a Windows prompt that might alert the victim.
How ChainScript uses the blockchain
ChainScript's most unusual trait is how it finds its Command and Control (C2) server. Instead of storing a fixed server address, it reads the current one from a smart contract on the Polygon blockchain. Researchers describe this as an EtherHiding-style technique.
Because blockchain records are public and hard to take down, the attackers can move to new servers simply by updating the contract. Infected computers pick up the new address automatically, so shutting down a single server does not cut off the victims. The agent then keeps a live connection to the server over WebSocket.
To make analysis harder, ChainScript also hides its configuration with several layers of encoding and waits a random 10 to 30 seconds before contacting the server for the first time. Blackpoint Cyber observed several build names (ComponentTask33, UpdateDigital, HostShared, and OrchidViolet66), all sharing the same core agent.
ChainScript's features
ChainScript gives attackers an interactive command prompt and PowerShell session on the infected machine, which means they can run practically any command. It can also browse, read, upload, overwrite, and delete files, as well as capture screenshots of the victim's desktop.
Another notable feature is a scan for cryptocurrency wallets, covering both desktop wallet apps and wallet extensions installed in web browsers. This makes the RAT especially dangerous for people who keep cryptocurrency on their computer.
On top of that, ChainScript can download and run further payloads (MSI installers, PowerShell or CMD scripts), execute arbitrary JavaScript code, update itself, and remove itself on command. As a result, a single infection can be used to deliver other malware, such as stealers or ransomware.
Persistence
To survive reboots, ChainScript creates a scheduled task that launches it every time the user logs in. If that does not work, it adds itself to the Run key in the Windows Registry as a fallback. Both methods work without administrator rights.
| Name | ChainScript remote access trojan |
| Threat Type | Remote Access Trojan (RAT) |
| Detection Names | ESET-NOD32 (MSIL/Riskware.Screenshooter.B application), Kaspersky (HEUR:Trojan.Script.Agent.gen), Microsoft (Trojan:Win32/Malgent), McAfee Scanner (Ti!20A9E297220F), Full List (VirusTotal) |
| Symptoms | Remote Access Trojans are designed to stealthily infiltrate the victim's computer and remain silent, and thus no particular symptoms are clearly visible on an infected machine. |
| Distribution methods | ClickFix, fake software installers, deceptive websites, social engineering. |
| Damage | Stolen passwords and banking information, identity theft, the victim's computer added to a botnet, additional infections, monetary loss, account hijacking. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
Conclusion
ChainScript gives cybercriminals broad control over an infected computer, from running commands and stealing files to hunting for cryptocurrency wallets and installing more malware. Its blockchain-based server lookup also makes it harder to disrupt. Victims risk financial loss, account hijacking, identity theft, and additional infections, so the RAT should be removed immediately. More examples of RATs are PEEP, DarkTortilla, and PollCat.
How did ChainScript RAT infiltrate my computer?
As reported by The Hacker News, ChainScript is being spread through ClickFix-style lures. These are deceptive web pages that show a fake verification check or error message and tell the visitor to open the Windows Run dialog (Win+R), paste a command, and press Enter. Doing so downloads and launches the malicious installer.
The installers are disguised as popular software, including Spotify, Zoom Workplace, and Microsoft Teams, and carry random-looking names such as ComponentTask33-4d14e6ac.msi or UpdateDigital-0c3c5204.msi. Users who believe they are setting up a familiar app end up infecting their own computer.
More generally, RATs like ChainScript are also distributed via phishing emails, malicious ads, fake download sites, pirated software and cracks, P2P networks, and fake updates. Malicious files usually arrive as archives, executables, MSI installers, documents, or scripts.
How to avoid installation of malware?
Never paste commands into the Run dialog, PowerShell, or a terminal because a website asks you to. No legitimate CAPTCHA or error fix works this way. Download software only from official websites and trusted app stores, and avoid cracks, key generators, and pirated programs.
Be careful with unexpected emails, attachments, and links, and ignore suspicious ads and pop-ups on questionable websites. Keep the operating system and installed apps up to date, and use reputable security software. If you believe that your computer is already infected, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate infiltrated malware.
Instant automatic malware removal:
Manual threat removal might be a lengthy and complicated process that requires advanced IT skills. Combo Cleaner is a professional automatic malware removal tool that is recommended to get rid of malware. Download it by clicking the button below:
DOWNLOAD Combo CleanerBy downloading any software listed on this website you agree to our Privacy Policy and Terms of Use. To use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
Quick menu:
- What is ChainScript RAT?
- STEP 1. Manual removal of ChainScript RAT malware.
- STEP 2. Check if your computer is clean.
How to remove malware manually?
Manual malware removal is a complicated task - usually it is best to allow antivirus or anti-malware programs to do this automatically. To remove this malware we recommend using Combo Cleaner Antivirus for Windows.
If you wish to remove malware manually, the first step is to identify the name of the malware that you are trying to remove. Here is an example of a suspicious program running on a user's computer:
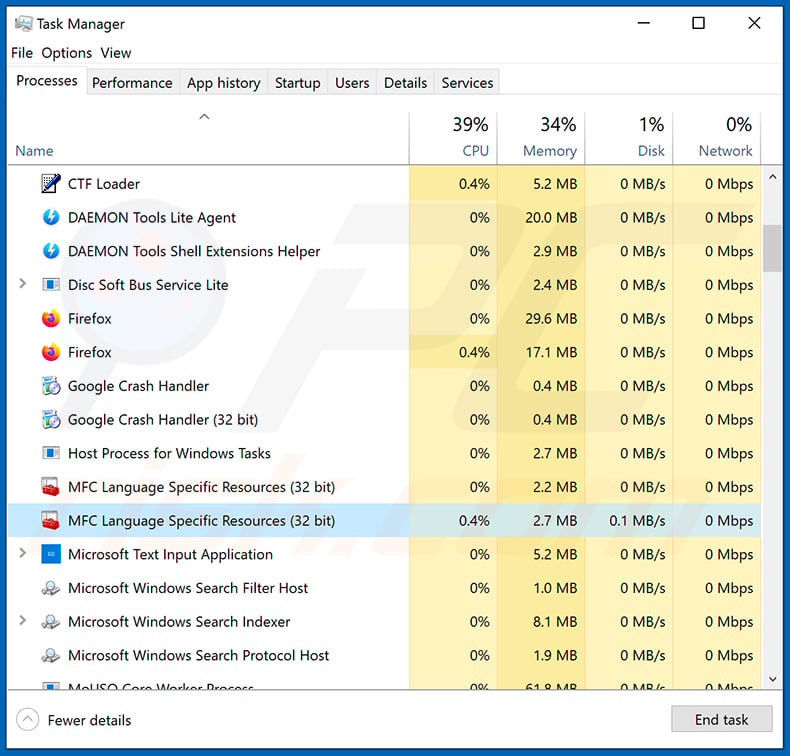
If you checked the list of programs running on your computer, for example, using task manager, and identified a program that looks suspicious, you should continue with these steps:
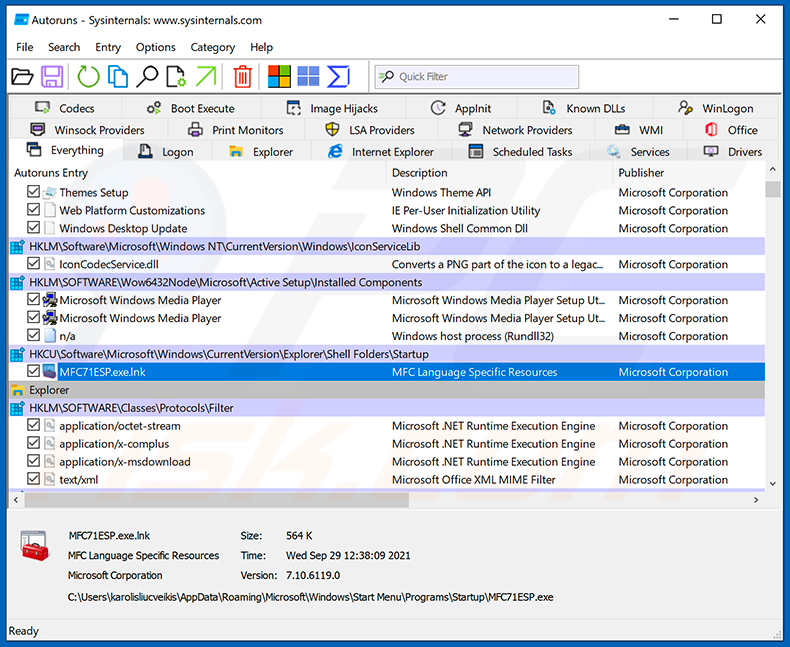
 Download a program called Autoruns. This program shows auto-start applications, Registry, and file system locations:
 Restart your computer into Safe Mode:
Windows XP and Windows 7 users: Start your computer in Safe Mode. Click Start, click Shut Down, click Restart, click OK. During your computer start process, press the F8 key on your keyboard multiple times until you see the Windows Advanced Option menu, and then select Safe Mode with Networking from the list.
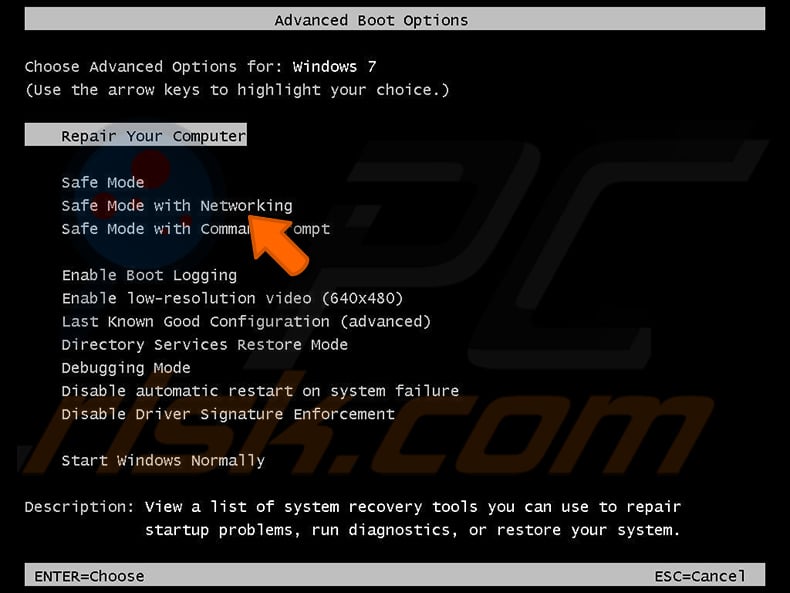
Video showing how to start Windows 7 in "Safe Mode with Networking":
Windows 8 users: Start Windows 8 is Safe Mode with Networking - Go to Windows 8 Start Screen, type Advanced, in the search results select Settings. Click Advanced startup options, in the opened "General PC Settings" window, select Advanced startup.
Click the "Restart now" button. Your computer will now restart into the "Advanced Startup options menu". Click the "Troubleshoot" button, and then click the "Advanced options" button. In the advanced option screen, click "Startup settings".
Click the "Restart" button. Your PC will restart into the Startup Settings screen. Press F5 to boot in Safe Mode with Networking.
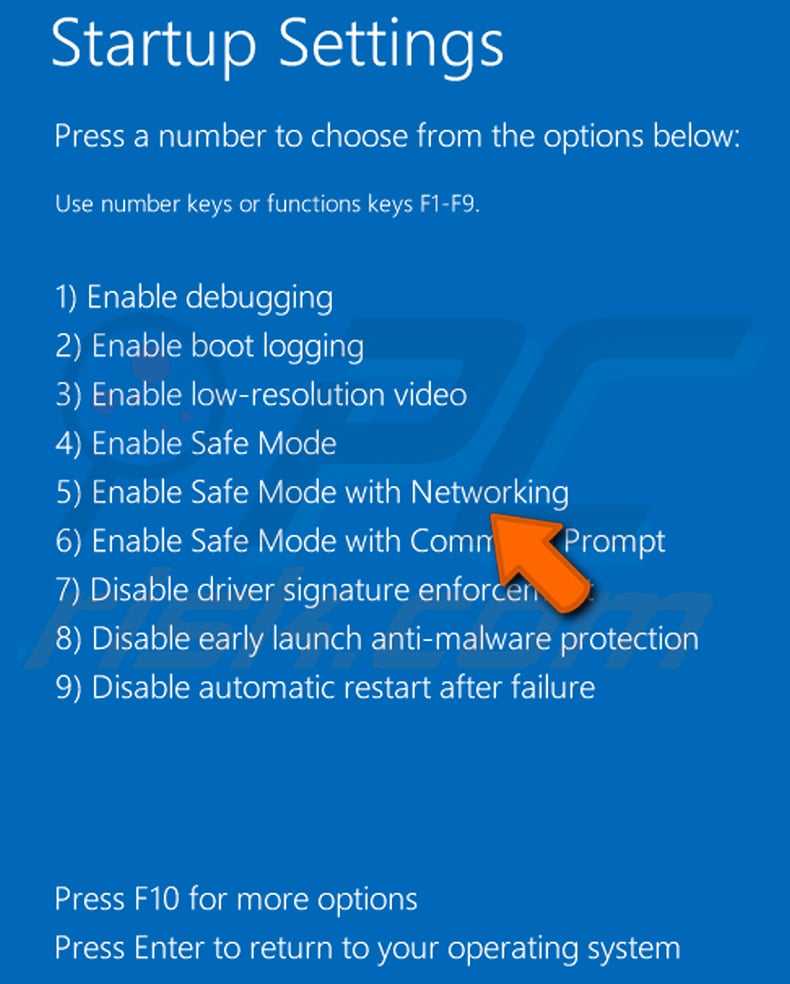
Video showing how to start Windows 8 in "Safe Mode with Networking":
Windows 10 users: Click the Windows logo and select the Power icon. In the opened menu click "Restart" while holding "Shift" button on your keyboard. In the "choose an option" window click on the "Troubleshoot", next select "Advanced options".
In the advanced options menu select "Startup Settings" and click on the "Restart" button. In the following window you should click the "F5" button on your keyboard. This will restart your operating system in safe mode with networking.
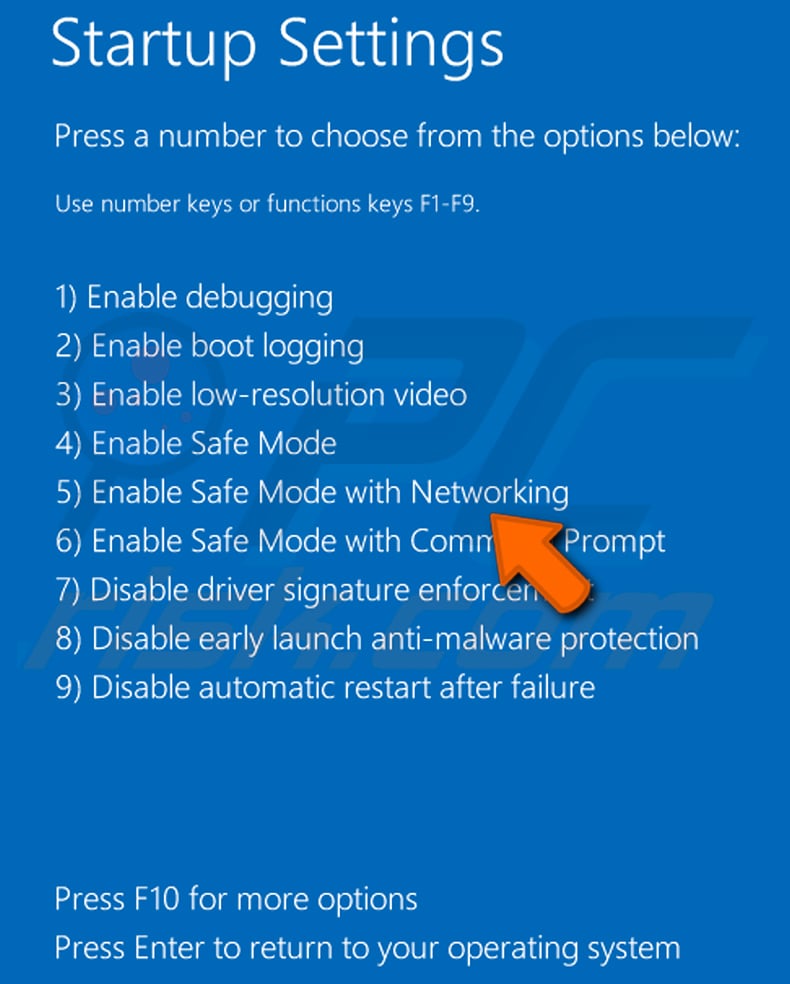
Video showing how to start Windows 10 in "Safe Mode with Networking":
 Extract the downloaded archive and run the Autoruns.exe file.
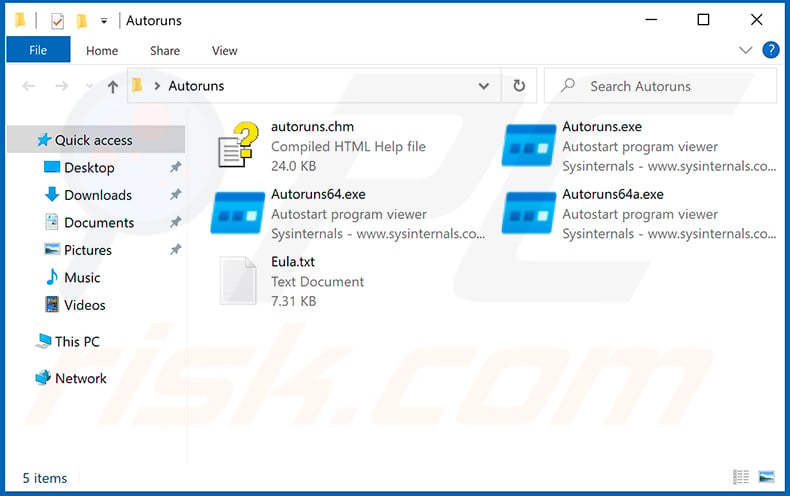
 In the Autoruns application, click "Options" at the top and uncheck "Hide Empty Locations" and "Hide Windows Entries" options. After this procedure, click the "Refresh" icon.
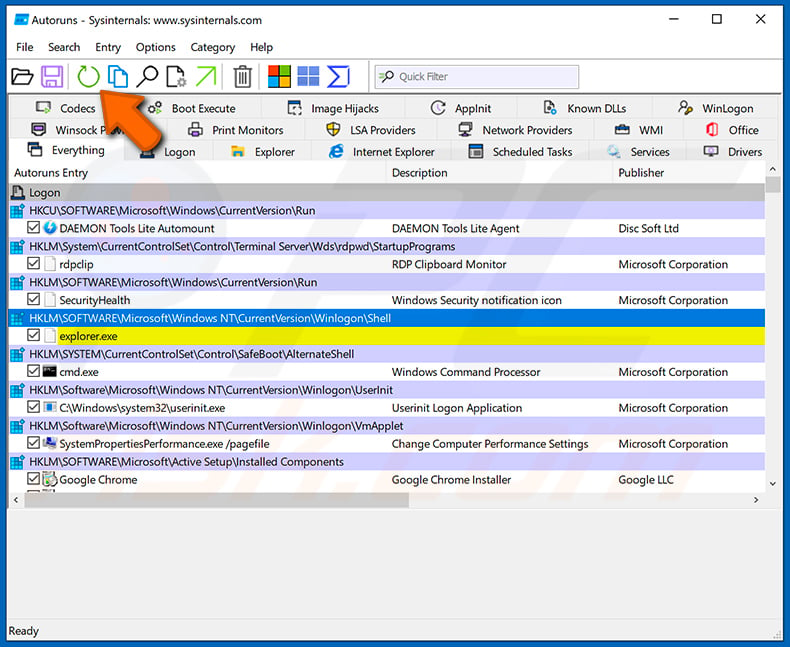
 Check the list provided by the Autoruns application and locate the malware file that you want to eliminate.
You should write down its full path and name. Note that some malware hides process names under legitimate Windows process names. At this stage, it is very important to avoid removing system files. After you locate the suspicious program you wish to remove, right click your mouse over its name and choose "Delete".
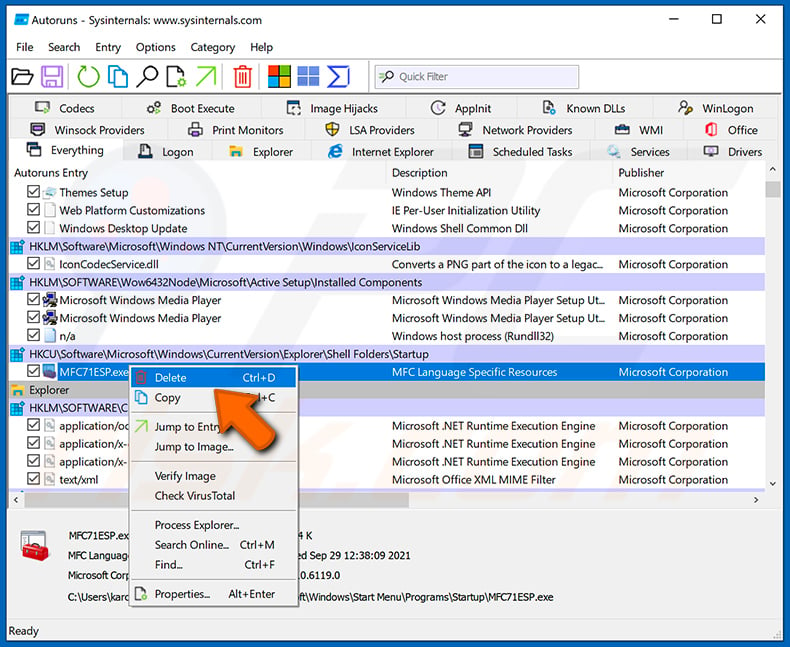
After removing the malware through the Autoruns application (this ensures that the malware will not run automatically on the next system startup), you should search for the malware name on your computer. Be sure to enable hidden files and folders before proceeding. If you find the filename of the malware, be sure to remove it.
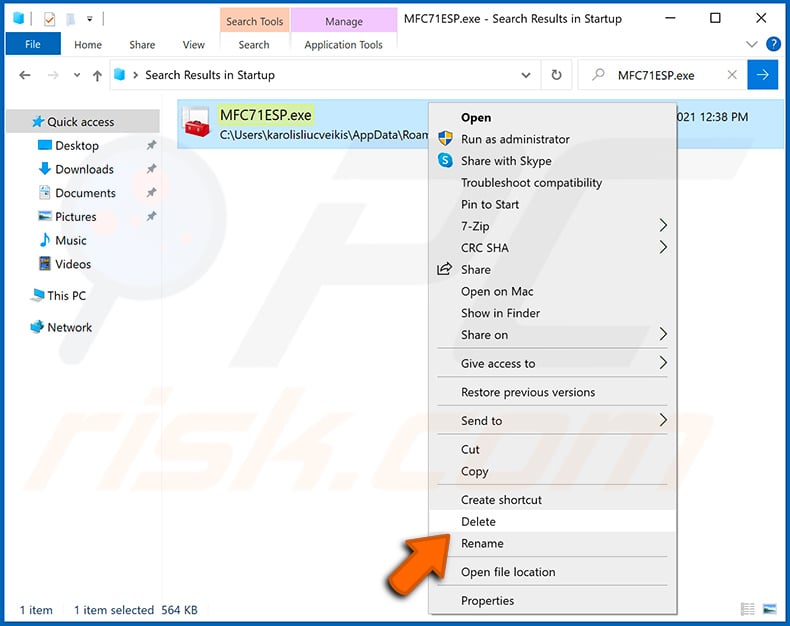
Reboot your computer in normal mode. Following these steps should remove any malware from your computer. Note that manual threat removal requires advanced computer skills. If you do not have these skills, leave malware removal to antivirus and anti-malware programs.
These steps might not work with advanced malware infections. As always it is best to prevent infection than try to remove malware later. To keep your computer safe, install the latest operating system updates and use antivirus software. To be sure your computer is free of malware infections, we recommend scanning it with Combo Cleaner Antivirus for Windows.
Frequently Asked Questions (FAQ)
My computer is infected with ChainScript RAT malware, should I format my storage device to get rid of it?
Formatting the drive would remove ChainScript, but it would also erase all of your files. Try a reputable security tool such as Combo Cleaner first and keep reformatting as a last resort.
What are the biggest issues that ChainScript RAT malware can cause?
ChainScript lets attackers run commands, steal or delete files, spy on the screen, find cryptocurrency wallets, and install more malware. This can lead to stolen funds, account takeover, identity theft, and further infections such as stealers or ransomware.
What is the purpose of ChainScript RAT malware?
The purpose of ChainScript is to give attackers hidden remote control over infected Windows computers so they can steal data, look for cryptocurrency wallets, and deploy additional payloads whenever they want.
How did ChainScript RAT malware infiltrate my computer?
ChainScript has been spread through ClickFix lures that trick users into running a command via the Run dialog, and through fake installers disguised as Spotify, Zoom Workplace, and Microsoft Teams. Threats of this kind also spread via phishing emails, fake download sites, pirated software, and malicious ads.
Will Combo Cleaner protect me from malware?
Yes. Combo Cleaner can detect and remove most known malware, including RATs. Since advanced threats can hide deep in the system, running a full system scan is recommended to make sure nothing is left behind.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion