

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What is XiaoBa?
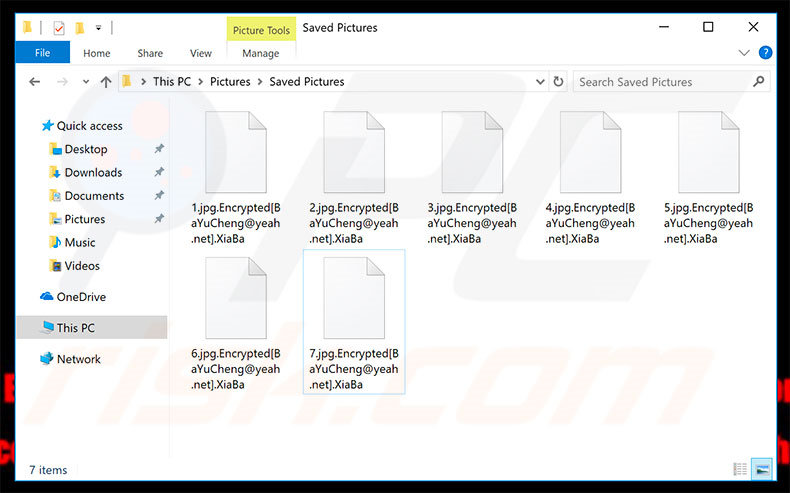
First discovered by MalwareHunterTeam, XiaoBa is a ransomware-type virus that stealthily infiltrates systems and encrypts stored files. During encryption, XiaoBa appends filenames with the ".Encrypted[BaYuCheng@yeah.net].XiaBa" extension (e.g., "sample.jpg" is renamed to "sample.jpg.Encrypted[BaYuCheng@yeah.net].XiaBa").
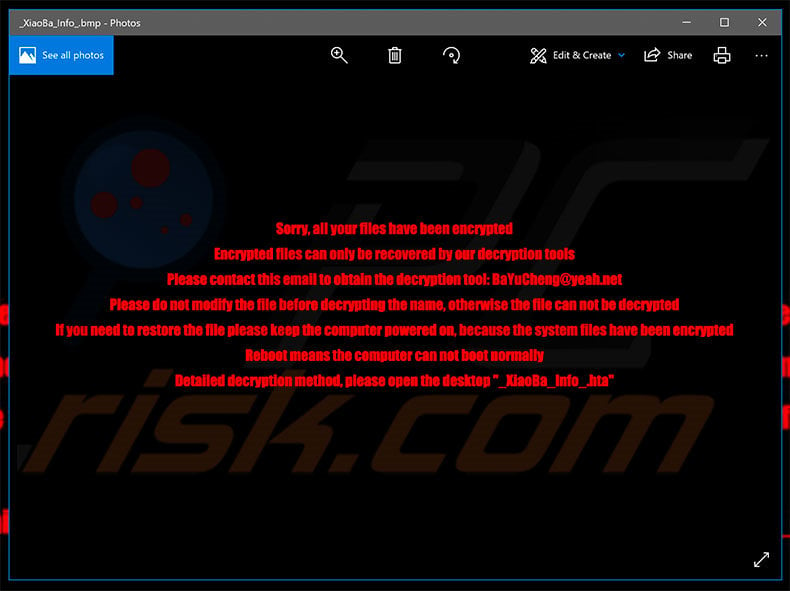
Following successful encryption, XiaoBa creates two files ("_XiaoBa_Info_.hta" and "_XiaoBa_Info_.bmp"), placing them on the desktop. It also opens the .hta file and sets the .bmp file as the desktop wallpaper. Other variants of this ransomware use ".[BaYuCheng@yeah.net].china" and .[xiaoba_666@163.com]Encrypted_(victim ID).XIAOBA extensions for encrypted files.
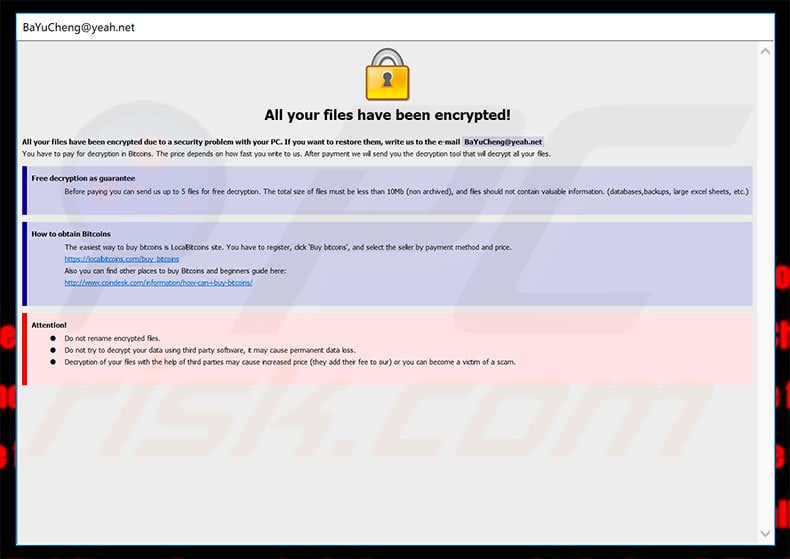
The opened .hta file displays a pop-up window with a ransom-demand message. The .bmp file also contains a similar, yet shorter message. The entire window and text is very similar to that of GlobeImposter and its newer variants. The message states that files are encrypted and that the victim must pay a ransom to decrypt them.
It is currently unknown which type of cryptography (symmetric or asymmetric) XiaoBa uses - this information is not provided, however, it is safe to assume that decryption requires unique keys generated for each victim. These keys are stored on a remote server controlled by XiaoBa's developers.
Users are encouraged to pay a ransom by contacting developers via an email address provided. The cost depends on how quickly victims make contact. In most cases, cyber criminals demand $500-$1500 in Bitcoins or another cryptocurrency.
Victims are also permitted to attach up to five selected files (up to 10 Mb in total), which are then decrypted and returned to the victim free of charge. This, supposedly to 'guarantee' that decryption is possible. Despite this, cyber criminals should never be trusted. Research shows that these people often ignore victims, once payments are submitted.
Therefore, you are strongly advised to ignore all requests to contact these people or pay any ransoms. In most cases, paying gives no positive result and you will be scammed. Unfortunately, there are currently no tools capable of restoring files encrypted by XiaoBa. Therefore, the only solution is to restore everything from a backup.
Screenshot of a message encouraging users to pay a ransom to decrypt their compromised data:
XiaoBa is virtually identical to GANDCRAB, SUSPENDED, DataKeeper, Saturn, and dozens of other ransomware-type viruses. Although these viruses are developed by different cyber criminals, all have identical behavior - they encrypt data and make ransom demands. In most cases, the size of ransom and type of encryption algorithm used are the only major differences.
Research shows that, unfortunately, most of these viruses employ algorithms (e.g., RSA, AES, and so on) that generate unique decryption keys.
Therefore, unless these viruses have certain bugs/flaws (e.g., the keys are stored locally, they are hard-coded or similar), file decryption manually without involvement of developers (contacting these people is not recommended) is impossible.
Ransomware is one of the main reasons why you should keep regular data backups, however, backup files must be stored on a remote server or unplugged external storage, otherwise they will also be encrypted.
How did ransomware infect my computer?
To proliferate ransomware, developers typically use spam emails, unofficial download sources, fake software updaters, and trojans. Spam emails might contain infectious attachments (e.g., MS Office documents, JavaScript files, and so on) that, once opened, download and install malware.
Third party download sources (peer-to-peer networks, freeware download websites, free file hosting websites, etc.) present malicious executables as legitimate software, thereby tricking users into downloading and installing malware. Fake update tools infect the system by exploiting outdated softwares bugs/flaws or downloading/installing viruses rather than software updates.
Trojans are the simplest - they merely open "backdoors" for other viruses to infiltrate the system. Ultimately, the main reasons for computer infections are poor knowledge and careless behavior.
| Name | XiaoBa virus |
| Threat Type | Ransomware, Crypto Virus, Files locker |
| Encrypted Files Extension | .XiaoBa, .XIAOBA, .china, .XiaBa |
| Ransom Demanding Message | _XiaoBa_Decryption_Method_.txt, _XiaoBa_Decryption_Method_.bmp, _XiaoBa_Info_.hta, _XiaoBa_Info_.bmp |
| Cyber Criminal Contact | BaYuCheng@yeah.net, xiaoba_666@163.com, B32588601@163.com |
| Detection Names | Avast (Win32:Malware-gen), BitDefender (Gen:Variant.Ransom.208), ESET-NOD32 (A Variant Of Win32/Filecoder.NOP), Kaspersky (UDS:Trojan.Win32.Generic), Microsoft (Program:Win32/Wacapew.C!ml), Full List Of Detections (VirusTotal) |
| Symptoms | Cannot open files stored on your computer, previously functional files now have a different extension (for example, my.docx.locked). A ransom demand message is displayed on your desktop. Cyber criminals demand payment of a ransom (usually in bitcoins) to unlock your files. |
| Distribution methods | Infected email attachments (macros), torrent websites, malicious ads. |
| Damage | All files are encrypted and cannot be opened without paying a ransom. Additional password-stealing trojans and malware infections can be installed together with a ransomware infection. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
How to protect yourself from ransomware infections?
Be very cautious when browsing the Internet. Never open files received from suspicious/unrecognizable email addresses. These emails should be deleted immediately, without reading. It is also important to download/install your applications from official sources only, using direct download links.
Bear in mind that criminals proliferate rogue apps via third party download/installation set-ups, and thus, these tools should never be used.
Keep installed applications updated and use a legitimate anti-virus/anti-spyware suite, however, since criminals proliferate ransomware using fake update tools, you are advised to use implemented updated features or tools provided by the official developer only. The key to computer safety is caution.
Text presented in XiaoBi ransomware pop-up ("_XiaoBa_Info_.hta"):
All your files have been encrypted!
All your files have been encrypted due to a security problem with your PC. If you want to restore them, write us to the e-mail BaYuCheng@yeah.net
You have to pay for decryption in Bitcoins. The price depends on how fast you write to us. After payment we will send you the decryption tool that will decrypt all your files.
Free decryption as guarantee
Before paying you can send us up to 5 files for free decryption. The total size of files must be less than 10Mb (non archived), and files should not contain valuable information. (databases,backups, large excel sheets, etc.)
How to obtain Bitcoins
The easiest way to buy bitcoins is LocalBitcoins site. You have to register, click 'Buy bitcoins', and select the seller by payment method and price.
hxxps://localbitcoins.com/buy_bitcoins
Also you can find other places to buy Bitcoins and beginners guide here:
hxxp://www.coindesk.com/information/how-can-i-buy-bitcoins/
Attention!
Do not rename encrypted files.
Do not try to decrypt your data using third party software, it may cause permanent data loss.
Decryption of your files with the help of third parties may cause increased price (they add their fee to our) or you can become a victim of a scam.
Screenshot of XiaoBa desktop wallpaper:
Screenshot of files encrypted by XiaoBa (".Encrypted[BaYuCheng@yeah.net].XiaBa" extension):
Screenshots of a desktop wallpaper set by another variant of XiaoBa ransomware:
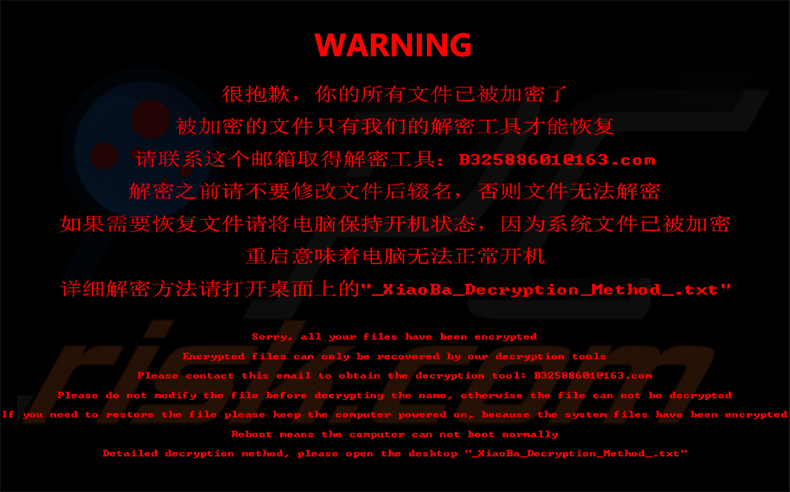
Appearance of a text file dropped by another variant of XiaoBa ransomware (GIF):
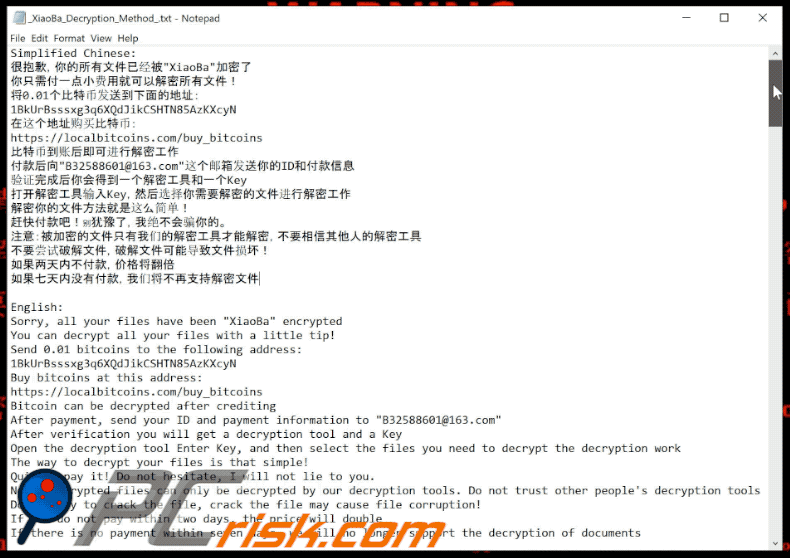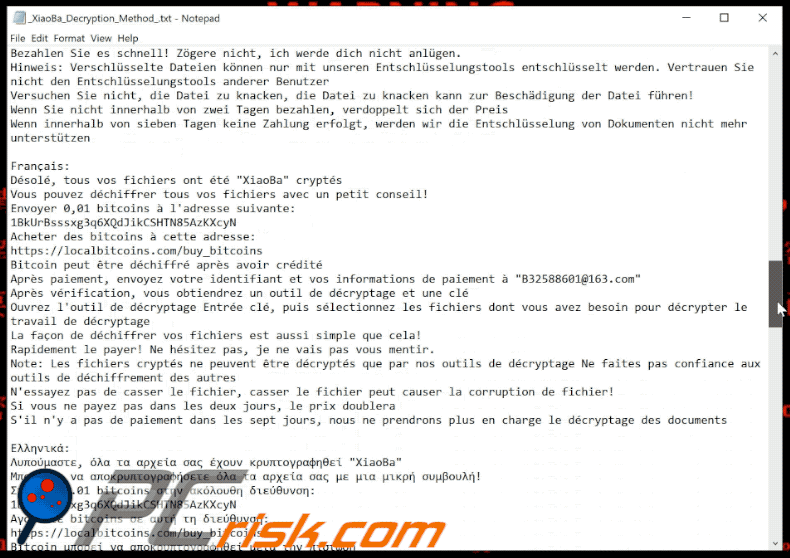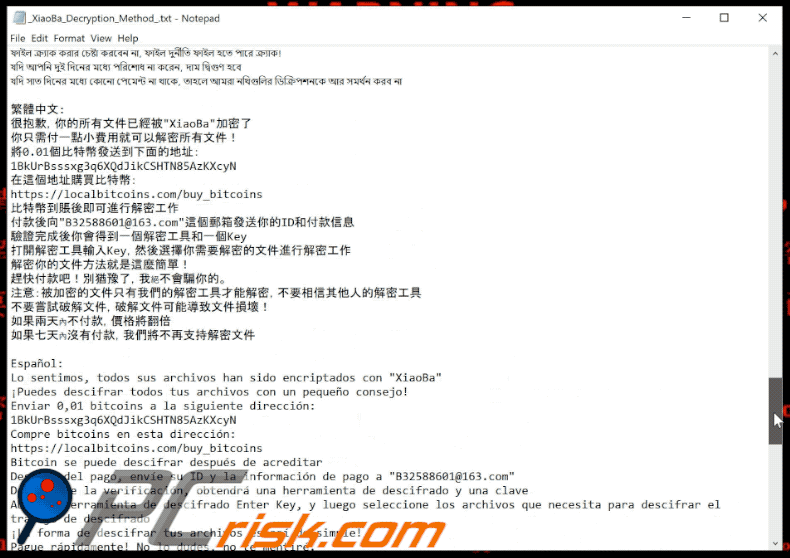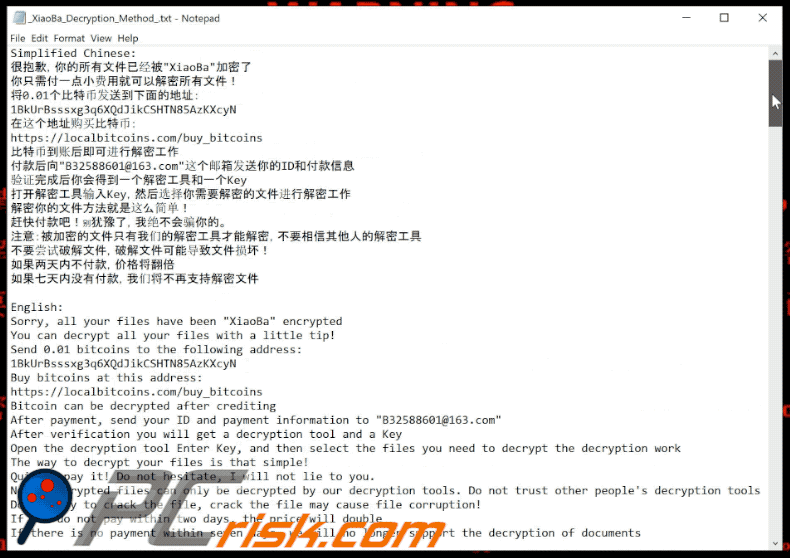
Text presented within the wallpaper and text file:
Simplified Chinese:
很抱歉,你的所有文件已经被"XiaoBa"加密了
你只需付一点小费用就可以解密所有文件!
将0.01个比特币发送到下面的地址:
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
在这个地址购买比特币:
hxxps://localbitcoins.com/buy_bitcoins
比特币到账后即可进行解密工作
付款后向"B32588601@163.com"这个邮箱发送你的ID和付款信息
验证完成后你会得到一个解密工具和一个Key
打开解密工具输入Key,然后选择你需要解密的文件进行解密工作
解密你的文件方法就是这么简单!
赶快付款吧!别犹豫了,我绝不会骗你的。
注意:被加密的文件只有我们的解密工具才能解密,不要相信其他人的解密工具
不要尝试破解文件,破解文件可能导致文件损坏!
如果两天内不付款,价格将翻倍
如果七天内没有付款,我们将不再支持解密文件
English:
Sorry, all your files have been "XiaoBa" encrypted
You can decrypt all your files with a little tip!
Send 0.01 bitcoins to the following address:
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
Buy bitcoins at this address:
hxxps://localbitcoins.com/buy_bitcoins
Bitcoin can be decrypted after crediting
After payment, send your ID and payment information to "B32588601@163.com"
After verification you will get a decryption tool and a Key
Open the decryption tool Enter Key, and then select the files you need to decrypt the decryption work
The way to decrypt your files is that simple!
Quickly pay it! Do not hesitate, I will not lie to you.
Note: Encrypted files can only be decrypted by our decryption tools. Do not trust other people's decryption tools
Do not try to crack the file, crack the file may cause file corruption!
If you do not pay within two days, the price will double
If there is no payment within seven days, we will no longer support the decryption of documents
Japanese:
申し訳ありませんが、あなたのすべてのファイルは "XiaoBa"暗号化されています
ちょっとしたヒントですべてのファイルを解読できます!
次のアドレスに0.01 bitcoinsを送信します。
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
このアドレスでビットコインを購入する:
hxxps://localbitcoins.com/buy_bitcoins
Bitcoinはクレジット処理後に復号化できます
お支払い後、IDとお支払い情報を「B32588601@163.com」にお送りください
確認の後、解読ツールとキーを取得します
復号化ツールEnterキーを開き、復号化作業の復号化に必要なファイルを選択します
あなたのファイルを解読する方法は簡単です!
すぐにそれを支払う! 私はあなたに嘘をつきません。
注:暗号化されたファイルは、私たちの解読ツールでのみ解読できます。他人の解読ツールを信用しないでください
ファイルを解読しようとしないで、ファイルを解読してファイルの破損を引き起こす可能性があります!
2日以内に支払いをしないと、価格は2倍になります
7日以内に支払いがない場合、私たちはもはや文書の解読をサポートしません
русский:
Извините, все ваши файлы были «XiaoBa» зашифрованы
Вы можете расшифровать все свои файлы с помощью небольшого наконечника!
Отправьте 0.01 биткойны по следующему адресу:
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
Купите биткойны по этому адресу:
hxxps://localbitcoins.com/buy_bitcoins
Биткойн можно расшифровать после кредитования
После оплаты отправьте свой идентификатор и платежную информацию на "B32588601@163.com"
После проверки вы получите инструмент дешифрования и ключ
Откройте инструмент дешифрования Enter Key, а затем выберите файлы, необходимые для расшифровки работы дешифрования
Способ дешифрования файлов - это просто!
Быстро заплатите! Не стесняйтесь, я не буду врать вам.
Примечание. Зашифрованные файлы могут быть дешифрованы только нашими инструментами дешифрования. Не доверяйте инструментам дешифрования других людей
Не пытайтесь взломать файл, взломать файл может привести к повреждению файла!
Если вы не заплатите в течение двух дней, цена удвоится
Если в течение семи дней нет оплаты, мы больше не будем поддерживать расшифровку документов
한국어:
죄송합니다. 모든 파일은 "XiaoBa"암호화되어 있습니다.
당신은 작은 팁으로 모든 파일을 해독 할 수 있습니다!
0.01 비트 코인을 다음 주소로 보냅니다.
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
이 주소에서 비트 코를 구입하십시오.
hxxps://localbitcoins.com/buy_bitcoins
Bitcoin은 신용 한 후에 해독 할 수 있습니다.
지불 후 ID와 지불 정보를 "B32588601@163.com"으로 보내십시오.
확인 후 암호 해독 도구와 키를 받게됩니다.
암호 해독 도구 Enter 키를 누른 다음 암호 해독 작업의 암호 해독에 필요한 파일을 선택하십시오
파일을 해독하는 방법은 간단합니다!
빨리 지불하십시오! 망설이지 마라, 나는 너에게 거짓말하지 않을 것이다.
참고 : 암호화 된 파일은 당사의 암호 해독 도구로만 해독 할 수 있습니다. 다른 사람의 암호 해독 도구를 신뢰하지 마십시오.
파일을 해독하려고하지 마십시오, 파일을 부수는 파일 손상을 일으킬 수 있습니다!
2 일 이내에 지불하지 않으면 가격이 두 배가됩니다.
7 일 이내에 지불이 없으면 더 이상 문서 해독을 지원하지 않습니다.
Deutsch:
Entschuldigung, alle Ihre Dateien wurden "XiaoBa" verschlüsselt
Sie können alle Ihre Dateien mit einem kleinen Tipp entschlüsseln!
Senden Sie 0,01 Bitcoins an die folgende Adresse:
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
Kaufen Sie Bitcoins unter dieser Adresse:
hxxps://localbitcoins.com/buy_bitcoins
Bitcoin kann nach der Gutschrift entschlüsselt werden
Nach der Zahlung senden Sie Ihre ID und Zahlungsinformationen an "B32588601@163.com"
Nach der Überprüfung erhalten Sie ein Entschlüsselungstool und einen Schlüssel
Öffnen Sie das Entschlüsselungswerkzeug Enter Key und wählen Sie dann die Dateien aus, die Sie zum Entschlüsseln der Entschlüsselungsarbeiten benötigen
Die Art, Ihre Dateien zu entschlüsseln, ist so einfach!
Bezahlen Sie es schnell! Zögere nicht, ich werde dich nicht anlügen.
Hinweis: Verschlüsselte Dateien können nur mit unseren Entschlüsselungstools entschlüsselt werden. Vertrauen Sie nicht den Entschlüsselungstools anderer Benutzer
Versuchen Sie nicht, die Datei zu knacken, die Datei zu knacken kann zur Beschädigung der Datei führen!
Wenn Sie nicht innerhalb von zwei Tagen bezahlen, verdoppelt sich der Preis
Wenn innerhalb von sieben Tagen keine Zahlung erfolgt, werden wir die Entschlüsselung von Dokumenten nicht mehr unterstützen
Français:
Désolé, tous vos fichiers ont été "XiaoBa" cryptés
Vous pouvez déchiffrer tous vos fichiers avec un petit conseil!
Envoyer 0,01 bitcoins à l'adresse suivante:
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
Acheter des bitcoins à cette adresse:
hxxps://localbitcoins.com/buy_bitcoins
Bitcoin peut être déchiffré après avoir crédité
Après paiement, envoyez votre identifiant et vos informations de paiement à "B32588601@163.com"
Après vérification, vous obtiendrez un outil de décryptage et une clé
Ouvrez l'outil de décryptage Entrée clé, puis sélectionnez les fichiers dont vous avez besoin pour décrypter le travail de décryptage
La façon de déchiffrer vos fichiers est aussi simple que cela!
Rapidement le payer! Ne hésitez pas, je ne vais pas vous mentir.
Note: Les fichiers cryptés ne peuvent être décryptés que par nos outils de décryptage Ne faites pas confiance aux outils de déchiffrement des autres
N'essayez pas de casser le fichier, casser le fichier peut causer la corruption de fichier!
Si vous ne payez pas dans les deux jours, le prix doublera
S'il n'y a pas de paiement dans les sept jours, nous ne prendrons plus en charge le décryptage des documents
Ελληνικά:
Λυπούμαστε, όλα τα αρχεία σας έχουν κρυπτογραφηθεί "XiaoBa"
Μπορείτε να αποκρυπτογραφήσετε όλα τα αρχεία σας με μια μικρή συμβουλή!
Στείλτε 0.01 bitcoins στην ακόλουθη διεύθυνση:
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
Αγοράστε bitcoins σε αυτή τη διεύθυνση:
hxxps://localbitcoins.com/buy_bitcoins
Bitcoin μπορεί να αποκρυπτογραφηθεί μετά την πίστωση
Μετά την πληρωμή, στείλτε τα στοιχεία ταυτότητας και πληρωμής σας στο "B32588601@163.com"
Μετά την επαλήθευση θα έχετε ένα εργαλείο αποκρυπτογράφησης και ένα κλειδί
Ανοίξτε το εργαλείο αποκρυπτογράφησης Enter Key και, στη συνέχεια, επιλέξτε τα αρχεία που χρειάζεστε για να αποκρυπτογραφήσετε το έργο αποκρυπτογράφησης
Ο τρόπος για να αποκρυπτογραφήσετε τα αρχεία σας είναι τόσο απλό!
Πληρώστε γρήγορα! Μη διστάσετε, δεν θα σας ψέψω.
Σημείωση: Τα κρυπτογραφημένα αρχεία μπορούν να αποκρυπτογραφηθούν μόνο από τα εργαλεία αποκρυπτογράφησης. Μην εμπιστεύεστε τα εργαλεία αποκρυπτογράφησης άλλων ανθρώπων
Μην προσπαθήσετε να σπάσετε το αρχείο, ρωγμή το αρχείο μπορεί να προκαλέσει διαφθορά αρχείο!
Αν δεν πληρώσετε εντός δύο ημερών, η τιμή θα διπλασιαστεί
Αν δεν υπάρξει πληρωμή εντός επτά ημερών, δεν θα υποστηρίζουμε πλέον την αποκρυπτογράφηση εγγράφων
বাংলা ভাষার:
দুঃখিত, আপনার সমস্ত ফাইল এনক্রিপ্ট হয়েছে "XiaoBa" হয়েছে
আপনি একটু টিপ সঙ্গে আপনার ফাইল ডিক্রিপ্ট করতে পারেন!
নিম্নোক্ত ঠিকানায় 0.01 বিটকয়েন প্রেরণ করুন:
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
এই ঠিকানায় বিটকয়েন কিনুন:
hxxps://localbitcoins.com/buy_bitcoins
ক্রেডিট করার পরে বিটকয়েনকে ডিক্রিপ্ট করা যায়
অর্থ প্রদানের পরে, আপনার আইডি এবং পেমেন্ট তথ্য "B32588601@163.com" তে পাঠান
যাচাই করার পর আপনি একটি ডিক্রিপশন টুল এবং একটি কী পাবেন
ডিক্রিপশন টুলটি খুলুন কি কী প্রবেশ করান, এবং তারপরে ডিক্রিপশন কাজটি ডিক্রিপ্ট করতে আপনার প্রয়োজনীয় ফাইলগুলি নির্বাচন করুন
আপনার ফাইল decrypt উপায় যে সহজ!
দ্রুত তা পরিশোধ! দ্বিধা করবেন না, আমি আপনার কাছে মিথ্যা বলব না।
দ্রষ্টব্য: এনক্রিপ্ট করা ফাইলগুলিকে শুধুমাত্র আমাদের ডিক্রিপশন সরঞ্জামগুলি দ্বারা ডিক্রিপ্ট করা যায়। অন্য লোকেদের ডিক্রিপশন সরঞ্জামগুলিতে বিশ্বাস করবেন না
ফাইল ক্র্যাক করার চেষ্টা করবেন না, ফাইল দুর্নীতি ফাইল হতে পারে ক্র্যাক!
যদি আপনি দুই দিনের মধ্যে পরিশোধ না করেন, দাম দ্বিগুণ হবে
যদি সাত দিনের মধ্যে কোনো পেমেন্ট না থাকে, তাহলে আমরা নথিগুলির ডিক্রিপশনকে আর সমর্থন করব না
繁體中文:
很抱歉,你的所有文件已經被"XiaoBa"加密了
你只需付一點小費用就可以解密所有文件!
將0.01個比特幣發送到下面的地址:
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
在這個地址購買比特幣:
hxxps://localbitcoins.com/buy_bitcoins
比特幣到賬後即可進行解密工作
付款後向"B32588601@163.com"這個郵箱發送你的ID和付款信息
驗證完成後你會得到一個解密工具和一個Key
打開解密工具輸入Key,然後選擇你需要解密的文件進行解密工作
解密你的文件方法就是這麼簡單!
趕快付款吧!別猶豫了,我絕不會騙你的。
注意:被加密的文件只有我們的解密工具才能解密,不要相信其他人的解密工具
不要嘗試破解文件,破解文件可能導致文件損壞!
如果兩天內不付款,價格將翻倍
如果七天內沒有付款,我們將不再支持解密文件
Español:
Lo sentimos, todos sus archivos han sido encriptados con "XiaoBa"
¡Puedes descifrar todos tus archivos con un pequeño consejo!
Enviar 0,01 bitcoins a la siguiente dirección:
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
Compre bitcoins en esta dirección:
hxxps://localbitcoins.com/buy_bitcoins
Bitcoin se puede descifrar después de acreditar
Después del pago, envíe su ID y la información de pago a "B32588601@163.com"
Después de la verificación, obtendrá una herramienta de descifrado y una clave
Abra la herramienta de descifrado Enter Key, y luego seleccione los archivos que necesita para descifrar el trabajo de descifrado
¡La forma de descifrar tus archivos es así de simple!
Pague rápidamente! No lo dudes, no te mentiré.
Nota: las herramientas de descifrado solo pueden descifrar los archivos cifrados. No confíe en las herramientas de descifrado de otras personas.
¡No intente descifrar el archivo, crackear el archivo puede causar daños en el archivo!
Si no paga dentro de dos días, el precio se duplicará
Si no se realiza el pago dentro de los siete días, ya no admitiremos el descifrado de documentos.
Portugues:
Desculpe, todos os seus arquivos foram "XiaoBa" criptografados
Você pode descriptografar todos os seus arquivos com uma pequena dica!
Envie 0.01 bitcoins para o seguinte endereço:
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
Compre bitcoins neste endereço:
hxxps://localbitcoins.com/buy_bitcoins
Bitcoin pode ser descriptografado após o crédito
Após o pagamento, envie suas informações de identificação e pagamento para "B32588601@163.com"
Após a verificação, você obterá uma ferramenta de descriptografia e uma Chave
Abra a ferramenta de descriptografia Enter Key e selecione os arquivos que você precisa para descriptografar o trabalho de descriptografia
A maneira de descriptografar seus arquivos é tão simples!
Rapidamente pague! Não hesite, não vou mentir para você.
Nota: Os arquivos criptografados só podem ser descriptografados por nossas ferramentas de descriptografia. Não confie nas ferramentas de descriptografia de outras pessoas
Não tente quebrar o arquivo, quebrar o arquivo pode causar corrupção de arquivos!
Se você não paga no prazo de dois dias, o preço irá dobrar
Se não houver pagamento dentro de sete dias, não iremos suportar o decodificação de documentos
Монгол хэл:
Уучлаарай, бүх файлууд нь "XiaoBa" шифрлэгдсэн байна
Та бүх файлаа бага зэрэг оройгоор буцааж шифрлэх боломжтой!
0.01 bitcoins-ыг дараах хаягаар илгээх:
1BkUrBsssxg3q6XQdJikCSHTN85AzKXcyN
Энэ хаягаар bitcoins худалдаж авах:
hxxps://localbitcoins.com/buy_bitcoins
Bitcoin кредит хийсний дараа буцааж шифрлэх боломжтой
Төлбөр хийгдсэний дараа таны ID болон төлбөрийн мэдээллийг "B32588601@163.com"
Баталгаажсаны дараа та шифрлэх хэрэгсэл болон түлхүүр авах болно
Шифрлэх хэрэгслийг Түлхүүрийг оруулаад, дараа нь шифрлэхийг буцааж шифрлэхэд шаардлагатай файлуудыг сонго
Файлуудыг буцааж шифрлэх арга нь ийм хялбар юм!
Хурдан төлөх! Бүү эргэлзээрэй, би чамайг худал хэлэхгүй.
Тэмдэглэл: Шифрлэгдсэн файлыг зөвхөн манай шифрлэх хэрэгслийг буцааж шифрлэх боломжтой. Бусад хүмүүсийн шифрлэх хэрэгслийг ашиглахгүй байх
Файлыг эвдэх гэж бүү оролдоорой, файлыг файлын эвдрэлд хүргэж болзошгүй!
Хэрэв та хоёр хоногийн дотор төлөхгүй бол үнэ хоёр дахин нэмэгдэх болно
Хэрэв 7 хоногийн дотор төлбөр төлөөгүй бол бид баримт бичгийн шифрийг цаашид дэмжихгүй болно
Screenshot of files encrypted by this XiaoBa ransomware variant:
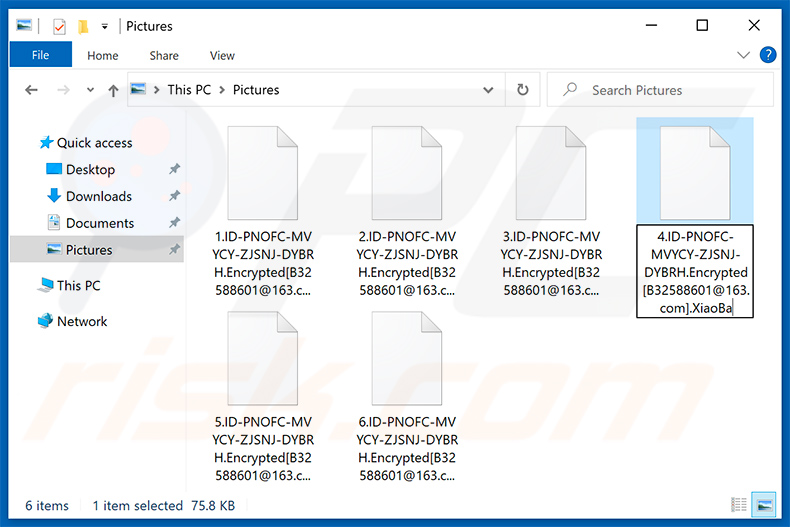
XiaoBa ransomware removal:
Instant automatic malware removal:
Manual threat removal might be a lengthy and complicated process that requires advanced IT skills. Combo Cleaner is a professional automatic malware removal tool that is recommended to get rid of malware. Download it by clicking the button below:
DOWNLOAD Combo CleanerBy downloading any software listed on this website you agree to our Privacy Policy and Terms of Use. To use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
Removal and file recovery procedure
If your files are encrypted with a new extension and a ransom note has appeared, you've been hit by ransomware. Don't pay. The procedure below works in order: contain the infection, identify the variant, remove the ransomware itself (so anything you restore doesn't get re-encrypted), and try to recover files using free decryption tools, Windows Volume Shadow Copies, or backups. Run a full system scan with Combo Cleaner to remove the infection - then move on to file recovery.
Common ransomware behaviors
VisibleEncrypts your files and renames them
The ransomware reads each file, encrypts the contents with the attacker's public key, and writes the encrypted bytes back to disk. Most variants also rename the file by appending a new extension - .net, .locked, .crypt, .lockbit, .djvu, etc. Without the matching private key, the encrypted files cannot be opened normally. Recovery depends on a free decryption tool, a recoverable Volume Shadow Copy, or a clean backup.
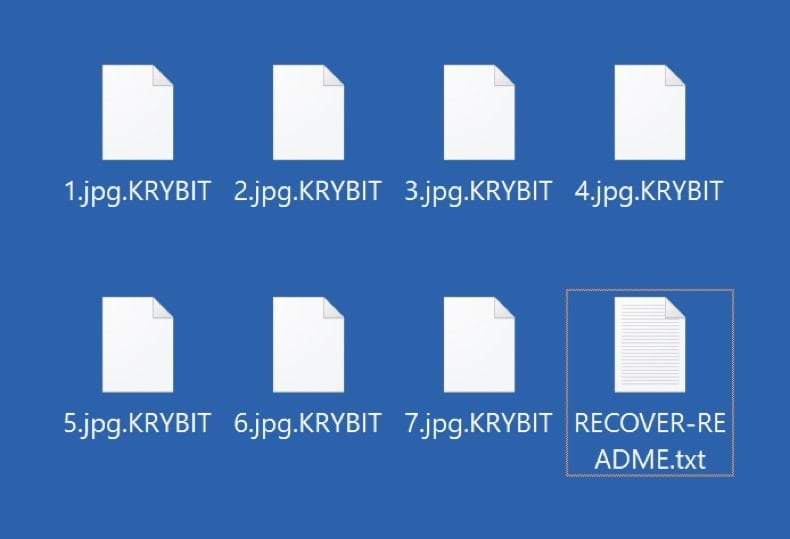
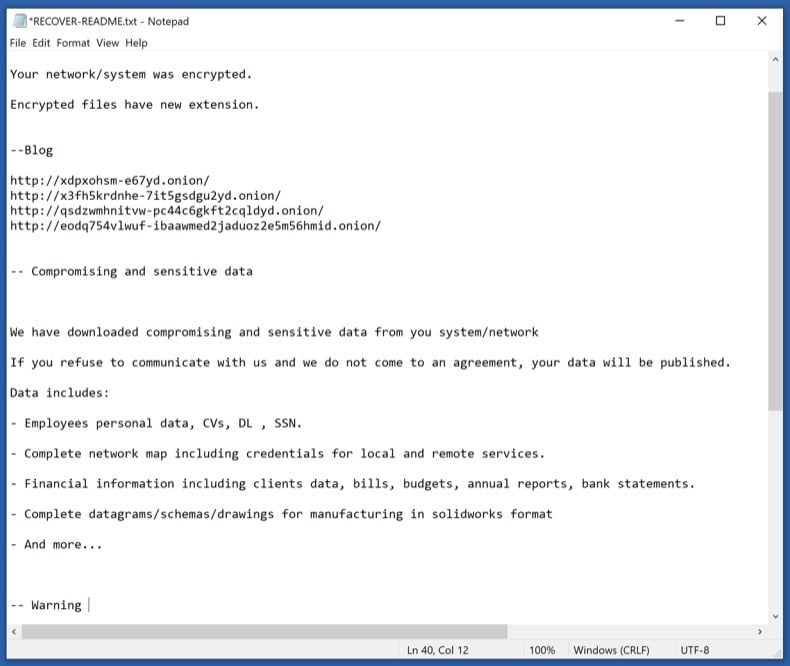
VisibleDrops a ransom note in every encrypted folder
A text or HTML file (usually named HOW_TO_DECRYPT.txt, README.txt, _readme.txt, or similar) is placed in every folder that contains encrypted files. The note explains the situation, lists a payment amount in cryptocurrency, gives a deadline, and provides a contact email or .onion site. Save the note - don't delete it. Its exact wording, the email address, and the bitcoin wallet are how you identify the variant in the next phase.
VisibleReplaces the desktop wallpaper
Many ransomware variants change the Windows wallpaper to a black or red image with the ransom message and instructions. The wallpaper is just a visual scare tactic - it doesn't add any actual capability and reverts to normal once the ransomware is removed. Photograph it before removal in case the contact details are useful for variant identification or for reporting to authorities.
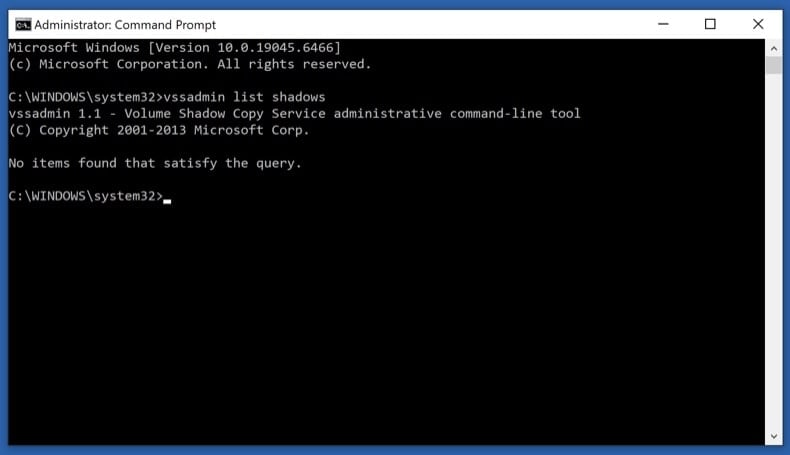
HiddenDeletes Volume Shadow Copies
One of the first things modern ransomware does after launching is run vssadmin delete shadows /all /quiet to wipe Windows' built-in Volume Shadow Copies - the snapshots that Previous Versions and System Restore rely on. Some ransomware doesn't fully succeed (especially on systems where the user lacks full admin rights), leaving partial shadow copies recoverable. Phase 4 step 11 covers how to check what survived.
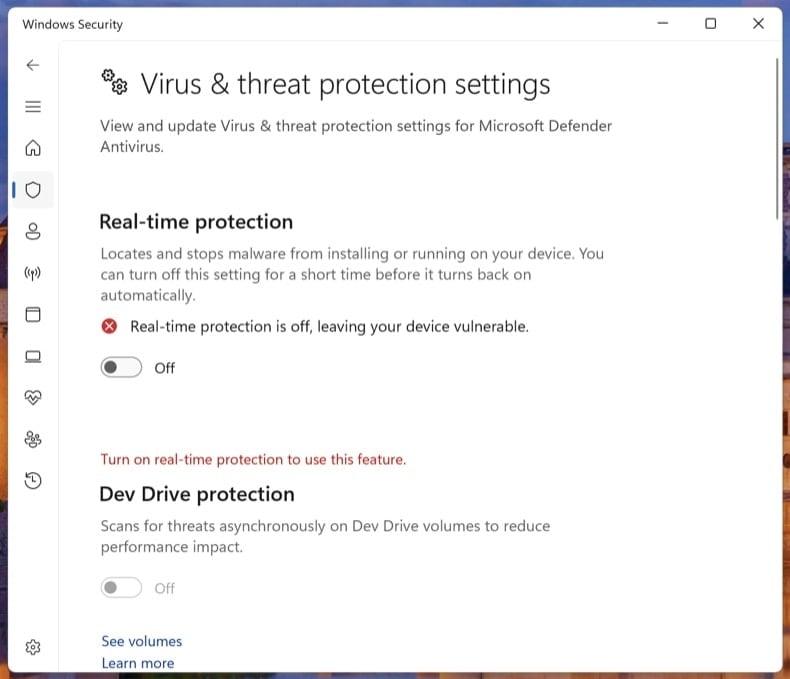
HiddenDisables Windows Defender and other security tools
Before encrypting, the ransomware tries to silence anything that could alert you or block it - Windows Defender real-time protection, third-party antivirus services, backup agents (Veeam, Acronis), and sometimes the Windows Event Log service. It often modifies Group Policy or registry keys to keep these off after reboot. Phase 3 step 9 explicitly turns Tamper Protection back on so the next ransomware attempt can't repeat the trick.
HiddenSpreads laterally to other PCs on the network
Network-aware ransomware (LockBit, Conti, BlackCat, Akira families) doesn't stop at the first machine. It scans for SMB shares, mapped drives, and other PCs on the same network, then encrypts whatever it can reach. On Windows domains, a single compromised user with admin rights can lead to all-domain encryption. This is why Phase 1 step 2 disconnects the network as the very first action - it stops the spread immediately.
HiddenSteals data before encrypting (double extortion)
Modern ransomware (LockBit, BlackCat / ALPHV, Akira, Cl0p, Royal) almost always exfiltrates data before encrypting. The attacker then runs a "double extortion" play: pay the ransom for decryption, plus pay again to prevent the stolen data from being leaked on the group's leak site. Paying the first ransom does not get the leaked data back - assume that anything the ransomware could read was uploaded. This is one more reason not to pay: the data is already out.
Don't pay the ransom
Paying the ransom does not guarantee you'll get your files back. Major ransomware response studies consistently show that a meaningful percentage of paying victims either receive a non-working decryptor, only partial decryption, or no decryptor at all. Beyond that:
- Paying confirms you as a willing target - re-attack rates within 12 months are high
- Several ransomware groups have been sanctioned (US OFAC, UK OFSI). Paying these groups may be illegal under sanctions law in your country
- The ransom funds the next attack - on you or someone else
- Modern ransomware almost always exfiltrates data first, so paying doesn't get the leaked data back. Assume anything the malware could read was uploaded
- Decryptors, even when they work, often leave files corrupted because the encryption itself was buggy or rushed
The path below tries every legal, free recovery option first. Pay only as an absolute last resort, after consulting a lawyer and your country's cyber crime authority.
Disconnect from the network and log out of cloud storage
Pull the Ethernet cable and turn off Wi-Fi on the affected PC. If multiple computers share the network, do the same on every machine you suspect could be affected, including any servers and NAS units.
Then sign out of cloud storage clients (OneDrive, Dropbox, Google Drive, iCloud) from their app settings. If you can, pause the sync. Some ransomware uses the running sync client to push encrypted versions over your clean cloud copies.
Modern ransomware spreads laterally across SMB shares, mapped drives, RDP, and reachable network neighbors. Disconnecting stops the spread the moment you do it. Logging out of cloud sync clients prevents the ransomware from encrypting the cloud copies of your files via the sync API.
Unplug external drives and USB storage
Safely eject any external drives, USB sticks, SD cards, and network-attached storage shares - then unplug them. If a drive was connected when the ransomware ran, the files on it may already be encrypted, but unplugging stops further damage.
Critically: don't reconnect any drive (including your most recent backup) to this PC until the ransomware is removed in Phase 3. Reconnecting an external backup to an actively-infected PC is the most common way that backup gets encrypted too.
Save the ransom note and a sample encrypted file
Copy the ransom note and one small encrypted file (under 1 MB) to a USB stick, or photograph the note with your phone. You'll need both for the variant identification step.
The ransom note is usually one of:
- A
.txtfile in every encrypted folder (typicallyHOW_TO_DECRYPT.txt,README.txt, or_readme.txt) - An
.htmlfile with the same purpose - A changed desktop wallpaper - photograph it
- A lock-screen interrupt that runs at startup - rarer
Don't delete the note. Variant identification depends on its exact wording, the contact email, and the bitcoin wallet address. The note is also evidence if you report to authorities.
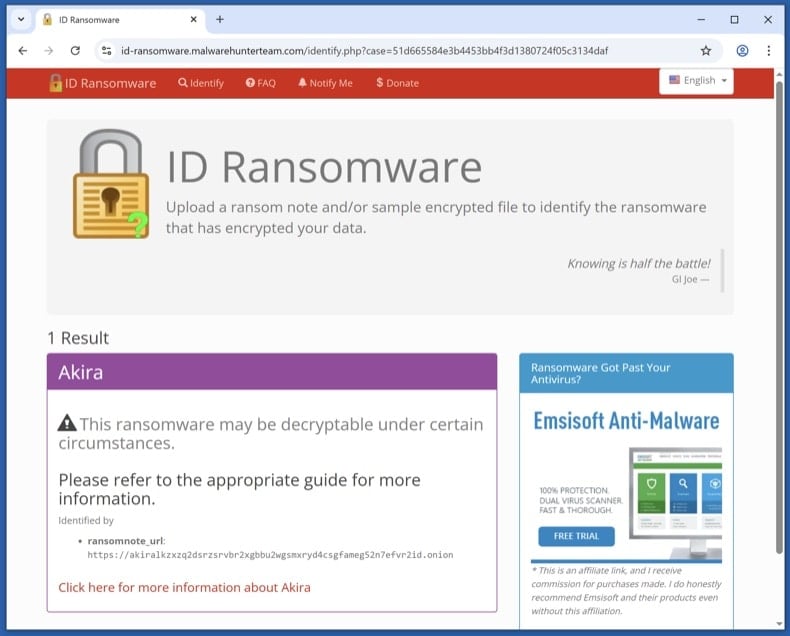
Identify the variant with ID Ransomware
From a clean device (your phone is fine, or another PC that wasn't on the affected network), visit id-ransomware.malwarehunterteam.com. Upload the ransom note and the sample encrypted file. The site identifies the variant family and tells you whether a free decryptor exists.
ID Ransomware is run by the Malware Hunter Team. Files you upload are kept private - they're used for analysis, not published. If you're concerned about uploading data anyway, you can paste the contact email and bitcoin wallet from the note - those are often enough for identification.
The ransomware itself must be removed before any file recovery. If it's still active, anything you restore in Phase 4 gets re-encrypted within minutes.
Boot to Safe Mode with Networking and download the scanners
Safe Mode loads only the minimal Windows drivers, which prevents most ransomware from auto-running while you set up the scanners.
Windows 11: open , click Restart now next to Advanced startup. After the restart, click , then press 5 or F5.
Windows 10: click the Windows logo, hold Shift, click the Power icon and choose Restart. From the Choose-an-option screen, click , then press F5.
Once Safe Mode has loaded, turn Wi-Fi back on and download Combo Cleaner (used in step 8) and Microsoft Safety Scanner (used in step 9). Save both installers to your Desktop, then disconnect Wi-Fi again before scanning.
Run Microsoft Defender Offline
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts into a stripped-down environment and scans the disk before Windows fully loads.
Some ransomware variants drop bootkit components or kernel hooks that hide from any scanner running on the same Windows session that's already infected. A pre-boot offline scan sees the disk before the malware can load itself.
VB100 certified. Includes anti-trojan, registry/persistence scanning, and anti-spyware in one pass. The 7-day free trial is available.
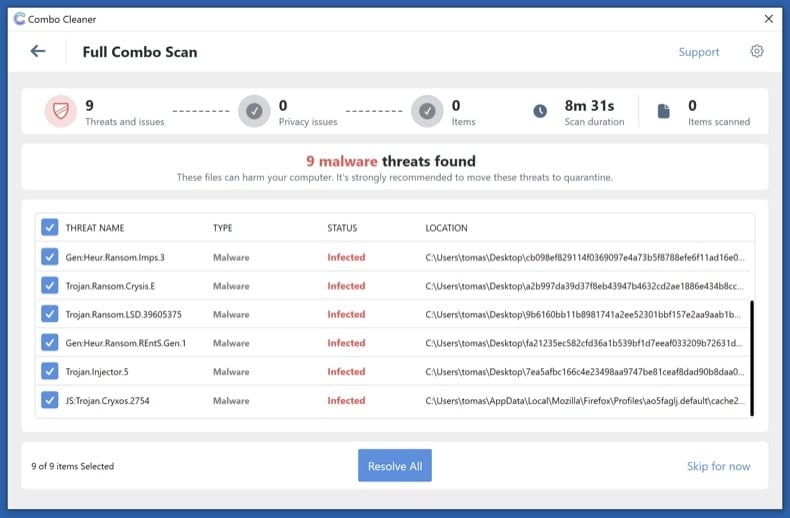
Download Combo CleanerRun a full Combo Cleaner scan
Run the installer you downloaded in step 6 and start a full system scan (not the quick scan). Let it complete, review what it detected, and apply the recommended actions. Combo Cleaner quarantines the ransomware executable and the registry / scheduled-task entries that re-launch it on reboot.
Run Microsoft Safety Scanner and re-enable Defender
Run Microsoft Safety Scanner (MSERT.exe) as a second-opinion full scan. The binary expires every 10 days so the copy you downloaded has the latest signatures.
Once it finishes, open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all on. Many ransomware variants disable Defender during the attack - this is where you switch it back on so the next attempt can't repeat the trick.
Different scanning engines catch different threats. Running an additional Microsoft scan after Combo Cleaner is the most underused verification step in malware removal - and free.
Try the steps in order. The first decryptor that works ends the recovery process - no need to do all four.
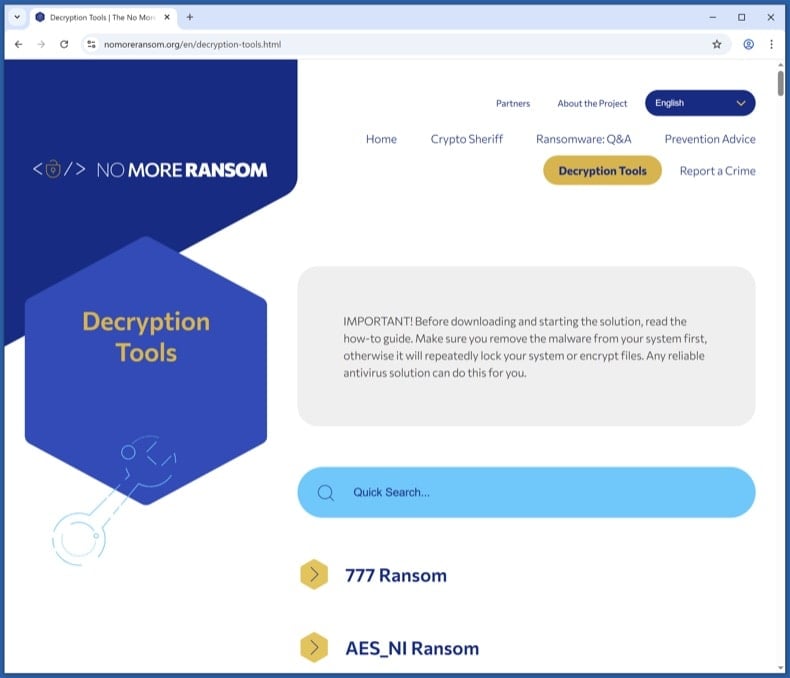
Check the No More Ransom Project for a free decryptor
Visit nomoreransom.org and search the Decryption Tools list for the variant name returned by ID Ransomware. The project is run by Europol, the Dutch Police, and security vendors - everything listed is legitimate and free.
If a decryptor exists, download it onto a clean PC, copy it across, and follow its instructions exactly. Decryptors usually want you to point them at a sample encrypted file plus its known unencrypted version (sometimes any image you previously had a backup of works).
Free decryptors exist for parts of the STOP/Djvu, GandCrab, REvil, Avaddon, Conti and Hive families, among others. Most modern variants don't have public decryptors - if yours isn't listed, that's expected; move to the next step.
Try Windows Volume Shadow Copies
Windows automatically creates Volume Shadow Copies of files when System Restore points are made or scheduled backups run. Most ransomware tries to wipe these (vssadmin delete shadows /all /quiet), but the deletion sometimes fails partially - especially if the running user doesn't have full admin rights. When it does fail, snapshots survive that contain pre-encryption versions of your files.
First, check what's there. Open Command Prompt as Administrator and run:
vssadmin list shadows
If you see entries listed, shadow copies survived. To restore from them:
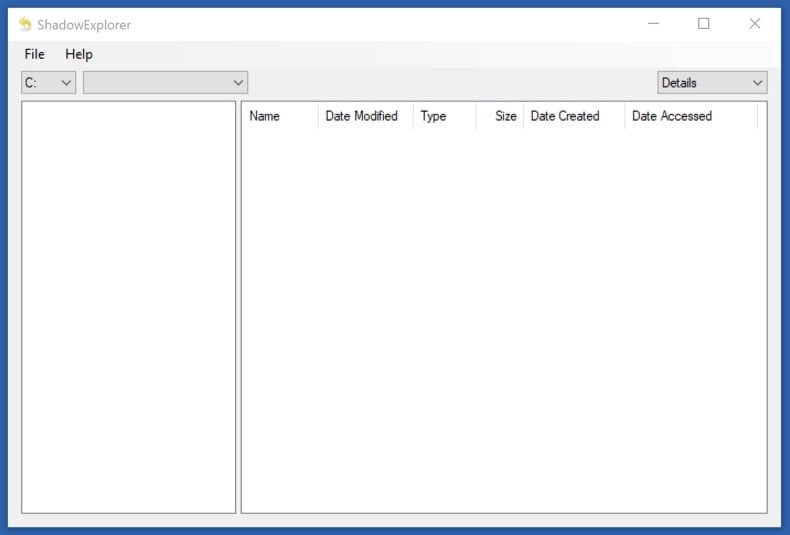
- Built-in: right-click any folder → Properties → Previous Versions tab. Pick a snapshot dated before the infection and restore.
- Better tool for browsing: install Shadow Explorer (free). It shows all snapshots as a normal file tree and lets you copy out only the files you want.
Shadow Copies recover the original files exactly, with no risk of decryption errors. If they survived, this is faster and cleaner than running a decryptor on the encrypted set.
Restore from cloud or external backup
If you have a backup that pre-dates the infection, this is the cleanest recovery available. Important precautions:
- Don't reconnect a backup drive until Phase 3 is complete. If the ransomware is still active, plugging in the backup encrypts it too.
- For cloud backups (OneDrive, Dropbox, Google Drive, iCloud), use the Version History feature to roll individual files back to pre-encryption versions.
- OneDrive specifically has a "Restore your OneDrive" feature: if it detected mass file changes, you can roll back the entire account up to 30 days. Sign in at OneDrive on the web, click the Settings gear, and choose Restore your OneDrive. Microsoft 365 subscribers also get ransomware detection alerts; non-subscribers get one free recovery.
- Verify the restored files open correctly before you delete the encrypted set. Test a few documents, photos, and any database / project files.
Try Recuva as a last-resort recovery
Recuva is a long shot, not a primary recovery tool. Most modern ransomware encrypts files in place - it reads the original, encrypts the data, and writes the encrypted bytes back to the same disk location. In that case, the original isn't deleted, just rewritten - and Recuva has nothing to find.
But for older or simpler variants that deleted originals before creating encrypted copies (rather than encrypting in place), Recuva can sometimes pull the originals from unallocated disk space. Worth trying as a last resort, especially before you use the disk much further.
If you try it:
- Stop using the disk as much as possible - every disk write reduces recovery odds
- Run Recuva from a USB stick, not from the affected disk
- Use Deep Scan mode (slower but the only mode worth running for this scenario)
Don't skip the steps above expecting Recuva to bail you out. It works in maybe 5-20% of cases, depending on the variant and how soon you try.
Report the attack to authorities
Even if your files aren't recovered, your report helps authorities track variants, attribute groups, and warn future victims. In some jurisdictions (especially the US and UK) early reporting can sometimes help recall a wired ransom payment via banking partners.
Save the report number - banks, insurers, and credit bureaus will ask for it. If you operate a business, you may also have legal disclosure obligations (GDPR in the EU, state breach laws in the US) that run on a 72-hour clock.
Plan 3-2-1 backups going forward
The single best defense against ransomware is a tested backup. Use the 3-2-1 rule:
- 3 copies of your data
- 2 different storage media (e.g., internal drive + external drive)
- 1 offline / air-gapped copy (an external drive that isn't always connected)
Recommended cadence:
- Daily: cloud sync (OneDrive, Dropbox, Google Drive) - convenient, but vulnerable if the ransomware reaches the sync folder. The Version History feature is what saves you
- Weekly: external drive that you connect briefly, then disconnect - the air-gap is what protects against ransomware
- Monthly: a second external drive stored off-site (different physical location) - protects against fire, theft, flood
Test the backup at least once. Open a few files from it, check sizes match, restore one to a different folder. An untested backup isn't a backup - it's a hope.
Patch the entry point and monitor for 30 days
Most reinfections happen via the same vector that worked the first time. Until you've patched the entry point, watch for:
- Unusual disk activity, unexpected file modifications, or unfamiliar processes in Task Manager
- Unexpected reboots or new accounts you didn't create
- Defender or your antivirus turning itself off again
Common entry vectors and what to do about each:
- Phishing email with a malicious attachment - review email filters and train yourself / staff to recognise the patterns - see pcrisk's Phishing/Scam reference
- Exposed RDP with weak passwords - disable Remote Desktop from if you don't need it. If you do, put it behind a VPN and require a long password plus MFA
- Unpatched VPN appliances or public-facing apps - check the vendor's advisories page and apply the latest firmware
- Cracked / pirated software - was the most common vector for STOP/Djvu in particular. Don't run software from torrent sites
Run a Combo Cleaner scan weekly for the first month. Update Windows, browsers, and applications aggressively.
Important: Removing a ransomware infection requires a full system scan, not a manual file delete. If you're not confident with the manual procedure, run an automated scan with Combo Cleaner and Windows Defender and stop there - that combination removes the vast majority of consumer ransomware variants. Then move to Phase 4 for file recovery, or to Phase 5 if your files are unrecoverable and you need to start fresh from a clean Windows install.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion