
How to eliminate Imminent Monitor RAT from the operating system
TrojanAlso Known As: Imminent Monitor remote access tool

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What is Imminent Monitor?
Imminent Monitor is a legitimate remote access tool (RAT) allowing users to control Microsoft Windows-based servers and computers remotely, however, cyber criminals use 'cracked' versions of Imminent Monitor to generate revenue. Therefore, although the tool itself is legitimate, it can be misused in various ways.
The presence of Imminent Monitor on a system controlled by another party might thus cause serious problems.
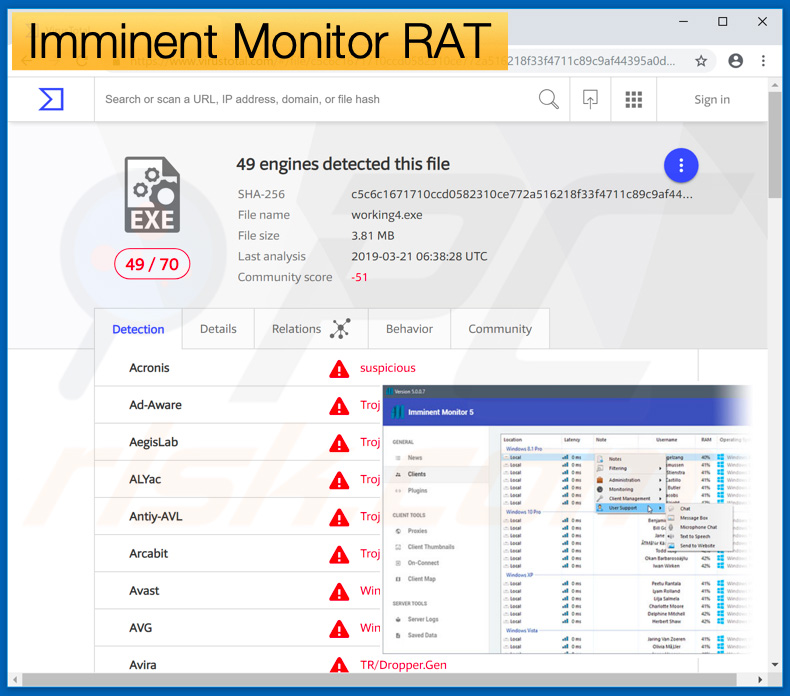
Imminent Monitor overview
Note that Imminent Monitor is a very advanced RAT with a long feature list. It allows users to record keystrokes, download/execute files, extract logins/passwords from browsers, terminate running processes, and perform dozens of other actions (you can find the entire list here).
When used by the computer's owner, this tool is very useful, however, if cyber criminals gain remote access using Imminent Monitor, the risk of computer infections, financial/data loss, and serious privacy issues is extremely high. Cyber criminals often use remote access tools to inject additional malware into the system.
RATs are often used to proliferate trojan-type infections (which typically gather personal data), ransomware, cryptominers, and browser hijackers/adware. Data-stealing trojans are designed to record browsing activity, keystrokes, credit card information, saved logins/passwords, etc. The presence of such infections might lead to serious privacy issues and significant financial loss.
Although Imminent Monitor is capable of performing these aforementioned actions, it is unlikely that criminals will use it to proliferate data stealers. Ransomware is designed to compromise stored data (usually, by encryption) and make demands for ransom payments in exchange for recovery of files.
Note, however, that ransomware developers often ignore victims, once payments are submitted. Therefore, paying usually gives no positive result, users are scammed, and the data remains encrypted. Cryptominers are malicious applications that misuse system resources to mine cryptocurrency without users' consent.
Mining can take up to 100% of system resources, and thus the system becomes unstable (can easily crash), virtually unusable (barely responds), and the hardware components might eventually overheat. Adware and browser hijackers are less harmful - most simply deliver intrusive advertisements, cause unwanted redirects, and gather data.
In summary, the presence of Imminent Monitor might lead to significant data/financial losses, serious privacy issues (identity theft), and high-risk computer infections. Fortunately, detecting and eliminating this infection is straightforward. Imminent Monitor creates a folder called "Imminent" within the Application Data folder.
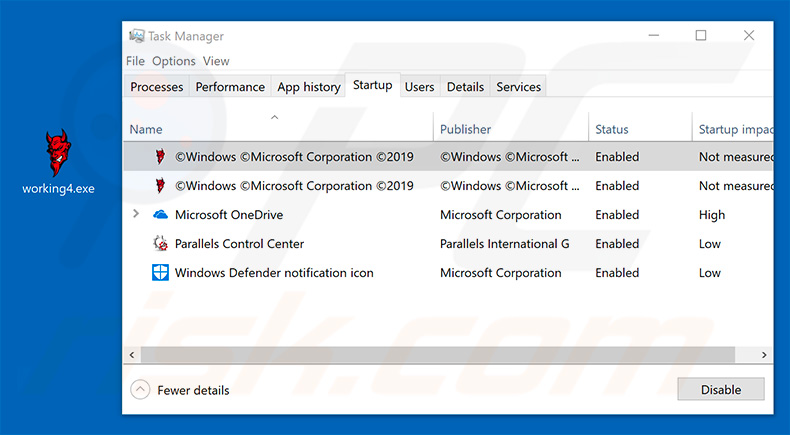
Furthermore, cracked process versions in Windows Task Manager have suspicious names. The sample we analyzed ran a process called "©Windows ©Microsoft Corporation ©2019". The executable itself was named "working4.exe" and its icon was a devil's face.
If you observe such a file or folder on your system or notice any suspicious activity, immediately scan the system with a reputable anti-virus/anti-spyware suite and eliminate all detected threats.
| Name | Imminent Monitor remote access tool |
| Threat Type | Trojan, Password stealing virus, Banking malware, Spyware. |
| Detection Names | Avast (Win32:RATX-gen [Trj]), Combo Cleaner (Gen:Trojan.Mardom.PN.15), ESET-NOD32 (A Variant Of MSIL/Kryptik.ORX), Kaspersky (HEUR:Trojan-Ransom.MSIL.Blocker.gen), Microsoft (PWS:MSIL/Fareit.VV!MTB), Full List Of Detections (VirusTotal) |
| Symptoms | Trojans are designed to stealthily infiltrate the victim's computer and remain silent. Thus, no particular symptoms are clearly visible on an infected machine. |
| Distribution methods | Infected email attachments, malicious online advertisements, social engineering, software cracks. |
| Damage | Stolen banking information, passwords, identity theft, victim's computer added to a botnet. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
Remote access tool/trojan examples
There are dozens of remote access tools used by cyber criminals including, for example, H-Worm, CrimsonRAT, Megalodon, and ExileRat. Some are legitimate, whilst others are developed by cyber criminals. All of these viruses are used for the same purpose: to generate as much revenue as possible. Therefore, uninstall all unwanted remote access tools immediately.
How did Imminent Monitor infiltrate my computer?
It is currently unknown exactly how developers proliferate Imminent Monitor, however, they often use spam email campaigns, fake software updaters/cracks, trojans, and unofficial software download sources.
Criminals use spam campaigns to send hundreds of thousands of emails containing malicious attachments (MS Office documents, PDFs, executables, etc.) and deceptive messages encouraging users to open them. Doing so results in various system infections.
Fake updaters infect systems by misusing outdated software bugs/flaws or simply downloading and installing malware rather than promised updates. Cracks have similar behavior - they activate paid software free of charge, however, since criminals use them to proliferate malware, users often end up infecting their computers rather than gaining access to paid features.
Trojans are essentially malicious apps that stealthily infiltrate computers and inject system with additional malware.
P2P networks (eMule, torrents, etc.), freeware download websites, free file hosting sites, and other third party download sources present malicious executables as legitimate software. This tricks users into manually downloading, installing, and running malware.
How to avoid installation of malware?
The main reasons for computer infections are poor knowledge of the threats and careless behavior. The key to safety is caution. Therefore, pay close attention when browsing the internet and downloading, installing, and updating software. We strongly recommend that you think twice before opening email attachments.
Be sure that the received file/link is relevant and the sender is known. If not, do not open anything and delete the email immediately. Download applications from official sources only, using direct download links. Third party downloaders/installers often include rogue applications, and thus such tools should never be used.
The same applies to software updates. Installed applications and operating systems should be kept up-to-date, however, this should be achieved only through implemented functions or tools provided by the official developer. Never attempt to crack installed applications - software piracy is a cyber crime and the risk of infections is extremely high.
Use a reputable anti-virus/anti-spyware suite, since these tools can detect and eliminate malware before the system is harmed. If you believe that your computer is already infected, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate infiltrated malware.
Screenshot of cracked Imminent Monitor executable ("working4.exe") and associated process ("©Windows ©Microsoft Corporation ©2019") in Windows Task Manager:
Update December 2nd, 2019 - Law enforcement agencies have recently shut down the entire Imminent Monitor network and arrested thirteen of its most prolific users who were using this tool for malicious purposes.
Agencies also seized over 400 computer devices and shut down Imminent Monitor's website. It is currently unconfirmed whether Imminent Monitor's developer was arrested or not. You can find more details in Europol's official press release.
How to remove malware manually?
Most trojan infections can be removed by running a full system scan with Combo Cleaner. The full manual procedure below is for cases where automatic removal failed, where you want to verify a scan caught everything, or where the threat has multiple persistence points.
Disconnect from the network
Unplug your Ethernet cable and turn off Wi-Fi. If you're on a laptop, the airplane-mode key works fastest.
Many trojans exfiltrate data - saved browser passwords, banking sessions, screenshots - and accept remote commands. Cutting the network stops both immediately. Keep it disconnected until Phase 4.
Boot into Safe Mode with Networking
Safe Mode loads a minimal set of drivers and stops most malware from auto-running. "With Networking" lets you download tools - re-enable Wi-Fi only after you've booted in.
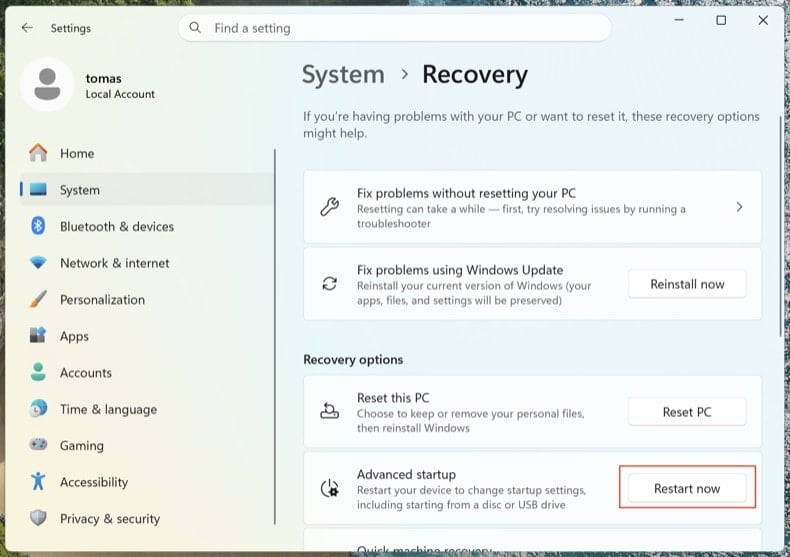
Open . Click Restart now next to Advanced startup.
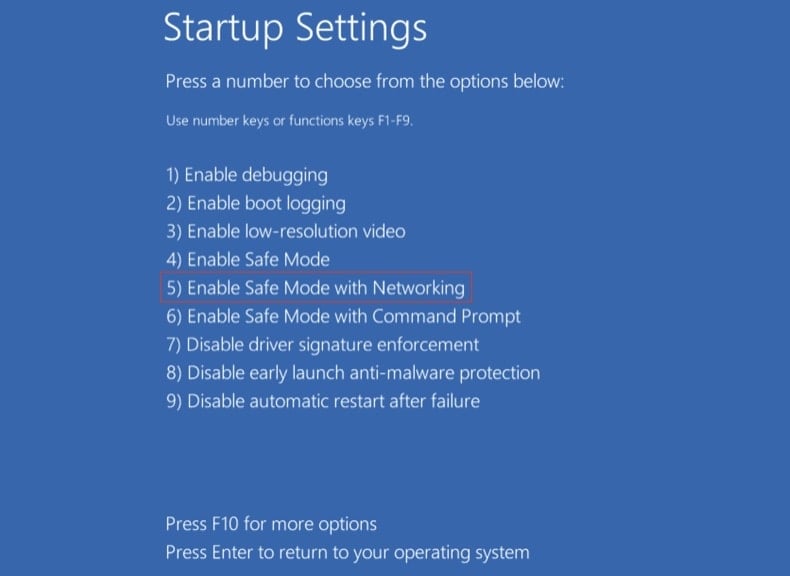
Your computer will restart into the "Choose an option" menu. Click . After the second reboot, press 5 or F5.
Click the Windows logo, hold Shift, click the Power icon and choose Restart. In the Choose an option screen, click . Press F5.
Windows 8
Go to the Start Screen, type Advanced, select Settings → Advanced startup options → Restart now → Troubleshoot → Advanced options → Startup settings → Restart → F5.
Note: Windows 8 reached end-of-life in January 2023 - running on it puts you at much higher risk of reinfection.
Windows 7
Click Start → Shut Down → Restart → OK. As the system boots, press F8 repeatedly until the Windows Advanced Options menu appears, then choose Safe Mode with Networking.
Note: Windows 7 reached end-of-life in January 2020 - running on it puts you at much higher risk of reinfection.
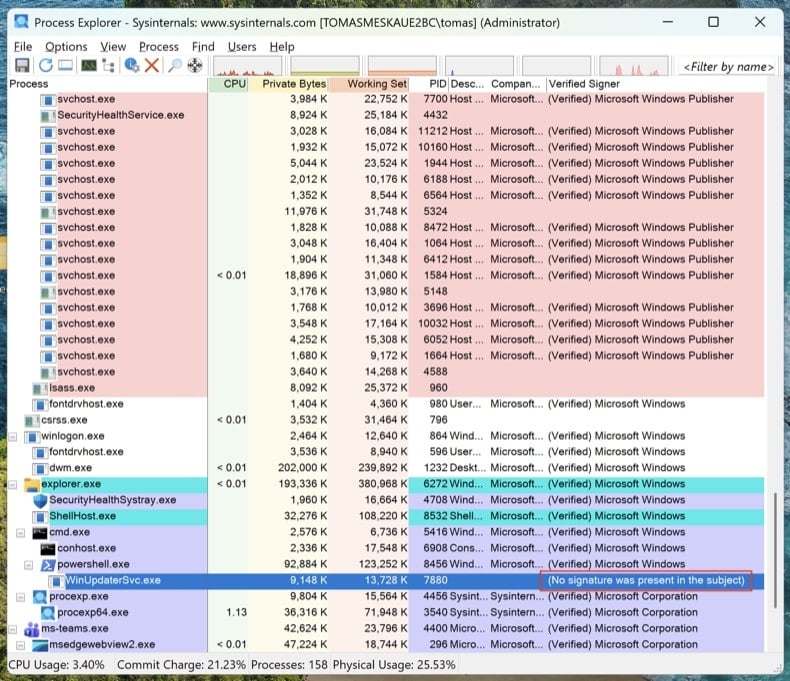
Inspect running processes with Process Explorer
Download Process Explorer from Microsoft Sysinternals. Run it as Administrator. Click and .
Sort by "Verified Signer." Anything unsigned running from %AppData%, %LocalAppData%, %Temp%, or %ProgramData% is suspicious. Right-click → Properties to see the full image path. Right-click → "Search Online" to look up unfamiliar process names.
Task Manager hides full file paths, doesn't show digital signatures, and groups processes in ways that make malware easy to miss. Process Explorer is the same tool Microsoft engineers use.
Map every persistence point with Autoruns
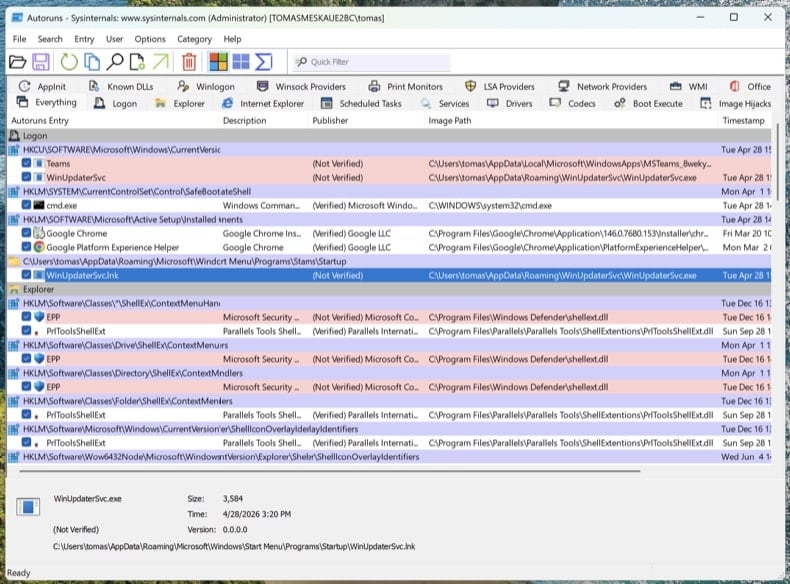
Download Autoruns. Right-click Autoruns.exe and choose Run as administrator - without elevation, Autoruns can't inspect protected registry hives.
In the menu, open and , then click Refresh.
Modern trojans don't just live in startup. Walk through these tabs and look for unsigned or unfamiliar entries:
- Logon - classic Run/RunOnce keys
- Scheduled Tasks - frequent hiding spot, especially tasks with PowerShell, MSHTA, or rundll32 actions
- Services - unsigned services in non-Microsoft folders
- WMI - Event Subscriptions are a stealthy persistence mechanism (MITRE T1546.003)
- Image Hijacks - Image File Execution Options "Debugger" abuse
- AppInit - DLLs loaded into every GUI process
- Browser plug-ins - unsigned add-ons across all installed browsers
Right-click any suspicious entry → "Jump to Image" to see the actual file. Right-click → "Search Online" opens VirusTotal for the file hash. Don't delete yet - just write down the file paths and entry names. We'll remove them after the scans.
Check the hosts file and DNS settings
Trojans often redirect bank, antivirus, and update domains to attacker-controlled servers by editing the hosts file or DNS settings.
Hosts file: Open Notepad as Administrator and open C:\Windows\System32\drivers\etc\hosts. Legitimate entries are commented with #. Any uncommented IP-to-domain mapping is suspicious - especially redirects for microsoft.com, windowsupdate, or your bank.
DNS settings: Open Command Prompt as Administrator and run ipconfig /all. Confirm your DNS servers point to your ISP, your router, or a known public resolver (Cloudflare 1.1.1.1, Google 8.8.8.8). Then open and verify both DNS and DNS over HTTPS (DoH) settings haven't been hijacked.
A clean PC with hijacked DNS is still a compromised PC. You'll think you're at chase.com and you'll be at the attacker's clone.
No single antivirus catches everything. The order below is intentional: offline scan first (catches rootkits before Windows fully loads), then on-demand scanners on the running system, then manual cleanup of anything they missed.
Run Microsoft Defender Offline
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. Your computer will restart into a stripped-down environment and scan before the full operating system loads.
Rootkits and bootkits hide from any scanner running on the same Windows session that's already infected. A pre-boot offline scan sees the disk before the malware can hide itself.
VB100 certified. Includes anti-trojan, registry/persistence scanning, anti-spyware in one pass. The 7-day free trial is available.
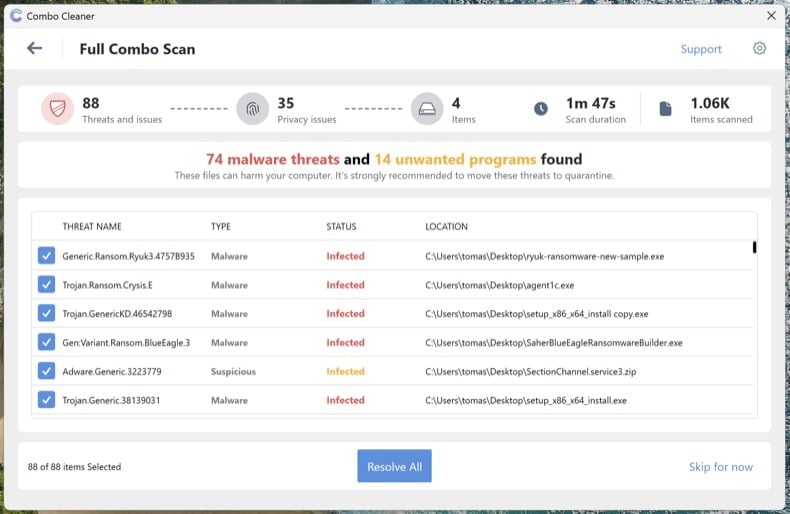
Download Combo CleanerRun Combo Cleaner full system scan
Install Combo Cleaner and run a full system scan (not the quick scan). Let it complete fully, review the detected threats, and apply the recommended actions. Combo Cleaner will quarantine known trojans and registry persistence.
Run Microsoft Safety Scanner as a second-opinion scan
Download Microsoft Safety Scanner (MSERT.exe), Microsoft's free on-demand tool. The binary expires every 10 days, which means every download has the latest signatures. Run a full scan after Combo Cleaner to catch anything one engine alone might miss.
Different scanning engines catch different threats. Running an additional Microsoft scan after Combo Cleaner is the single most underused verification step in malware removal.
Manually remove anything still listed in Autoruns
Reopen Autoruns. Anything you flagged in Step 4 that's still present hasn't been caught by the automated scans. For each remaining suspicious entry: right-click → Delete in Autoruns (this removes the persistence registration), then navigate to the file path and delete the actual file. Empty the Recycle Bin.
Some malware files reappear after deletion because something else on the system recreates them. If you delete a file and it returns within minutes, you have a remaining persistence point that Autoruns didn't show - usually a service or scheduled task running under SYSTEM. Re-run the scans from Steps 6-8 or proceed to a clean install (see end of guide).
Reset browsers and clear notification permissions
Trojans and adware frequently hijack browsers - change the default search engine, install rogue extensions, or grant themselves notification permissions to keep displaying scam pop-ups even after the malware is gone.
- Chrome: visit
chrome://settings/resetand click "Restore settings to their original defaults." Then visitchrome://settings/content/notificationsand remove any unfamiliar sites. - Edge: visit
edge://settings/reset. Then checkedge://settings/content/notifications. - Firefox: open
about:supportand click Refresh Firefox (Firefox uses "Refresh," not "Reset"). Then check Settings → Privacy & Security → Permissions → Notifications.
Review installed extensions in each browser and remove anything you don't recognize, especially extensions you didn't install yourself.
Re-enable Defender, Tamper Protection, and update everything
Many trojans disable security software. Open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all turned on. Tamper Protection prevents malware from disabling Defender silently.
Then run Windows Update () and update your browsers and applications. The infection vector that let the trojan in originally usually involves outdated software.
Change passwords from a clean device
If the trojan was an info-stealer (Lumma, RedLine, Vidar, and similar are extremely common), assume every password saved in your browser is compromised. Change them from a different, known-clean device - your phone is fine if it's not infected.
Recommended order:
- Primary email first - it's the recovery hub for everything else
- Banking and financial accounts
- Password manager master password (if you use one)
- Social media, shopping, and remaining accounts
Where available, enable phishing-resistant multi-factor authentication (passkeys / FIDO2 hardware keys / authenticator apps) - SMS-based MFA is bypassable by sophisticated attackers.
Verify the clean and monitor for 7 days
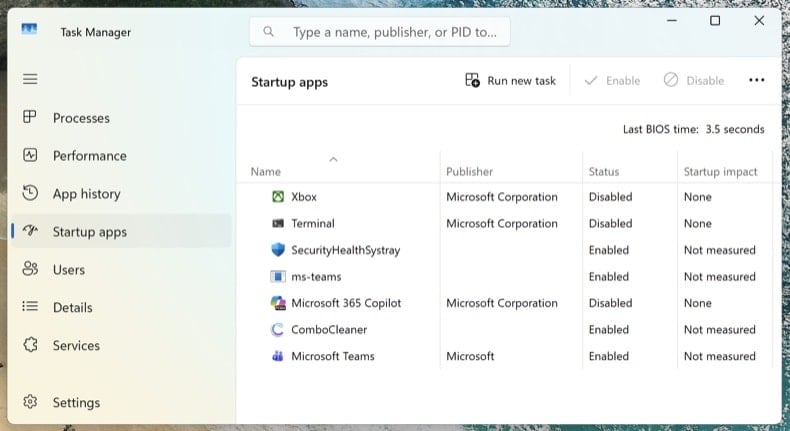
Reconnect to the network and run one final full scan with Combo Cleaner. Open Task Manager (Ctrl + Shift + Esc) and switch to the Startup apps tab - confirm nothing suspicious has reappeared.
Over the next 7 days, watch for symptom recurrence: unexpected high CPU usage, unknown processes returning, browser redirects, or pop-ups. If anything returns, you missed a persistence point and the procedure needs to be repeated - or you may have a deeper compromise that requires a clean install.
When to clean install Windows instead
Manual removal isn't always the right answer. Reinstalling Windows from scratch is the only way to be 100% certain when:
- The malware reappears after every removal attempt
- A bootkit or UEFI rootkit was detected (this class of threat sits below the operating system and survives a normal Windows reinstall)
- A confirmed credential-theft trojan ran with administrator privileges (Lumma, RedLine, Vidar) - the system likely has multiple unknown payloads
- The PC is used for online banking, business email, or anything where partial doubt isn't acceptable
A clean install is a 30-60 minute process: Windows 11 reinstall via . Back up documents to external storage first, scan the backup with Combo Cleaner before restoring it, and reinstall applications fresh - never restore them from a backup of the infected system.
Important: Manual removal requires advanced computer skills. If you're not confident identifying system files from malicious files, run an automated scan with Combo Cleaner and Windows Defender and stop there - that path catches the vast majority of consumer trojans without the risk of breaking Windows by deleting the wrong file.
Frequently Asked Questions (FAQ)
My computer is infected with Imminent Monitor, should I format my storage device to get rid of it?
No, Imminent Monitor's removal does not require formatting.
What are the biggest issues that Imminent Monitor can cause?
Imminent Monitor is capable of enabling remote access/control over machines, and it has a wide variety of functionalities. This program can perform various actions on devices, extract data, upload/execute files (a feature that can be used to infect systems with additional malware), and so on. Therefore, the threats posed by Imminent Monitor infections are especially broad and include severe privacy issues, financial losses, and identity theft.
What is the purpose of Imminent Monitor?
Imminent Monitor is a legitimate Remote Access Tool, but cyber criminals use it for nefarious purposes. Typically, system infections are used to generate revenue. However, criminals may also use malware to amuse themselves, carry out personal grudges, disrupt processes (e.g., websites, services, companies, etc.), or even launch politically/geopolitically motivated attacks.
How did Imminent Monitor infiltrate my computer?
Malware is primarily distributed through drive-by downloads, malicious attachments/links in spam emails and messages, online scams, untrustworthy download channels (e.g., unofficial and freeware sites, P2P sharing networks, etc.), illegal program activation tools ("cracks"), and fake updates. Furthermore, some malicious programs can self-proliferate via local networks and removable storage devices (e.g., external hard drives, USB flash drives, etc.).
Will Combo Cleaner protect me from malware?
Yes, Combo Cleaner is capable of detecting and eliminating nearly all known malware infections. It is noteworthy that performing a complete system scan is paramount - since high-end malicious software tends to hide deep within systems.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion