

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What kind of malware is One Decryptor Ransomware?
One Decryptor Ransomware is ransomware discovered by our researchers during a routine inspection of new submissions to the VirusTotal website. It encrypts files using AES-256 combined with RSA-2048 key wrapping, leaving victims unable to access their data without the private key held by the attackers.
The ransomware also deletes shadow volume copies, removes the backup catalog, and disables the recovery environment to prevent standard restoration methods from working.
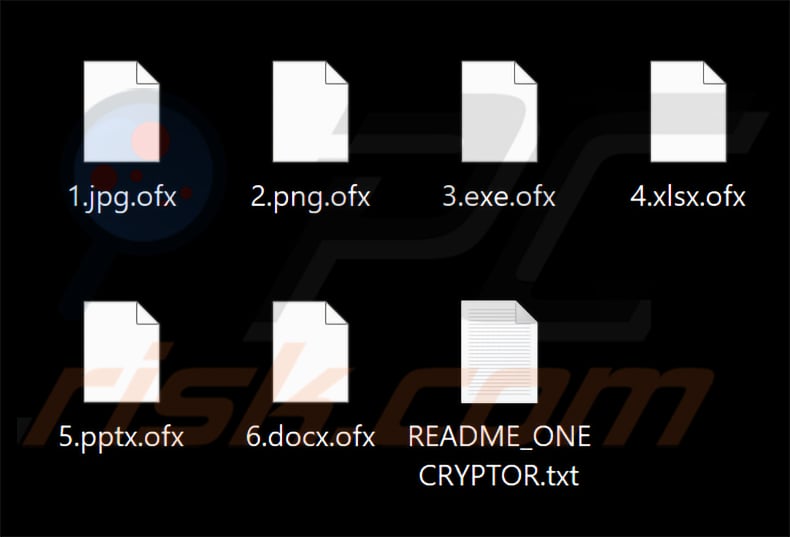
On our test machine, files were encrypted and the ".ofx" extension was appended to filenames. A file named "1.jpg" became "1.jpg.ofx", "2.png" became "2.png.ofx", and so on. Afterward, One Decryptor displayed a ransom note in a pop-up window and dropped a text file titled "README_ONECRYPTOR.txt".
Screenshot of files encrypted by One Decryptor ransomware:
One Decryptor ransom note overview
The text file informs victims that all their documents, images, archives, and databases have been encrypted with AES-256. Each file carries its own session key, wrapped using RSA-2048, and the private key is not stored anywhere on the infected machine.
The note also describes what the ransomware has already done: files were renamed with the .ofx extension, shadow copies and the backup catalog were removed, and the recovery environment was disabled.
Payment of 0.42 BNB via the BEP-20 network is required within 72 hours. After the deadline, the demanded amount doubles to 0.84 BNB. Victims are told to include a specific memo with the transaction and then email onecryptor@onionmail.org with the transaction hash after payment.
The decryptor is reportedly sent once payment confirms. The note also warns against renaming or editing encrypted files and states that recovery tools cannot derive the encryption key.
The pop-up window conveys the same demands: 0.42 BNB via BEP-20 only, a countdown timer until the deadline, and the same price-doubling threat. It warns that any other cryptocurrency will not count toward the ransom and advises victims not to restart the system.
One Decryptor ransomware overview
One Decryptor uses AES-256 for file encryption and RSA-2048 to protect each individual session key. This combination means there is no key material left on the local disk, and recovery without the attacker's cooperation is not feasible through conventional means.
In general, files locked by ransomware cannot be recovered without the attackers' involvement. The only exceptions are cases involving serious implementation flaws, which are uncommon and have not been identified in this ransomware.
Paying the ransom carries no guarantee. Cybercriminals often fail to provide a working decryptor even after receiving payment. We strongly advise against meeting their demands.
Removing One Decryptor from the system is essential to stop ongoing encryption. It is important to understand, however, that removal does not restore already-encrypted files. Recovery depends on having a clean backup stored on a separate device or a remote server.
Ransomware in general
The core purpose of ransomware attacks is to extort money by holding files hostage. Most ransomware programs operate the same way. The primary differences between strains lie in the symmetric or asymmetric encryption algorithms used and the ransom amounts demanded. Additional ransomware examples are Coffin Locker, Citrus, and Hexsomeware.
How did ransomware infect my computer?
Ransomware most commonly spreads through phishing emails carrying malicious attachments or links. Files used in these campaigns often include Microsoft Office documents with macros, JavaScript files, PDFs, and executables disguised as ordinary content.
Other common vectors include trojans already present on the system, peer-to-peer networks, unofficial download sites, fake software updaters, and pirated software or cracks.
Once a malicious file is opened or executed, the ransomware runs silently in the background and encrypts files. By the time the victim notices, recovery without a backup is rarely possible.
| Name | One Decryptor virus |
| Threat Type | Ransomware, Crypto Virus, Files locker |
| Encrypted Files Extension | .ofx |
| Ransom Demanding Message | Pop-up window, README_ONECRYPTOR.txt |
| Free Decryptor Available? | No |
| Cybercriminal Contact | onecryptor@onionmail.org |
| Detection Names | Avast (MalwareX-gen [Ransom]), Malwarebytes (Ransom.OneCryptor), McAfee (Ti!799D96730E07), Microsoft (Trojan:Win32/Sonbokli.A!cl), Full List Of Detections (VirusTotal) |
| Symptoms | Cannot open files stored on your computer, previously functional files now have a different extension (for example, my.docx.locked). A ransom demand message is displayed on your desktop. Cybercriminals demand payment of a ransom (usually in bitcoins) to unlock your files. |
| Distribution methods | Infected email attachments (macros), torrent websites, malicious ads. |
| Damage | All files are encrypted and cannot be opened without paying a ransom. Additional password-stealing trojans and malware infections can be installed together with a ransomware infection. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
How to protect yourself from ransomware infections?
Approach emails carefully, especially unsolicited messages with attachments or links. Download software only from official sources and authorized stores. Always update and activate programs through legitimate means, not through third-party tools or cracks.
If your computer is already infected with One Decryptor ransomware, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate this ransomware.
Screenshot of One Decryptor ransomware's ransom note ("README_ONECRYPTOR.txt"):
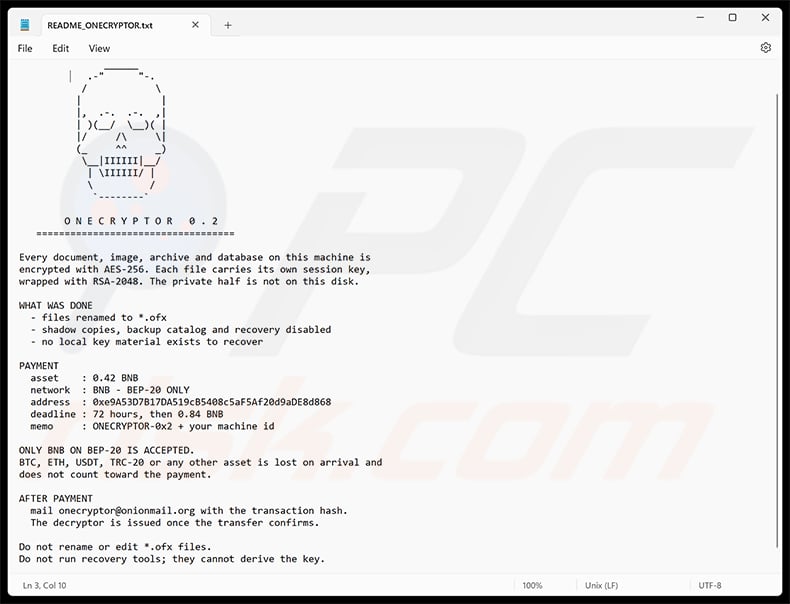
Text presented in this ransom note:
O N E C R Y P T O R 0 . 2
===================================
Every document, image, archive and database on this machine is
encrypted with AES-256. Each file carries its own session key,
wrapped with RSA-2048. The private half is not on this disk.
WHAT WAS DONE
- files renamed to *.ofx
- shadow copies, backup catalog and recovery disabled
- no local key material exists to recover
PAYMENT
asset: 0.42 BNB
network: BNB - BEP-20 ONLY
address: [cryptocurrency wallet address]
deadline : 72 hours, then 0.84 BNB
memo : ONECRYPTOR-0x2 + your machine id
ONLY BNB ON BEP-20 IS ACCEPTED.
BTC, ETH, USDT, TRC-20 or any other asset is lost on arrival and
does not count toward the payment.
AFTER PAYMENT
mail onecryptor@onionmail.org with the transaction hash.
The decryptor is issued once the transfer confirms.
Do not rename or edit *.ofx files.
Do not run recovery tools; they cannot derive the key.
Screenshot of One Decryptor ransomware's pop-up window:
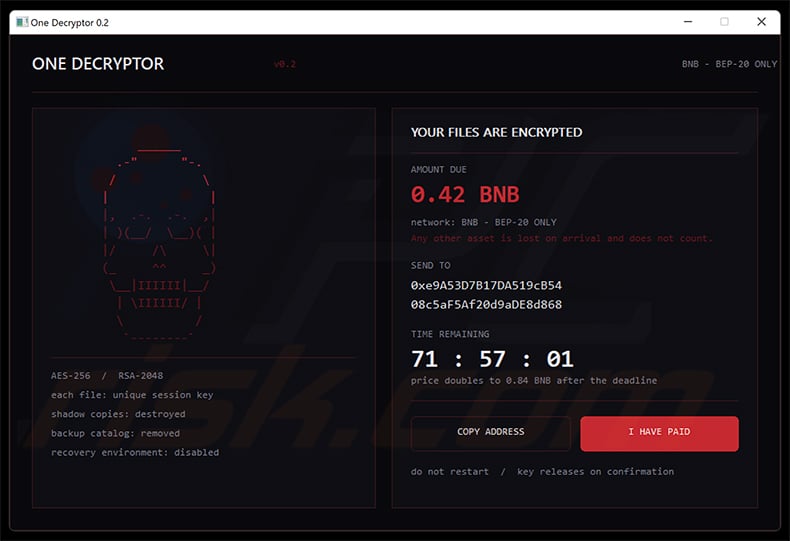
Text presented in this pop-up:
ONE DECRYPTOR
YOUR FILES ARE ENCRYPTED
AMOUNT DUE 0.42 BNB
network: BNB - BEP-20 ONLY
Any other asset is lost on arrival and does not count.
SEND TO [cryptocurrency wallet address]
TIME REMAINING
price doubles to 0.84 BNB after the deadline
do not restart / key releases on confirmation
One Decryptor ransomware removal:
Instant automatic malware removal:
Manual threat removal might be a lengthy and complicated process that requires advanced IT skills. Combo Cleaner is a professional automatic malware removal tool that is recommended to get rid of malware. Download it by clicking the button below:
DOWNLOAD Combo CleanerBy downloading any software listed on this website you agree to our Privacy Policy and Terms of Use. To use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
Removal and file recovery procedure
If your files are encrypted with a new extension and a ransom note has appeared, you've been hit by ransomware. Don't pay. The procedure below works in order: contain the infection, identify the variant, remove the ransomware itself (so anything you restore doesn't get re-encrypted), and try to recover files using free decryption tools, Windows Volume Shadow Copies, or backups. Run a full system scan with Combo Cleaner to remove the infection - then move on to file recovery.
Common ransomware behaviors
VisibleEncrypts your files and renames them
The ransomware reads each file, encrypts the contents with the attacker's public key, and writes the encrypted bytes back to disk. Most variants also rename the file by appending a new extension - .net, .locked, .crypt, .lockbit, .djvu, etc. Without the matching private key, the encrypted files cannot be opened normally. Recovery depends on a free decryption tool, a recoverable Volume Shadow Copy, or a clean backup.
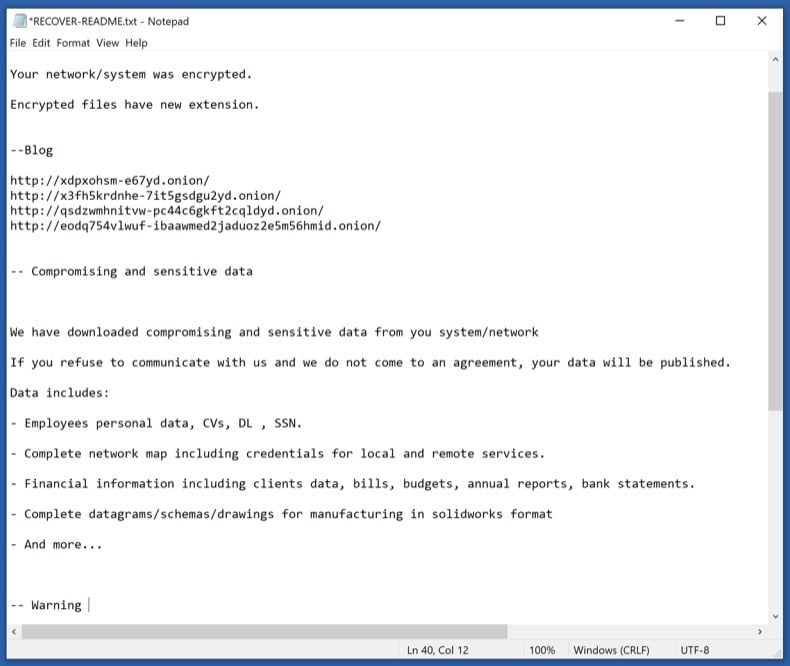
VisibleDrops a ransom note in every encrypted folder
A text or HTML file (usually named HOW_TO_DECRYPT.txt, README.txt, _readme.txt, or similar) is placed in every folder that contains encrypted files. The note explains the situation, lists a payment amount in cryptocurrency, gives a deadline, and provides a contact email or .onion site. Save the note - don't delete it. Its exact wording, the email address, and the bitcoin wallet are how you identify the variant in the next phase.
VisibleReplaces the desktop wallpaper
Many ransomware variants change the Windows wallpaper to a black or red image with the ransom message and instructions. The wallpaper is just a visual scare tactic - it doesn't add any actual capability and reverts to normal once the ransomware is removed. Photograph it before removal in case the contact details are useful for variant identification or for reporting to authorities.
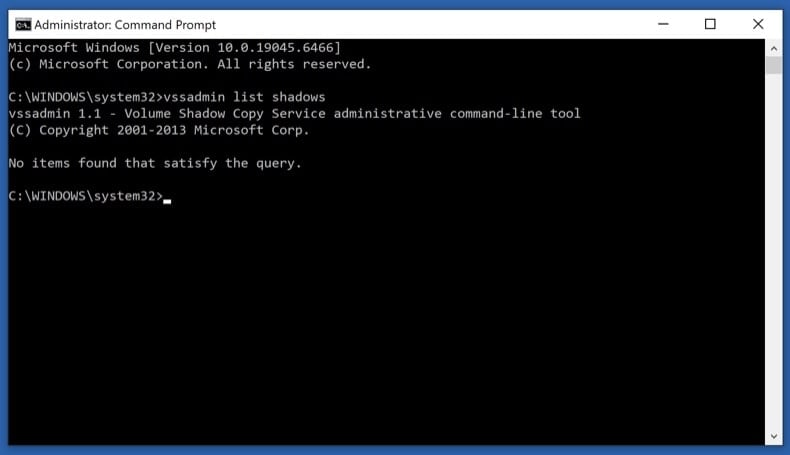
HiddenDeletes Volume Shadow Copies
One of the first things modern ransomware does after launching is run vssadmin delete shadows /all /quiet to wipe Windows' built-in Volume Shadow Copies - the snapshots that Previous Versions and System Restore rely on. Some ransomware doesn't fully succeed (especially on systems where the user lacks full admin rights), leaving partial shadow copies recoverable. Phase 4 step 11 covers how to check what survived.
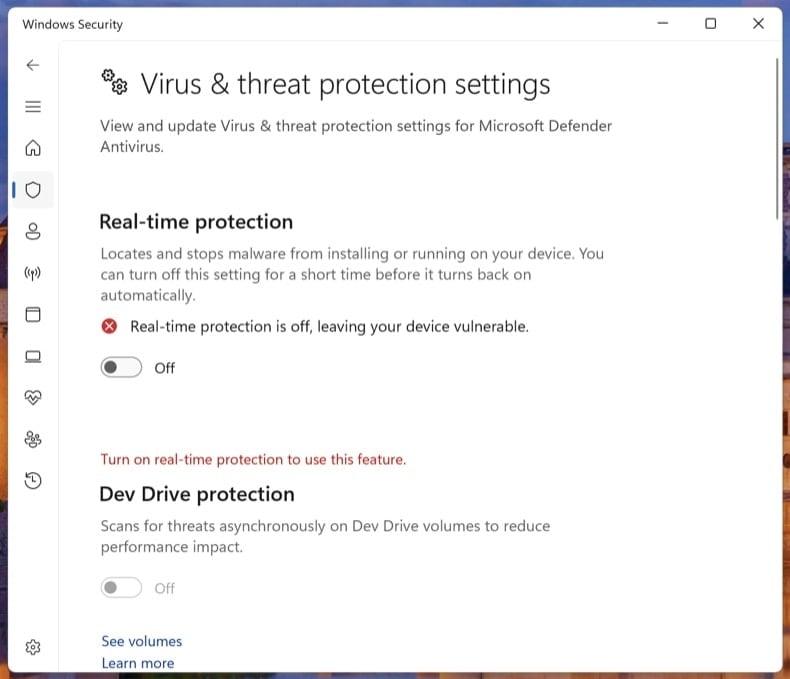
HiddenDisables Windows Defender and other security tools
Before encrypting, the ransomware tries to silence anything that could alert you or block it - Windows Defender real-time protection, third-party antivirus services, backup agents (Veeam, Acronis), and sometimes the Windows Event Log service. It often modifies Group Policy or registry keys to keep these off after reboot. Phase 3 step 9 explicitly turns Tamper Protection back on so the next ransomware attempt can't repeat the trick.
HiddenSpreads laterally to other PCs on the network
Network-aware ransomware (LockBit, Conti, BlackCat, Akira families) doesn't stop at the first machine. It scans for SMB shares, mapped drives, and other PCs on the same network, then encrypts whatever it can reach. On Windows domains, a single compromised user with admin rights can lead to all-domain encryption. This is why Phase 1 step 2 disconnects the network as the very first action - it stops the spread immediately.
HiddenSteals data before encrypting (double extortion)
Modern ransomware (LockBit, BlackCat / ALPHV, Akira, Cl0p, Royal) almost always exfiltrates data before encrypting. The attacker then runs a "double extortion" play: pay the ransom for decryption, plus pay again to prevent the stolen data from being leaked on the group's leak site. Paying the first ransom does not get the leaked data back - assume that anything the ransomware could read was uploaded. This is one more reason not to pay: the data is already out.
Don't pay the ransom
Paying the ransom does not guarantee you'll get your files back. Major ransomware response studies consistently show that a meaningful percentage of paying victims either receive a non-working decryptor, only partial decryption, or no decryptor at all. Beyond that:
- Paying confirms you as a willing target - re-attack rates within 12 months are high
- Several ransomware groups have been sanctioned (US OFAC, UK OFSI). Paying these groups may be illegal under sanctions law in your country
- The ransom funds the next attack - on you or someone else
- Modern ransomware almost always exfiltrates data first, so paying doesn't get the leaked data back. Assume anything the malware could read was uploaded
- Decryptors, even when they work, often leave files corrupted because the encryption itself was buggy or rushed
The path below tries every legal, free recovery option first. Pay only as an absolute last resort, after consulting a lawyer and your country's cyber crime authority.
Disconnect from the network and log out of cloud storage
Pull the Ethernet cable and turn off Wi-Fi on the affected PC. If multiple computers share the network, do the same on every machine you suspect could be affected, including any servers and NAS units.
Then sign out of cloud storage clients (OneDrive, Dropbox, Google Drive, iCloud) from their app settings. If you can, pause the sync. Some ransomware uses the running sync client to push encrypted versions over your clean cloud copies.
Modern ransomware spreads laterally across SMB shares, mapped drives, RDP, and reachable network neighbors. Disconnecting stops the spread the moment you do it. Logging out of cloud sync clients prevents the ransomware from encrypting the cloud copies of your files via the sync API.
Unplug external drives and USB storage
Safely eject any external drives, USB sticks, SD cards, and network-attached storage shares - then unplug them. If a drive was connected when the ransomware ran, the files on it may already be encrypted, but unplugging stops further damage.
Critically: don't reconnect any drive (including your most recent backup) to this PC until the ransomware is removed in Phase 3. Reconnecting an external backup to an actively-infected PC is the most common way that backup gets encrypted too.
Save the ransom note and a sample encrypted file
Copy the ransom note and one small encrypted file (under 1 MB) to a USB stick, or photograph the note with your phone. You'll need both for the variant identification step.
The ransom note is usually one of:
- A
.txtfile in every encrypted folder (typicallyHOW_TO_DECRYPT.txt,README.txt, or_readme.txt) - An
.htmlfile with the same purpose - A changed desktop wallpaper - photograph it
- A lock-screen interrupt that runs at startup - rarer
Don't delete the note. Variant identification depends on its exact wording, the contact email, and the bitcoin wallet address. The note is also evidence if you report to authorities.
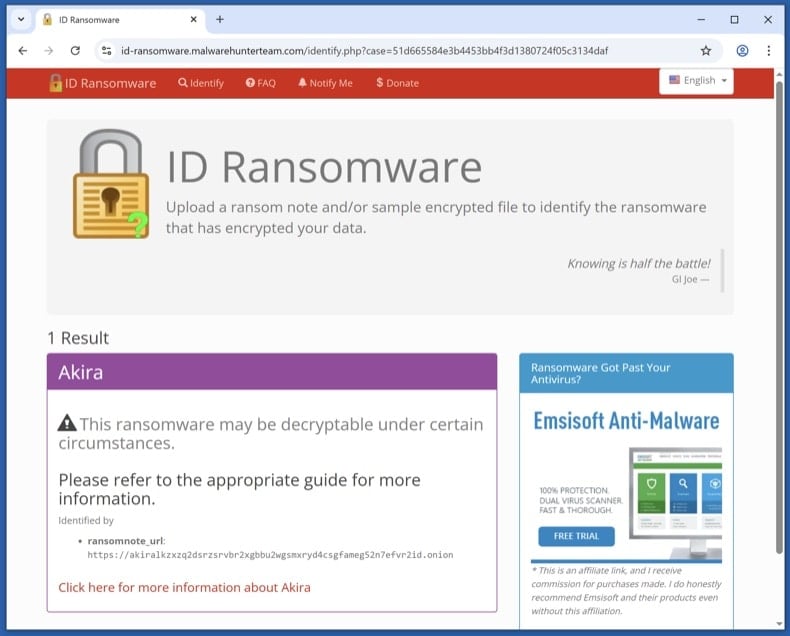
Identify the variant with ID Ransomware
From a clean device (your phone is fine, or another PC that wasn't on the affected network), visit id-ransomware.malwarehunterteam.com. Upload the ransom note and the sample encrypted file. The site identifies the variant family and tells you whether a free decryptor exists.
ID Ransomware is run by the Malware Hunter Team. Files you upload are kept private - they're used for analysis, not published. If you're concerned about uploading data anyway, you can paste the contact email and bitcoin wallet from the note - those are often enough for identification.
The ransomware itself must be removed before any file recovery. If it's still active, anything you restore in Phase 4 gets re-encrypted within minutes.
Boot to Safe Mode with Networking and download the scanners
Safe Mode loads only the minimal Windows drivers, which prevents most ransomware from auto-running while you set up the scanners.
Windows 11: open , click Restart now next to Advanced startup. After the restart, click , then press 5 or F5.
Windows 10: click the Windows logo, hold Shift, click the Power icon and choose Restart. From the Choose-an-option screen, click , then press F5.
Once Safe Mode has loaded, turn Wi-Fi back on and download Combo Cleaner (used in step 8) and Microsoft Safety Scanner (used in step 9). Save both installers to your Desktop, then disconnect Wi-Fi again before scanning.
Run Microsoft Defender Offline
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts into a stripped-down environment and scans the disk before Windows fully loads.
Some ransomware variants drop bootkit components or kernel hooks that hide from any scanner running on the same Windows session that's already infected. A pre-boot offline scan sees the disk before the malware can load itself.
VB100 certified. Includes anti-trojan, registry/persistence scanning, and anti-spyware in one pass. The 7-day free trial is available.
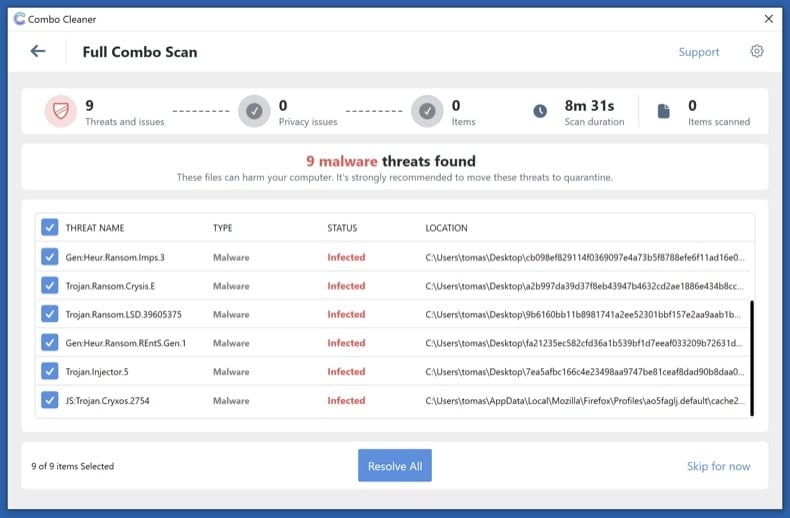
Download Combo CleanerRun a full Combo Cleaner scan
Run the installer you downloaded in step 6 and start a full system scan (not the quick scan). Let it complete, review what it detected, and apply the recommended actions. Combo Cleaner quarantines the ransomware executable and the registry / scheduled-task entries that re-launch it on reboot.
Run Microsoft Safety Scanner and re-enable Defender
Run Microsoft Safety Scanner (MSERT.exe) as a second-opinion full scan. The binary expires every 10 days so the copy you downloaded has the latest signatures.
Once it finishes, open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all on. Many ransomware variants disable Defender during the attack - this is where you switch it back on so the next attempt can't repeat the trick.
Different scanning engines catch different threats. Running an additional Microsoft scan after Combo Cleaner is the most underused verification step in malware removal - and free.
Try the steps in order. The first decryptor that works ends the recovery process - no need to do all four.
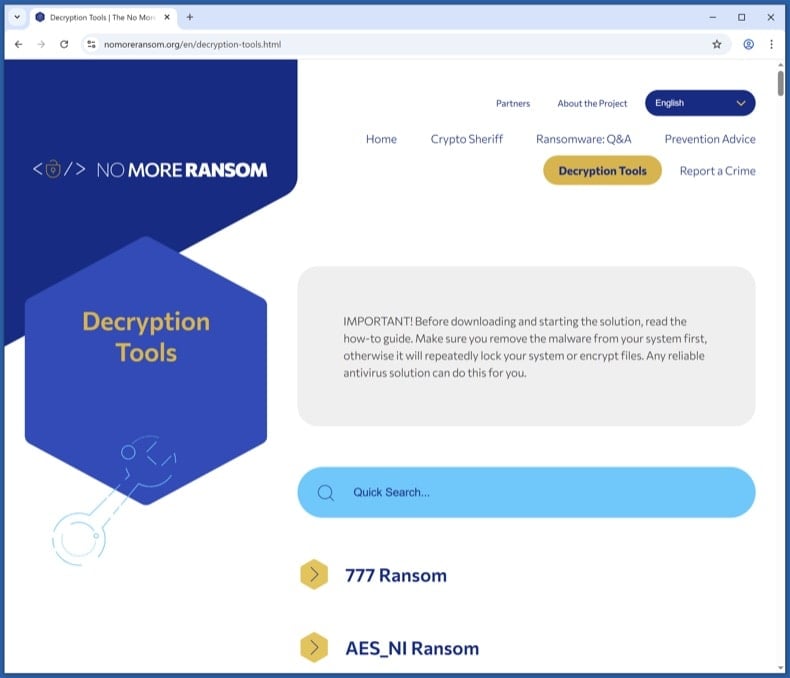
Check the No More Ransom Project for a free decryptor
Visit nomoreransom.org and search the Decryption Tools list for the variant name returned by ID Ransomware. The project is run by Europol, the Dutch Police, and security vendors - everything listed is legitimate and free.
If a decryptor exists, download it onto a clean PC, copy it across, and follow its instructions exactly. Decryptors usually want you to point them at a sample encrypted file plus its known unencrypted version (sometimes any image you previously had a backup of works).
Free decryptors exist for parts of the STOP/Djvu, GandCrab, REvil, Avaddon, Conti and Hive families, among others. Most modern variants don't have public decryptors - if yours isn't listed, that's expected; move to the next step.
Try Windows Volume Shadow Copies
Windows automatically creates Volume Shadow Copies of files when System Restore points are made or scheduled backups run. Most ransomware tries to wipe these (vssadmin delete shadows /all /quiet), but the deletion sometimes fails partially - especially if the running user doesn't have full admin rights. When it does fail, snapshots survive that contain pre-encryption versions of your files.
First, check what's there. Open Command Prompt as Administrator and run:
vssadmin list shadows
If you see entries listed, shadow copies survived. To restore from them:
- Built-in: right-click any folder → Properties → Previous Versions tab. Pick a snapshot dated before the infection and restore.
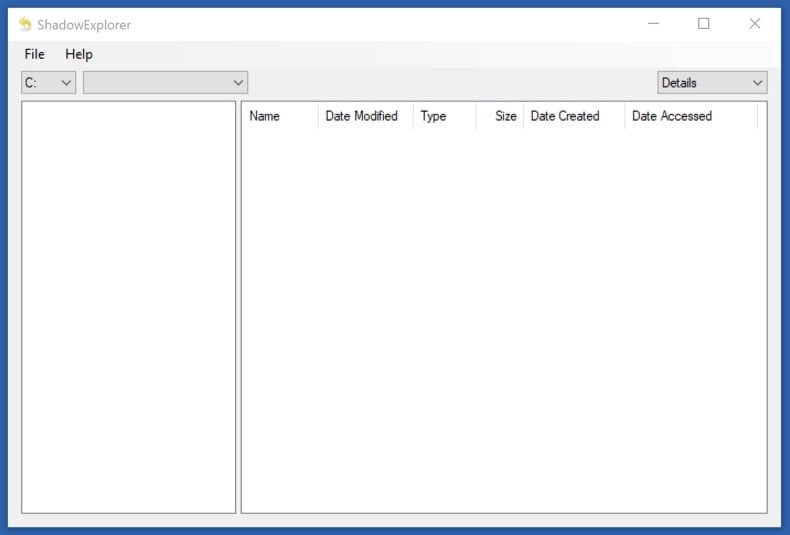
- Better tool for browsing: install Shadow Explorer (free). It shows all snapshots as a normal file tree and lets you copy out only the files you want.
Shadow Copies recover the original files exactly, with no risk of decryption errors. If they survived, this is faster and cleaner than running a decryptor on the encrypted set.
Restore from cloud or external backup
If you have a backup that pre-dates the infection, this is the cleanest recovery available. Important precautions:
- Don't reconnect a backup drive until Phase 3 is complete. If the ransomware is still active, plugging in the backup encrypts it too.
- For cloud backups (OneDrive, Dropbox, Google Drive, iCloud), use the Version History feature to roll individual files back to pre-encryption versions.
- OneDrive specifically has a "Restore your OneDrive" feature: if it detected mass file changes, you can roll back the entire account up to 30 days. Sign in at OneDrive on the web, click the Settings gear, and choose Restore your OneDrive. Microsoft 365 subscribers also get ransomware detection alerts; non-subscribers get one free recovery.
- Verify the restored files open correctly before you delete the encrypted set. Test a few documents, photos, and any database / project files.
Try Recuva as a last-resort recovery
Recuva is a long shot, not a primary recovery tool. Most modern ransomware encrypts files in place - it reads the original, encrypts the data, and writes the encrypted bytes back to the same disk location. In that case, the original isn't deleted, just rewritten - and Recuva has nothing to find.
But for older or simpler variants that deleted originals before creating encrypted copies (rather than encrypting in place), Recuva can sometimes pull the originals from unallocated disk space. Worth trying as a last resort, especially before you use the disk much further.
If you try it:
- Stop using the disk as much as possible - every disk write reduces recovery odds
- Run Recuva from a USB stick, not from the affected disk
- Use Deep Scan mode (slower but the only mode worth running for this scenario)
Don't skip the steps above expecting Recuva to bail you out. It works in maybe 5-20% of cases, depending on the variant and how soon you try.
Report the attack to authorities
Even if your files aren't recovered, your report helps authorities track variants, attribute groups, and warn future victims. In some jurisdictions (especially the US and UK) early reporting can sometimes help recall a wired ransom payment via banking partners.
Save the report number - banks, insurers, and credit bureaus will ask for it. If you operate a business, you may also have legal disclosure obligations (GDPR in the EU, state breach laws in the US) that run on a 72-hour clock.
Plan 3-2-1 backups going forward
The single best defense against ransomware is a tested backup. Use the 3-2-1 rule:
- 3 copies of your data
- 2 different storage media (e.g., internal drive + external drive)
- 1 offline / air-gapped copy (an external drive that isn't always connected)
Recommended cadence:
- Daily: cloud sync (OneDrive, Dropbox, Google Drive) - convenient, but vulnerable if the ransomware reaches the sync folder. The Version History feature is what saves you
- Weekly: external drive that you connect briefly, then disconnect - the air-gap is what protects against ransomware
- Monthly: a second external drive stored off-site (different physical location) - protects against fire, theft, flood
Test the backup at least once. Open a few files from it, check sizes match, restore one to a different folder. An untested backup isn't a backup - it's a hope.
Patch the entry point and monitor for 30 days
Most reinfections happen via the same vector that worked the first time. Until you've patched the entry point, watch for:
- Unusual disk activity, unexpected file modifications, or unfamiliar processes in Task Manager
- Unexpected reboots or new accounts you didn't create
- Defender or your antivirus turning itself off again
Common entry vectors and what to do about each:
- Phishing email with a malicious attachment - review email filters and train yourself / staff to recognise the patterns - see pcrisk's Phishing/Scam reference
- Exposed RDP with weak passwords - disable Remote Desktop from if you don't need it. If you do, put it behind a VPN and require a long password plus MFA
- Unpatched VPN appliances or public-facing apps - check the vendor's advisories page and apply the latest firmware
- Cracked / pirated software - was the most common vector for STOP/Djvu in particular. Don't run software from torrent sites
Run a Combo Cleaner scan weekly for the first month. Update Windows, browsers, and applications aggressively.
Important: Removing a ransomware infection requires a full system scan, not a manual file delete. If you're not confident with the manual procedure, run an automated scan with Combo Cleaner and Windows Defender and stop there - that combination removes the vast majority of consumer ransomware variants. Then move to Phase 4 for file recovery, or to Phase 5 if your files are unrecoverable and you need to start fresh from a clean Windows install.
Frequently Asked Questions (FAQ)
How was my computer hacked and how did hackers encrypt my files?
Ransomware is often delivered through email attachments disguised as ordinary files. Once opened, the payload runs silently in the background and encrypts the victim's data. It can also arrive via trojans, pirated software, fake software update prompts, malvertising, or unsafe download sources.
How to open ".ofx" files?
Files encrypted by One Decryptor ransomware cannot be opened in their current state. Decryption requires a tool held exclusively by the attackers.
Where should I look for free decryption tools for One Decryptor ransomware?
In the event of a ransomware infection, we recommend checking the No More Ransom project website (more information above).
I can pay you a lot of money, can you decrypt files for me?
We do not offer decryption services. In most cases, recovering encrypted files without the attackers' tools is not possible. Third-party services that claim to decrypt files are frequently scams or act as middlemen between victims and the criminals.
Will Combo Cleaner help me remove One Decryptor ransomware?
Combo Cleaner can scan the system, detect an active One Decryptor ransomware infection, and remove it. However, it cannot decrypt files that have already been encrypted; antivirus software does not have that capability.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion