
Locked_fille ransomware virus - removal and recovery options
RansomwareAlso Known As: Locked_fille virus

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What is Locked_fille ransomware?
Locked_fille is a malicious program that imitates ransomware. Malware within the ransomware classification is designed to encrypt data and make ransom demands for the decryption. However, Locked_fille has no cryptographic abilities. Although the multi-lingual ransom note ("Readme.txt") this malware creates claims that it encrypts data, Locked_fille renames it instead.
On our test machine, this fake ransomware retitled files according to this pattern - "Locked_[file_number].Locked_fille", e.g., a file named "1.jpg" appeared as "Locked_1.Locked_fille", "2.png" as "Locked_2.Locked_fille", etc.
It is exceedingly unlikely that the cyber criminals behind Locked_fille can restore the affected files. However, the data may be manually recovered if the victim knows the exact original filenames.
Screenshot of files encrypted by Locked_fille ransomware:

Locked_fille ransomware overview
Locked_fille operates by renaming victims' files and by creating a ransom note. The message in the text file is presented in the English, Russian, Portuguese, German, Spanish, French, and Turkish languages. The note falsely claims that the files modified by Locked_fille have been encrypted.
Victims are given seven days to meet the ransom demands, as after this deadline - the data will be rendered undecryptable. The payment is 300 USD in Bitcoin cryptocurrency, but if victims do not contact the attackers within three days - the sum will double (600 USD in Bitcoins).
Generally, decryption is impossible without the cyber criminals' interference, and it is always advised against meeting the ransom demands since victims often do not receive the decryption tools despite paying. While Locked_fille does not encrypt data, the latter recommendation remains true.
Since this malware does not make any attempt to take note of the original filenames - it is exceedingly unlikely that the criminals have any tools capable of recovering the files by retrieving their proper titles since they are not stored anywhere.
Victims may be able to recover their files by renaming them manually - but the process will only be successful if they have knowledge of each file's exact filename and extension. To elaborate, if the victim knows that a file appearing as "Locked_1.Locked_fille" was initially named "1.jpg" - by renaming it to "1.jpg" - the file will become usable once more.
To prevent Locked_fille from affecting more files - it must be eliminated from the operating system. However, the removal itself will not restore already modified files.
Additionally, Locked_fille attempts to delete the data in all system drives (A:\ – Z:\) except for the C:\ drive. Due to a misspelling of one executable, it does not launch properly and thus disrupts the whole action chain. Hence, the system drives remain unaffected by the deletion attempt.
In standard ransomware infections, decryption is rarely viable without the attackers' involvement, and so the only solution is recovering the encrypted files from a backup.
Therefore, as a preventative measure against permanent data loss, we highly recommend keeping data backups in multiple different locations (e.g., remote servers, unplugged storage devices, etc.).
Ransomware examples
We have analyzed thousands of ransomware-type programs; Flying Dutchman, Dkey, Solo (VoidCrypt), and Towz are merely a few examples.
This malicious software usually operates the same - encrypts data and demands payment for decryption. However, there are two significant differences in-between standard ransomware-type programs - the cryptographic algorithms they use (symmetric or asymmetric) and the ransom size.
How did ransomware infect my computer?
Locked_fille has been observed being proliferated through malicious links hosted on (potentially fake) dating and adult-oriented websites. These download links result in victims acquiring the ransomware executables. Their filenames have two extensions in order to trick users into thinking that they have downloaded a different format file such as an image (e.g., "SexyPhotos.JPG.exe", etc.).
However, other distribution methods are likely. Generally, malware is spread using phishing and social engineering techniques. It is usually disguised as or bundled with ordinary software/media. Virulent files can be executables (.exe, .run, etc.), archives (RAR, ZIP, etc.), Microsoft Office and PDF documents, JavaScript, and so on.
The most widely used malware proliferation methods include: online scams, drive-by (stealthy/deceptive) downloads, malicious attachments/links in spam emails and messages, dubious download channels (e.g., unofficial and freeware sites, Peer-to-Peer sharing networks, etc.), illegal software activation ("cracking") tools, fake updates, and malvertising.
| Name | Locked_fille virus |
| Threat Type | Ransomware, Crypto Virus, Files locker |
| Modified Files Extension | Files are renamed according to Locked_[file_number].Locked_fille pattern |
| Ransom Demanding Message | Readme.txt |
| Ransom Amount | 300/600$ in Bitcoin cryptocurrency |
| Cyber Criminal Cryptowallet Address | bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq (Bitcoin) |
| Detection Names | Avast (Win32:Malware-gen), Combo Cleaner (Trojan.GenericKD.62186295), ESET-NOD32 (Multiple Detections), Kaspersky (Trojan.BAT.KillFiles.rn), Microsoft (Trojan:Win32/Woreflint.A!cl), Full List Of Detections (VirusTotal) |
| Related Domains | nude-girlss.mywire[.]org, sexyphotos.kozow[.]com, sexy-photo[.]online |
| Symptoms | Cannot open files stored on your computer, previously functional files now have a different extension (for example, my.docx.locked). A ransom demand message is displayed on your desktop. Cyber criminals demand payment of a ransom (usually in bitcoins) to unlock your files. |
| Distribution methods | Infected email attachments (macros), torrent websites, malicious ads. |
| Damage | All files are corrupted. Additional password-stealing trojans and malware infections can be installed together with a ransomware infection. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
How to protect yourself from ransomware infections?
We strongly advise exercising caution when browsing since fraudulent/malicious content usually appears legitimate. Another recommendation is to be vigilant with incoming emails, PMs/DMs, and other messages. Therefore, the attachments and links found in suspicious/irrelevant mail must not be opened since they can be malicious and cause system infections.
We also advise downloading from official and verified sources. Additionally, all programs must be activated and updated using genuine functions/tools, as illegal activation tools ("cracks") and third-party updaters may contain malware.
It is paramount to have a reputable anti-virus installed and kept updated. This software must be used to run regular system scans and to remove detected threats. If your computer is already infected with Locked_fille, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate this ransomware.
Screenshot of Locked_fille ransomware's text file ("Readme.txt"):
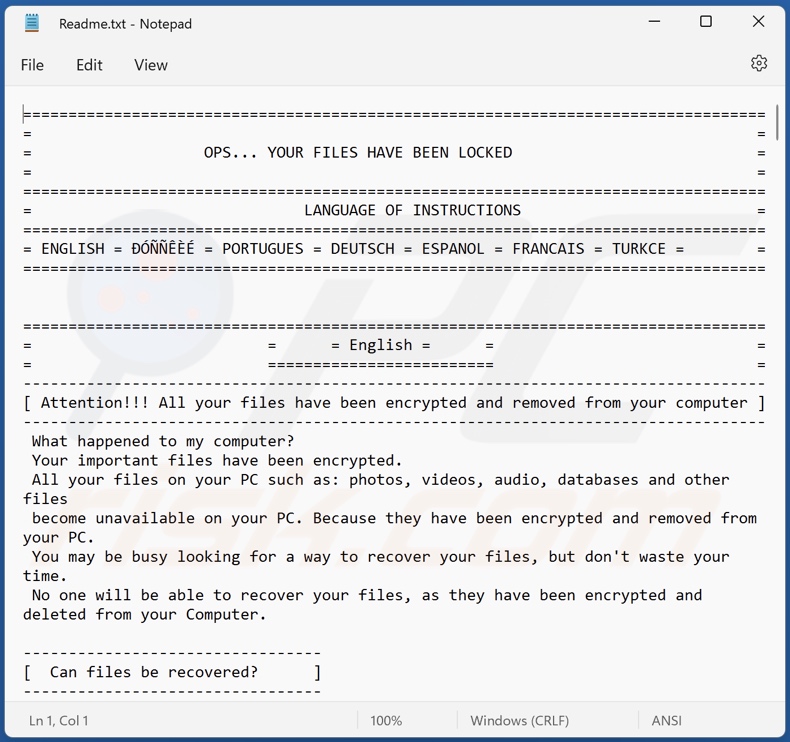
Text presented in this message:
========================================= =========================================
= =
= OPS... YOUR FILES HAVE BEEN LOCKED =
= =
========================================= =========================================
= LANGUAGE OF INSTRUCTIONS =
========================================= =========================================
= ENGLISH = РУССКИЙ = PORTUGUES = DEUTSCH = ESPANOL = FRANCAIS = TURKCE = =
========================================= =========================================
========================================= =========================================
= = = English = = =
= ========================= =
----------------------------------------------------------------------------------
[ Attention!!! All your files have been encrypted and removed from your computer ]
----------------------------------------------------------------------------------
What happened to my computer?
Your important files have been encrypted.
All your files on your PC such as: photos, videos, audio, databases and other files
become unavailable on your PC. Because they have been encrypted and removed from your PC.
You may be busy looking for a way to recover your files, but don't waste your time.
No one will be able to recover your files, as they have been encrypted and deleted from your Computer.
---------------------------------
[ Can files be recovered? ]
---------------------------------
Of course, we guarantee that you can easily and safely recover all files on your computer.
All your files have been uploaded to our server and will be returned to you after payment of $300
But you don't have much time.
If you want to decrypt and get your files back to your PC, you need to pay 300$
to bitcoin wallet with address bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
You have 3 days to pay to send the payment. After 3 days, the price will be doubled to 600$
In addition, if you do not pay within 7 days. Your files will be permanently deleted on our servers
And you will never be able to restore them again.
---------------------
[ How can I pay? ]
---------------------
Payment is accepted only in Bitcoins
You need to pay 300$ dollars to a bitcoin address bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
What is bitcoin, you can find out on the Internet, for example, through the Google search engine.
You can buy bitcoin on: cryptocurrency exchanges, through exchange services, on trading floors,
or find it on google.
-----------------------------------------------
[ What if you don't have money to pay? ]
-----------------------------------------------
You can borrow money from friends. Not a big bank loan, ask friends or relatives.
Remember that if you do not pay within 7 days, your files will be deleted forever!!!
==================================================
========================================= =========================================
= = = РУССКИЙ = = =
= ========================= =
----------------------------------------------------------------------------------
[ Внимание!!! Все ваши файлы были зашифрованы и удалены с Вашего компьютера ]
----------------------------------------------------------------------------------
Что случилось с моим компьютером?
Ваши важные файлы были зашифрованы.
Все Ваши файлы на вашем ПК такие как : фотографии, видео, аудио, базы данных и остальные файлы
стали не доступными на Вашем ПК. Поскольку они были зашифрованы и удалены с вашего ПК.
Возможно Вы будите заняты поиском способа восстановления Ваших файлов, но не тратьте свое время.
Никто Вам не сможет восстановить Ваши файлы, так как они были зашифрованы и удалены с Вашего Компьютера.
---------------------------------
[ Можно ли восстановить файлы ? ]
---------------------------------
Конечно, мы гарантируем что Вы сможете легко и безопасно восстановить все файлы на Вашем компьютере.
Все Ваши файлы были загружены на Наш сервер и будут возвращены Вам после оплаты 300$
Но у вас не так много времени.
Если Вы хотите расшифровать и вернуть Ваши файлы обратно на Ваш ПК, Вам нужно заплатить 300$
на Биткоин кошелек с адресом bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
На оплату у Вас есть 3 дня, что бы отправить платеж. После 3 дней, цена будет удвоена до 600$
Кроме того, если Вы не оплатите в течении 7 дней. Ваши файлы будут удален на наших серверах навсегда
И вы больше никогда не сможете их восстановить.
---------------------
[ Как мне оплатить? ]
---------------------
Оплата принимается только в Биткоинах
Вам нужно оплатить 300$ долларов на биткоин адрес bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
Что такое биткоин, Вы можете узнать в интернете, например через поисковик гугл.
Купить биткоин вы можете на : биржах криптовалют, через обменные сервисы, на торговых площадках,
или найти в посковике гугл.
-----------------------------------------------
[ Что делать если у вас нет денег на оплату? ]
-----------------------------------------------
Вы можете взять денег в долг у друзей. Не большой кредит в банке, попросить у знакомых или родственников.
Помните, что если Вы не оплатите в течении 7 дней, ваши файлы будут удалены навсегда!!!
========================================= =========================================
= = = Portugues = = =
= ========================= =
----------------------------------------------------------------------------------
[ Atencao!!! Todos os seus arquivos foram criptografados e removidos do seu computador ]
----------------------------------------------------------------------------------
O que aconteceu com meu computador?
Seus arquivos importantes foram criptografados.
Todos os seus arquivos em seu PC, como: fotos, videos, audio, bancos de dados e outros arquivos
ficar indisponivel no seu PC. Porque eles foram criptografados e removidos do seu PC.
Voce pode estar ocupado procurando uma maneira de recuperar seus arquivos, mas nao perca seu tempo.
Ninguem podera recuperar seus arquivos, pois eles foram criptografados e excluidos do seu computador.
---------------------------------
[ Os arquivos podem ser recuperados? ]
---------------------------------
Claro, garantimos que voce pode recuperar com facilidade e seguranca todos os arquivos em seu computador.
Todos os seus arquivos foram enviados para o nosso servidor e serao devolvidos a voce apos o pagamento de $ 300
Mas voce nao tem muito tempo.
Se voce deseja descriptografar e obter seus arquivos de volta ao seu PC, voce precisa pagar 300 $
para carteira bitcoin com endereco bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
Voce tem 3 dias para pagar para enviar o pagamento. Apos 3 dias, o preco sera dobrado para 600$
Alem disso, se voce nao pagar no prazo de 7 dias. Seus arquivos serao excluidos permanentemente em nossos servidores
E voce nunca podera restaura-los novamente.
---------------------
[ Como eu posso pagar? ]
---------------------
O pagamento e aceito apenas em Bitcoins
Voce precisa pagar 300$ dolares para um endereco bitcoin bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
O que e bitcoin, voce pode descobrir na Internet, por exemplo, atraves do mecanismo de busca do Google.
Voce pode comprar bitcoin em: exchanges de criptomoedas, atraves de servicos de cambio, em pregoes,
ou encontre no google.
-----------------------------------------------
[ E se voce nao tiver dinheiro para pagar? ]
-----------------------------------------------
Voce pode pedir dinheiro emprestado a amigos. Nao e um grande emprestimo bancario, pergunte a amigos ou parentes.
Lembre-se que se voce nao pagar em 7 dias, seus arquivos serao deletados para sempre!!!
========================================= =========================================
= = = Deutsch = = =
= ========================= =
----------------------------------------------------------------------------------
[ Aufmerksamkeit!!! Alle Ihre Dateien wurden verschlusselt und von Ihrem Computer entfernt ]
----------------------------------------------------------------------------------
Was ist mit meinem Computer passiert?
Ihre wichtigen Dateien wurden verschlusselt.
Alle Ihre Dateien auf Ihrem PC wie: Fotos, Videos, Audio, Datenbanken und andere Dateien
auf Ihrem PC nicht mehr verfugbar. Weil sie verschlusselt und von Ihrem PC entfernt wurden.
Moglicherweise sind Sie damit beschaftigt, nach einer Moglichkeit zu suchen, Ihre Dateien wiederherzustellen, aber verschwenden Sie nicht Ihre Zeit.
Niemand kann Ihre Dateien wiederherstellen, da sie verschlusselt und von Ihrem Computer geloscht wurden.
---------------------------------
[ Konnen Dateien wiederhergestellt werden? ]
---------------------------------Naturlich garantieren wir, dass Sie alle Dateien auf Ihrem Computer einfach und sicher wiederherstellen konnen.
Alle Ihre Dateien wurden auf unseren Server hochgeladen und werden Ihnen nach Zahlung von 300 $ zuruckgeschickt
Aber Sie haben nicht viel Zeit.
Wenn Sie Ihre Dateien entschlusseln und zuruck auf Ihren PC bringen mochten, mussen Sie 300 $ bezahlen
zu bitcoin wallet mit adresse bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
Sie haben 3 Tage Zeit, um die Zahlung zu senden. Nach 3 Tagen verdoppelt sich der Preis auf 600$
Au?erdem, wenn Sie nicht innerhalb von 7 Tagen bezahlen. Ihre Dateien werden dauerhaft auf unseren Servern geloscht
Und Sie werden sie nie wieder wiederherstellen konnen.
---------------------
[ Wie kann ich bezahlen? ]
---------------------
Die Zahlung wird nur in Bitcoins akzeptiert
Sie mussen 300 $ Dollar an eine Bitcoin-Adresse zahlen bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
Was Bitcoin ist, konnen Sie im Internet zum Beispiel uber die Google-Suchmaschine herausfinden.
Sie konnen Bitcoin kaufen an: Kryptowahrungsborsen, uber Borsendienste, auf Borsenparketts,
oder bei google suchen.
-----------------------------------------------
[ Was ist, wenn Sie kein Geld zum Bezahlen haben? ]
-----------------------------------------------
Sie konnen Geld von Freunden leihen. Kein gro?er Bankkredit, fragen Sie Freunde oder Verwandte.
Denken Sie daran, dass Ihre Dateien fur immer geloscht werden, wenn Sie nicht innerhalb von 7 Tagen bezahlen!!!
========================================= =========================================
= = = espanol= = =
= ========================= =
----------------------------------------------------------------------------------
[ ???Atencion!!! Todos sus archivos han sido encriptados y eliminados de su computadora ]
----------------------------------------------------------------------------------
?Que le paso a mi computadora?
Sus archivos importantes han sido encriptados.
Todos sus archivos en su PC como: fotos, videos, audio, bases de datos y otros archivos
deje de estar disponible en su PC. Porque han sido encriptados y eliminados de su PC.
Puede estar ocupado buscando una forma de recuperar sus archivos, pero no pierda el tiempo.
Nadie podra recuperar sus archivos, ya que han sido encriptados y eliminados de su computadora.
---------------------------------
[ ?Se pueden recuperar los archivos?]
---------------------------------
Por supuesto, le garantizamos que puede recuperar todos los archivos de su computadora de manera facil y segura.
Todos sus archivos han sido subidos a nuestro servidor y le seran devueltos despues del pago de $300
Pero no tienes mucho tiempo.
Si desea descifrar y recuperar sus archivos en su PC, debe pagar 300 $
a billetera bitcoin con direccion bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
Tienes 3 dias para pagar para enviar el pago. Despues de 3 dias, el precio se duplicara a 600 $
Ademas, si no paga dentro de los 7 dias. Sus archivos seran eliminados permanentemente en nuestros servidores
Y nunca podras restaurarlos de nuevo.
---------------------
[ ?Como puedo pagar? ]
---------------------
El pago se acepta solo en Bitcoins
Debe pagar 300 $ dolares a una direccion de bitcoin bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
Que es bitcoin, puedes averiguarlo en Internet, por ejemplo, a traves del buscador de Google.
Puede comprar bitcoins en: intercambios de criptomonedas, a traves de servicios de intercambio, en pisos comerciales,
o buscarlo en google.
-----------------------------------------------
[ ?Que pasa si no tienes dinero para pagar? ]
-----------------------------------------------
Puedes pedir dinero prestado a tus amigos. No es un gran prestamo bancario, pregunte a amigos o familiares.
?Recuerde que si no paga dentro de los 7 dias, sus archivos se eliminaran para siempre!
========================================= =========================================
= = = francais= = =
= ========================= =
----------------------------------------------------------------------------------
[ Attention!!! Tous vos fichiers ont ete cryptes et supprimes de votre ordinateur ]
----------------------------------------------------------------------------------
Qu'est-il arrive a mon ordinateur ?
Vos fichiers importants ont ete cryptes.
Tous vos fichiers sur votre PC tels que : photos, videos, audio, bases de donnees et autres fichiers
deviennent indisponibles sur votre PC. Parce qu'ils ont ete cryptes et supprimes de votre PC.
Vous etes peut-etre occupe a chercher un moyen de recuperer vos fichiers, mais ne perdez pas votre temps.
Personne ne pourra recuperer vos fichiers, car ils ont ete cryptes et supprimes de votre ordinateur.
---------------------------------
[ Les fichiers peuvent-ils etre recuperes ? ]
---------------------------------
Bien sur, nous garantissons que vous pouvez facilement et en toute securite recuperer tous les fichiers sur votre ordinateur.
Tous vos fichiers ont ete telecharges sur notre serveur et vous seront retournes apres paiement de 300 $
Mais vous n'avez pas beaucoup de temps.
Si vous voulez decrypter et recuperer vos fichiers sur votre PC, vous devez payer 300 $
au portefeuille bitcoin avec adresse bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
Vous avez 3 jours pour payer pour envoyer le paiement. Apres 3 jours, le prix sera double a 600$
De plus, si vous ne payez pas dans les 7 jours. Vos fichiers seront definitivement supprimes sur nos serveurs
Et vous ne pourrez plus jamais les restaurer.
---------------------
[ Comment puis-je payer? ]
---------------------
Le paiement est accepte uniquement en Bitcoins
Vous devez payer 300$ dollars a une adresse bitcoin bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
Qu'est-ce que le bitcoin, vous pouvez le decouvrir sur Internet, par exemple via le moteur de recherche Google.
Vous pouvez acheter des bitcoins sur : les echanges de crypto-monnaie, via les services d'echange, dans les salles de marche,
ou le trouver sur google.
-----------------------------------------------
[ Et si vous n'avez pas d'argent pour payer ? ]
-----------------------------------------------
Vous pouvez emprunter de l'argent a des amis. Pas un gros pret bancaire, demandez a des amis ou a des proches.
N'oubliez pas que si vous ne payez pas dans les 7 jours, vos fichiers seront definitivement supprimes !!!
========================================= =========================================
= = = Turk Dili= = =
= ========================= =
----------------------------------------------------------------------------------
[ Dikkat!!! Tum dosyalar?n?z sifrelendi ve bilgisayar?n?zdan kald?r?ld? ]
----------------------------------------------------------------------------------
Bilgisayar?ma ne oldu?
Onemli dosyalar?n?z sifrelendi.
Fotograflar, videolar, ses dosyalar?, veritabanlar? ve diger dosyalar gibi bilgisayar?n?zdaki tum dosyalar?n?z
PC'nizde kullan?lamaz hale gelir. Cunku bunlar sifrelenmis ve bilgisayar?n?zdan kald?r?lm?st?r.
Dosyalar?n?z? kurtarman?n bir yolunu aramakla mesgul olabilirsiniz, ancak zaman?n?z? bosa harcamay?n.
Dosyalar?n?z sifrelenip Bilgisayar?n?zdan silindigi icin hic kimse dosyalar?n?z? kurtaramaz.
---------------------------------
[ Dosyalar kurtar?labilir mi?]
---------------------------------
Elbette bilgisayar?n?zdaki tum dosyalar? kolayca ve guvenle kurtarabileceginizi garanti ediyoruz.
Tum dosyalar?n?z sunucumuza yuklendi ve 300$ odeme yap?ld?ktan sonra size iade edilecektir.
Ama fazla vaktin yok.
Sifreyi cozmek ve dosyalar?n?z? bilgisayar?n?za geri almak istiyorsan?z, 300$ odemeniz gerekir.
adresli bitcoin cuzdan?na bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
Odemeyi gondermek icin odemeniz gereken 3 gununuz var. 3 gun sonra fiyat iki kat?na c?kar ve 600$'a c?kar.
Ayr?ca 7 gun icinde odemezseniz. Dosyalar?n?z sunucular?m?zda kal?c? olarak silinecek
Ve onlar? bir daha asla geri yukleyemezsiniz.
---------------------
[ Nas?l odeyebilirim? ]
---------------------
Odeme sadece Bitcoins ile kabul edilir
Bir bitcoin adresine 300$ odemeniz gerekiyor bc1qlv29rvquxj9p4sd8lcecmvqldmharvu95gguaq
Bitcoin nedir, ornegin Google arama motoru arac?l?g?yla Internette ogrenebilirsiniz.
Bitcoin sat?n alabilirsiniz: kripto para borsalar?, takas hizmetleri arac?l?g?yla, ticaret katlar?nda,
veya google'da bulun.
-----------------------------------------------
[ Ya odeyecek paran yoksa? ]
-----------------------------------------------
Arkadaslardan borc para alabilirsiniz. Buyuk bir banka kredisi degil, arkadaslar?n?za veya akrabalar?n?za sorun.
Unutmay?n ki 7 gun icinde odeme yapmazsan?z dosyalar?n?z sonsuza kadar silinecektir!!!
Locked_fille ransomware removal:
Instant automatic malware removal:
Manual threat removal might be a lengthy and complicated process that requires advanced IT skills. Combo Cleaner is a professional automatic malware removal tool that is recommended to get rid of malware. Download it by clicking the button below:
DOWNLOAD Combo CleanerBy downloading any software listed on this website you agree to our Privacy Policy and Terms of Use. To use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
Removal and file recovery procedure
If your files are encrypted with a new extension and a ransom note has appeared, you've been hit by ransomware. Don't pay. The procedure below works in order: contain the infection, identify the variant, remove the ransomware itself (so anything you restore doesn't get re-encrypted), and try to recover files using free decryption tools, Windows Volume Shadow Copies, or backups. Run a full system scan with Combo Cleaner to remove the infection - then move on to file recovery.
Common ransomware behaviors
VisibleEncrypts your files and renames them
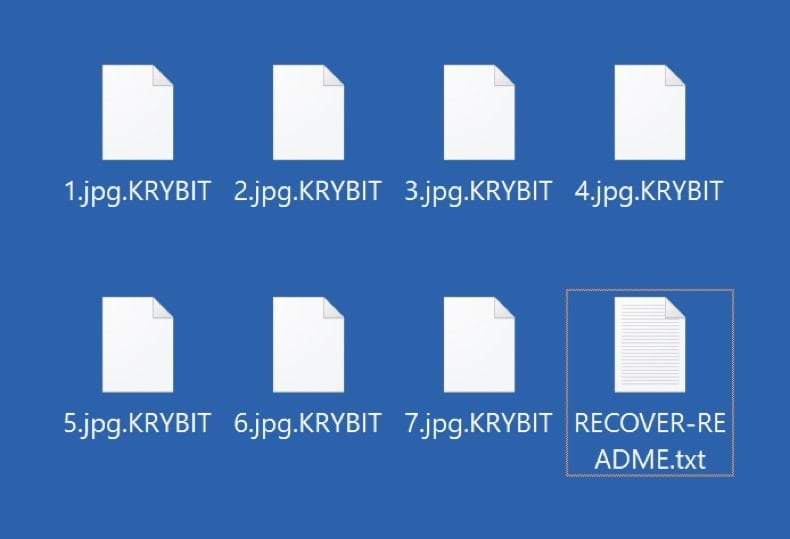
The ransomware reads each file, encrypts the contents with the attacker's public key, and writes the encrypted bytes back to disk. Most variants also rename the file by appending a new extension - .net, .locked, .crypt, .lockbit, .djvu, etc. Without the matching private key, the encrypted files cannot be opened normally. Recovery depends on a free decryption tool, a recoverable Volume Shadow Copy, or a clean backup.
VisibleDrops a ransom note in every encrypted folder
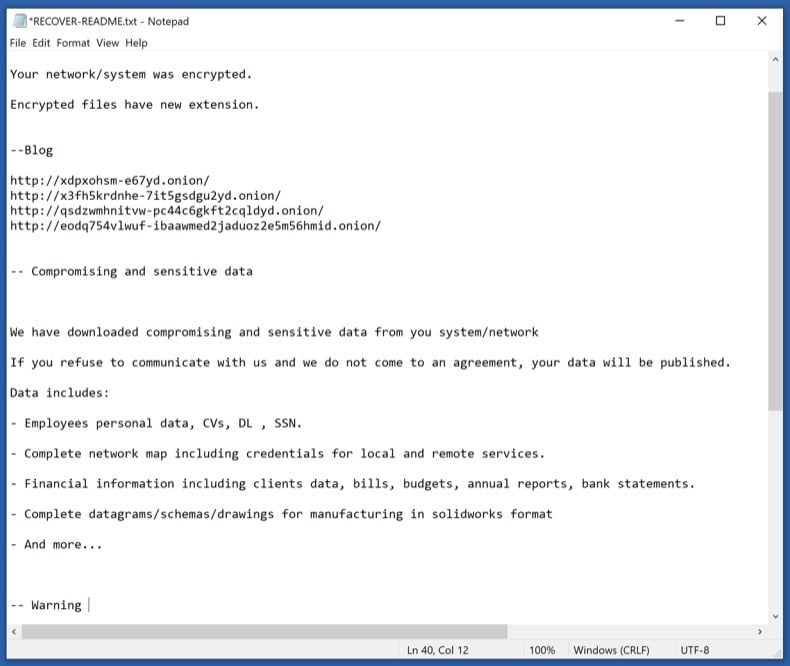
A text or HTML file (usually named HOW_TO_DECRYPT.txt, README.txt, _readme.txt, or similar) is placed in every folder that contains encrypted files. The note explains the situation, lists a payment amount in cryptocurrency, gives a deadline, and provides a contact email or .onion site. Save the note - don't delete it. Its exact wording, the email address, and the bitcoin wallet are how you identify the variant in the next phase.
VisibleReplaces the desktop wallpaper
Many ransomware variants change the Windows wallpaper to a black or red image with the ransom message and instructions. The wallpaper is just a visual scare tactic - it doesn't add any actual capability and reverts to normal once the ransomware is removed. Photograph it before removal in case the contact details are useful for variant identification or for reporting to authorities.
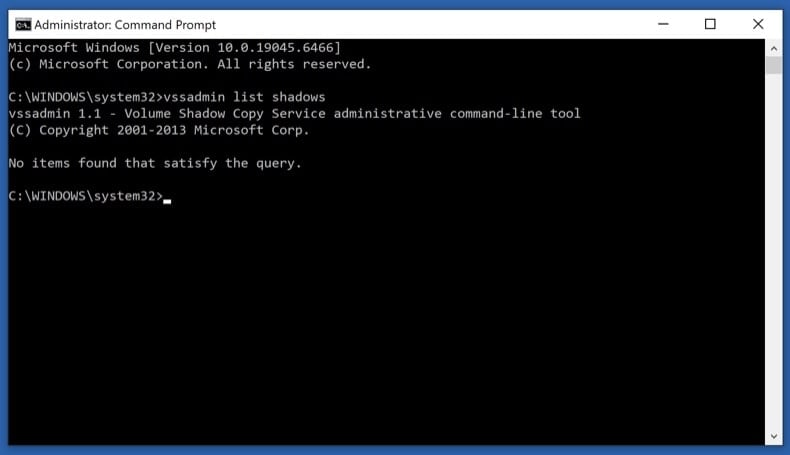
HiddenDeletes Volume Shadow Copies
One of the first things modern ransomware does after launching is run vssadmin delete shadows /all /quiet to wipe Windows' built-in Volume Shadow Copies - the snapshots that Previous Versions and System Restore rely on. Some ransomware doesn't fully succeed (especially on systems where the user lacks full admin rights), leaving partial shadow copies recoverable. Phase 4 step 11 covers how to check what survived.
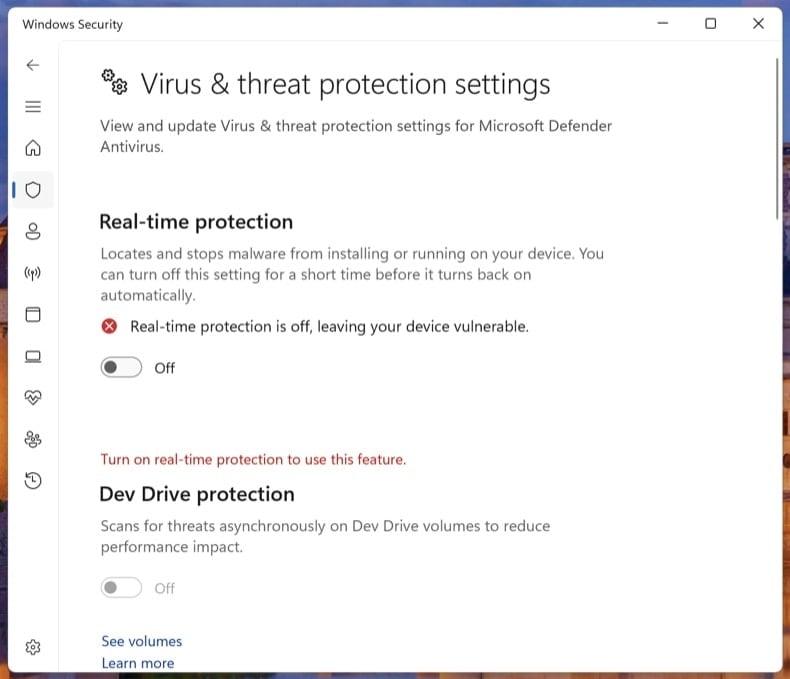
HiddenDisables Windows Defender and other security tools
Before encrypting, the ransomware tries to silence anything that could alert you or block it - Windows Defender real-time protection, third-party antivirus services, backup agents (Veeam, Acronis), and sometimes the Windows Event Log service. It often modifies Group Policy or registry keys to keep these off after reboot. Phase 3 step 9 explicitly turns Tamper Protection back on so the next ransomware attempt can't repeat the trick.
HiddenSpreads laterally to other PCs on the network
Network-aware ransomware (LockBit, Conti, BlackCat, Akira families) doesn't stop at the first machine. It scans for SMB shares, mapped drives, and other PCs on the same network, then encrypts whatever it can reach. On Windows domains, a single compromised user with admin rights can lead to all-domain encryption. This is why Phase 1 step 2 disconnects the network as the very first action - it stops the spread immediately.
HiddenSteals data before encrypting (double extortion)
Modern ransomware (LockBit, BlackCat / ALPHV, Akira, Cl0p, Royal) almost always exfiltrates data before encrypting. The attacker then runs a "double extortion" play: pay the ransom for decryption, plus pay again to prevent the stolen data from being leaked on the group's leak site. Paying the first ransom does not get the leaked data back - assume that anything the ransomware could read was uploaded. This is one more reason not to pay: the data is already out.
Don't pay the ransom
Paying the ransom does not guarantee you'll get your files back. Major ransomware response studies consistently show that a meaningful percentage of paying victims either receive a non-working decryptor, only partial decryption, or no decryptor at all. Beyond that:
- Paying confirms you as a willing target - re-attack rates within 12 months are high
- Several ransomware groups have been sanctioned (US OFAC, UK OFSI). Paying these groups may be illegal under sanctions law in your country
- The ransom funds the next attack - on you or someone else
- Modern ransomware almost always exfiltrates data first, so paying doesn't get the leaked data back. Assume anything the malware could read was uploaded
- Decryptors, even when they work, often leave files corrupted because the encryption itself was buggy or rushed
The path below tries every legal, free recovery option first. Pay only as an absolute last resort, after consulting a lawyer and your country's cyber crime authority.
Disconnect from the network and log out of cloud storage
Pull the Ethernet cable and turn off Wi-Fi on the affected PC. If multiple computers share the network, do the same on every machine you suspect could be affected, including any servers and NAS units.
Then sign out of cloud storage clients (OneDrive, Dropbox, Google Drive, iCloud) from their app settings. If you can, pause the sync. Some ransomware uses the running sync client to push encrypted versions over your clean cloud copies.
Modern ransomware spreads laterally across SMB shares, mapped drives, RDP, and reachable network neighbors. Disconnecting stops the spread the moment you do it. Logging out of cloud sync clients prevents the ransomware from encrypting the cloud copies of your files via the sync API.
Unplug external drives and USB storage
Safely eject any external drives, USB sticks, SD cards, and network-attached storage shares - then unplug them. If a drive was connected when the ransomware ran, the files on it may already be encrypted, but unplugging stops further damage.
Critically: don't reconnect any drive (including your most recent backup) to this PC until the ransomware is removed in Phase 3. Reconnecting an external backup to an actively-infected PC is the most common way that backup gets encrypted too.
Save the ransom note and a sample encrypted file
Copy the ransom note and one small encrypted file (under 1 MB) to a USB stick, or photograph the note with your phone. You'll need both for the variant identification step.
The ransom note is usually one of:
- A
.txtfile in every encrypted folder (typicallyHOW_TO_DECRYPT.txt,README.txt, or_readme.txt) - An
.htmlfile with the same purpose - A changed desktop wallpaper - photograph it
- A lock-screen interrupt that runs at startup - rarer
Don't delete the note. Variant identification depends on its exact wording, the contact email, and the bitcoin wallet address. The note is also evidence if you report to authorities.
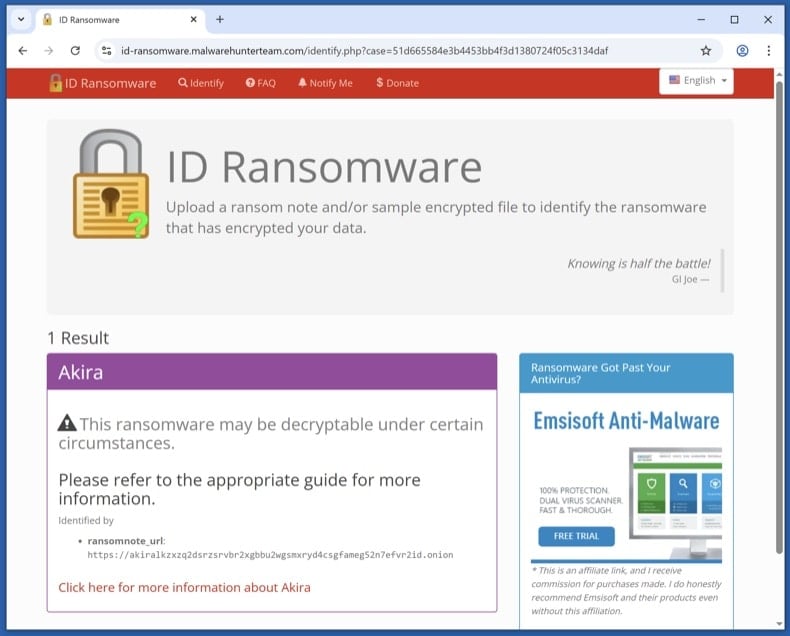
Identify the variant with ID Ransomware
From a clean device (your phone is fine, or another PC that wasn't on the affected network), visit id-ransomware.malwarehunterteam.com. Upload the ransom note and the sample encrypted file. The site identifies the variant family and tells you whether a free decryptor exists.
ID Ransomware is run by the Malware Hunter Team. Files you upload are kept private - they're used for analysis, not published. If you're concerned about uploading data anyway, you can paste the contact email and bitcoin wallet from the note - those are often enough for identification.
The ransomware itself must be removed before any file recovery. If it's still active, anything you restore in Phase 4 gets re-encrypted within minutes.
Boot to Safe Mode with Networking and download the scanners
Safe Mode loads only the minimal Windows drivers, which prevents most ransomware from auto-running while you set up the scanners.
Windows 11: open , click Restart now next to Advanced startup. After the restart, click , then press 5 or F5.
Windows 10: click the Windows logo, hold Shift, click the Power icon and choose Restart. From the Choose-an-option screen, click , then press F5.
Once Safe Mode has loaded, turn Wi-Fi back on and download Combo Cleaner (used in step 8) and Microsoft Safety Scanner (used in step 9). Save both installers to your Desktop, then disconnect Wi-Fi again before scanning.
Run Microsoft Defender Offline
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts into a stripped-down environment and scans the disk before Windows fully loads.
Some ransomware variants drop bootkit components or kernel hooks that hide from any scanner running on the same Windows session that's already infected. A pre-boot offline scan sees the disk before the malware can load itself.
VB100 certified. Includes anti-trojan, registry/persistence scanning, and anti-spyware in one pass. The 7-day free trial is available.
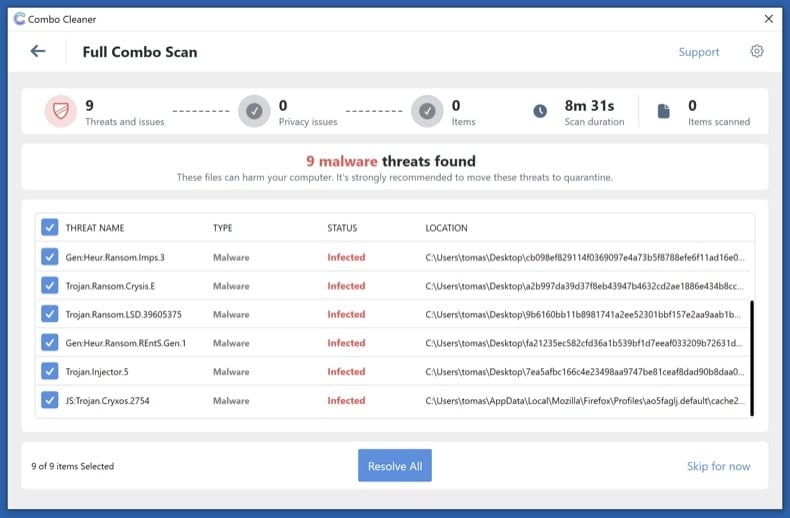
Download Combo CleanerRun a full Combo Cleaner scan
Run the installer you downloaded in step 6 and start a full system scan (not the quick scan). Let it complete, review what it detected, and apply the recommended actions. Combo Cleaner quarantines the ransomware executable and the registry / scheduled-task entries that re-launch it on reboot.
Run Microsoft Safety Scanner and re-enable Defender
Run Microsoft Safety Scanner (MSERT.exe) as a second-opinion full scan. The binary expires every 10 days so the copy you downloaded has the latest signatures.
Once it finishes, open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all on. Many ransomware variants disable Defender during the attack - this is where you switch it back on so the next attempt can't repeat the trick.
Different scanning engines catch different threats. Running an additional Microsoft scan after Combo Cleaner is the most underused verification step in malware removal - and free.
Try the steps in order. The first decryptor that works ends the recovery process - no need to do all four.
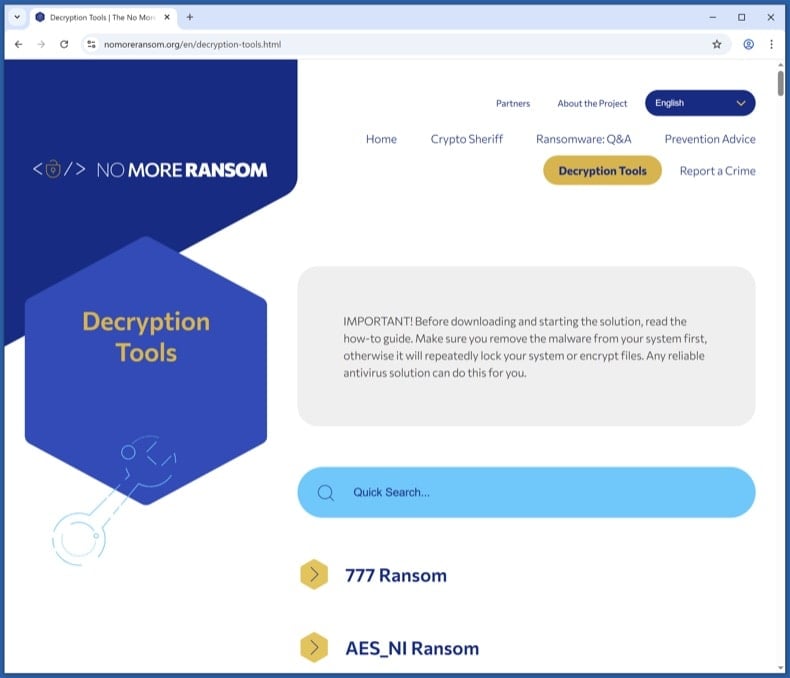
Check the No More Ransom Project for a free decryptor
Visit nomoreransom.org and search the Decryption Tools list for the variant name returned by ID Ransomware. The project is run by Europol, the Dutch Police, and security vendors - everything listed is legitimate and free.
If a decryptor exists, download it onto a clean PC, copy it across, and follow its instructions exactly. Decryptors usually want you to point them at a sample encrypted file plus its known unencrypted version (sometimes any image you previously had a backup of works).
Free decryptors exist for parts of the STOP/Djvu, GandCrab, REvil, Avaddon, Conti and Hive families, among others. Most modern variants don't have public decryptors - if yours isn't listed, that's expected; move to the next step.
Try Windows Volume Shadow Copies
Windows automatically creates Volume Shadow Copies of files when System Restore points are made or scheduled backups run. Most ransomware tries to wipe these (vssadmin delete shadows /all /quiet), but the deletion sometimes fails partially - especially if the running user doesn't have full admin rights. When it does fail, snapshots survive that contain pre-encryption versions of your files.
First, check what's there. Open Command Prompt as Administrator and run:
vssadmin list shadows
If you see entries listed, shadow copies survived. To restore from them:
- Built-in: right-click any folder → Properties → Previous Versions tab. Pick a snapshot dated before the infection and restore.
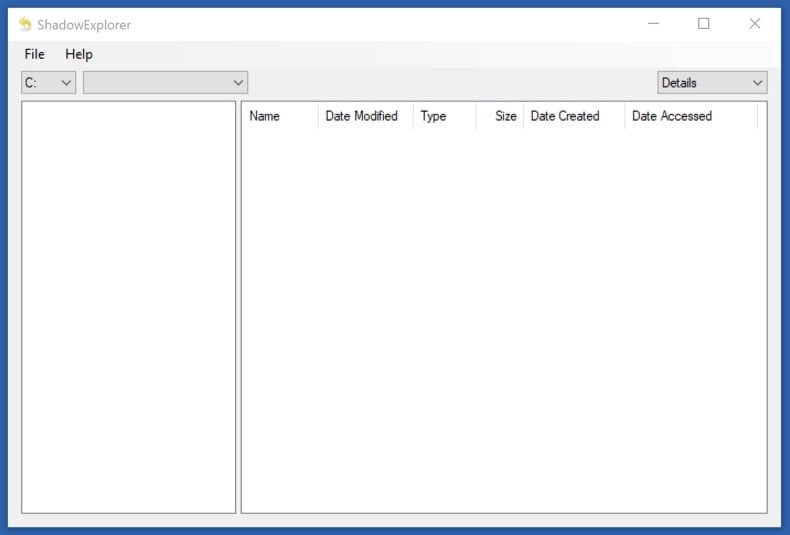
- Better tool for browsing: install Shadow Explorer (free). It shows all snapshots as a normal file tree and lets you copy out only the files you want.
Shadow Copies recover the original files exactly, with no risk of decryption errors. If they survived, this is faster and cleaner than running a decryptor on the encrypted set.
Restore from cloud or external backup
If you have a backup that pre-dates the infection, this is the cleanest recovery available. Important precautions:
- Don't reconnect a backup drive until Phase 3 is complete. If the ransomware is still active, plugging in the backup encrypts it too.
- For cloud backups (OneDrive, Dropbox, Google Drive, iCloud), use the Version History feature to roll individual files back to pre-encryption versions.
- OneDrive specifically has a "Restore your OneDrive" feature: if it detected mass file changes, you can roll back the entire account up to 30 days. Sign in at OneDrive on the web, click the Settings gear, and choose Restore your OneDrive. Microsoft 365 subscribers also get ransomware detection alerts; non-subscribers get one free recovery.
- Verify the restored files open correctly before you delete the encrypted set. Test a few documents, photos, and any database / project files.
Try Recuva as a last-resort recovery
Recuva is a long shot, not a primary recovery tool. Most modern ransomware encrypts files in place - it reads the original, encrypts the data, and writes the encrypted bytes back to the same disk location. In that case, the original isn't deleted, just rewritten - and Recuva has nothing to find.
But for older or simpler variants that deleted originals before creating encrypted copies (rather than encrypting in place), Recuva can sometimes pull the originals from unallocated disk space. Worth trying as a last resort, especially before you use the disk much further.
If you try it:
- Stop using the disk as much as possible - every disk write reduces recovery odds
- Run Recuva from a USB stick, not from the affected disk
- Use Deep Scan mode (slower but the only mode worth running for this scenario)
Don't skip the steps above expecting Recuva to bail you out. It works in maybe 5-20% of cases, depending on the variant and how soon you try.
Report the attack to authorities
Even if your files aren't recovered, your report helps authorities track variants, attribute groups, and warn future victims. In some jurisdictions (especially the US and UK) early reporting can sometimes help recall a wired ransom payment via banking partners.
Save the report number - banks, insurers, and credit bureaus will ask for it. If you operate a business, you may also have legal disclosure obligations (GDPR in the EU, state breach laws in the US) that run on a 72-hour clock.
Plan 3-2-1 backups going forward
The single best defense against ransomware is a tested backup. Use the 3-2-1 rule:
- 3 copies of your data
- 2 different storage media (e.g., internal drive + external drive)
- 1 offline / air-gapped copy (an external drive that isn't always connected)
Recommended cadence:
- Daily: cloud sync (OneDrive, Dropbox, Google Drive) - convenient, but vulnerable if the ransomware reaches the sync folder. The Version History feature is what saves you
- Weekly: external drive that you connect briefly, then disconnect - the air-gap is what protects against ransomware
- Monthly: a second external drive stored off-site (different physical location) - protects against fire, theft, flood
Test the backup at least once. Open a few files from it, check sizes match, restore one to a different folder. An untested backup isn't a backup - it's a hope.
Patch the entry point and monitor for 30 days
Most reinfections happen via the same vector that worked the first time. Until you've patched the entry point, watch for:
- Unusual disk activity, unexpected file modifications, or unfamiliar processes in Task Manager
- Unexpected reboots or new accounts you didn't create
- Defender or your antivirus turning itself off again
Common entry vectors and what to do about each:
- Phishing email with a malicious attachment - review email filters and train yourself / staff to recognise the patterns - see pcrisk's Phishing/Scam reference
- Exposed RDP with weak passwords - disable Remote Desktop from if you don't need it. If you do, put it behind a VPN and require a long password plus MFA
- Unpatched VPN appliances or public-facing apps - check the vendor's advisories page and apply the latest firmware
- Cracked / pirated software - was the most common vector for STOP/Djvu in particular. Don't run software from torrent sites
Run a Combo Cleaner scan weekly for the first month. Update Windows, browsers, and applications aggressively.
Important: Removing a ransomware infection requires a full system scan, not a manual file delete. If you're not confident with the manual procedure, run an automated scan with Combo Cleaner and Windows Defender and stop there - that combination removes the vast majority of consumer ransomware variants. Then move to Phase 4 for file recovery, or to Phase 5 if your files are unrecoverable and you need to start fresh from a clean Windows install.
Frequently Asked Questions (FAQ)
How was my computer hacked and how did hackers encrypt my files?
Ransomware and other malware executables are often opened by the victims themselves, as these files are usually presented as or bundled with ordinary software/media. Locked_fille has been observed being distributed via malicious files promoted by adult-themed websites. Other popular malware distribution methods include: drive-by downloads, spam emails and messages, online scams, untrustworthy download sources (e.g., unofficial and freeware sites, P2P sharing networks, etc.), illegal program activation tools ("cracks"), fake updates, and malvertising.
How to open the files affected by Locked_fille?
The files renamed by Locked_fille cannot be opened unless their original titles are restored. Hence, if the victim knows a file's exact filename and extension - by manually renaming it - they will restore its usability. Otherwise, the data can only be recovered from a backup (if one is available).
Will Combo Cleaner help me remove Locked_fille ransomware?
Yes, Combo Cleaner will scan your device and eliminate detected ransomware infections. Note that while using an anti-virus is the first step in ransomware recovery, security programs are incapable of recovering encrypted or corrupted files.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion