

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What is Dharma ransomware?
Dharma is a ransomware-type program, a type of malware designed to encrypt data and make ransom demands for the decryption. It is based on Crysis and uses asymmetric cryptography for encryption. Throughout the years, Dharma has evolved into a ransomware family that includes a multitude of versions. Since 2020 Dharma's developers have begun offering it as RaaS (Ransomware-as-a-Service), thereby making it accessible to countless threat actors.
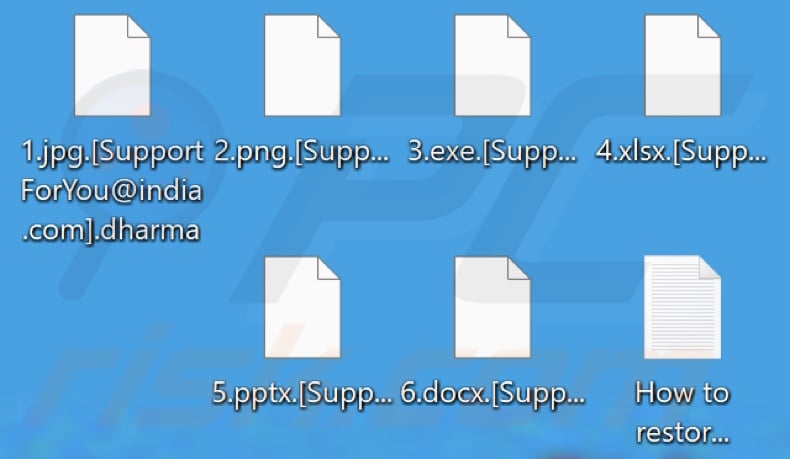
Typically, ransomware-type programs rename encrypted files, and Dharma is not an exception. Originally, this ransomware appended files with a ".dharma" extension (e.g., "1.jpg" modified into "1.jpg.dharma", etc.). However, how the filenames are altered depends on the program's variant.
The renaming patterns include appending original titles with: a unique ID, the cyber criminals' contact information (typically, email), and an extension, or just the contact info and extension, or only an extension. For example, a file named "1.jpg" could appear as "1.jpg.id-9ECFA84E.[king2022@msgden.com].gnik", "1.jpg.[Beamsell@qq.com].bip", "1.jpg.KICK", or a myriad of other variations (list of examples).
Once the encryption is complete, Dharma creates ransom notes (filename list), and some variants also change the desktop wallpapers. The messages and wallpapers differ depending on the ransomware's version. However, since Dharma's update in 2017, it consistently creates the same pop-up window and text file titled "How to restore data.txt".
Screenshot of files encrypted by Dharma ransomware:
Dharma ransomware overview
As mentioned in the introduction, the text presented within Dharma's ransom notes differs depending on the program's variant. However, the pop-ups displayed and text files dropped since 2017 are more consistent. Typically, the message in the text files is brief and urges victims to contact the attackers' to restore their data.
The pop-ups tend to provide more information regarding the infection. These notes can state that the file decryption will require paying a ransom and the desired currency (most often, Bitcoin cryptocurrency). The pop-up windows can also include various warnings against action that may lead to increased financial losses and permanent data loss.
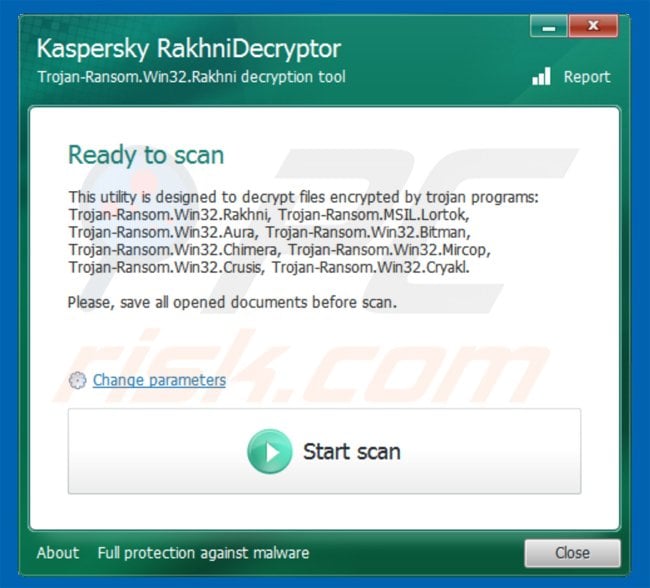
Based on our extensive experience researching ransomware infections, we can conclude that decryption is usually impossible without the cyber criminals' interference. It is only viable if the ransomware-type program is severely flawed. While older Dharma versions can be decrypted by using Kaspersky's Rakhni decryptor (more information), this tool is incapable of restoring files affected by later variants.
It must be emphasized that despite meeting the ransom demands - victims often do not receive the promised decryption tools. Therefore, we advise against it, as data recovery is not guaranteed, and paying also supports this illegal activity.
To prevent ransomware from encrypting more data, it must be removed from the operating system. Unfortunately, removal will not restore already compromised files. The sole solution is recovering them from a backup, if one was created prior and is stored elsewhere.
To avoid permanent data loss, we highly recommend keeping backups in multiple different locations (e.g., remote servers, unplugged storage devices, etc.).
Ransomware examples
We have analyzed thousands of ransomware samples; Gnik, K1ng, Zxcvb, and Watch are some of the newest programs belonging to the Dharma family, while 62IX, BlackBit, Polis - are a few of our latest ransomware finds in general.
Malicious software within this classification operates practically the same, i.e., encrypts data and demands payment for decryption. However, ransomware-type programs have two significant differences in-between - the cryptographic algorithms they use (symmetric or asymmetric) and the ransom size.
How did ransomware infect my computer?
Ransomware and other malware are primarily distributed using phishing and social engineering tactics. Malicious programs are usually presented as or bundled with ordinary software/media.
Virulent files can be executables (.exe, run, etc.), archives (RAR, ZIP, etc.), Microsoft Office and PDF documents, JavaScript, and so on. Once a malicious file is executed, run, or otherwise opened - the infection chain is triggered.
The most widespread distribution techniques include: drive-by (stealthy/deceptive) downloads, online scams, malicious attachments/links in spam emails and messages, dubious download channels (e.g., freeware and third-party sites, Peer-to-Peer sharing networks, etc.), illegal software activation tools ("cracks"), fake updates, and malvertising.
| Name | Dharma virus |
| Threat Type | Ransomware, Crypto Virus, Files locker |
| Encrypted Files Extension | Original extension - ".dharma"; however, they vary depending on the ransomware's variant, e.g., ".KICK", ".crash", ".harma", ".PLUT", ".wal", ".txt", ".FREDD", "[Lockhelp@qq.com].Gate", ".LDPR", ".stun", ".back", ".adobe", ".boost", ".[paydecryption@qq.com].brrr", "[symabkp@protonmail.com].bip", ".[paymentbtc@firemail.cc].cmb", ".[combo@tutanota.de].combo", ".[Beamsell@qq.com].bip", ".[needyoulove@cock.li].java", ".[pain@onefinedstay.com].java", ".arrow", ".java", ".arena", ".[black.mirror@qq.com].cesar", ".[Gladius_Adeptus@aol.com].onion", ".[Satan-Stn@bitmessage.ch].wallet", ".[aligi@zakazaka.group].wallet", ".[moneymaker2@india.com].wallet", ".[legionfromheaven@india.com].wallet", ".[destroed_total@aol.com].wallet", ".[stopper@india.com].wallet", ".[fire.show@aol.com].wallet", "[mkgoro@india.com].xtbl", ".[bitcoin143@india.com].dharma", ".[Mkliukang@india.com].wallet", ".[lavandos@dr.com].wallet", ".[mollymcgee@india.com].dharma", etc. |
| Ransom Demanding Message | Ransom notes vary depending on the variant, e.g., text presented in the pop-up window, desktop wallpaper, "How to restore data.txt", "FILES ENCRYPTED.txt", "README.txt", "Document.txt.[amagnus@india.com].zzzzz", etc. |
| Free Decryptor Available? | Partial (more information below) |
| Cyber Criminal Contact | Varies depending on the variant. |
| Detection Names | Avast (Win32:Malware-gen), Combo Cleaner (Dropped:Generic.Ransom.Crysis.222627A1), ESET-NOD32 (A Variant Of Win32/Filecoder.Crysis.K), Kaspersky (HEUR:Trojan.Win32.Generic), Microsoft (Ransom:Win32/Crysis.A!hoa), Full List Of Detections (VirusTotal) |
| Rogue Process Name | Disguised as "taskhost.exe" (process name may vary) |
| Symptoms | Cannot open files stored on your computer, previously functional files now have a different extension (for example, my.docx.locked). A ransom demand message is displayed on your desktop. Cyber criminals demand payment of a ransom (usually in bitcoins) to unlock your files. |
| Distribution methods | Infected email attachments (macros), torrent websites, malicious ads. |
| Damage | All files are encrypted and cannot be opened without paying a ransom. Additional password-stealing trojans and malware infections can be installed together with a ransomware infection. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
How to protect yourself from ransomware infections?
We highly recommend downloading only from official and verified sources. Furthermore, software must be activated and updated using legitimate functions/tools, as illegal activation ("cracking") tools and fake updaters can contain malware.
We advise being vigilant with incoming mail. The attachments and links present in suspicious/irrelevant emails and messages must not be opened since that may lead to a system infection. Another recommendation is to be cautious when browsing - as fraudulent and malicious content usually appears legitimate.
We must emphasize the importance of having a dependable anti-virus installed and kept up-to-date. Security programs must be used to run regular system scans and to remove detected threats and issues. If your computer is already infected with Dharma, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate this ransomware.
Screenshot of Dharma ransomware's pop-up window:
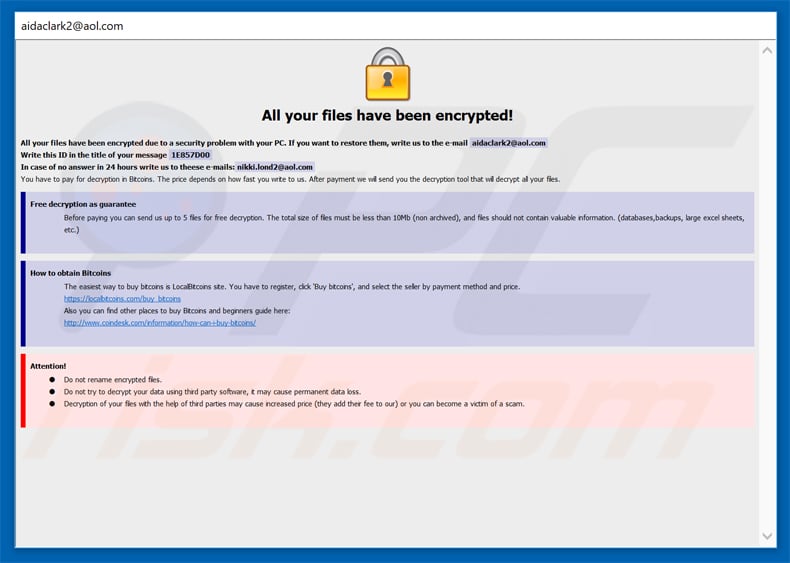
Text presented in this pop-up:
All your files have been encrypted!
All your files have been encrypted due to a security problem with your PC. If you want to restore them, write us to the e-mail aidaclark2@aol.com
Write this ID in the title of your message -
In case of no answer in 24 hours write us to theese e-mails:nikki.lond2@aol.com
You have to pay for decryption in Bitcoins. The price depends on how fast you write to us. After payment we will send you the decryption tool that will decrypt all your files.
Free decryption as guarantee
Before paying you can send us up to 5 files for free decryption. The total size of files must be less than 10Mb (non archived), and files should not contain valuable information. (databases,backups, large excel sheets, etc.)
How to obtain Bitcoins
The easiest way to buy bitcoins is LocalBitcoins site. You have to register, click 'Buy bitcoins', and select the seller by payment method and price.
hxxps://localbitcoins.com/buy_bitcoins
Also you can find other places to buy Bitcoins and beginners guide here:
hxxp://www.coindesk.com/information/how-can-i-buy-bitcoins/
Attention!
Do not rename encrypted files.
Do not try to decrypt your data using third party software, it may cause permanent data loss.
Decryption of your files with the help of third parties may cause increased price (they add their fee to our) or you can become a victim of a scam.
Screenshot of Dharma's text file ("How to restore data.txt"):
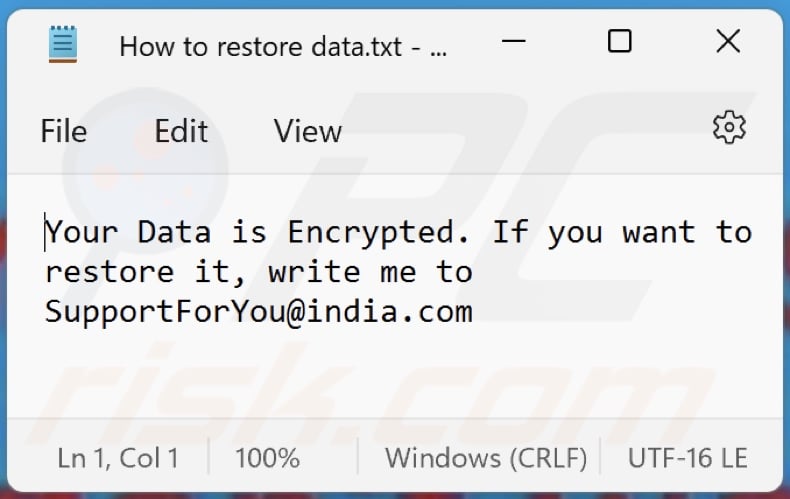
Text presented in this file:
Your Data is Encrypted. If you want to restore it, write me to SupportForYou@india.com
Screenshot of Dharma's desktop wallpaper:
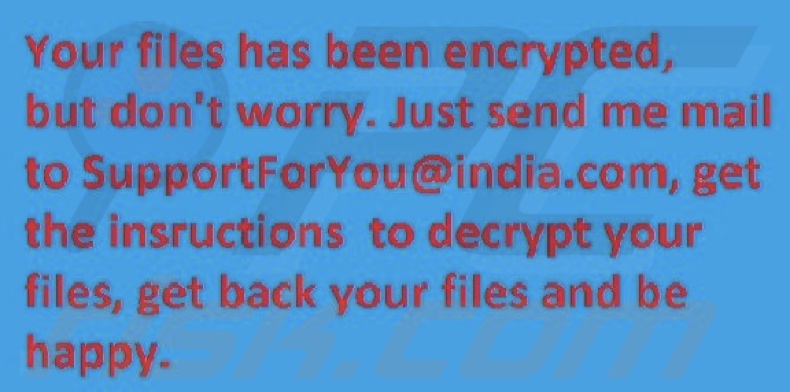
Text presented on this wallpaper:
Your files has been encrypted, but don't worry. Just send me mail to SupportForYou@india.com, get the insructions to decrypt your files, get back your files and be happy.
Screenshot of the ransom demanding message displayed by a variant of this ransomware:
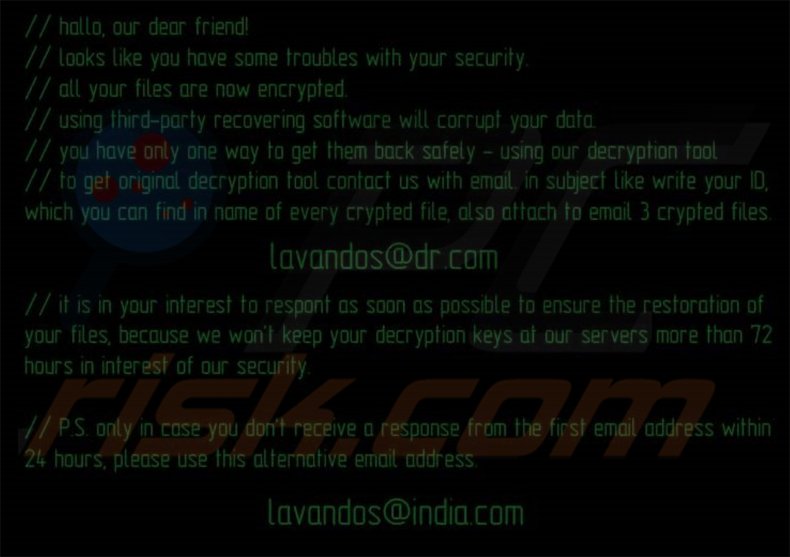
Text presented in this message:
hallo, our dear friend!
looks like you have some troubles with your security
all your files are now encrypted
using third-party recovering software will corrupt your data
you have only one way to get them back safety - using our decryption tool
to get original decryption tool contact us with email is subject like write your ID which your can find
in name of every encrypted file, also attach to email 3 crypted files.
lavandos@dr.com
It is your interest to respond as soon as possible to ensure the restoration of your files because we won’t keep your decryption keys at our servers more than 72 hours in interest of our security
PS. only in case you don’t receive a response from the first email address within 24 hours, please use this alternative email address
lavandos@india.com
Screenshot of the text file created by a variant of this ransomware ("README.TXT"):
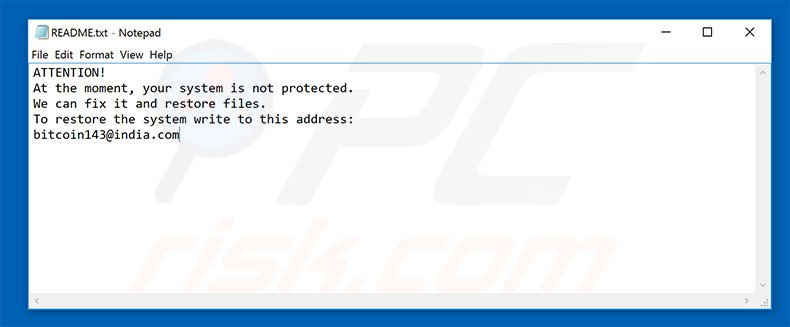
Text presented in this file:
ATTENTION!
At the moment, your system is not protected.
We can fix it and restore files.
To restore the system write to this address:
bitcoin143@india.com
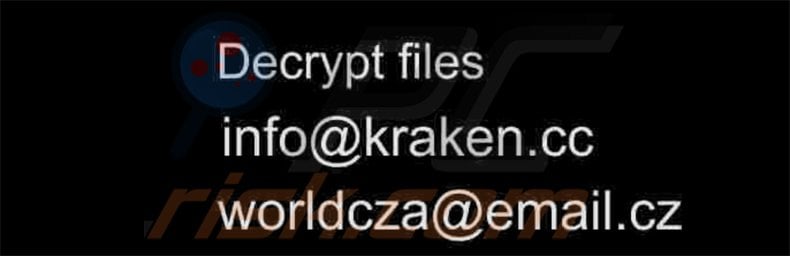
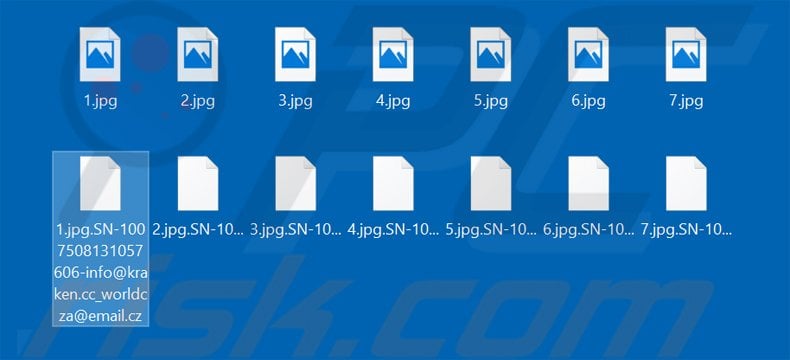
Update 2017, March 2 - Cyber criminals have updated this ransomware. It now creates a separate file for each encrypted one. Encrypted files now get “.serial number-info@kraken.cc_worldcza@smail.cz extension”. For example "1.jpg" file after encryption would appear as "1.jpg.SN-1007508131057606-info@kraken.cc_worldcza@email.cz". Below are screenshots of how it looks like.
Wallpaper:
Encrypted files:
Update 26 March, 2018 - Cyber criminals have updated the appearance of this ransomware. Current variant adds presents the ransom demanding messages in a pop-up window (screenshot above) and "FILES ENCRYPTED.txt" file.
Ransom demanding message in the "FILES ENCRYPTED.txt" file:
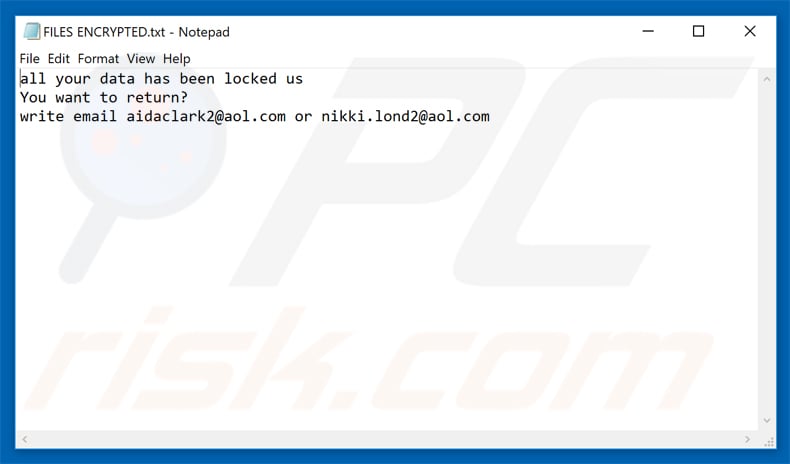
Text presented in this file:
all your data has been locked us
You want to return?
write email aidaclark2@aol.com or nikki.lond2@aol.com
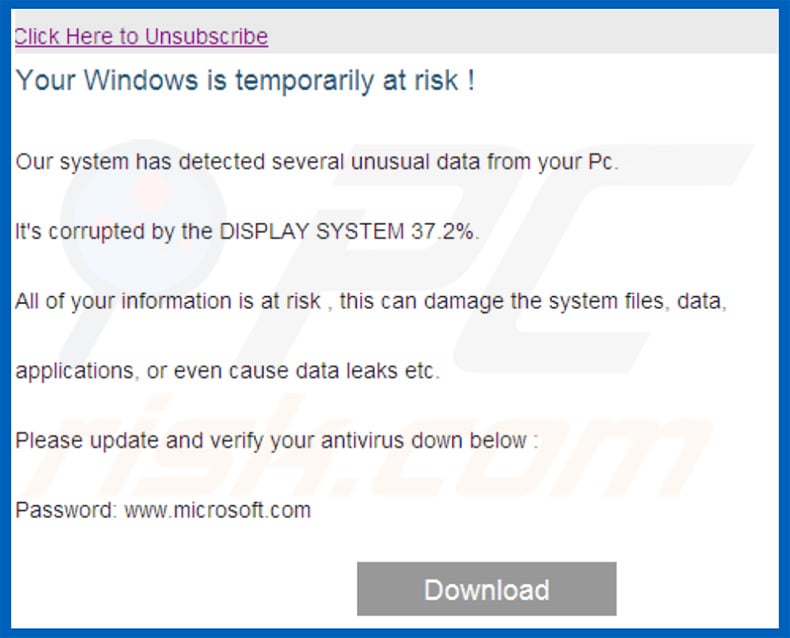
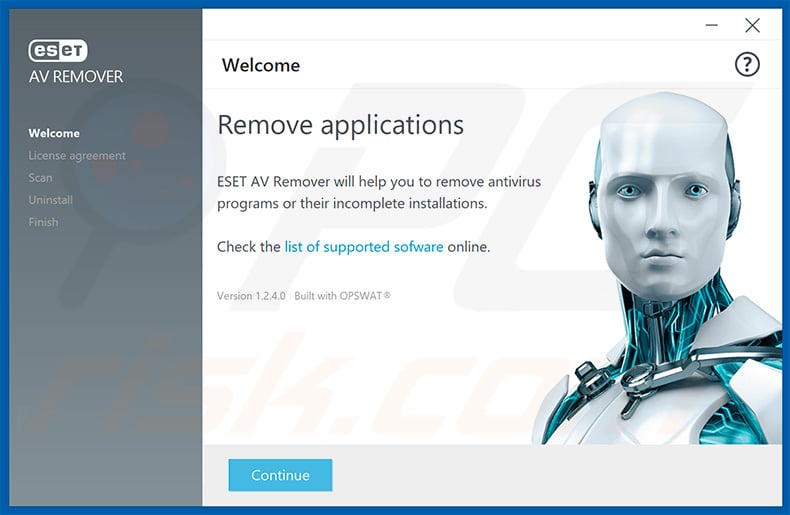
Update May 9, 2019 - Cyber criminals have recently started spreading Dharma ransomware by using the notorious "bundling" method. To be more specific, crooks use ESET AV Remover as a disguise.
The installer is typically proliferated using email spam campaigns which contain messages (supposedly, Microsoft company warnings) claiming that the system is infected and that users should immediately scan download a malware removal tool.
At the time of research emails contained an attachment - download link of the "remover", which is packed to a password-protected (self-running) archive named "Defender.exe". Password is provided in the email as well. Now, once extracted, the archive drops an outdated ESET AV Remover installer named "Defender_nt32_enu.exe" into the system.
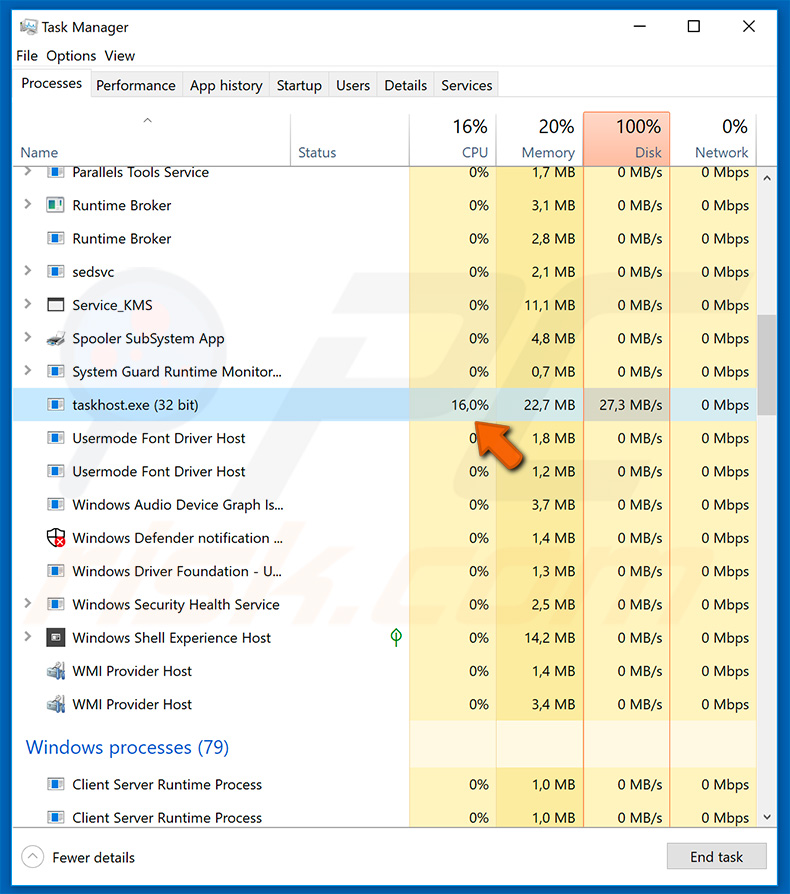
Additionally, it drops "taskhost.exe" file to "C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Startup\" directory and automatically runs it. This "taskhost.exe" process instantly starts encrypting data without users' consent. The aforementioned "Defender_nt32_enu.exe" is automatically executed as well.
Now what's interesting is that both "Defender.exe" email attachment and dropped "Defender_nt32_enu.exe" file have Windows Defender's icon, while in reality one is an archive and the other one is ESET AV Remover 's installer.
Nevertheless, it is a mere disguise used to draw victims attention from the "taskhost.exe" file which is encrypting while victim is trying to install the remover.
Again, the ESET AV Remover's installer is genuine (yet outdated) and harmless. The file responsible for all the damage caused is "taskhost.exe". At the time of research this method was used to spread Dharma's .ETH variant.
Screenshot of a deceptive email used to distribute Dharma ransomware:
Screenshot of "taskhost.exe" process in Windows Task Manager. Now be aware that "taskhost.exe" is a name of genuine Microsoft Windows operating system's process. Typically, the system runs multiple "taskhost.exe" instances at once to handle a number of different tasks.
Cyber criminals often attempt to take advantage of such situations and disguise malicious applications by using names of genuine system's processes.
It is important to know that the genuine processes barely use any system's resources, while encrypting process may take up to 100% of system's CPU (depending on how powerful the system is). Therefore, determining which process is malicious is rather easy.
Screenshot of the ESET AV Remover's installer:
Update March 10, 2020 - Cyber criminal group known as PARINACOTA is continually spread Dharma ransomware in various targeted attacks. They use a so-called "smash-and-grab" technique. This group typically targets machines/servers connected to large networks. Targeted devices usually have Remote Desktop Control (RDP) exposed to the Internet.
In order to infiltrate these machines PARINACOTA uses brute-force attacks. What's important is that these actions are human-operated. Although this group is notorious for dropping a number of different payloads during various time periods, the most recent one is Dharma.
More detailed information can be found in Microsoft's article ("PARINACOTA group: Smash-and-grab monetization campaigns" section).
Update April 14, 2020 - With the increased concerns over the Coronavirus/COVID-19 pandemic, cyber criminals have incorporated it into their scams. This has been observed in Dharma ransomware distribution as well. The proliferation techniques in themselves are varied, however the underlying theme is the same.
For example, spam campaigns with virulent attachments or links to malicious websites - relating to Coronavirus in some manner.
Update August 13, 2020 - Developers of the Dharma ransomware have begun offering a hacking toolkit to their affiliates. Unlike in many of the other RaaS (Ransomware-as-a-Service) operations, which target large enterprises, the ransoms demanded by Dharma attacks - are significantly smaller.
This is due to the low requirements for new affiliates, in comparison to other RaaS operations that cooperate only with the best. Therefore, the number of affiliates for Dharma is remarkably larger, as is the net of potential victims. However, with the need of many operators - the aforementioned operation affiliates with amateur cyber criminals.
To maintain a successful operation, the Dharma RaaS has developed a toolkit to aid newcomers and compensate for their lack of skill. More information on these developments can be found in an article by Lawrence Abrams on BleepingComputer.
Screenshot of Kaspersky’s Rakhni decryptor capable of decrypting files affected by older Dharma versions (you can download it HERE):
Dharma ransomware removal:
Instant automatic malware removal:
Manual threat removal might be a lengthy and complicated process that requires advanced IT skills. Combo Cleaner is a professional automatic malware removal tool that is recommended to get rid of malware. Download it by clicking the button below:
DOWNLOAD Combo CleanerBy downloading any software listed on this website you agree to our Privacy Policy and Terms of Use. To use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
Removal and file recovery procedure
If your files are encrypted with a new extension and a ransom note has appeared, you've been hit by ransomware. Don't pay. The procedure below works in order: contain the infection, identify the variant, remove the ransomware itself (so anything you restore doesn't get re-encrypted), and try to recover files using free decryption tools, Windows Volume Shadow Copies, or backups. Run a full system scan with Combo Cleaner to remove the infection - then move on to file recovery.
Common ransomware behaviors
VisibleEncrypts your files and renames them
The ransomware reads each file, encrypts the contents with the attacker's public key, and writes the encrypted bytes back to disk. Most variants also rename the file by appending a new extension - .net, .locked, .crypt, .lockbit, .djvu, etc. Without the matching private key, the encrypted files cannot be opened normally. Recovery depends on a free decryption tool, a recoverable Volume Shadow Copy, or a clean backup.
VisibleDrops a ransom note in every encrypted folder
A text or HTML file (usually named HOW_TO_DECRYPT.txt, README.txt, _readme.txt, or similar) is placed in every folder that contains encrypted files. The note explains the situation, lists a payment amount in cryptocurrency, gives a deadline, and provides a contact email or .onion site. Save the note - don't delete it. Its exact wording, the email address, and the bitcoin wallet are how you identify the variant in the next phase.
VisibleReplaces the desktop wallpaper
Many ransomware variants change the Windows wallpaper to a black or red image with the ransom message and instructions. The wallpaper is just a visual scare tactic - it doesn't add any actual capability and reverts to normal once the ransomware is removed. Photograph it before removal in case the contact details are useful for variant identification or for reporting to authorities.
HiddenDeletes Volume Shadow Copies
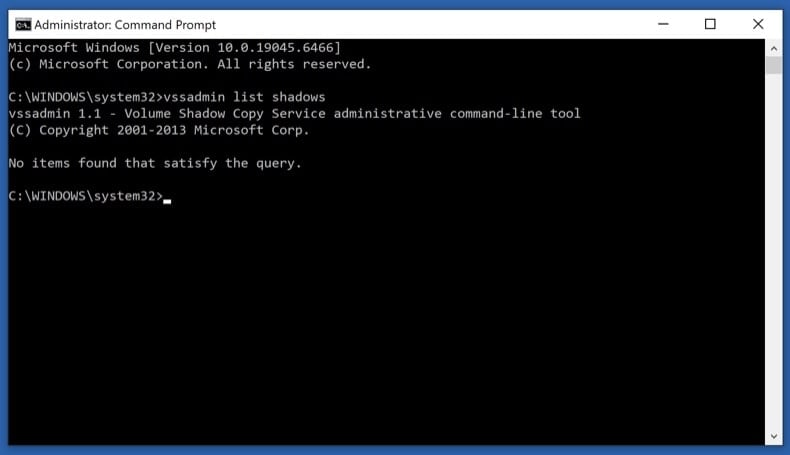
One of the first things modern ransomware does after launching is run vssadmin delete shadows /all /quiet to wipe Windows' built-in Volume Shadow Copies - the snapshots that Previous Versions and System Restore rely on. Some ransomware doesn't fully succeed (especially on systems where the user lacks full admin rights), leaving partial shadow copies recoverable. Phase 4 step 11 covers how to check what survived.
HiddenDisables Windows Defender and other security tools
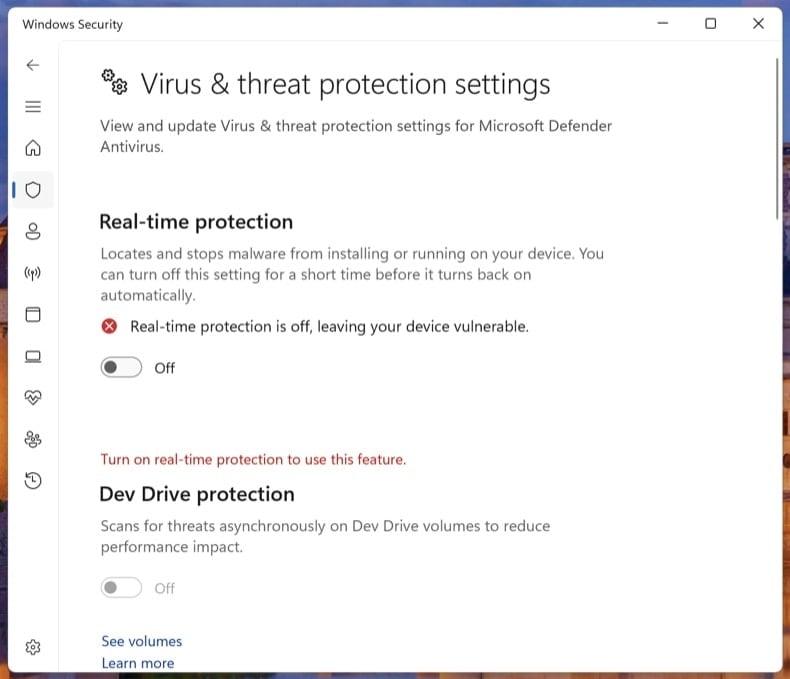
Before encrypting, the ransomware tries to silence anything that could alert you or block it - Windows Defender real-time protection, third-party antivirus services, backup agents (Veeam, Acronis), and sometimes the Windows Event Log service. It often modifies Group Policy or registry keys to keep these off after reboot. Phase 3 step 9 explicitly turns Tamper Protection back on so the next ransomware attempt can't repeat the trick.
HiddenSpreads laterally to other PCs on the network
Network-aware ransomware (LockBit, Conti, BlackCat, Akira families) doesn't stop at the first machine. It scans for SMB shares, mapped drives, and other PCs on the same network, then encrypts whatever it can reach. On Windows domains, a single compromised user with admin rights can lead to all-domain encryption. This is why Phase 1 step 2 disconnects the network as the very first action - it stops the spread immediately.
HiddenSteals data before encrypting (double extortion)
Modern ransomware (LockBit, BlackCat / ALPHV, Akira, Cl0p, Royal) almost always exfiltrates data before encrypting. The attacker then runs a "double extortion" play: pay the ransom for decryption, plus pay again to prevent the stolen data from being leaked on the group's leak site. Paying the first ransom does not get the leaked data back - assume that anything the ransomware could read was uploaded. This is one more reason not to pay: the data is already out.
Don't pay the ransom
Paying the ransom does not guarantee you'll get your files back. Major ransomware response studies consistently show that a meaningful percentage of paying victims either receive a non-working decryptor, only partial decryption, or no decryptor at all. Beyond that:
- Paying confirms you as a willing target - re-attack rates within 12 months are high
- Several ransomware groups have been sanctioned (US OFAC, UK OFSI). Paying these groups may be illegal under sanctions law in your country
- The ransom funds the next attack - on you or someone else
- Modern ransomware almost always exfiltrates data first, so paying doesn't get the leaked data back. Assume anything the malware could read was uploaded
- Decryptors, even when they work, often leave files corrupted because the encryption itself was buggy or rushed
The path below tries every legal, free recovery option first. Pay only as an absolute last resort, after consulting a lawyer and your country's cyber crime authority.
Disconnect from the network and log out of cloud storage
Pull the Ethernet cable and turn off Wi-Fi on the affected PC. If multiple computers share the network, do the same on every machine you suspect could be affected, including any servers and NAS units.
Then sign out of cloud storage clients (OneDrive, Dropbox, Google Drive, iCloud) from their app settings. If you can, pause the sync. Some ransomware uses the running sync client to push encrypted versions over your clean cloud copies.
Modern ransomware spreads laterally across SMB shares, mapped drives, RDP, and reachable network neighbors. Disconnecting stops the spread the moment you do it. Logging out of cloud sync clients prevents the ransomware from encrypting the cloud copies of your files via the sync API.
Unplug external drives and USB storage
Safely eject any external drives, USB sticks, SD cards, and network-attached storage shares - then unplug them. If a drive was connected when the ransomware ran, the files on it may already be encrypted, but unplugging stops further damage.
Critically: don't reconnect any drive (including your most recent backup) to this PC until the ransomware is removed in Phase 3. Reconnecting an external backup to an actively-infected PC is the most common way that backup gets encrypted too.
Save the ransom note and a sample encrypted file
Copy the ransom note and one small encrypted file (under 1 MB) to a USB stick, or photograph the note with your phone. You'll need both for the variant identification step.
The ransom note is usually one of:
- A
.txtfile in every encrypted folder (typicallyHOW_TO_DECRYPT.txt,README.txt, or_readme.txt) - An
.htmlfile with the same purpose - A changed desktop wallpaper - photograph it
- A lock-screen interrupt that runs at startup - rarer
Don't delete the note. Variant identification depends on its exact wording, the contact email, and the bitcoin wallet address. The note is also evidence if you report to authorities.
Identify the variant with ID Ransomware
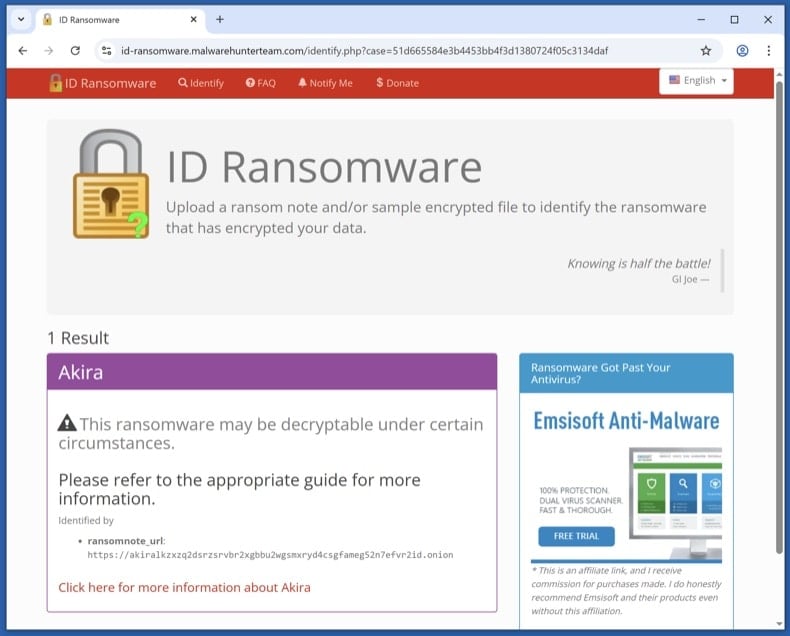
From a clean device (your phone is fine, or another PC that wasn't on the affected network), visit id-ransomware.malwarehunterteam.com. Upload the ransom note and the sample encrypted file. The site identifies the variant family and tells you whether a free decryptor exists.
ID Ransomware is run by the Malware Hunter Team. Files you upload are kept private - they're used for analysis, not published. If you're concerned about uploading data anyway, you can paste the contact email and bitcoin wallet from the note - those are often enough for identification.
The ransomware itself must be removed before any file recovery. If it's still active, anything you restore in Phase 4 gets re-encrypted within minutes.
Boot to Safe Mode with Networking and download the scanners
Safe Mode loads only the minimal Windows drivers, which prevents most ransomware from auto-running while you set up the scanners.
Windows 11: open , click Restart now next to Advanced startup. After the restart, click , then press 5 or F5.
Windows 10: click the Windows logo, hold Shift, click the Power icon and choose Restart. From the Choose-an-option screen, click , then press F5.
Once Safe Mode has loaded, turn Wi-Fi back on and download Combo Cleaner (used in step 8) and Microsoft Safety Scanner (used in step 9). Save both installers to your Desktop, then disconnect Wi-Fi again before scanning.
Run Microsoft Defender Offline
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts into a stripped-down environment and scans the disk before Windows fully loads.
Some ransomware variants drop bootkit components or kernel hooks that hide from any scanner running on the same Windows session that's already infected. A pre-boot offline scan sees the disk before the malware can load itself.
VB100 certified. Includes anti-trojan, registry/persistence scanning, and anti-spyware in one pass. The 7-day free trial is available.
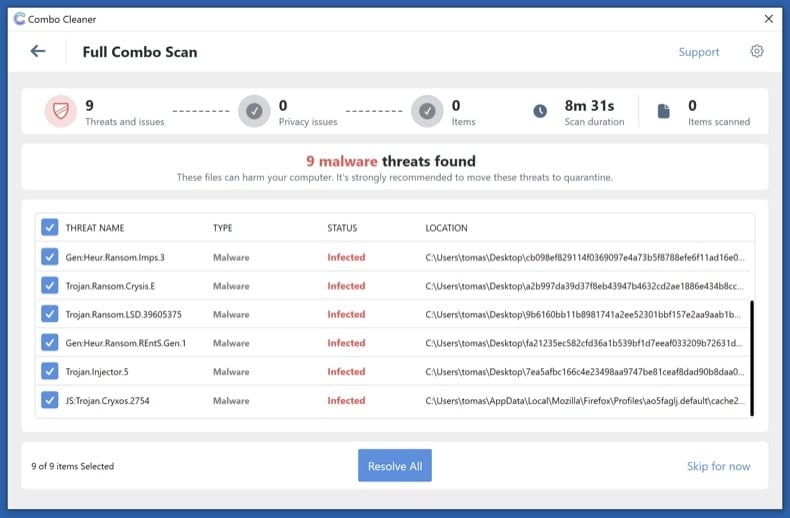
Download Combo CleanerRun a full Combo Cleaner scan
Run the installer you downloaded in step 6 and start a full system scan (not the quick scan). Let it complete, review what it detected, and apply the recommended actions. Combo Cleaner quarantines the ransomware executable and the registry / scheduled-task entries that re-launch it on reboot.
Run Microsoft Safety Scanner and re-enable Defender
Run Microsoft Safety Scanner (MSERT.exe) as a second-opinion full scan. The binary expires every 10 days so the copy you downloaded has the latest signatures.
Once it finishes, open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all on. Many ransomware variants disable Defender during the attack - this is where you switch it back on so the next attempt can't repeat the trick.
Different scanning engines catch different threats. Running an additional Microsoft scan after Combo Cleaner is the most underused verification step in malware removal - and free.
Try the steps in order. The first decryptor that works ends the recovery process - no need to do all four.
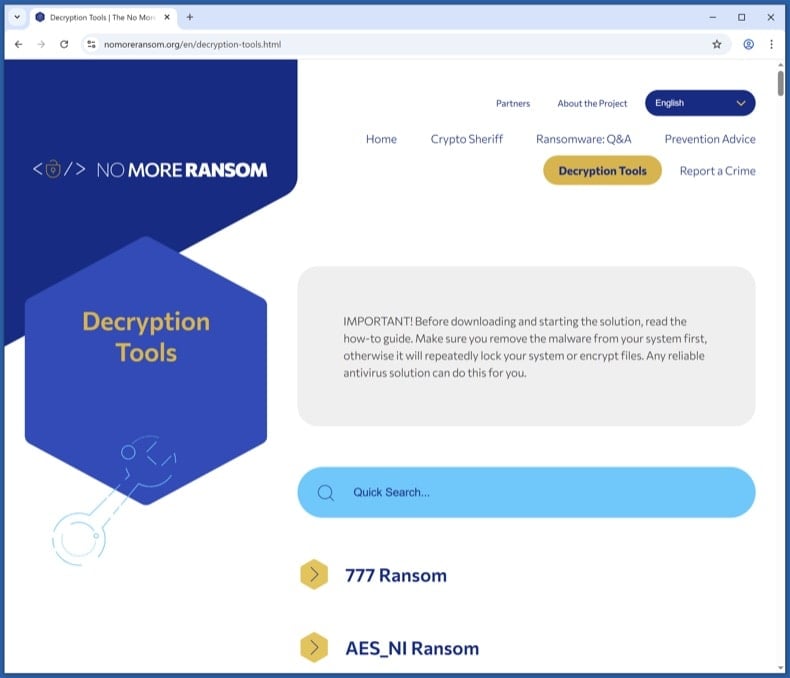
Check the No More Ransom Project for a free decryptor
Visit nomoreransom.org and search the Decryption Tools list for the variant name returned by ID Ransomware. The project is run by Europol, the Dutch Police, and security vendors - everything listed is legitimate and free.
If a decryptor exists, download it onto a clean PC, copy it across, and follow its instructions exactly. Decryptors usually want you to point them at a sample encrypted file plus its known unencrypted version (sometimes any image you previously had a backup of works).
Free decryptors exist for parts of the STOP/Djvu, GandCrab, REvil, Avaddon, Conti and Hive families, among others. Most modern variants don't have public decryptors - if yours isn't listed, that's expected; move to the next step.
Try Windows Volume Shadow Copies
Windows automatically creates Volume Shadow Copies of files when System Restore points are made or scheduled backups run. Most ransomware tries to wipe these (vssadmin delete shadows /all /quiet), but the deletion sometimes fails partially - especially if the running user doesn't have full admin rights. When it does fail, snapshots survive that contain pre-encryption versions of your files.
First, check what's there. Open Command Prompt as Administrator and run:
vssadmin list shadows
If you see entries listed, shadow copies survived. To restore from them:
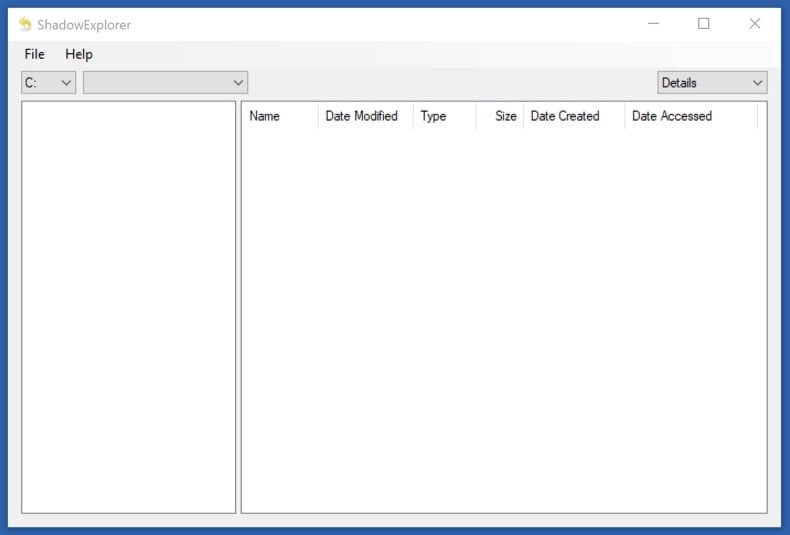
- Built-in: right-click any folder → Properties → Previous Versions tab. Pick a snapshot dated before the infection and restore.
- Better tool for browsing: install Shadow Explorer (free). It shows all snapshots as a normal file tree and lets you copy out only the files you want.
Shadow Copies recover the original files exactly, with no risk of decryption errors. If they survived, this is faster and cleaner than running a decryptor on the encrypted set.
Restore from cloud or external backup
If you have a backup that pre-dates the infection, this is the cleanest recovery available. Important precautions:
- Don't reconnect a backup drive until Phase 3 is complete. If the ransomware is still active, plugging in the backup encrypts it too.
- For cloud backups (OneDrive, Dropbox, Google Drive, iCloud), use the Version History feature to roll individual files back to pre-encryption versions.
- OneDrive specifically has a "Restore your OneDrive" feature: if it detected mass file changes, you can roll back the entire account up to 30 days. Sign in at OneDrive on the web, click the Settings gear, and choose Restore your OneDrive. Microsoft 365 subscribers also get ransomware detection alerts; non-subscribers get one free recovery.
- Verify the restored files open correctly before you delete the encrypted set. Test a few documents, photos, and any database / project files.
Try Recuva as a last-resort recovery
Recuva is a long shot, not a primary recovery tool. Most modern ransomware encrypts files in place - it reads the original, encrypts the data, and writes the encrypted bytes back to the same disk location. In that case, the original isn't deleted, just rewritten - and Recuva has nothing to find.
But for older or simpler variants that deleted originals before creating encrypted copies (rather than encrypting in place), Recuva can sometimes pull the originals from unallocated disk space. Worth trying as a last resort, especially before you use the disk much further.
If you try it:
- Stop using the disk as much as possible - every disk write reduces recovery odds
- Run Recuva from a USB stick, not from the affected disk
- Use Deep Scan mode (slower but the only mode worth running for this scenario)
Don't skip the steps above expecting Recuva to bail you out. It works in maybe 5-20% of cases, depending on the variant and how soon you try.
Report the attack to authorities
Even if your files aren't recovered, your report helps authorities track variants, attribute groups, and warn future victims. In some jurisdictions (especially the US and UK) early reporting can sometimes help recall a wired ransom payment via banking partners.
Save the report number - banks, insurers, and credit bureaus will ask for it. If you operate a business, you may also have legal disclosure obligations (GDPR in the EU, state breach laws in the US) that run on a 72-hour clock.
Plan 3-2-1 backups going forward
The single best defense against ransomware is a tested backup. Use the 3-2-1 rule:
- 3 copies of your data
- 2 different storage media (e.g., internal drive + external drive)
- 1 offline / air-gapped copy (an external drive that isn't always connected)
Recommended cadence:
- Daily: cloud sync (OneDrive, Dropbox, Google Drive) - convenient, but vulnerable if the ransomware reaches the sync folder. The Version History feature is what saves you
- Weekly: external drive that you connect briefly, then disconnect - the air-gap is what protects against ransomware
- Monthly: a second external drive stored off-site (different physical location) - protects against fire, theft, flood
Test the backup at least once. Open a few files from it, check sizes match, restore one to a different folder. An untested backup isn't a backup - it's a hope.
Patch the entry point and monitor for 30 days
Most reinfections happen via the same vector that worked the first time. Until you've patched the entry point, watch for:
- Unusual disk activity, unexpected file modifications, or unfamiliar processes in Task Manager
- Unexpected reboots or new accounts you didn't create
- Defender or your antivirus turning itself off again
Common entry vectors and what to do about each:
- Phishing email with a malicious attachment - review email filters and train yourself / staff to recognise the patterns - see pcrisk's Phishing/Scam reference
- Exposed RDP with weak passwords - disable Remote Desktop from if you don't need it. If you do, put it behind a VPN and require a long password plus MFA
- Unpatched VPN appliances or public-facing apps - check the vendor's advisories page and apply the latest firmware
- Cracked / pirated software - was the most common vector for STOP/Djvu in particular. Don't run software from torrent sites
Run a Combo Cleaner scan weekly for the first month. Update Windows, browsers, and applications aggressively.
Important: Removing a ransomware infection requires a full system scan, not a manual file delete. If you're not confident with the manual procedure, run an automated scan with Combo Cleaner and Windows Defender and stop there - that combination removes the vast majority of consumer ransomware variants. Then move to Phase 4 for file recovery, or to Phase 5 if your files are unrecoverable and you need to start fresh from a clean Windows install.
Frequently Asked Questions (FAQ)
How was my computer hacked and how did hackers encrypt my files?
Ransomware executables are commonly executed (opened) by the victims themselves, as these files are usually presented as or bundled with ordinary software/media. Malware (ransomware included) is primarily spread through drive-by downloads, spam emails and messages, online scams, dubious download channels (e.g., unofficial and freeware sites, P2P sharing networks, etc.), illegal program activation tools ("cracks"), fake updates, and malvertising.
How to open files encrypted by Dharma ransomware?
Ransomware-encrypted files require decryption for continued usage. In other words, the affected files can neither be opened nor otherwise used - unless they are decrypted.
Where should I look for free decryption tools for Dharma ransomware?
Older versions of Dharma ransomware can be decrypted by using Kaspersky's Rakhni decryptor (more information above). However, if you have experienced a ransomware attack involving a newer Dharma variant, we advise you to check out the No More Ransom project website (more information above).
I can pay you a lot of money, can you decrypt files for me?
We do not offer services of this kind. In fact, decryption is rarely possible without the cyber criminals' interference. Therefore, third-parties offering paid decryption are likely scams or middleman services between victims and criminals.
Will Combo Cleaner help me remove Dharma ransomware?
Yes, Combo Cleaner can scan devices and eliminate detected ransomware infections. It must be mentioned that while using an anti-virus is the first step in ransomware recovery - security software is incapable of decrypting files.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion