

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What is Plomb?
This program was discovered by Jakub Kroustek. There are many ransomware-type programs online, including Plomb, which belongs to the Dharm ransomware family. Developers (cyber criminals) use it to encrypt data stored on users' computers and then to demand ransom payments for retrieval of files.
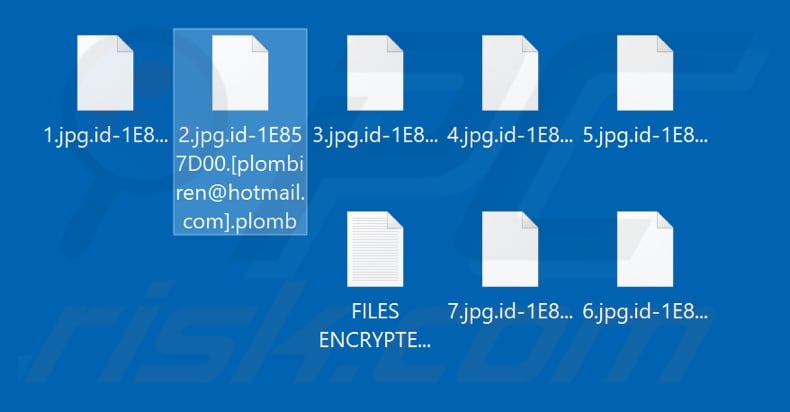
When encrypted, each file is renamed by adding the ".plomb" extension plus an email address and the victim's ID. For example, "1.jpg" is renamed to "1.jpg.id-1E857D00.[plombiren@hotmail.com].plomb". Like most malicious programs of this type, Plomb creates a ransom message (within the "FILES ENCRYPTED.txt" file) and displays a pop-up window with instructions.
The main information is provided in a pop-up window, whilst the "FILES ENCRYPTED.txt" file simply contains an email address to contact the cyber criminals who developed Plomb.
According to the information provided in the pop-up window, people who have computers infected with this ransomware-type program, must contact Plomb's developers via the plombiren@hotmail.com email address to retrieve their files. This email address is identical to that included within the extension of encrypted files.
When sending the email, Plomb victims must provide the ID that can be found in the pop-up window and encrypted file extension. Once contacted, cyber criminals will provide a cryptocurrency wallet address to make payment for a decryption tool (i.e. to pay a ransom).
The cost of the decryption tool cost is unknown, however, Plomb developers state that this depends on how quickly they receive an email from victims. They promise to send the decryption tool as soon as they are contacted and the money (cryptocurrency) is received.
They even offer free decryption of one file as 'proof' that they have the tool capable of file decryption (for files encrypted by this ransomware). Plomb's pop-up also contains a warning that victims do not use any other tools to decrypt files, or to rename them with the help of third parties. According to cyber criminals, any of these actions might cause permanent data loss.
Unfortunately, cyber criminals use cryptography algorithms (symmetric or asymmetric) that make decryption without a specific tool impossible. In most cases, only cyber criminals (ransomware developers) have the tool and can decrypt files using it.
These criminals can never be trusted - they often ignore victims after they receive the ransom payment and people become victims of a scam. There are currently no free tools able to decrypt files encrypted with Plomb ransomware. The only free solution is to use a data backup if one was created prior to encryption.
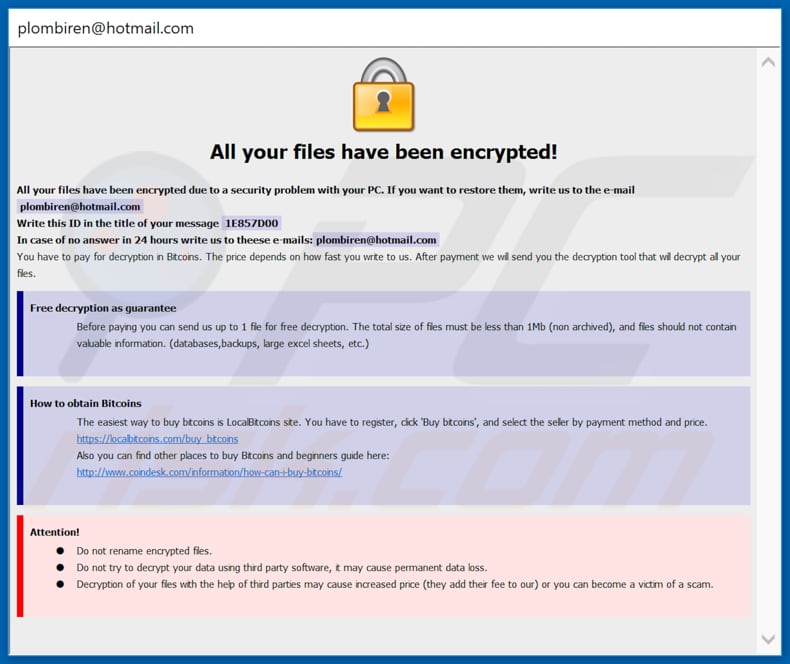
Screenshot of a message encouraging users to pay a ransom to decrypt their compromised data:
Many people develop ransomware-type programs. Plomb is just one example. Other examples are Dy8wud, MTP, and Kitty. These programs all encrypt data, which allows their developers to blackmail victims. Common differences are decryption tool cost and cryptography algorithm used to encrypt data.
Encryptions used with most ransomware-type malicious programs cannot be decrypted without the involvement of cyber criminals. This is only possible if the program is still in development or contains bug/flaws (this is quite rare). Therefore, maintain regular backups and store them on remote servers or unplugged storage devices.
How did ransomware infect my computer?
There are several different ways that cyber criminals use to infect computes with ransomware-type viruses: through untrustworthy software download sources, spam campaigns, fake (unofficial) software updaters, Trojans and software "cracking" tools.
Cyber criminals use unofficial software such as freeware download websites, free file hosting websites, P2P (peer-to-peer) networks such as torrents, eMule, and so on. They present malicious files (executables) that, once downloaded and opened or run, install malicious programs (such as ransomware). When using these tools, people cause computer infections.
Spam campaigns (emails) are used to infect computers through malicious attachments such as Microsoft Office documents (Word, Excel and others), archive files (RAR and ZIP), executables (.exe files), PDF documents, JavaScript files, and so on. When opened, they download and install ransomware or other infections.
Fake software updaters cause damage by exploiting bugs of outdated software or by downloading malicious software rather than the expected updates, fixes. If installed, trojans cause chain infections - they proliferate other computer infections. If a trojan is installed, it might be the reason why the computer was infected by ransomware.
Programs that are used to bypass activation of paid software often install malware rather than providing any other functions - cyber criminals employ these software "cracking" tools to proliferate computer viruses.
| Name | Plomb virus |
| Threat Type | Ransomware, Crypto Virus, Files locker |
| Symptoms | Can't open files stored on your computer, previously functional files now have a different extension, for example my.docx.locked. A ransom demanding message is displayed on your desktop. Cyber criminals are asking to pay a ransom (usually in bitcoins) to unlock your files. |
| Distribution methods | Infected email attachments (macros), torrent websites, malicious ads. |
| Damage | All files are encrypted and cannot be opened without paying a ransom. Additional password stealing trojans and malware infections can be installed together with a ransomware infection. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
How to protect yourself from ransomware infections?
To prevent computer infection with ransomware (or other high-risk computer infections), browse the internet, download, install, and update software with care. Do not to open attachments (or web links) that are received from unknown, suspicious addresses or presented in irrelevant emails.
Keep installed software up to date, however, use implemented, official tools that are provided by official software developers. Furthermore, download software using official websites or other reliable sources, and avoid using third party downloaders (or installers), Peer-to-Peer networks and other tools mentioned earlier.
The same applies to software "cracking" tools - they are illegal and are often the reason behind computer infections. Have reputable anti-virus or anti-spyware software installed and keep it enabled at all times. If your computer is already infected with Plomb, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate this ransomware.
Text presented in Plomb ransomware pop-up window:
All your files have been encrypted!
All your files have been encrypted due to a security problem with your PC. If you want to restore them, write us to the e-mail plombiren@hotmail.com
Write this ID in the title of your message 1E857D00
In case of no answer in 24 hours write us to theese e-mails:plombiren@hotmail.com
You have to pay for decryption in Bitcoins. The price depends on how fast you write to us. After payment we will send you the decryption tool that will decrypt all your files.
Free decryption as guarantee
Before paying you can send us up to 1 file for free decryption. The total size of files must be less than 1Mb (non archived), and files should not contain valuable information. (databases,backups, large excel sheets, etc.)
How to obtain Bitcoins
The easiest way to buy bitcoins is LocalBitcoins site. You have to register, click 'Buy bitcoins', and select the seller by payment method and price.
https://localbitcoins.com/buy_bitcoins
Also you can find other places to buy Bitcoins and beginners guide here:
http://www.coindesk.com/information/how-can-i-buy-bitcoins/
Attention!
Do not rename encrypted files.
Do not try to decrypt your data using third party software, it may cause permanent data loss.
Decryption of your files with the help of third parties may cause increased price (they add their fee to our) or you can become a victim of a scam.
Screenshot of Plomb text file ("FILES ENCRYPTED"):
Text presented in Plomb text file:
all your data has been locked us
You want to return?
write email plombiren@hotmail.com
Screenshot of files encrypted by Plomb (".plomb" extension):
Plomb ransomware removal:
Instant automatic malware removal:
Manual threat removal might be a lengthy and complicated process that requires advanced IT skills. Combo Cleaner is a professional automatic malware removal tool that is recommended to get rid of malware. Download it by clicking the button below:
DOWNLOAD Combo CleanerBy downloading any software listed on this website you agree to our Privacy Policy and Terms of Use. To use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
Removal and file recovery procedure
If your files are encrypted with a new extension and a ransom note has appeared, you've been hit by ransomware. Don't pay. The procedure below works in order: contain the infection, identify the variant, remove the ransomware itself (so anything you restore doesn't get re-encrypted), and try to recover files using free decryption tools, Windows Volume Shadow Copies, or backups. Run a full system scan with Combo Cleaner to remove the infection - then move on to file recovery.
Common ransomware behaviors
VisibleEncrypts your files and renames them
The ransomware reads each file, encrypts the contents with the attacker's public key, and writes the encrypted bytes back to disk. Most variants also rename the file by appending a new extension - .net, .locked, .crypt, .lockbit, .djvu, etc. Without the matching private key, the encrypted files cannot be opened normally. Recovery depends on a free decryption tool, a recoverable Volume Shadow Copy, or a clean backup.
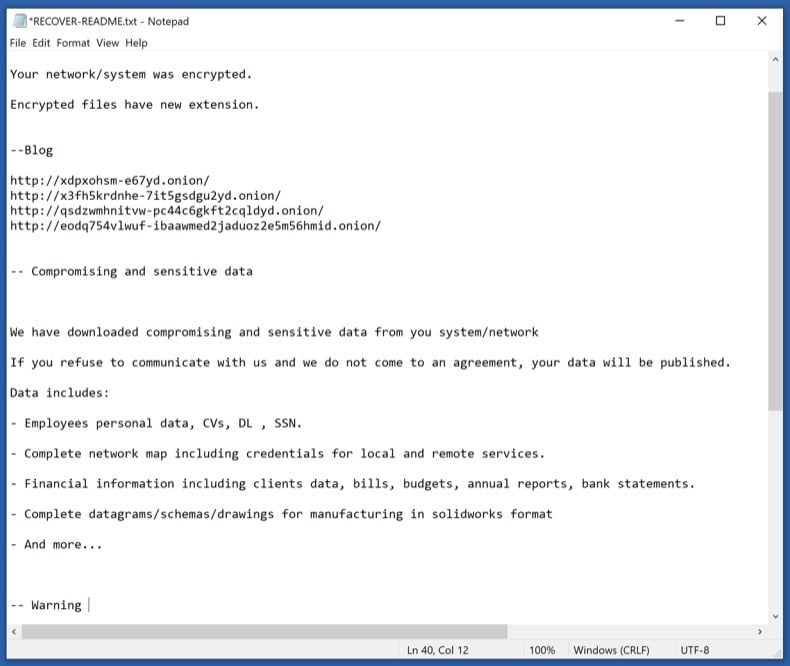
VisibleDrops a ransom note in every encrypted folder
A text or HTML file (usually named HOW_TO_DECRYPT.txt, README.txt, _readme.txt, or similar) is placed in every folder that contains encrypted files. The note explains the situation, lists a payment amount in cryptocurrency, gives a deadline, and provides a contact email or .onion site. Save the note - don't delete it. Its exact wording, the email address, and the bitcoin wallet are how you identify the variant in the next phase.
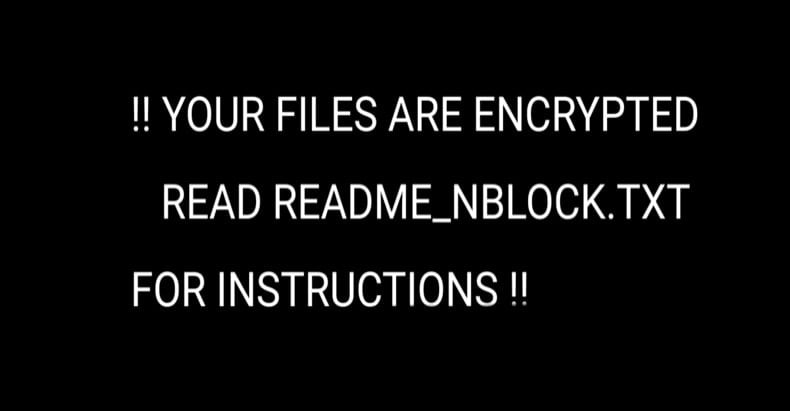
VisibleReplaces the desktop wallpaper
Many ransomware variants change the Windows wallpaper to a black or red image with the ransom message and instructions. The wallpaper is just a visual scare tactic - it doesn't add any actual capability and reverts to normal once the ransomware is removed. Photograph it before removal in case the contact details are useful for variant identification or for reporting to authorities.
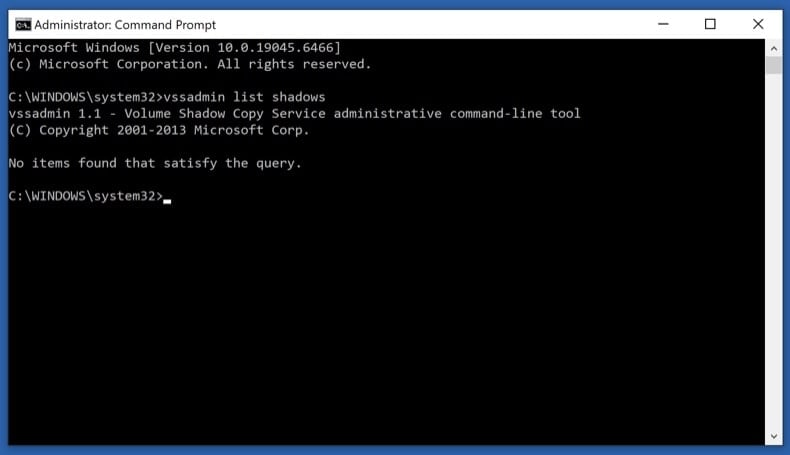
HiddenDeletes Volume Shadow Copies
One of the first things modern ransomware does after launching is run vssadmin delete shadows /all /quiet to wipe Windows' built-in Volume Shadow Copies - the snapshots that Previous Versions and System Restore rely on. Some ransomware doesn't fully succeed (especially on systems where the user lacks full admin rights), leaving partial shadow copies recoverable. Phase 4 step 11 covers how to check what survived.
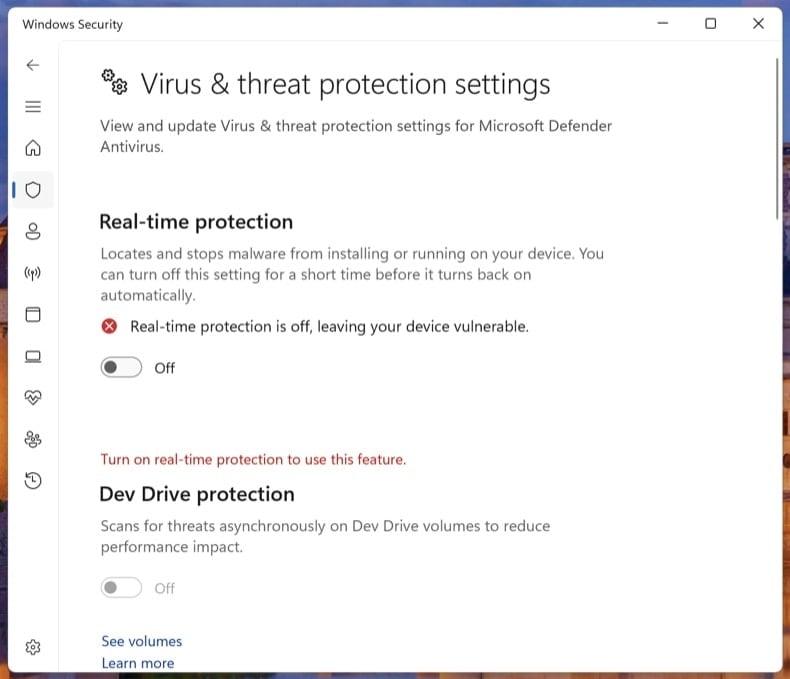
HiddenDisables Windows Defender and other security tools
Before encrypting, the ransomware tries to silence anything that could alert you or block it - Windows Defender real-time protection, third-party antivirus services, backup agents (Veeam, Acronis), and sometimes the Windows Event Log service. It often modifies Group Policy or registry keys to keep these off after reboot. Phase 3 step 9 explicitly turns Tamper Protection back on so the next ransomware attempt can't repeat the trick.
HiddenSpreads laterally to other PCs on the network
Network-aware ransomware (LockBit, Conti, BlackCat, Akira families) doesn't stop at the first machine. It scans for SMB shares, mapped drives, and other PCs on the same network, then encrypts whatever it can reach. On Windows domains, a single compromised user with admin rights can lead to all-domain encryption. This is why Phase 1 step 2 disconnects the network as the very first action - it stops the spread immediately.
HiddenSteals data before encrypting (double extortion)
Modern ransomware (LockBit, BlackCat / ALPHV, Akira, Cl0p, Royal) almost always exfiltrates data before encrypting. The attacker then runs a "double extortion" play: pay the ransom for decryption, plus pay again to prevent the stolen data from being leaked on the group's leak site. Paying the first ransom does not get the leaked data back - assume that anything the ransomware could read was uploaded. This is one more reason not to pay: the data is already out.
Don't pay the ransom
Paying the ransom does not guarantee you'll get your files back. Major ransomware response studies consistently show that a meaningful percentage of paying victims either receive a non-working decryptor, only partial decryption, or no decryptor at all. Beyond that:
- Paying confirms you as a willing target - re-attack rates within 12 months are high
- Several ransomware groups have been sanctioned (US OFAC, UK OFSI). Paying these groups may be illegal under sanctions law in your country
- The ransom funds the next attack - on you or someone else
- Modern ransomware almost always exfiltrates data first, so paying doesn't get the leaked data back. Assume anything the malware could read was uploaded
- Decryptors, even when they work, often leave files corrupted because the encryption itself was buggy or rushed
The path below tries every legal, free recovery option first. Pay only as an absolute last resort, after consulting a lawyer and your country's cyber crime authority.
Disconnect from the network and log out of cloud storage
Pull the Ethernet cable and turn off Wi-Fi on the affected PC. If multiple computers share the network, do the same on every machine you suspect could be affected, including any servers and NAS units.
Then sign out of cloud storage clients (OneDrive, Dropbox, Google Drive, iCloud) from their app settings. If you can, pause the sync. Some ransomware uses the running sync client to push encrypted versions over your clean cloud copies.
Modern ransomware spreads laterally across SMB shares, mapped drives, RDP, and reachable network neighbors. Disconnecting stops the spread the moment you do it. Logging out of cloud sync clients prevents the ransomware from encrypting the cloud copies of your files via the sync API.
Unplug external drives and USB storage
Safely eject any external drives, USB sticks, SD cards, and network-attached storage shares - then unplug them. If a drive was connected when the ransomware ran, the files on it may already be encrypted, but unplugging stops further damage.
Critically: don't reconnect any drive (including your most recent backup) to this PC until the ransomware is removed in Phase 3. Reconnecting an external backup to an actively-infected PC is the most common way that backup gets encrypted too.
Save the ransom note and a sample encrypted file
Copy the ransom note and one small encrypted file (under 1 MB) to a USB stick, or photograph the note with your phone. You'll need both for the variant identification step.
The ransom note is usually one of:
- A
.txtfile in every encrypted folder (typicallyHOW_TO_DECRYPT.txt,README.txt, or_readme.txt) - An
.htmlfile with the same purpose - A changed desktop wallpaper - photograph it
- A lock-screen interrupt that runs at startup - rarer
Don't delete the note. Variant identification depends on its exact wording, the contact email, and the bitcoin wallet address. The note is also evidence if you report to authorities.
Identify the variant with ID Ransomware
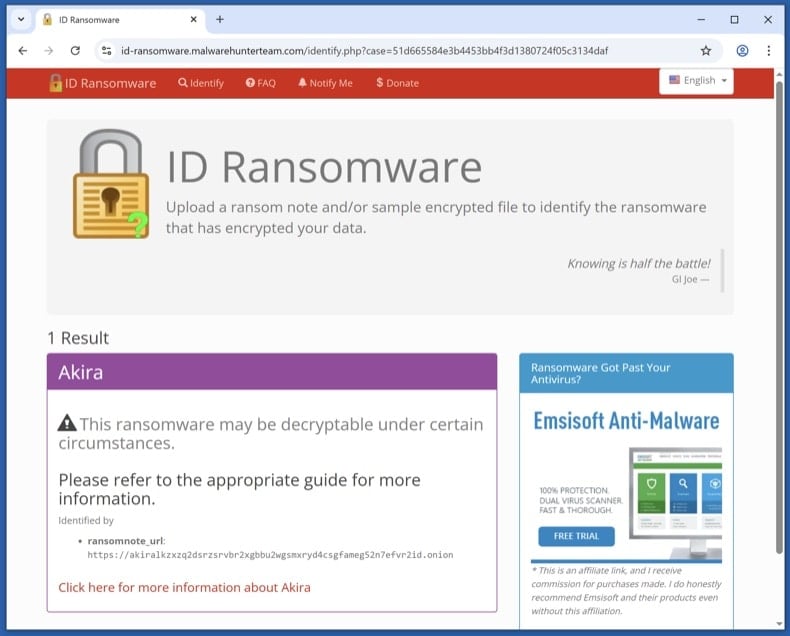
From a clean device (your phone is fine, or another PC that wasn't on the affected network), visit id-ransomware.malwarehunterteam.com. Upload the ransom note and the sample encrypted file. The site identifies the variant family and tells you whether a free decryptor exists.
ID Ransomware is run by the Malware Hunter Team. Files you upload are kept private - they're used for analysis, not published. If you're concerned about uploading data anyway, you can paste the contact email and bitcoin wallet from the note - those are often enough for identification.
The ransomware itself must be removed before any file recovery. If it's still active, anything you restore in Phase 4 gets re-encrypted within minutes.
Boot to Safe Mode with Networking and download the scanners
Safe Mode loads only the minimal Windows drivers, which prevents most ransomware from auto-running while you set up the scanners.
Windows 11: open , click Restart now next to Advanced startup. After the restart, click , then press 5 or F5.
Windows 10: click the Windows logo, hold Shift, click the Power icon and choose Restart. From the Choose-an-option screen, click , then press F5.
Once Safe Mode has loaded, turn Wi-Fi back on and download Combo Cleaner (used in step 8) and Microsoft Safety Scanner (used in step 9). Save both installers to your Desktop, then disconnect Wi-Fi again before scanning.
Run Microsoft Defender Offline
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts into a stripped-down environment and scans the disk before Windows fully loads.
Some ransomware variants drop bootkit components or kernel hooks that hide from any scanner running on the same Windows session that's already infected. A pre-boot offline scan sees the disk before the malware can load itself.
VB100 certified. Includes anti-trojan, registry/persistence scanning, and anti-spyware in one pass. The 7-day free trial is available.
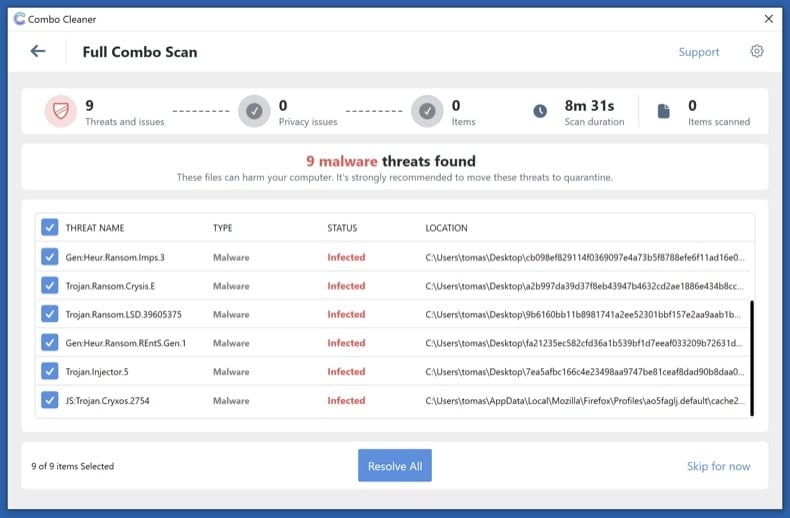
Download Combo CleanerRun a full Combo Cleaner scan
Run the installer you downloaded in step 6 and start a full system scan (not the quick scan). Let it complete, review what it detected, and apply the recommended actions. Combo Cleaner quarantines the ransomware executable and the registry / scheduled-task entries that re-launch it on reboot.
Run Microsoft Safety Scanner and re-enable Defender
Run Microsoft Safety Scanner (MSERT.exe) as a second-opinion full scan. The binary expires every 10 days so the copy you downloaded has the latest signatures.
Once it finishes, open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all on. Many ransomware variants disable Defender during the attack - this is where you switch it back on so the next attempt can't repeat the trick.
Different scanning engines catch different threats. Running an additional Microsoft scan after Combo Cleaner is the most underused verification step in malware removal - and free.
Try the steps in order. The first decryptor that works ends the recovery process - no need to do all four.
Check the No More Ransom Project for a free decryptor
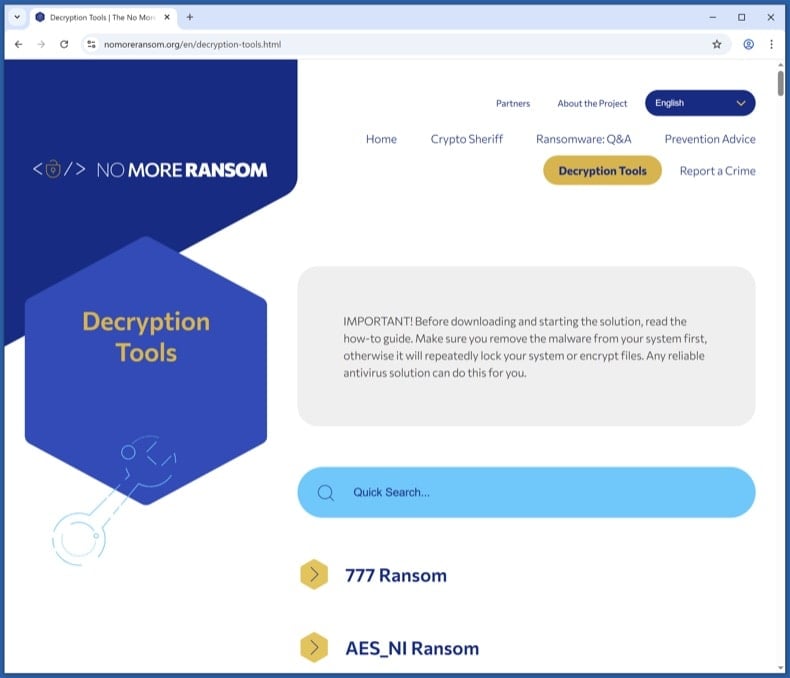
Visit nomoreransom.org and search the Decryption Tools list for the variant name returned by ID Ransomware. The project is run by Europol, the Dutch Police, and security vendors - everything listed is legitimate and free.
If a decryptor exists, download it onto a clean PC, copy it across, and follow its instructions exactly. Decryptors usually want you to point them at a sample encrypted file plus its known unencrypted version (sometimes any image you previously had a backup of works).
Free decryptors exist for parts of the STOP/Djvu, GandCrab, REvil, Avaddon, Conti and Hive families, among others. Most modern variants don't have public decryptors - if yours isn't listed, that's expected; move to the next step.
Try Windows Volume Shadow Copies
Windows automatically creates Volume Shadow Copies of files when System Restore points are made or scheduled backups run. Most ransomware tries to wipe these (vssadmin delete shadows /all /quiet), but the deletion sometimes fails partially - especially if the running user doesn't have full admin rights. When it does fail, snapshots survive that contain pre-encryption versions of your files.
First, check what's there. Open Command Prompt as Administrator and run:
vssadmin list shadows
If you see entries listed, shadow copies survived. To restore from them:
- Built-in: right-click any folder → Properties → Previous Versions tab. Pick a snapshot dated before the infection and restore.
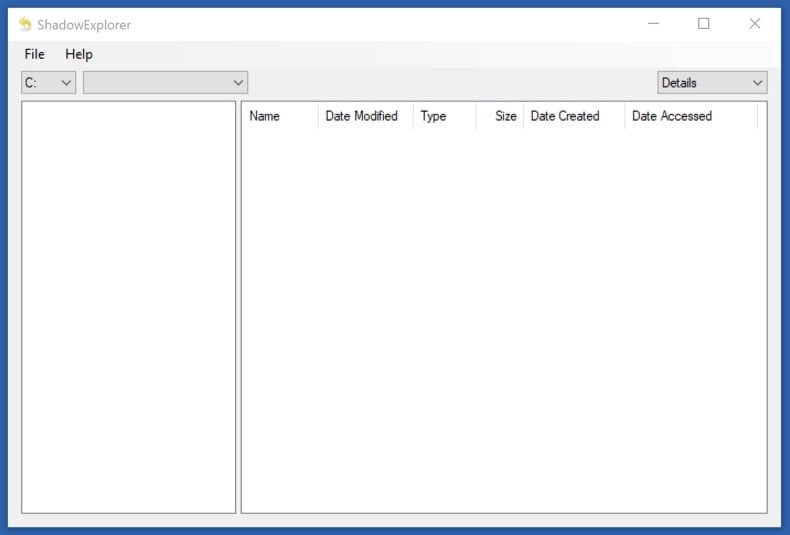
- Better tool for browsing: install Shadow Explorer (free). It shows all snapshots as a normal file tree and lets you copy out only the files you want.
Shadow Copies recover the original files exactly, with no risk of decryption errors. If they survived, this is faster and cleaner than running a decryptor on the encrypted set.
Restore from cloud or external backup
If you have a backup that pre-dates the infection, this is the cleanest recovery available. Important precautions:
- Don't reconnect a backup drive until Phase 3 is complete. If the ransomware is still active, plugging in the backup encrypts it too.
- For cloud backups (OneDrive, Dropbox, Google Drive, iCloud), use the Version History feature to roll individual files back to pre-encryption versions.
- OneDrive specifically has a "Restore your OneDrive" feature: if it detected mass file changes, you can roll back the entire account up to 30 days. Sign in at OneDrive on the web, click the Settings gear, and choose Restore your OneDrive. Microsoft 365 subscribers also get ransomware detection alerts; non-subscribers get one free recovery.
- Verify the restored files open correctly before you delete the encrypted set. Test a few documents, photos, and any database / project files.
Try Recuva as a last-resort recovery
Recuva is a long shot, not a primary recovery tool. Most modern ransomware encrypts files in place - it reads the original, encrypts the data, and writes the encrypted bytes back to the same disk location. In that case, the original isn't deleted, just rewritten - and Recuva has nothing to find.
But for older or simpler variants that deleted originals before creating encrypted copies (rather than encrypting in place), Recuva can sometimes pull the originals from unallocated disk space. Worth trying as a last resort, especially before you use the disk much further.
If you try it:
- Stop using the disk as much as possible - every disk write reduces recovery odds
- Run Recuva from a USB stick, not from the affected disk
- Use Deep Scan mode (slower but the only mode worth running for this scenario)
Don't skip the steps above expecting Recuva to bail you out. It works in maybe 5-20% of cases, depending on the variant and how soon you try.
Report the attack to authorities
Even if your files aren't recovered, your report helps authorities track variants, attribute groups, and warn future victims. In some jurisdictions (especially the US and UK) early reporting can sometimes help recall a wired ransom payment via banking partners.
Save the report number - banks, insurers, and credit bureaus will ask for it. If you operate a business, you may also have legal disclosure obligations (GDPR in the EU, state breach laws in the US) that run on a 72-hour clock.
Plan 3-2-1 backups going forward
The single best defense against ransomware is a tested backup. Use the 3-2-1 rule:
- 3 copies of your data
- 2 different storage media (e.g., internal drive + external drive)
- 1 offline / air-gapped copy (an external drive that isn't always connected)
Recommended cadence:
- Daily: cloud sync (OneDrive, Dropbox, Google Drive) - convenient, but vulnerable if the ransomware reaches the sync folder. The Version History feature is what saves you
- Weekly: external drive that you connect briefly, then disconnect - the air-gap is what protects against ransomware
- Monthly: a second external drive stored off-site (different physical location) - protects against fire, theft, flood
Test the backup at least once. Open a few files from it, check sizes match, restore one to a different folder. An untested backup isn't a backup - it's a hope.
Patch the entry point and monitor for 30 days
Most reinfections happen via the same vector that worked the first time. Until you've patched the entry point, watch for:
- Unusual disk activity, unexpected file modifications, or unfamiliar processes in Task Manager
- Unexpected reboots or new accounts you didn't create
- Defender or your antivirus turning itself off again
Common entry vectors and what to do about each:
- Phishing email with a malicious attachment - review email filters and train yourself / staff to recognise the patterns - see pcrisk's Phishing/Scam reference
- Exposed RDP with weak passwords - disable Remote Desktop from if you don't need it. If you do, put it behind a VPN and require a long password plus MFA
- Unpatched VPN appliances or public-facing apps - check the vendor's advisories page and apply the latest firmware
- Cracked / pirated software - was the most common vector for STOP/Djvu in particular. Don't run software from torrent sites
Run a Combo Cleaner scan weekly for the first month. Update Windows, browsers, and applications aggressively.
Important: Removing a ransomware infection requires a full system scan, not a manual file delete. If you're not confident with the manual procedure, run an automated scan with Combo Cleaner and Windows Defender and stop there - that combination removes the vast majority of consumer ransomware variants. Then move to Phase 4 for file recovery, or to Phase 5 if your files are unrecoverable and you need to start fresh from a clean Windows install.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion