

Get free scan and check if your device is infected.
Remove it nowTo use full-featured product, you have to purchase a license for Combo Cleaner. Seven days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
What kind of malware is CRPxO?
CRPxO is a ransomware-type program that locks files and demands payment for their decryption. It also claims to steal data before encrypting it, which the attackers use as extra leverage. Besides dropping two ransom notes, CRPxO changes the desktop wallpaper.
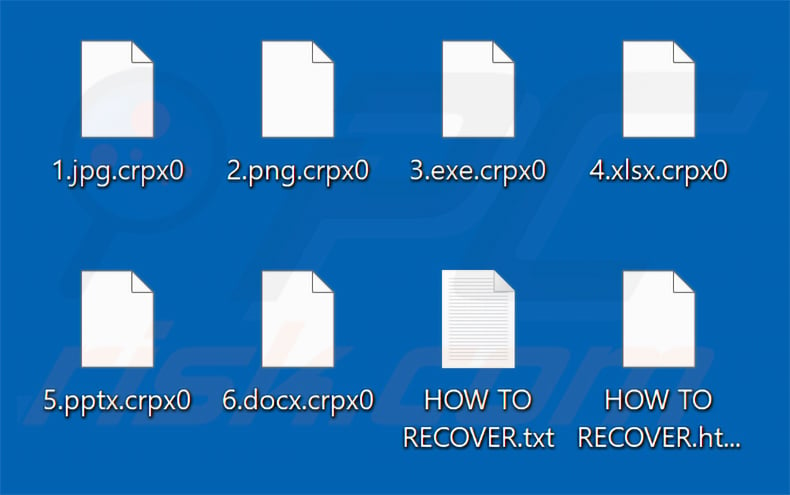
Files affected by this ransomware have the ".crpx0" extension appended to their names. For example, a file named "1.jpg" becomes "1.jpg.crpx0", "2.png" becomes "2.png.crpx0", and so on. Ransom notes are created in a text file named "HOW TO RECOVER.txt" and an HTML file named "HOW TO RECOVER.html".
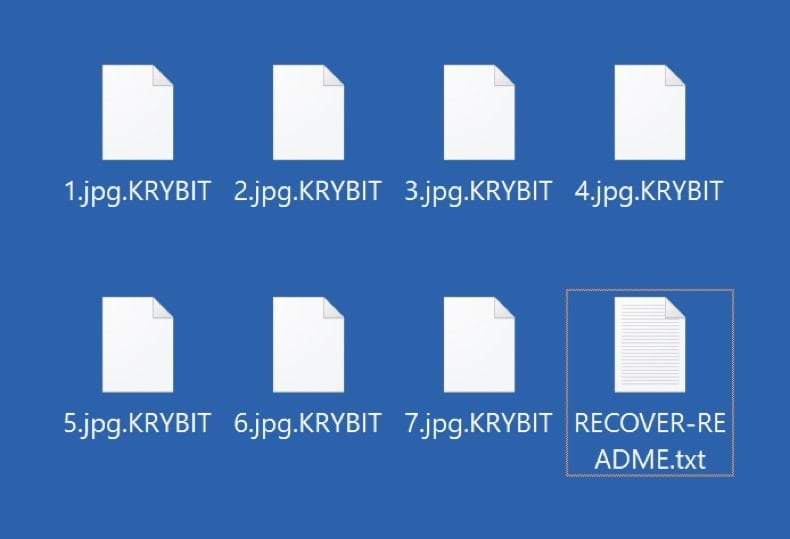
Screenshot of files encrypted by CRPxO ransomware:
CRPxO ransom note overview
The text file informs victims that their documents, databases, backups, images, and other files have been encrypted with AES-256 and RSA-2048. It also states that a copy of the data was downloaded to the attackers' servers before encryption took place.
The note sets a strict schedule. Victims who make contact within the first 24 hours are promised a 50% discount, while those who reach out between 24 and 48 hours must pay the full price. After 48 hours, the attackers threaten to publish the stolen data on their leak site and sell it to competitors and the public.
Three contact options are listed: a "negotiation room" accessed through the Tor Browser, the qTox chat app, and the Session messenger. Victims are told to include their recovery ID in the first message, and payment is requested in Bitcoin or Monero. As "proof", the attackers offer to decrypt 3-5 small files (under 4MB in total) for free.
The HTML file repeats essentially the same message and adds a countdown timer showing how much time is left before the data is published. Both notes warn against decrypting or renaming files, and against contacting law enforcement or data recovery services. They also threaten that the victim's patients, clients, and business partners will be notified if the ransom is not paid.
More about CRPxO
In most cases, files encrypted by ransomware cannot be restored without the attackers' decryption tool. Exceptions exist, but they usually involve ransomware with serious flaws in its code. Even so, paying is risky. Cybercriminals frequently fail to send the promised tools after receiving payment, and paying does not guarantee that stolen data will actually be deleted.
For this reason, we advise against meeting the ransom demands. CRPxO should be removed from the infected system as soon as possible, since it can keep encrypting new files while it remains active. Removal will not unlock the files that have already been encrypted, though.
The only reliable way to get them back is to restore them from a backup made before the infection. It is a good idea to keep copies of important data in several places, such as remote servers and storage devices that stay unplugged when not in use.
Ransomware in general
Ransomware attacks are all about money. The attackers lock files (and, more and more often, steal them too) and then charge victims for the means of getting them back. Most of these programs work in a similar way, with differences mainly in the symmetric or asymmetric encryption algorithms they use and the size of the ransom. Additional ransomware examples are AoQin, Dark Project, and Black Lotus.
How did ransomware infect my computer?
Ransomware is commonly spread through phishing and other social engineering tactics. Malicious files are often attached to or linked in spam emails and messages, disguised as invoices, shipping notices, or other ordinary documents. Some ransomware is also delivered by trojans that download extra malware once installed.
Infectious files come in various formats, including archives (ZIP, RAR), executables (EXE, RUN), PDFs, Microsoft Office and Microsoft OneNote documents, JavaScript, and so on. Opening one of these files is usually enough to start the infection.
Other common sources include drive-by downloads, malvertising, freeware and file-hosting sites, P2P networks, pirated software, illegal activation tools (cracks), and fake updates. In some cases, ransomware can also spread on its own through local networks and removable storage devices like USB drives.
| Name | CRPxO virus |
| Threat Type | Ransomware, Crypto Virus, Files locker |
| Encrypted Files Extension | .crpx0 |
| Ransom Demanding Message | HOW TO RECOVER.txt, HOW TO RECOVER.html, desktop wallpaper |
| Free Decryptor Available? | No |
| Cybercriminal Contact | Tor website (negotiation room), qTox, Session |
| Detection Names | Avast (Win32:MalwareX-gen [Misc]), Combo Cleaner (Gen:Variant.Ransom.CRP.1), ESET-NOD32 (Win32/TrojanDropper.Agent.TFQ Trojan), Kaspersky (UDS:Trojan.Win32.GenericML.xnet), Microsoft (Trojan:Win32/Draftor.GVA!MTB), Full List Of Detections (VirusTotal) |
| Symptoms | Cannot open files stored on your computer, previously functional files now have a different extension (for example, my.docx.locked). A ransom demand message is displayed on your desktop. Cybercriminals demand payment of a ransom (usually in bitcoins) to unlock your files. |
| Distribution methods | Infected email attachments (macros), torrent websites, malicious ads. |
| Damage | All files are encrypted and cannot be opened without paying a ransom. Additional password-stealing trojans and malware infections can be installed together with a ransomware infection. |
| Malware Removal (Windows) |
To eliminate possible malware infections, scan your computer with legitimate antivirus software. Our security researchers recommend using Combo Cleaner. Download Combo CleanerTo use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com. |
How to protect yourself from ransomware infections?
Be careful with incoming emails and messages, especially ones from unknown senders. Do not open attachments or links unless you are sure they are safe. Download software only from official websites and verified stores, and update or activate programs using the tools provided by their legitimate developers. Cracks and third-party "activators" are a common source of malware.
It is also important to have a reputable antivirus installed and kept up to date, and to run regular system scans. If your computer is already infected with CRPxO, we recommend running a scan with Combo Cleaner Antivirus for Windows to automatically eliminate this ransomware.
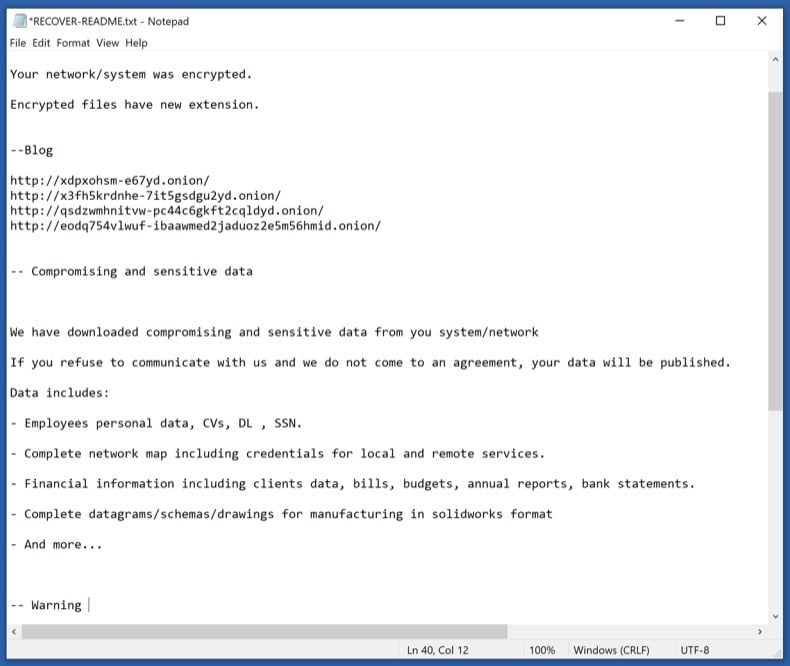
Screenshot of CRPxO's text file ("HOW TO RECOVER.txt"):
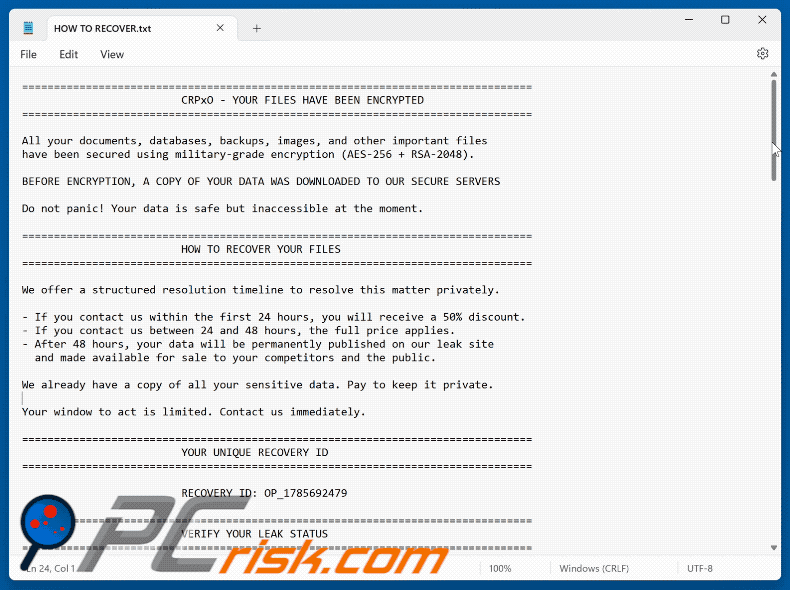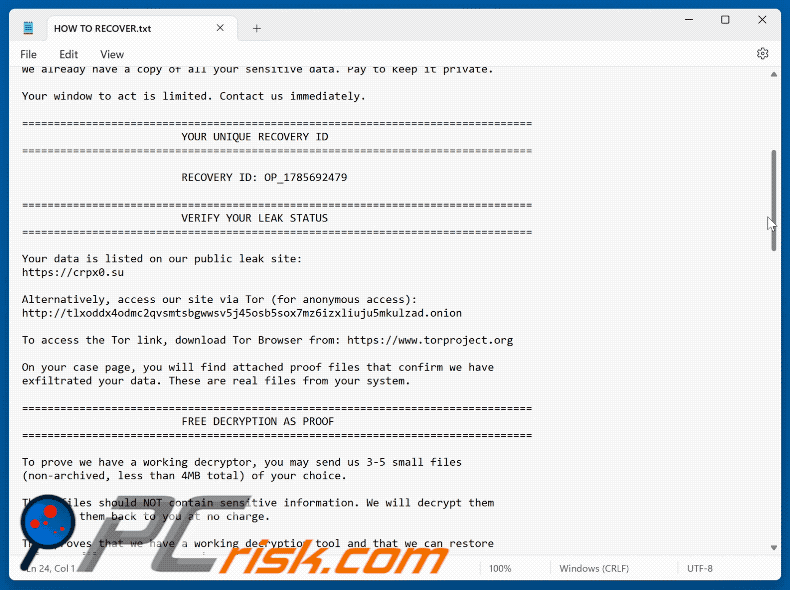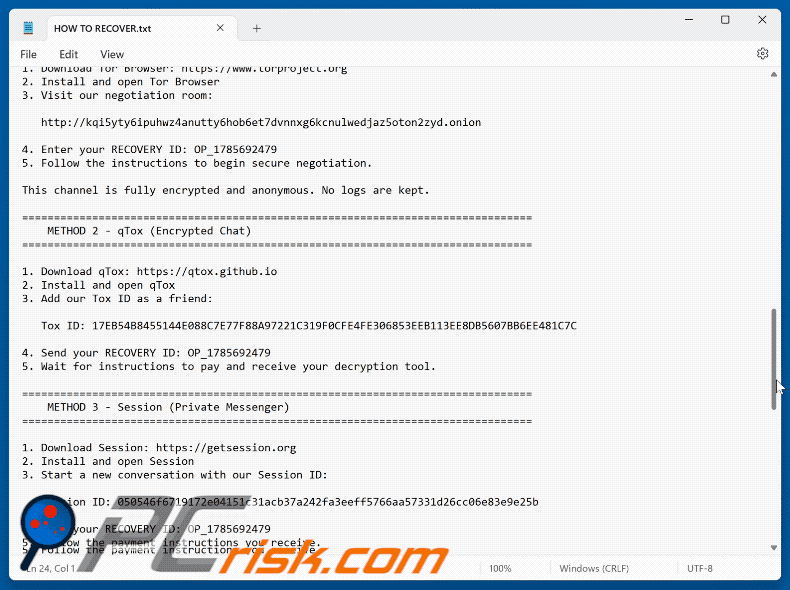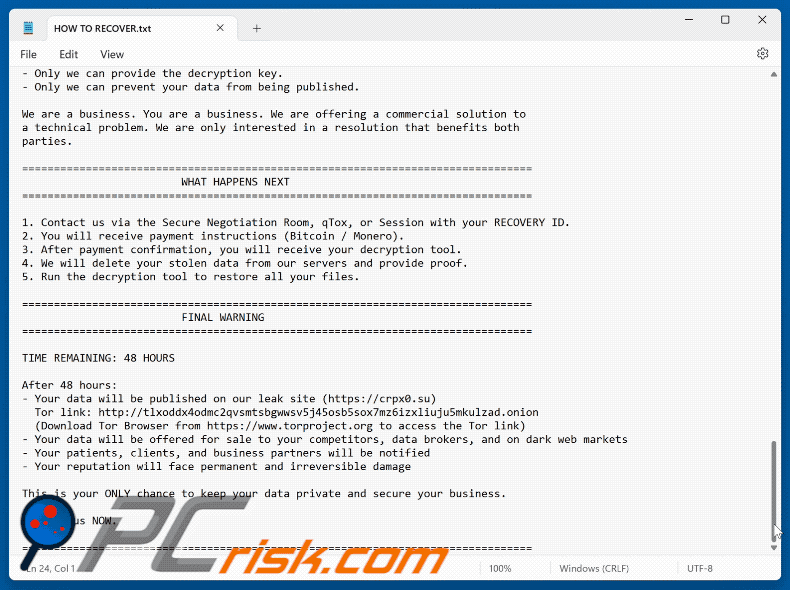
Text presented in this text file:
====================================================
CRPxO - YOUR FILES HAVE BEEN ENCRYPTED
====================================================All your documents, databases, backups, images, and other important files
have been secured using military-grade encryption (AES-256 + RSA-2048).BEFORE ENCRYPTION, A COPY OF YOUR DATA WAS DOWNLOADED TO OUR SECURE SERVERS
Do not panic! Your data is safe but inaccessible at the moment.
====================================================
HOW TO RECOVER YOUR FILES
====================================================We offer a structured resolution timeline to resolve this matter privately.
- If you contact us within the first 24 hours, you will receive a 50% discount.
- If you contact us between 24 and 48 hours, the full price applies.
- After 48 hours, your data will be permanently published on our leak site
and made available for sale to your competitors and the public.We already have a copy of all your sensitive data. Pay to keep it private.
Your window to act is limited. Contact us immediately.
====================================================
YOUR UNIQUE RECOVERY ID
====================================================RECOVERY ID: OP_1785692479
====================================================
VERIFY YOUR LEAK STATUS
====================================================Your data is listed on our public leak site:
hxxps://crpx0[.]suAlternatively, access our site via Tor (for anonymous access): -
To access the Tor link, download Tor Browser from: hxxps://www.torproject[.]org
On your case page, you will find attached proof files that confirm we have
exfiltrated your data. These are real files from your system.====================================================
FREE DECRYPTION AS PROOF
====================================================To prove we have a working decryptor, you may send us 3-5 small files
(non-archived, less than 4MB total) of your choice.These files should NOT contain sensitive information. We will decrypt them
and send them back to you at no charge.This proves that we have a working decryption tool and that we can restore
all your files once payment is made.Contact us using the methods below and we will provide instructions.
====================================================
CONTACT US IMMEDIATELY
====================================================You must contact us using ONE of the secure channels below.
Include your RECOVERY ID in your first message.====================================================
METHOD 1 - Secure Negotiation Room (Recommended)
====================================================We have set up a secure negotiation room on the darknet for you to resolve this
matter privately and confidentially.1. Download Tor Browser: hxxps://www.torproject[.]org
2. Install and open Tor Browser
3. Visit our negotiation room: -
4. Enter your RECOVERY ID: -
5. Follow the instructions to begin secure negotiation.This channel is fully encrypted and anonymous. No logs are kept.
====================================================
METHOD 2 - qTox (Encrypted Chat)
====================================================1. Download qTox: hxxps://qtox.github[.]io
2. Install and open qTox
3. Add our Tox ID as a friend:Tox ID: -
4. Send your RECOVERY ID: -
5. Wait for instructions to pay and receive your decryption tool.====================================================
METHOD 3 - Session (Private Messenger)
====================================================1. Download Session: hxxps://getsession[.]org
2. Install and open Session
3. Start a new conversation with our Session ID:Session ID: -
4. Send your RECOVERY ID: OP_1785692479
5. Follow the payment instructions you receive.====================================================
WARNING
====================================================- Do NOT attempt to decrypt files yourself - permanent data loss will occur.
- Do NOT rename or modify encrypted files - they will become unrecoverable.
- Do NOT contact law enforcement or data recovery services - they cannot help,
and your data will be leaked immediately.- Only we can provide the decryption key.
- Only we can prevent your data from being published.We are a business. You are a business. We are offering a commercial solution to
a technical problem. We are only interested in a resolution that benefits both
parties.====================================================
WHAT HAPPENS NEXT
====================================================1. Contact us via the Secure Negotiation Room, qTox, or Session with your RECOVERY ID.
2. You will receive payment instructions (Bitcoin / Monero).
3. After payment confirmation, you will receive your decryption tool.
4. We will delete your stolen data from our servers and provide proof.
5. Run the decryption tool to restore all your files.====================================================
FINAL WARNING
====================================================TIME REMAINING: 48 HOURS
After 48 hours:
- Your data will be published on our leak site (-)
Tor link: -
(Download Tor Browser from hxxps://www.torproject[.]org to access the Tor link)
- Your data will be offered for sale to your competitors, data brokers, and on dark web markets
- Your patients, clients, and business partners will be notified
- Your reputation will face permanent and irreversible damageThis is your ONLY chance to keep your data private and secure your business.
Contact us NOW.
====================================================
Screenshot of CRPxO's HTML file ("HOW TO RECOVER.html"):
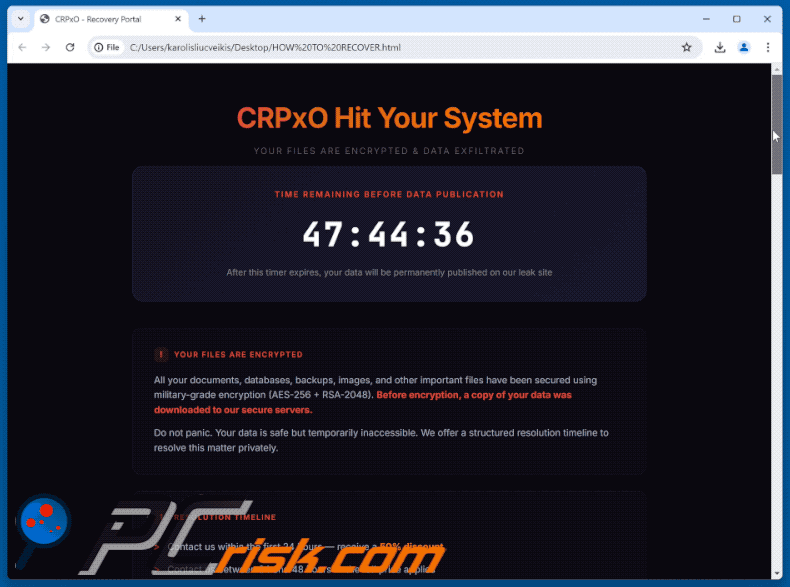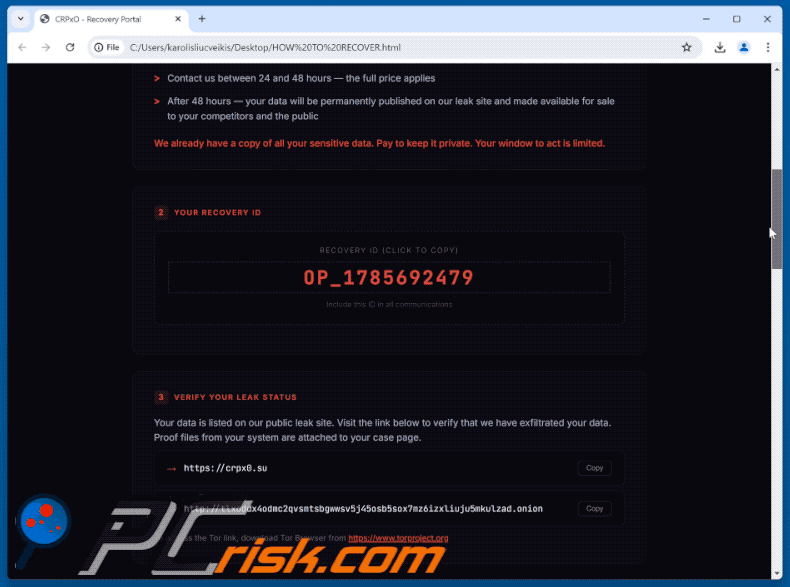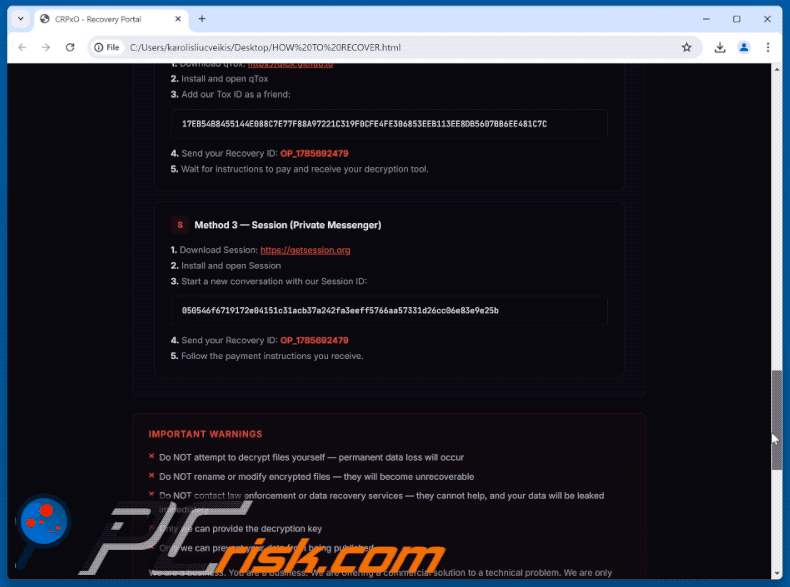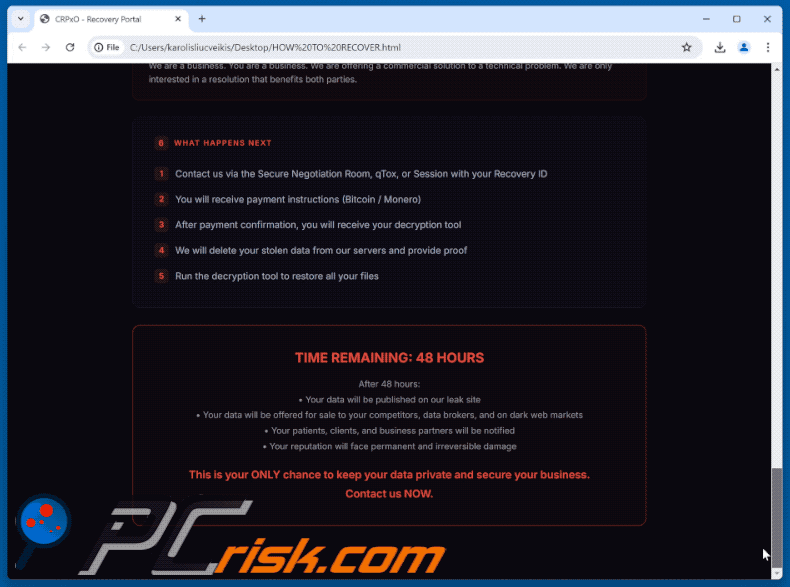
Text presented in this HTML file:
CRPxO Hit Your System
YOUR FILES ARE ENCRYPTED & DATA EXFILTRATED
TIME REMAINING BEFORE DATA PUBLICATION
47:46:23
After this timer expires, your data will be permanently published on our leak site
!
YOUR FILES ARE ENCRYPTED
All your documents, databases, backups, images, and other important files have been secured using military-grade encryption (AES-256 + RSA-2048). Before encryption, a copy of your data was downloaded to our secure servers.Do not panic. Your data is safe but temporarily inaccessible. We offer a structured resolution timeline to resolve this matter privately.
1
RESOLUTION TIMELINE
Contact us within the first 24 hours — receive a 50% discount
Contact us between 24 and 48 hours — the full price applies
After 48 hours — your data will be permanently published on our leak site and made available for sale to your competitors and the public
We already have a copy of all your sensitive data. Pay to keep it private. Your window to act is limited.2
YOUR RECOVERY ID
RECOVERY ID (CLICK TO COPY)
OP_1785692479
Include this ID in all communications
3
VERIFY YOUR LEAK STATUS
Your data is listed on our public leak site. Visit the link below to verify that we have exfiltrated your data. Proof files from your system are attached to your case page.To access the Tor link, download Tor Browser from hxxps://www.torproject[.]org
4
FREE DECRYPTION AS PROOF
To prove we have a working decryptor, you may send us 3-5 small files (non-archived, less than 4MB total) of your choice. These files should not contain sensitive information. We will decrypt them and send them back to you at no charge.Contact us using the methods below and we will provide instructions.
5
CONTACT US IMMEDIATELY
You must contact us using one of the secure channels below. Include your Recovery ID in your first message.N
Method 1 — Secure Negotiation Room
(Recommended)
We have set up a secure negotiation room on the darknet for you to resolve this matter privately and confidentially.1. Download Tor Browser: hxxps://www.torproject[.]org
2. Install and open Tor Browser
3. Visit our negotiation room: -
4. Enter your Recovery ID: OP_1785692479
5. Follow the instructions to begin secure negotiation.
This channel is fully encrypted and anonymous. No logs are kept.T
Method 2 — qTox (Encrypted Chat)
1. Download qTox: hxxps://qtox.github[.]io
2. Install and open qTox
3. Add our Tox ID as a friend:
-
4. Send your Recovery ID: OP_1785692479
5. Wait for instructions to pay and receive your decryption tool.
S
Method 3 — Session (Private Messenger)
1. Download Session: hxxps://getsession[.]org
2. Install and open Session
3. Start a new conversation with our Session ID: -
4. Send your Recovery ID: OP_1785692479
5. Follow the payment instructions you receive.
IMPORTANT WARNINGS
Do NOT attempt to decrypt files yourself — permanent data loss will occur
Do NOT rename or modify encrypted files — they will become unrecoverable
Do NOT contact law enforcement or data recovery services — they cannot help, and your data will be leaked immediately
Only we can provide the decryption key
Only we can prevent your data from being published
We are a business. You are a business. We are offering a commercial solution to a technical problem. We are only interested in a resolution that benefits both parties.6
WHAT HAPPENS NEXT
Contact us via the Secure Negotiation Room, qTox, or Session with your Recovery ID
You will receive payment instructions (Bitcoin / Monero)
After payment confirmation, you will receive your decryption tool
We will delete your stolen data from our servers and provide proof
Run the decryption tool to restore all your files
TIME REMAINING: 48 HOURS
After 48 hours:
• Your data will be published on our leak site
• Your data will be offered for sale to your competitors, data brokers, and on dark web markets
• Your patients, clients, and business partners will be notified
• Your reputation will face permanent and irreversible damageThis is your ONLY chance to keep your data private and secure your business.
Contact us NOW.
Screenshot of CRPxO's desktop wallpaper:
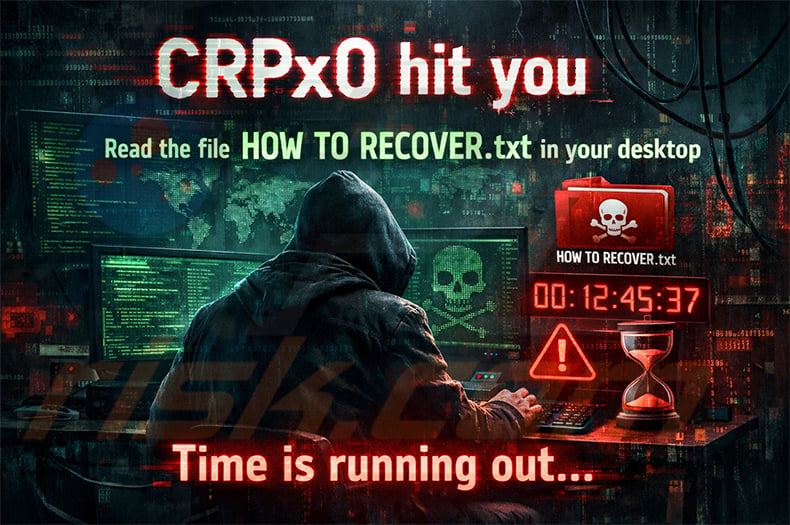
Text in the wallpaper:
CRPxO hit you
Read the file HOW TO RECOVER.txt in your desktop
Time is running out...
CRPxO ransomware removal:
Instant automatic malware removal:
Manual threat removal might be a lengthy and complicated process that requires advanced IT skills. Combo Cleaner is a professional automatic malware removal tool that is recommended to get rid of malware. Download it by clicking the button below:
DOWNLOAD Combo CleanerBy downloading any software listed on this website you agree to our Privacy Policy and Terms of Use. To use full-featured product, you have to purchase a license for Combo Cleaner. 7 days free trial available. Combo Cleaner is owned and operated by RCS LT, the parent company of PCRisk.com.
Removal and file recovery procedure
If your files are encrypted with a new extension and a ransom note has appeared, you've been hit by ransomware. Don't pay. The procedure below works in order: contain the infection, identify the variant, remove the ransomware itself (so anything you restore doesn't get re-encrypted), and try to recover files using free decryption tools, Windows Volume Shadow Copies, or backups. Run a full system scan with Combo Cleaner to remove the infection - then move on to file recovery.
Common ransomware behaviors
VisibleEncrypts your files and renames them
The ransomware reads each file, encrypts the contents with the attacker's public key, and writes the encrypted bytes back to disk. Most variants also rename the file by appending a new extension - .net, .locked, .crypt, .lockbit, .djvu, etc. Without the matching private key, the encrypted files cannot be opened normally. Recovery depends on a free decryption tool, a recoverable Volume Shadow Copy, or a clean backup.
VisibleDrops a ransom note in every encrypted folder
A text or HTML file (usually named HOW_TO_DECRYPT.txt, README.txt, _readme.txt, or similar) is placed in every folder that contains encrypted files. The note explains the situation, lists a payment amount in cryptocurrency, gives a deadline, and provides a contact email or .onion site. Save the note - don't delete it. Its exact wording, the email address, and the bitcoin wallet are how you identify the variant in the next phase.
VisibleReplaces the desktop wallpaper
Many ransomware variants change the Windows wallpaper to a black or red image with the ransom message and instructions. The wallpaper is just a visual scare tactic - it doesn't add any actual capability and reverts to normal once the ransomware is removed. Photograph it before removal in case the contact details are useful for variant identification or for reporting to authorities.
HiddenDeletes Volume Shadow Copies
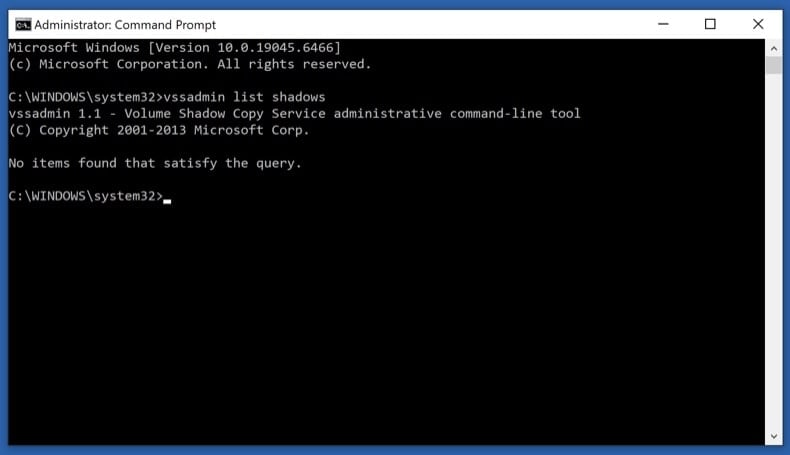
One of the first things modern ransomware does after launching is run vssadmin delete shadows /all /quiet to wipe Windows' built-in Volume Shadow Copies - the snapshots that Previous Versions and System Restore rely on. Some ransomware doesn't fully succeed (especially on systems where the user lacks full admin rights), leaving partial shadow copies recoverable. Phase 4 step 11 covers how to check what survived.
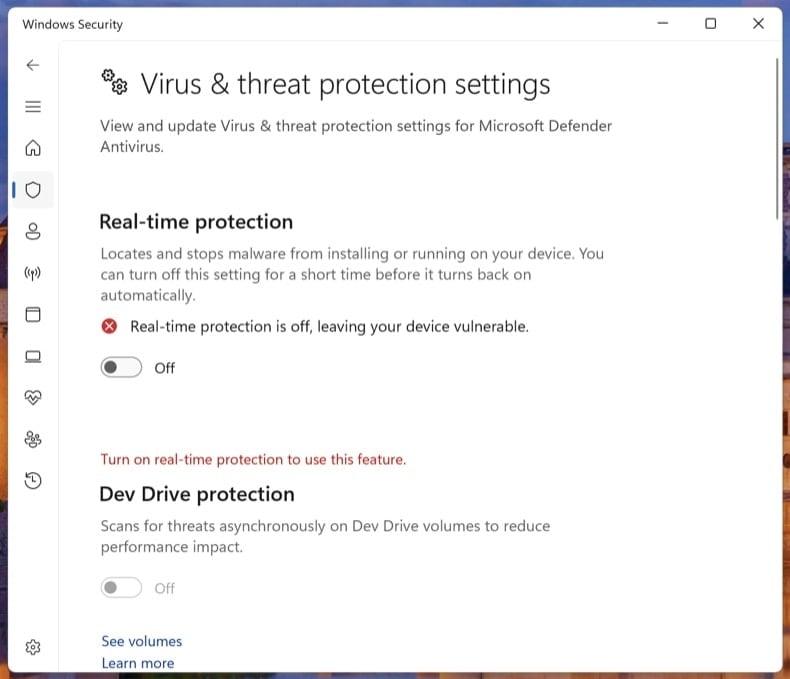
HiddenDisables Windows Defender and other security tools
Before encrypting, the ransomware tries to silence anything that could alert you or block it - Windows Defender real-time protection, third-party antivirus services, backup agents (Veeam, Acronis), and sometimes the Windows Event Log service. It often modifies Group Policy or registry keys to keep these off after reboot. Phase 3 step 9 explicitly turns Tamper Protection back on so the next ransomware attempt can't repeat the trick.
HiddenSpreads laterally to other PCs on the network
Network-aware ransomware (LockBit, Conti, BlackCat, Akira families) doesn't stop at the first machine. It scans for SMB shares, mapped drives, and other PCs on the same network, then encrypts whatever it can reach. On Windows domains, a single compromised user with admin rights can lead to all-domain encryption. This is why Phase 1 step 2 disconnects the network as the very first action - it stops the spread immediately.
HiddenSteals data before encrypting (double extortion)
Modern ransomware (LockBit, BlackCat / ALPHV, Akira, Cl0p, Royal) almost always exfiltrates data before encrypting. The attacker then runs a "double extortion" play: pay the ransom for decryption, plus pay again to prevent the stolen data from being leaked on the group's leak site. Paying the first ransom does not get the leaked data back - assume that anything the ransomware could read was uploaded. This is one more reason not to pay: the data is already out.
Don't pay the ransom
Paying the ransom does not guarantee you'll get your files back. Major ransomware response studies consistently show that a meaningful percentage of paying victims either receive a non-working decryptor, only partial decryption, or no decryptor at all. Beyond that:
- Paying confirms you as a willing target - re-attack rates within 12 months are high
- Several ransomware groups have been sanctioned (US OFAC, UK OFSI). Paying these groups may be illegal under sanctions law in your country
- The ransom funds the next attack - on you or someone else
- Modern ransomware almost always exfiltrates data first, so paying doesn't get the leaked data back. Assume anything the malware could read was uploaded
- Decryptors, even when they work, often leave files corrupted because the encryption itself was buggy or rushed
The path below tries every legal, free recovery option first. Pay only as an absolute last resort, after consulting a lawyer and your country's cyber crime authority.
Disconnect from the network and log out of cloud storage
Pull the Ethernet cable and turn off Wi-Fi on the affected PC. If multiple computers share the network, do the same on every machine you suspect could be affected, including any servers and NAS units.
Then sign out of cloud storage clients (OneDrive, Dropbox, Google Drive, iCloud) from their app settings. If you can, pause the sync. Some ransomware uses the running sync client to push encrypted versions over your clean cloud copies.
Modern ransomware spreads laterally across SMB shares, mapped drives, RDP, and reachable network neighbors. Disconnecting stops the spread the moment you do it. Logging out of cloud sync clients prevents the ransomware from encrypting the cloud copies of your files via the sync API.
Unplug external drives and USB storage
Safely eject any external drives, USB sticks, SD cards, and network-attached storage shares - then unplug them. If a drive was connected when the ransomware ran, the files on it may already be encrypted, but unplugging stops further damage.
Critically: don't reconnect any drive (including your most recent backup) to this PC until the ransomware is removed in Phase 3. Reconnecting an external backup to an actively-infected PC is the most common way that backup gets encrypted too.
Save the ransom note and a sample encrypted file
Copy the ransom note and one small encrypted file (under 1 MB) to a USB stick, or photograph the note with your phone. You'll need both for the variant identification step.
The ransom note is usually one of:
- A
.txtfile in every encrypted folder (typicallyHOW_TO_DECRYPT.txt,README.txt, or_readme.txt) - An
.htmlfile with the same purpose - A changed desktop wallpaper - photograph it
- A lock-screen interrupt that runs at startup - rarer
Don't delete the note. Variant identification depends on its exact wording, the contact email, and the bitcoin wallet address. The note is also evidence if you report to authorities.
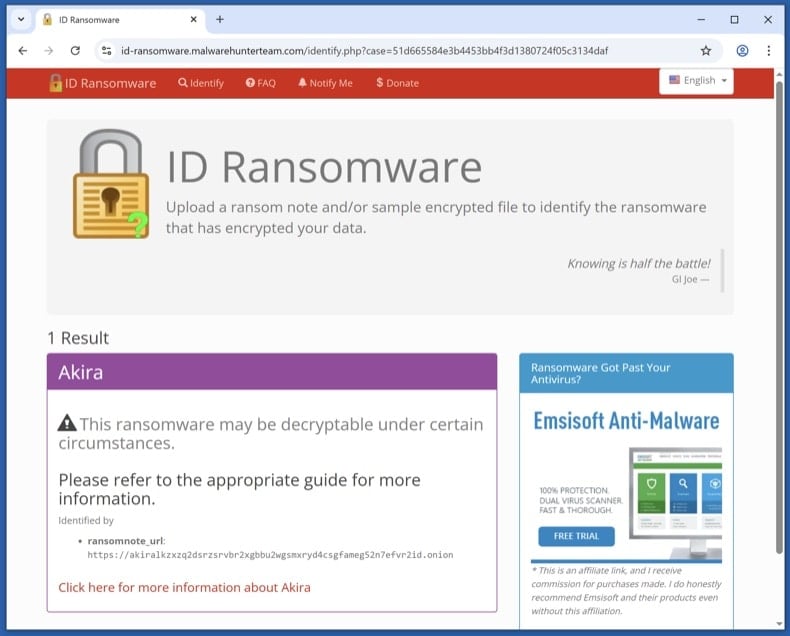
Identify the variant with ID Ransomware
From a clean device (your phone is fine, or another PC that wasn't on the affected network), visit id-ransomware.malwarehunterteam.com. Upload the ransom note and the sample encrypted file. The site identifies the variant family and tells you whether a free decryptor exists.
ID Ransomware is run by the Malware Hunter Team. Files you upload are kept private - they're used for analysis, not published. If you're concerned about uploading data anyway, you can paste the contact email and bitcoin wallet from the note - those are often enough for identification.
The ransomware itself must be removed before any file recovery. If it's still active, anything you restore in Phase 4 gets re-encrypted within minutes.
Boot to Safe Mode with Networking and download the scanners
Safe Mode loads only the minimal Windows drivers, which prevents most ransomware from auto-running while you set up the scanners.
Windows 11: open , click Restart now next to Advanced startup. After the restart, click , then press 5 or F5.
Windows 10: click the Windows logo, hold Shift, click the Power icon and choose Restart. From the Choose-an-option screen, click , then press F5.
Once Safe Mode has loaded, turn Wi-Fi back on and download Combo Cleaner (used in step 8) and Microsoft Safety Scanner (used in step 9). Save both installers to your Desktop, then disconnect Wi-Fi again before scanning.
Run Microsoft Defender Offline
Reboot to normal Windows. Open . Select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts into a stripped-down environment and scans the disk before Windows fully loads.
Some ransomware variants drop bootkit components or kernel hooks that hide from any scanner running on the same Windows session that's already infected. A pre-boot offline scan sees the disk before the malware can load itself.
VB100 certified. Includes anti-trojan, registry/persistence scanning, and anti-spyware in one pass. The 7-day free trial is available.
Download Combo CleanerRun a full Combo Cleaner scan
Run the installer you downloaded in step 6 and start a full system scan (not the quick scan). Let it complete, review what it detected, and apply the recommended actions. Combo Cleaner quarantines the ransomware executable and the registry / scheduled-task entries that re-launch it on reboot.
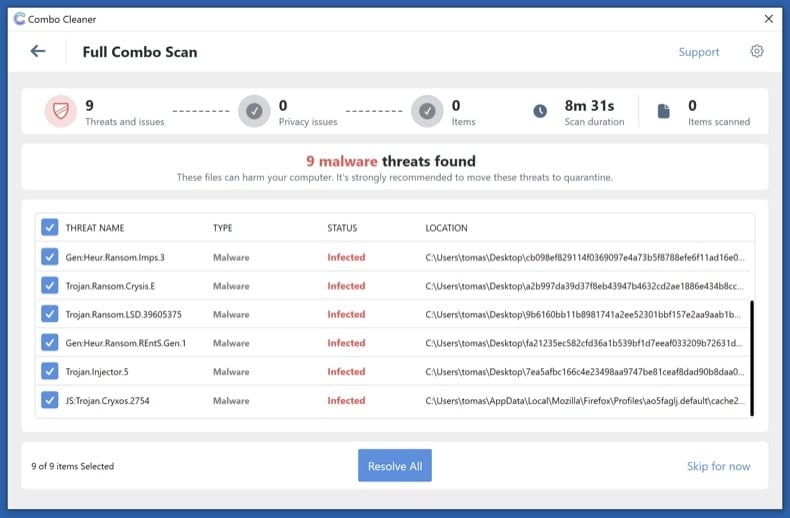
Run Microsoft Safety Scanner and re-enable Defender
Run Microsoft Safety Scanner (MSERT.exe) as a second-opinion full scan. The binary expires every 10 days so the copy you downloaded has the latest signatures.
Once it finishes, open and confirm Real-time protection, Cloud-delivered protection, and Tamper Protection are all on. Many ransomware variants disable Defender during the attack - this is where you switch it back on so the next attempt can't repeat the trick.
Different scanning engines catch different threats. Running an additional Microsoft scan after Combo Cleaner is the most underused verification step in malware removal - and free.
Try the steps in order. The first decryptor that works ends the recovery process - no need to do all four.
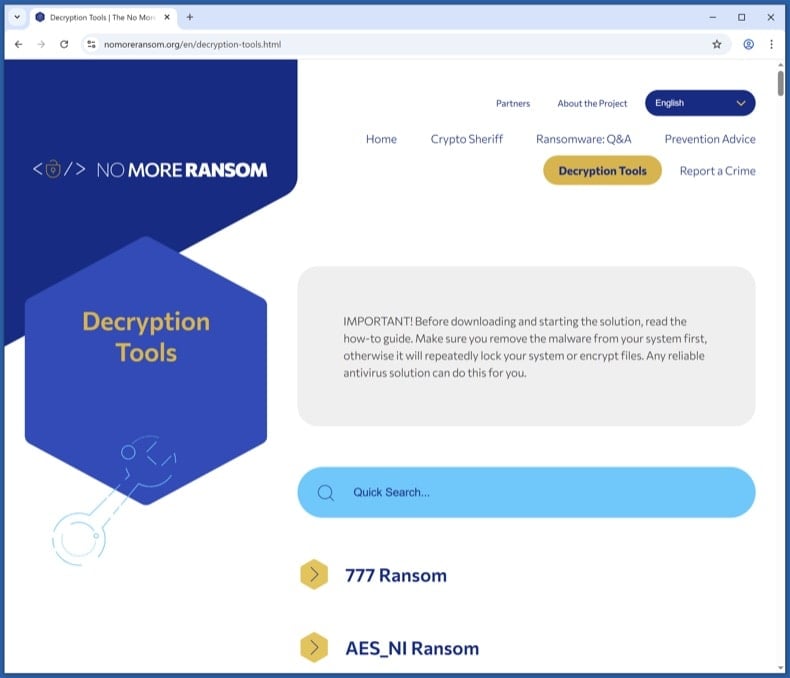
Check the No More Ransom Project for a free decryptor
Visit nomoreransom.org and search the Decryption Tools list for the variant name returned by ID Ransomware. The project is run by Europol, the Dutch Police, and security vendors - everything listed is legitimate and free.
If a decryptor exists, download it onto a clean PC, copy it across, and follow its instructions exactly. Decryptors usually want you to point them at a sample encrypted file plus its known unencrypted version (sometimes any image you previously had a backup of works).
Free decryptors exist for parts of the STOP/Djvu, GandCrab, REvil, Avaddon, Conti and Hive families, among others. Most modern variants don't have public decryptors - if yours isn't listed, that's expected; move to the next step.
Try Windows Volume Shadow Copies
Windows automatically creates Volume Shadow Copies of files when System Restore points are made or scheduled backups run. Most ransomware tries to wipe these (vssadmin delete shadows /all /quiet), but the deletion sometimes fails partially - especially if the running user doesn't have full admin rights. When it does fail, snapshots survive that contain pre-encryption versions of your files.
First, check what's there. Open Command Prompt as Administrator and run:
vssadmin list shadows
If you see entries listed, shadow copies survived. To restore from them:
- Built-in: right-click any folder → Properties → Previous Versions tab. Pick a snapshot dated before the infection and restore.
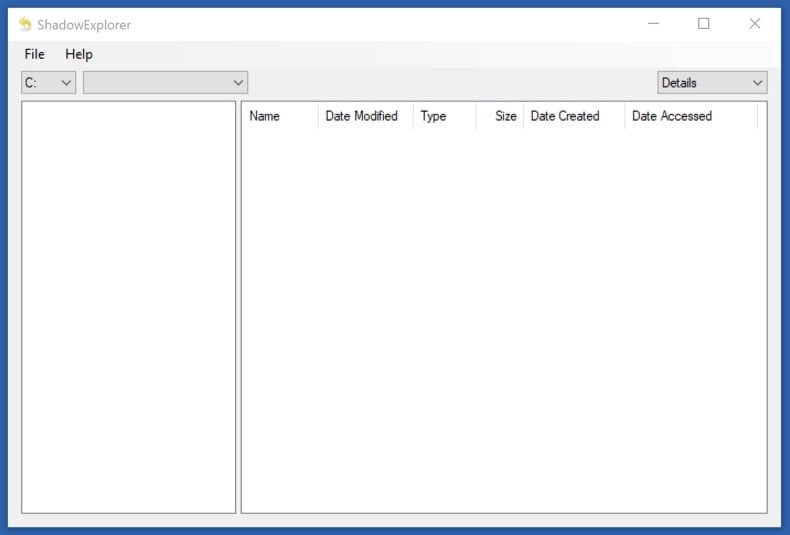
- Better tool for browsing: install Shadow Explorer (free). It shows all snapshots as a normal file tree and lets you copy out only the files you want.
Shadow Copies recover the original files exactly, with no risk of decryption errors. If they survived, this is faster and cleaner than running a decryptor on the encrypted set.
Restore from cloud or external backup
If you have a backup that pre-dates the infection, this is the cleanest recovery available. Important precautions:
- Don't reconnect a backup drive until Phase 3 is complete. If the ransomware is still active, plugging in the backup encrypts it too.
- For cloud backups (OneDrive, Dropbox, Google Drive, iCloud), use the Version History feature to roll individual files back to pre-encryption versions.
- OneDrive specifically has a "Restore your OneDrive" feature: if it detected mass file changes, you can roll back the entire account up to 30 days. Sign in at OneDrive on the web, click the Settings gear, and choose Restore your OneDrive. Microsoft 365 subscribers also get ransomware detection alerts; non-subscribers get one free recovery.
- Verify the restored files open correctly before you delete the encrypted set. Test a few documents, photos, and any database / project files.
Try Recuva as a last-resort recovery
Recuva is a long shot, not a primary recovery tool. Most modern ransomware encrypts files in place - it reads the original, encrypts the data, and writes the encrypted bytes back to the same disk location. In that case, the original isn't deleted, just rewritten - and Recuva has nothing to find.
But for older or simpler variants that deleted originals before creating encrypted copies (rather than encrypting in place), Recuva can sometimes pull the originals from unallocated disk space. Worth trying as a last resort, especially before you use the disk much further.
If you try it:
- Stop using the disk as much as possible - every disk write reduces recovery odds
- Run Recuva from a USB stick, not from the affected disk
- Use Deep Scan mode (slower but the only mode worth running for this scenario)
Don't skip the steps above expecting Recuva to bail you out. It works in maybe 5-20% of cases, depending on the variant and how soon you try.
Report the attack to authorities
Even if your files aren't recovered, your report helps authorities track variants, attribute groups, and warn future victims. In some jurisdictions (especially the US and UK) early reporting can sometimes help recall a wired ransom payment via banking partners.
Save the report number - banks, insurers, and credit bureaus will ask for it. If you operate a business, you may also have legal disclosure obligations (GDPR in the EU, state breach laws in the US) that run on a 72-hour clock.
Plan 3-2-1 backups going forward
The single best defense against ransomware is a tested backup. Use the 3-2-1 rule:
- 3 copies of your data
- 2 different storage media (e.g., internal drive + external drive)
- 1 offline / air-gapped copy (an external drive that isn't always connected)
Recommended cadence:
- Daily: cloud sync (OneDrive, Dropbox, Google Drive) - convenient, but vulnerable if the ransomware reaches the sync folder. The Version History feature is what saves you
- Weekly: external drive that you connect briefly, then disconnect - the air-gap is what protects against ransomware
- Monthly: a second external drive stored off-site (different physical location) - protects against fire, theft, flood
Test the backup at least once. Open a few files from it, check sizes match, restore one to a different folder. An untested backup isn't a backup - it's a hope.
Patch the entry point and monitor for 30 days
Most reinfections happen via the same vector that worked the first time. Until you've patched the entry point, watch for:
- Unusual disk activity, unexpected file modifications, or unfamiliar processes in Task Manager
- Unexpected reboots or new accounts you didn't create
- Defender or your antivirus turning itself off again
Common entry vectors and what to do about each:
- Phishing email with a malicious attachment - review email filters and train yourself / staff to recognise the patterns - see pcrisk's Phishing/Scam reference
- Exposed RDP with weak passwords - disable Remote Desktop from if you don't need it. If you do, put it behind a VPN and require a long password plus MFA
- Unpatched VPN appliances or public-facing apps - check the vendor's advisories page and apply the latest firmware
- Cracked / pirated software - was the most common vector for STOP/Djvu in particular. Don't run software from torrent sites
Run a Combo Cleaner scan weekly for the first month. Update Windows, browsers, and applications aggressively.
Important: Removing a ransomware infection requires a full system scan, not a manual file delete. If you're not confident with the manual procedure, run an automated scan with Combo Cleaner and Windows Defender and stop there - that combination removes the vast majority of consumer ransomware variants. Then move to Phase 4 for file recovery, or to Phase 5 if your files are unrecoverable and you need to start fresh from a clean Windows install.
Frequently Asked Questions (FAQ)
How was my computer hacked and how did hackers encrypt my files?
In many cases, victims run the ransomware themselves without realizing it, since it is usually disguised as a normal file or bundled with something else. Ransomware is mostly spread through phishing emails, trojans, malicious ads, drive-by downloads, untrustworthy download sites, pirated software, cracks, and fake updates.
How to open ".crpx0" files?
Files with the ".crpx0" extension are encrypted and cannot be opened or used until they are decrypted.
Where should I look for free decryption tools for CRPxO ransomware?
After a ransomware attack, we recommend checking the No More Ransom project website (more information above).
I can pay you a lot of money, can you decrypt files for me?
No, we do not provide decryption services. Unless the ransomware has serious flaws, encrypted files generally cannot be recovered without the attackers' involvement. Third parties offering paid decryption are often scammers or simply act as middlemen between victims and cybercriminals.
Will Combo Cleaner help me remove CRPxO ransomware?
Yes, Combo Cleaner can scan your computer and remove active ransomware infections like CRPxO. Keep in mind, however, that antivirus software cannot decrypt files that have already been encrypted.
Share:
 Facebook
 X.com
 LinkedIn
 Copy Link
Tomas Meskauskas
Expert security researcher, professional malware analyst
I am passionate about computer security and technology. I have an experience of over 10 years working in various companies related to computer technical issue solving and Internet security. I have been working as an author and editor for pcrisk.com since 2010. Follow me on Twitter and LinkedIn to stay informed about the latest online security threats.
PCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
DonatePCrisk security portal is brought by a company RCS LT.
Joined forces of security researchers help educate computer users about the latest online security threats. More information about the company RCS LT.
Our malware removal guides are free. However, if you want to support us you can send us a donation.
Donate
▼ Show Discussion